Skip to content

2003

SpamAssassin wins twice in OSDir.com's 2003 Editor's Choice Awards in Open Source (fwd)

SpamAssassin: The 2003 OSDir.com Editor's Choice Awards in Open Source. Woo!

Editor's Choice for Best Application (Top 5 environments):

Email: SpamAssassin (Double Winner)

SpamAssassin keeps keeps me out of Anger Management classes. If you are not running SpamAssassin get thee to SpamAssassin.org. Now. If you need your friendly neighborhood system administrator to do it.. start sending flowers or Scotch today with a nice little note asking to get SpamAssassin going medieval on your mail server.

Miscellaneous Editor's Choice:

Can't Live Without: SpamAssassin

The fact that this doesn't have to be explained says it all.

spamassassin anti-spam hacks

Wright Brothers Hack at MIT

Funny: The latest MIT 'hack': a replica of the Wright brothers' biplane on top of the MIT Great Dome. Nice work!

The model was dismantled Thursday by Barber and Cunha, the Institute's hack evaluation and removal team, who salvaged a completed FAA certificate of airworthiness form for the MIT Museum.

history hacking funny

How Not To Use OOP

Code: OOP over the top: a hilarious dissection of some of the most monstrous 'how to rewrite OO-style' I have ever seen -- take a 15-line if/elseif/else clause and rewrite as a thoroughly over-engineered unmaintainable 7-class, 15-method disaster, using the Singleton and Factory patterns. The rewrite in the original article is intended seriously, as far as I can tell.

As the xmldatabases.org article says: 'this is really a general problem with OO development. Fancy object oriented architectures have become the goal and this article maybe makes that point more clearly then anything I could ever say. It's representative of the thinking from a few years ago (written in 2000), and shows us just how much damage we now have to undo. It basically says that the simple solution that just works is wrong and will be unmaintainable. Maybe that's true, maybe it's not, nowhere does the article consider the question of whether or not that code actually needs to be that generic. It simply says that the simple solution is bad and that the seven class monster they came up with is the right solution. Talk about doing a disservice to students trying to learn how to build solid computer systems.'

(Found via sourcefrog.net -- Martin Pool's weblog, great for Linux and code bits).

WebMake: linux.com: An introduction to building sites with WebMake. W00t! Let's hope nobody asks any questions while I'm away for xmas ;)

coding programming software

The Wright Brothers and Patenting

Innovation: Maciej posts a fantastic look back on the Wright Brothers from an interesting angle -- their patent-related antics.

The Wright brothers won every patent case they fought, and it did them absolutely no good. The prospect of a fortune wasn't what motivated them to build an airplane, but ironically enough they could have made a fortune had they just passed on the litigation. In 1905, the Wrights were five years ahead of any potential competitor, and posessed a priceless body of practical knowledge. Their trade secrets and accumulated experience alone would have made them the leaders in the field, especially if they had teamed up with Curtiss. Instead, they got to watch heavily government-subsidized programs in Europe take the technical lead in airplane design as American aviation stagnated.

Fantastic article. If you're curious about the history of patenting, and its many fundamental failures, I can't recommend it enough.

Weblogs: Guardian's 'best of British blogging': good set of winners this year.

patents uspto swpats open-source ip

Racism in New Zealand, Teapot, and Lena

Politics: Lest we get carried away with the beauty, grooviness and coolness-in-general of New Zealand -- where 1 in 160 of the population was involved in the making of the LoTR trilogy -- up pops this story. It seems racism and xenophobia is finally arriving on the shores of Aotearoa.

Under the headline 'Whose country is it anyway?' Peters's leaflet rails against Asian immigrants, falsely claiming that hundreds of thousands are coming to New Zealand and blaming them for, among other things, traffic problems in Auckland. These immigrants are, according to Peters, simultaneously poor enough to be leeches on the welfare system, and rich enough to drive up the cost of housing.

It would be easy to dismiss all this as a piece of desperate populism. But, unlike the Australian One Nation party, New Zealand First is not a collapsing political joke: it is the third-biggest party in Wellington's parliament, and until 1999 Mr Peters was the country's deputy prime minister. Barring an electoral miracle, the opposition National party will have to take them on as coalition partners if it is ever to win another election.

'Traffic problems in Auckland'? WTF? (found via Danny Yee)

Computing: Amazing. via GirlHacker, it turns out that a teapot has long been used as a demonstration of complex computer graphics techiques -- with it's curved surfaces, hidden surfaces and the like (don't ask me, I'm no graphics guru). If you were around for the early 3-D graphics days, you've almost definitely seen the teapot.

Well, it turns out there was a real teapot. Here's the history.

A related image is that of 'Lenna', a standard test image used when testing image compression schemes, which features a woman giving the viewer a rather saucy come-hither look. It turns out she was a Swedish model, who posed for Playboy in 1972, and that picture was scanned by an (unauthorized) researcher at USC. Piracy!

Playboy later threatened to prosecute over the unauthorized use, but by now has recognised the unique history this now has, and has relented. Cool.

politics uk ireland

Racism in New Zealand, Teapot, and Lena

Lest we get carried away with the beauty, grooviness and coolness-in-general of New Zealand -- where 1 in 160 of the population was involved in the making of the LoTR trilogy -- up pops this story. It seems racism and xenophobia is finally arriving on the shores of Aotearoa.

Under the headline 'Whose country is it anyway?' Peters's leaflet rails against Asian immigrants, falsely claiming that hundreds of thousands are coming to New Zealand and blaming them for, among other things, traffic problems in Auckland. These immigrants are, according to Peters, simultaneously poor enough to be leeches on the welfare system, and rich enough to drive up the cost of housing.

It would be easy to dismiss all this as a piece of desperate populism. But, unlike the Australian One Nation party, New Zealand First is not a collapsing political joke: it is the third-biggest party in Wellington's parliament, and until 1999 Mr Peters was the country's deputy prime minister. Barring an electoral miracle, the opposition National party will have to take them on as coalition partners if it is ever to win another election.

'Traffic problems in Auckland'? WTF? (found via Danny Yee)

Computing: Amazing. via GirlHacker, it turns out that a teapot has long been used as a demonstration of complex computer graphics techiques -- with it's curved surfaces, hidden surfaces and the like (don't ask me, I'm no graphics guru). If you were around for the early 3-D graphics days, you've almost definitely seen the teapot.

Well, it turns out there was a real teapot. Here's the history.

A related image is that of 'Lenna', a standard test image used when testing image compression schemes, which features a woman giving the viewer a rather saucy come-hither look. It turns out she was a Swedish model, who posed for Playboy in 1972, and that picture was scanned by an (unauthorized) researcher at USC. Piracy!

Playboy later threatened to prosecute over the unauthorized use, but by now has recognised the unique history this now has, and has relented. Cool.

politics uk ireland

Aug 14th 2003 Blackout and the Blaster worm

Security: Bruce Schneier points out some interesting angles on the official report into the US power blackout of Aug 14th:

Why the tortured prose? The writers take pains to assure us that the power generation and delivery systems were not affected by MSBlast. But what about the alarm systems? Clearly, they were all affected by something--and all at the same time.

To be honest, it sounds pretty damn close to me, as I've said before.

security hacks games

That Samuel L. Jackson quote again

Ireland: Looks like I was wrong about that Samuel L. Jackson quote -- it really did happen!

Tom did the heavy lifting, and asked the production company; here's the scoop:

Anyway in answer to your question, similar comments were indeed made on the TV Special 'SWAT - The Movie'. In the programme Colin is considered a very successful 'fish out of water' in LA and the line of questioning was exploring how the Americans view him. Kate was 'claiming' Colin as our own in an 'inclusive' way. It was meant as a mark of comradeship rather than thievery and being of liberal mind I can assure you Kate has no intention of staking any real claims! It went like this.

KATE THORNTON:
Now lets talk about Colin because in the UK he's become the man of the moment.

SAMUEL L.JACKSON:
Really? Only in the UK?

KT: Well everywhere but we kind of claim him as our own because he's from Ireland.

SLJ: You can't claim him because he's from Ireland.

KT: Well we do because it's close by. (laughter)

SLJ: Ok. That's the source of all the conflict over there. You people always claiming the Irish as yours. We got a little problem just like that here called slavery but that's ok we don't need to talk about that so lets go. (more laughter)

KT: Well Colin is a very well paid slave.

SLJ: Ok good.

KT: As are you.

SLJ: Yeah all right.

KT: What did you know about him before you came to work with him on this project?

SLJ: I knew he was a hot, young, Irish actor who was good looking and I talked to a couple of people about him. I talked to Bruce about him and I talked to some script supervisors that had worked with him on a couple of things and they all loved him.

KT: So you checked him out?

SLJ: Yeah

The programme was an irreverent promotional vehicle for SWAT and it's cast and I must say that Colin gave the most honest interview I've ever heard on a junket. Long may his attitude prevail. Does this answer your question and win you the bet?

Yours sincerely,

Rufus Roubicek
Executive Producer
matchboxtv.com

ireland politics history uk coding funny

Overheard on the radio

Funny: overheard on the radio just now, from the DJ interrupted during a station ident: 'Your phone's ringing. What, you have a text message? Fancy!'

Just to remind me I'm in the US ;)

Mind you, the DJ seems a bit out of touch; he's clearly just discovered the Rock Gods that are The Darkness.

music mp3 filesharing

Pharma companies 'hoodwinking' medical journals

Health: Revealed: how drug firms 'hoodwink' medical journals (Observer) -- an
amazing attempt to mislead scientific progress for short-term commercial gain. (via forteana):

Hundreds of articles in medical journals claiming to be written by academics or doctors have been penned by ghostwriters in the pay of drug companies, an Observer inquiry reveals. The journals, bibles of the profession, have huge influence on which drugs doctors prescribe and the treatment hospitals provide. ...

Estimates suggest that almost half of all articles published in journals are by ghostwriters. While doctors who have put their names to the papers can be paid handsomely for 'lending' their reputations, the ghostwriters remain hidden. They, and the involvement of the pharmaceutical firms, are rarely revealed. ...

(One) email, seen by The Observer, said: 'In order to reduce your workload to a minimum, we have had our ghostwriter produce a first draft based on your published work. I attach it here.' The article was a 12-page review paper ready to be presented at an forthcoming conference. Healy's name appeared as the sole author, even though he had never seen a single word of it before. But he was unhappy with the glowing review of the drug in question, so he suggested some changes. The company replied, saying he had missed some 'commercially important' points. In the end, the ghostwritten paper appeared at the conference and in a psychiatric journal in its original form - under another doctor's name.

linux data privacy

That Samuel L. Jackson quote again

Looks like I was wrong about that Samuel L. Jackson quote -- it really did happen!

Tom did the heavy lifting, and asked the production company; here's the scoop:

Anyway in answer to your question, similar comments were indeed made on the TV Special 'SWAT - The Movie'. In the programme Colin is considered a very successful 'fish out of water' in LA and the line of questioning was exploring how the Americans view him. Kate was 'claiming' Colin as our own in an 'inclusive' way. It was meant as a mark of comradeship rather than thievery and being of liberal mind I can assure you Kate has no intention of staking any real claims! It went like this.

KATE THORNTON: Now lets talk about Colin because in the UK he's become the man of the moment.

SAMUEL L.JACKSON: Really? Only in the UK?

KT: Well everywhere but we kind of claim him as our own because he's from Ireland.

SLJ: You can't claim him because he's from Ireland.

KT: Well we do because it's close by. (laughter)

SLJ: Ok. That's the source of all the conflict over there. You people always claiming the Irish as yours. We got a little problem just like that here called slavery but that's ok we don't need to talk about that so lets go. (more laughter)

KT: Well Colin is a very well paid slave.

SLJ: Ok good.

KT: As are you.

SLJ: Yeah all right.

KT: What did you know about him before you came to work with him on this project?

SLJ: I knew he was a hot, young, Irish actor who was good looking and I talked to a couple of people about him. I talked to Bruce about him and I talked to some script supervisors that had worked with him on a couple of things and they all loved him.

KT: So you checked him out?

SLJ: Yeah.

[....]

The programme was an irreverent promotional vehicle for SWAT and it's cast and I must say that Colin gave the most honest interview I've ever heard on a junket. Long may his attitude prevail. Does this answer your question and win you the bet?

Yours sincerely,

Rufus Roubicek
Executive Producer
matchboxtv.com

politics ireland uk history eu coding

Windows/Linux Biculturalism

Software: Joel on Biculturalism: 'What are the cultural differences between Unix and Windows programmers? There are many details and subtleties, but for the most part it comes down to one thing: Unix culture values code which is useful to other programmers, while Windows culture values code which is useful to non-programmers.'

I'm not sure I agree; I've met lots of Windows programmers who take what Joel calls the 'UNIX' orientation, and even a few Unix people who are as user-oriented in their coding as what Joel calls the 'Windows' way.

But, talking of the Unix/Win divide -- it seems that Ward Cunningham, inventor of the Wiki, is joining MS, who have something called SharePoint Team Services, an editable-web group sharing system as part of Front Page.

If you ever wanted to see an illustration of a Windows-Unix divide in the web age, it sounds like this is it: Wiki has quick-and-dirty links in FuglyBouncingCaps, is text-heavy, has obscure text markup formats, has little in the way of roles, access control, or a workflow model, and has some odd magic pages that live in the same namespace as everything else despite being different.

SharePoint, by contrast, is integrated with everything in Office, is a great success where the MS Kool-Aid is viewed as tasty, uses role-based security and a workflow, and seems to be generally reviled elsewhere.

No better illustration. The only thing that could improve that would be if SharePoint has a talking paperclip I've missed.

coding programming unix

A New Toy

Fun: C just got her xmas present; a digital camera, the Sony DSC P10 to be exact. Results to right ;)

Good: Sony's easy-to-use use of USB mass-storage and open formats (GIF, JPEG, and MPEG). pnmstitch.

Bad: having to upgrade my kernel to 2.4.23 to get the bloody thing mounted! (Of course, iPhoto recognised it right away.)

hardware ireland linux images

Irish Anti-Spam Law, and Gaven Stubberfield Arrested

Spam: Let me take this moment to welcome our UK friends to the 'spam now illegal' club; unlike the US, the European and Australian anti-spam laws seem to be shaping up nicely, requiring opt-in before 'email marketing' can be sent.

This actually happened in Ireland a couple of weeks ago, but I think I forgot to mention it here, so here's the details:

Announcement, full text, full text as HTML. (It's section 13 you want to read. Note that OpenOffice seems to have miscounted the bullet points in the HTML version ;)

The good stuff:

  • it's opt-in, not opt-out like the cruddy CAN-SPAM act in the US. so that's a fundamentally anti-spam position. Thanks EU!
  • each spam counts as a separate offence = lots of damages, I'd guess.
  • forging/disguising of originating header info is prohibited.

The bad:

  • if you run a mailing list, and you're not sure that you got everyone's permission to receive your mails (and if not, why not?), you'd better do a reconfirmation run quick ;)
  • no private right of action; but that's pretty much std for Europe. we're reliant on the Regulator to take action against spammers.
  • spamming to mailing lists is not prohibited -- but then, I haven't seen that blocked by any other law.
  • it's unclear if spamming to role addresses (e.g. 'foo-admin', 'info@company', etc.) is prohibited. I would guess that if they wind up in the mailbox of a 'natural person' it would be. But this may have to be worked out in court.
  • talks about 'direct marketing'. Does this mean that faked-up 'newsletters' will be a loophole? Also, means that religious and political spam is permitted. But I haven't seen much of that in Ireland... yet...
  • won't be any good against US-based spammers. No surprise there. HOWEVER it may be useful against large multinational companies taking advantage of CAN-SPAM's relaxed regime to indulge in a little spamming, if they have an Irish office.

    And, of course, it'll mean that Ireland won't develop Florida's reputation any time soon, which is a good thing.

  • Will it be useful against spammers in other parts of the EU? That's another question. Anyone know? I know of a bunch in France I'd really like to deal with.

    Brian Nisbet reckons it may.

I was reminded by this letter from the Department of Communications received by UCC , which notes:

But the Minister has announced that he intends using Ireland's Presidency of the EU to initiate global partnership in clamping down on 'spam.'

Global? Just don't ask for any help from the Florida state government. ;)

Spam: Other (big) spam news: 'Gaven Stubberfield' arrested for 'falsifying his identity so that his e-mails could not be traced'. SBL say that Jeremy Jaynes, aka 'Gaven Stubberfield' is the eight-most prolific spammer in the world, and is 'notorious for 'horsey porn' spam'.

Irish: Irish WWW pioneer Peter Flynn now has a weblog, it seems. As far as I can tell, Peter was responsible for much of the good stuff at celt.ucc.ie, which reminds me to post this link to Pangur Bán I've been meaning to post.

Messe ocus Pangur Bán,
cechtar nathar fria saindan:
bíth a menmasam fri seilgg,
mu memna céin im saincheirdd.

In my case, it's mise agus Bubba Liath, otherwise pretty close despite the intervening 11 centuries...

spam ireland law anti-spam data-protection web sms email

Great WashPost article on patents

Patents: The Washington Post gets it. 'The country "needs to revamp not just the patent system, but the entire system of intellectual property law," said Andrew S. Grove, chairman of Intel Corp. "It needs to redefine it for an era that is the information age as compared to the industrial age."'

BTW, one thing people say is that software patents are fine, as long as the technique is novel and new. What that misses is that novel, new techniques quickly become commonplace and standard infrastructure; consider image/audio/video compression, general compression techniques, cryptography, and so on. Those were all high-tech, super-complex schemes 5 years ago. Nowadays, we have JPEG, gzip, openssl, ssh, and all these other standard tools that are just part and parcel of our basic infrastructure. In software, 'new and novel' becomes 'standard infrastructure' remarkably quickly, and that's what's driving software innovation.

swpats patents law software patenting

Now THAT is cool

Software: There's a certain frisson to be had when you find out that your software is running somewhere really cool; I got this when I found out that PLP was being used in McMurdo Base, Antarctica and SpamAssassin as The Well's spam filtering system (SpamAssassin's now even more widely deployed, which is amazing -- but this was the first 'woo!' moment).

However, I think Justin Frankel of WinAmp has got me well beat -- the International Space Station. Bloody hell.

Aside: I wonder if they need a spam filter up there? ;)

Funny: We Love The SCO Information Minister. 'Their assertions are incorrect. The source code is absolutely owned by SCO.'

Spam: 2 South Florida men agree to post $1 million bonds before spamming in future after an FTC bust -- looks like a mortgage-scam spam team. Yay FTC!

The two portrayed themselves as mortgage lenders in unsolicited commercial e-mail, the FTC said, but their 30 Minute Mortgage operation was in fact not a lender and did not offer 30-year loans at 3.95 percent, as advertised.

Instead, the two were interested in getting potential customers to divulge their Social Security numbers, income and other sensitive financial data, which they then tried to sell to others, the FTC charged.

spam anti-spam botnets spamassassin

Samuel L. Jackson's 'Irish' comment

Here's a hot UL that's floating around the irish web right now --

In a British program about Samuel L Jackson and Colin Farrell's lastest movie SWAT presented by British presenter, Kate Thornton, the following exchange occured:

Thornton: What was it like working with Colin (Farrell), cos he is just so hot in the U.K. right now?

Jackson: He's pretty hot in the U.S. too.

Thornton: Yeah, but he is one of our own.

Jackson: Isn't he from Ireland?

Thornton: Yeah, but we can claim him cos Ireland is beside us.

Jackson: You see that's your problem right there. You British keep claiming people that don't belong to you. We had that problem here in America too, it was called slavery.

... yeah, right. ;)

(Update: Actually, believe it or not, that's more or less how it really went. Here's the transcript.)

Some commentary at
TheReggaeBoyz.com (quote: 'I NEARLY DEAD TO RASS!!!!') and Kuro5hin.

It looks like the TV programme does exist; no scripts online, unfortunately, so we'll never figure out if this one really happened, I think.

IMO, it's made up for sure. That last line is just a little too harsh for a primetime schmooze-a-gram, at the very least. Plus, it's the kind of thing only an Irishman would give a shit about -- the perpetual adoption of Irish celebs and worthies by the UK media is a continual source of irritation for the Irish -- as Dervala puts it:

'No, Oscar Wilde was ours. You put him in jail, though. And Shaw was ours. And Yeats. And Johnny Rotten.'

ireland funny history

Spam Surrealism

Spam: Yoz comments on the bizarre new names appearing in spam, linking to a 2lmc spool entry and this entry at rereviewed.com, featuring such beauties as:

  • Inflorescence B. Afghan
  • Petards Q. Blinkers
  • Foobar Economides
  • Hillock H. Fossilized
  • Hotel K. Primate
  • Networked T. Crowley
  • Jitterbug I. Catastrophes
  • Pragmatism O. Playhouses

Me, I'm looking forward to getting spam from Collately Sisters with the international finance arse and Peter O'Hanraha-hanrahan on new Euro-quota rates.

Oh look, I've found some war:

MORRIS: Back live now, progress on The Day Today smart bomb - Jonathan! Get rid of Hurd! Thanks!

(Hurd vanishes from a monitor, replaced by a bomb's eye view of the war zone.)

MAN WITH GLASSES: Well, Chris, as you can see there's the missile, cruising at around 2000 per second trying to locate the target the soldier it's aimed at - there's the soldier, it goes in through the mouth, down through the oesophagus, into the stomach and there's the explosion. (The camera enters the gob of a surprised trooper before the picture turns to static)

MORRIS: Absolutely bang! That's The Day Today bringing you another tear on the face of the world's mother! Alan! Sport!

spam anti-spam weblogs

She's Back

Irish: Sarah Carey's back -- good to see it. Delivering a prime piece of moral outrage regarding malls (or 'shopping centres' as they're quaintly called on the eastern shores), and their intolerance of political speech.

ireland dublin life

Redistributing the Future

Politics: WorldChanging.org on open source: 'we pay a lot of attention to it here, so much so that several worldchangers have asked why. Outside of the realm of computing, they ask, what does collaborative software have to do with changing the world? With sustainability? With democracy? With justice?'

'... as William Gibson reminds us, the future is here, it's just not well-distributed yet. The answer to our problems is not to redistribute wealth, it's to redistribute the future. In very practical terms, that's what the open source (OS) movement is doing.'

Great article -- and great picture from the CSMonitor (copied above) to illustrate it!

open-source software privacy

Warren Ellis on pop

Music: Warren Ellis on pop:

The American music industry ... seems to have sunk into a bizarre obsession with paedophilia. Britney Spears has gone from schoolgirl gear to a deeply strange hentai look, little-girl head stuck above great shiny plastic boobs, singing in a Minnie Mouse voice. No wonder she was being stalked by a shifty-looking middle-aged Japanese bloke. He probably had a suitcase full of tentacles to use on her. Christina Aguilera gifts us with the vision of a twelve-year-old girl in leather chaps and a rubber bra.

He's right, you know... I blame porn-addled middle-aged music biz producers, myself. (Found via the null device.)

mp3 music ireland blogs funny filtering

Warren Ellis on pop

Warren Ellis on pop:

The American music industry ... seems to have sunk into a bizarre obsession with paedophilia. Britney Spears has gone from schoolgirl gear to a deeply strange hentai look, little-girl head stuck above great shiny plastic boobs, singing in a Minnie Mouse voice. No wonder she was being stalked by a shifty-looking middle-aged Japanese bloke. He probably had a suitcase full of tentacles to use on her. Christina Aguilera gifts us with the vision of a twelve-year-old girl in leather chaps and a rubber bra.

He's right, you know... I blame porn-addled middle-aged music biz producers, myself. (Found via the null device.)

mp3 music ireland blogs funny filtering

Kayaking the L.A. River

Environment: (the built one, that is): LA Observed links to a couple of stories about kayaking the grim concrete trench that is the Los Angeles River. Well worth a read, and don't miss the 1999 LA Weekly story, in which the journalist makes it to the sea before being picked up by police.

The LA river was once a real river, but due to its tendency to flash-flood, was turned into a trickle in a concrete trench back in the 1930s. Since then, it's starred in a wide variety of movies and TV; the ones I can remember from the top of my head are Terminator 2, Earthquake, and V (which hilariously stole the river scenes directly from Earthquake, the cheapskates).

BTW, one interesting factor of living in the LA area is that you realise just how much of the TV and film of your childhood is taken directly from these surroundings; last time I was at the local train station, I looked out over a patch of sun-baked scrub and a couple of warehouses, and could clearly see The Six-Million Dollar Man running across it in my mind's eye -- wakka-wakka-wakka.

All along, I'd assumed these great sets were chosen for a particular reason, not just because they were right around the corner from the studio ;)

Talking of my local train station, here's a good article about a very Irvine situation; it seems people keep a second, clunker car at the train station, due to the shortcomings of the Southern California public transit system.

history tv games

MS and Marshall Phelps

Patents: Wonder why MS is just now starting to monetize^W'liberalise' its patent portfolio, starting with a VFAT royalty fee for digital cameras?

Here's a possible reason why -- they've hired Marshall Phelps, from IBM, the executive who began IBM's aggressive patent-based revenue program in 1985.

Microsoft has reached a point, (Eben Moglen) says, where the company can no longer enjoy the same annual revenue growth that it did in the 1990s. Like IBM in the eighties, it's now looking for 'creative' ways to keep the shareholders happy.

CDWow: Anti-IRMA, pro-CDWow leaflet to print out and post somewhere (link via Donncha).

swpats patents patenting

Report on Belgium's Magic 4096 Votes

E-Voting: Very interesting page reproducing a translation of part of an expert report detailing an incident that occurred during an 'electronic election' in Belgium on May 18th 2003.

The latest EDRI-gram notes:

The total number of preferential votes cast on a specific candidate was higher than the total number of votes for his list. A series of tests was conducted on the computer of the president of the voting committee, but the error could not be reproduced. The difference in votes was exactly 4096, leading the research-team to the conclusion that the error was probably due to a spontaneous inversion of a binary position in the read-write memory of the PC.

This serves as a pretty good pointer to how, even if the software is audited to death and pronounced reliable, the hardware can still trip you up. Computers are fundamentally unreliable.

The solution? Why, a Voter-Verifiable Audit Trail of course. ;)

e-voting security elections uk

cdwow.ie

Music: So the current news on the Irish web scene is the Irish Recorded Music Association, Ireland's very own mini-RIAA, attempting to sue cheap CD vendor CDWow.ie out of the Irish market.

CDWow sell CDs cheap, by shipping from Hong Kong. Yes, the price differential between Hong Kong and Europe is so big that even considering the shipping costs, it works out significantly cheaper for the consumer.

The IRMA page on the issue is hilarious, with vague threats of 'credit cards floating through cyberspace' (whatever that means), and comments like: 'Remember every CD Wow purchase is a nail in the coffin of an Irish job', because so much of the bland, multinational, big-music-industry output is produced in Ireland. Suuuure.

Read on at the Boards.IE discussion. 'Doctor J' on that forum notes:

I saw a Ween cd, manufactured in the USA, on sale in HMV for EUR44.99 last night.
  • CD Universe - EUR14.99
  • HMV.co.uk - UKP17.99
  • Tower.co.uk - UKP9.41
  • Are IRMA seriously suggesting it is in the interests of the Irish consumer

    to be ripped off by almost EUR30???

ireland mp3 music copyright

'the exhilarating whoops and pant-hoots of a troop of Rhesus monkeys'

Humour: This year's bad sex prizewinners. I think Rod Liddle deserved it, myself, purely for his comment:

Columnist and former Today programme editor Rod Liddle was almost struck out on the grounds that his sex scenes were actually rather well done, but his novel Too Beautiful for You, ('after a modicum of congenial thrusting, she came with the exhilarating whoops and pant- hoots of a troop of Rhesus monkeys') was reinstated after he said the judges were unqualified, since nobody on the Literary Review had had sex since 1936, in Abyssinia.

news politics google

Self-plagiarised Horoscopes

Funny: Mick @ P45 has a good entry today on plagiarism. He notes that an academic pal once wrote a program to test for plagiarism by his students:

It uses a fairly rough and ready 'brute force' approach. Nonetheless, it can identify significant strings that have been regurgitated from Text A in Text B.

Anyway, he decided just for fun to fire the program at the website's astrology predictions for the previous 18 months or so. The program churned away, and duly spat out the results. And - well heavens above - hadn't the astrologer been copying and pasting very large chunks of his own predictions, apparently at random and nothing to do with 'Uranus being in the ascendent' or other such drivel that horoscopes concern themselves with.

copyright plagiarism writing

Seldom-Asked Questions About Japan

Japan: This is fantastic; full of odd little facts about Japan. Here's one I really like:

  1. '(How do you explain) the frequency of Japanese people (usually women) running or jogging for no apparent reason. In the travel agency, 'let me get you a copy' and she runs away. In my office a woman runs to the bathroom (can be explained) and then runs back to her desk (huh?). Most of the teachers I work with wait for the bell in the teacher's room, and then practically sprint to their classes. Do you know why all this running is going on? Fitness? Service? An Edo-era leftover?'--Question submitted by Ben Schwartz
  2. I once teasingly asked a female with whom I worked why she always did a sort of feigned jog to and from the copier, especially since her jog was slower than her walk. The humour wasn't lost on her, but she explained that many Japanese do this at work because the appearance of urgency is important in more traditional office environments. You don't have to truly run around frantically, but just offer the gesture.--Answer kindly submitted by Lou C.

Another good one -- it seems Bob the Builder had to have a finger added for the Japanese market, in order to not look like a yakuza.

japan funny business work

Seldom-Asked Questions About Japan

This is fantastic; full of odd little facts about Japan. Here's one I really like:

  1. '(How do you explain) the frequency of Japanese people (usually women) running or jogging for no apparent reason. In the travel agency, 'let me get you a copy' and she runs away. In my office a woman runs to the bathroom (can be explained) and then runs back to her desk (huh?). Most of the teachers I work with wait for the bell in the teacher's room, and then practically sprint to their classes. Do you know why all this running is going on? Fitness? Service? An Edo-era leftover?'--Question submitted by Ben Schwartz
  2. I once teasingly asked a female with whom I worked why she always did a sort of feigned jog to and from the copier, especially since her jog was slower than her walk. The humour wasn't lost on her, but she explained that many Japanese do this at work because the appearance of urgency is important in more traditional office environments. You don't have to truly run around frantically, but just offer the gesture.--Answer kindly submitted by Lou C.

Another good one -- it seems Bob the Builder had to have a finger added for the Japanese market, in order to not look like a yakuza.

japan work funny business

Canadian Pharmacy FUD debunked

Health: Canadian Pharmacy FUD debunked: ''After nearly a year of sharp warnings about the dangers of prescription drugs from Canada,' the Philadelphia Inquirer reports, 'U.S. Food and Drug Administration officials cannot produce a single U.S. consumer who was killed or injured by inferior medications from Canada.' Neither can its Canadian counterpart.'

health ip patents

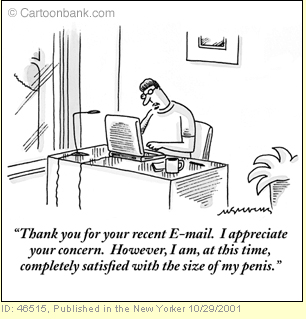
Potentially objectionable xscreensaver

Humour: xscreensaver, the default (and greatest) screensaver on most free UNIX distros, may contain R-rated content, as this mail to the Fedora discussion list notes.

Much to my surprise, I stumbled across it drawing an 'erect penis' when I returned from lunch today. So I did some investigating:

    $ strings /usr/X11R6/lib/xscreensaver/glsnake | grep penis
    erect penis
    flaccid penis
  

graphics history censorship

Potentially objectionable xscreensaver

xscreensaver, the default (and greatest) screensaver on most free UNIX distros, may contain R-rated content, as this mail to the Fedora discussion list notes.

Much to my surprise, I stumbled across it drawing an 'erect penis' when I returned from lunch today. So I did some investigating:

$ strings /usr/X11R6/lib/xscreensaver/glsnake | grep penis
erect penis
flaccid penis

-----BEGIN PGP SIGNED MESSAGE-----
Hash: SHA1

Date: Tue, 02 Dec 2003 13:45:35 -0500
From: Sean Millichamp ...
To: ...
Subject: Potentially objectionable xscreensaver module (GLSnake)

I just wanted to let everyone know that the xscreensaver module "GLSnake" has two object displays that some folks might feel is inappropriate or objectionable.

Much to my surprise, I stumbled across it drawing an "erect penis" when I returned from lunch today. So I did some investigating:

$ strings /usr/X11R6/lib/xscreensaver/glsnake | grep penis erect penis
flaccid penis

$ rpm -q xscreensaver
xscreensaver-4.14-2

Some folks who are planning on (or have) installed Fedora Core at home or in conservative office settings might want to check and make sure glsnake isn't enabled by default.

If I end up deploying Fedora Core 1 to any desktops at my clients I will clearly have to sanitize or remove this module in some fashion.

I hope that the heads-up helps someone...

Sean

  • --


fedora-list mailing list
...
To unsubscribe: http://www.redhat.com/mailman/listinfo/fedora-list

-----BEGIN PGP SIGNATURE-----
Version: GnuPG v1.2.2 (GNU/Linux)
Comment: Exmh CVS

iD8DBQE/zOjlQTcbUG5Y7woRAmsPAKCgQyfMtjwzMLFI/+6AOGMiorpd+wCgiBj9 pK/I94s4fgzbtKdSIraWgKM=
=gIci
-----END PGP SIGNATURE-----

history security uk censorship filtering politics ireland

Using Bugzilla for commercial code

Software: How Funcom Squashed Bugs With Bugzilla (GamaSutra, free reg required).

There's some differences between the commercial and free-software development styles; writing games is probably one of the most extreme of the commercial development environments, with extremely aggressive schedules and a single, long-term product development arc building up to one really big release.

A really good way to use bugzilla is to track development -- essentially, using it to track work instead of bugs. In other words, when work is planned, a bug is created to track that work's progress and provide a forum for discussion of the work's design, implementation details, etc.

This article gives a great overview of the additions Funcom have made to Bugzilla to do this, including time estimates, MS Project integration.

bugs coding open-source

Post-Thanksgiving bits

Quickies: I like Thanksgiving! A holiday based around a roast fowl and some booze; can't go too far wrong with that. Thumbs up.

FrodoPalm -- run C=64 games on your Palm handheld. Insanely cool. (via /.) I wonder what the controls are like, though -- that can totally kill a game's playability.

Escape From Woomera -- nice press-grabbing idea, but I can't imagine that the game will be too hot, though. (via Boing Boing)

The Bearer of This Card is a Genuine and Authorized Tsar, via Blather Shitegeist.

ABC.net.au: push for 'open source' biotech. I was just thinking about this last week; interesting to see this happening.

'Biotechnology, the way it is right now, is needed in the developing world like a screen door on a submarine,' said Jefferson. 'What it really needs is what good science can do in biology, in biotechnology. And that means a different agenda and a different group of innovators.'

'He added such tools could also help us understand and improve agricultural management systems such as organic approaches. An example of this would be the development of new 'bioindicator' plant varieties that would tell farmers about their soil nitrogen levels.'

Fantastic idea. I hope this takes off...

science open-source papers

'Nepalese Nose-Leech' hits the Beeb

Health: via Forteana, BBC: Invasion of the Bodysnatchers. It seems the Beeb is producing a new TV series about parasites, and the PR blitz starts here (and also in The Sun).

Interestingly, halfway through the BBC article, there's this:

Soon after travel writer, Broughton Coburn, returned from Nepal he began to experience regular, inexplicable nosebleeds. They continued for three weeks until an embarrassing encounter in a teashop made him realise that something was seriously wrong.

As he was being served, the waiter took one look at him and fled in horror. Broughton chased him down the street urging him to tell him what was wrong. But the boy would only point, wordlessly, at his nose.

Broughton returned home and sat in trepidation in front of a mirror. His patience was rewarded when a brown worm-like creature emerged from his right nostril and looked around.

'I swear it had two beady eyes on it. And it came out two or three inches, looked around and then retracted. I thought it was a dream, a vision of some sort.'

In shock, Broughton rushed off to his doctor who tried to remove the mysterious creature. But it wasn't going to give up its home easily.

'He had this thing pulled out eight or ten inches and I'm looking at it cross-eyed down the end of my nose, and he's looking at it, he has a look of absolute horror on his face. And the thing came off. And there was this leech.'

This is the same story (modulo minor differences) as this oft-posted story, 'A True Story from the Himalayas', which is captioned

This is a supposedly true story I received from an associate. I have no additional evidence as to its veracity but it makes a good tale. -- Editor'.

No better way to announce an urban legend!

So is the Beeb printing a UL? Or did an author called Broughton Coburn really pick up a nose-leech in Nepal shortly after arriving with the Peace Corps, and before becoming a successful travel writer? It could be, I suppose...

Update: it's looking more and more likely, given:

This Hong Kong Medical Journal report on the removal of a large leech from a woman's nose:

The woman said that one month before her symptoms developed, she swam and washed her face in a stream while hiking. Doctors checked other members of her hiking group and found another leech in the nose of a man who washed his face in the stream, the journal said.

And this NY Times interview with a leech researcher, who notes:

"There are all sorts of things out there like Dinobdella ferox, which means the terrifying and ferocious leech," Dr. Siddall said. "It lives in eastern Bengal, and it will literally crawl up your nose and lodge in the back of your throat."

Back to the Broughton Coburn account. An Amazon reviewer comment notes that this story appeared in Travelers' Tales Nepal, a book by Rajenda S. Khadka. In addition, Broughton Coburn has a website nowadays, so someone could always ask! Finally, this copy of the full account has some more research.

While on the subject of Nepal, here's an incredible cautionary tale -- don't do the non-tourist treks in Nepal without a guide, if you value your life:

A wall of furiously churning brown water was racing toward us. Behind it the lodge by the river where we had lunch an hour earlier was disintegrating. The water level had increased another ten feet and was annihilating everything in its path.

yikes. Lots more great travel stories, including almost swimming in shit, diarrhoea in a west African minefield, and strangling muggers in Peru on that site, BTW. And he can write!

Ireland: Knick Knack Paddy Hack -- 'Paul Clerkin and Mick Cunningham explain how their crazy-ass website p45.net suckered the (Irish) media.'

nature papers wildlife

Giant Mekong catfish becoming extinct

Environment: Long-time taint.org readers (yeah, right) may recall last year's encounter with the pla beuk, the Mekong giant catfish. (hey, it made for a good story in the end!)

Well, it seems the pla beuk now listed as 'critically endangered'. 2Bangkok points to this Yahoo! story:

More data, including Hogan's, have shown that its numbers fell by at least 80 percent over the last 13 years, a 'pretty massive decline' that prompted the critically endangered classification in the group's latest list released Nov. 18, Pollock said.

It seems recent dam-building and dredging may be to blame:

The river had mostly remained isolated due to wars and geography, but dams recently built along it in China and work on the upper Mekong River to clear navigation channels for large boats are threatening the catfish and other species, said Chainarong Sretthachau, director of the Southeast Asia Rivers Network.

animals environment thailand

Great article on e-voting issues

E-Voting: Do not miss this fantastic round-up on the e-voting situation in the US. It contains these amazing quotes from the leaked Diebold memos:

''Over (the past three years) I have become increasingly concerned about the apparent lack of concern over the practice of writing contracts to provide products and services which do not exist and then attempting to build these items on an unreasonable timetable with no written plan, little to no time for testing, and minimal resources. It also seems to be an accepted practice to exaggerate our progress and functionality to our customers and ourselves then make excuses at delivery time when these products and services do not meet expectations.' (Source: 'Resignation', announce.w3archive/200110/msg00001.html, dated 5 October 2001)

'It does not matter whether we get anything certified or not, if we can't even get the foundation of Global stable. This company is a mess! We should stop development on all new, and old products and concentrate on making them stable instead of showing vaporware. Selling a new account will only load more crap on an already over burdened entity. ... You are taxing the development team beyond what they can handle. ... Why is it so hard to get things right! I have never been at any other company that has been so miss managed (sic).' (Source: 'Fw: Battery Status & Charging---and too much bull!!', announce.w3archive/200110/msg00002.html, dated 20 October 2001)'

I'm speechless. At least the NEDAP system planned for Ireland isn't this bad -- or is it? We can't tell.

Support the calls for a Voter-Verifiable Paper Audit Trail. There's no other way to continue to have a trustworthy democratic system with widespread use of e-voting in place.

eu ireland banking

Debunking Offshore Spam

Spam: Since the CAN-SPAM act passed Congress, there's been quite a few comments raised against it -- unsurprising, as it does still have quite a few shortcomings.

However, one of the negative comments needs to be debunked -- namely the old favourite, 'most spam comes from countries outside the US'. In April, Declan McCullagh even quoted the CTO of Brightmail to this effect.

This is not true.

What's happening here is that it appears a lot of spam is coming via non-US servers, if do simplistic analysis of the IP addresses that are connecting to your mail servers. But look a little deeper -- some testing will reveal that those IPs are compromised hosts, running proxies or trojans to relay spam from their genuine origin.

Capturing relays in foreign countries is good sense for a spammer, because the network-abuse staff of a foreign ISP will be slower to react to complaints if they don't speak the complainant's language; in addition, some offshore ISPs seem to tolerate much more than US/European ISPs would. For example, in a few cases, US-based spammers are installing servers in offshore colocation facilities to operate their spam runs, and generally getting away with it -- much more than they would in the US or Europe. In some cases, there's serious abuse occurring -- here's a ROKSO report indicating Chinese servers being used to operate a massive SMTP AUTH username/password cracking operation against hosts across the world.

Once you get beyond these origin-obfuscation methods, and follow the spam to the source (which is hard work BTW!), you find yourself back in the US. The Spamhaus.org front page 'top 10 worst spam countries' list still features the US at number 1.

Now, what about if a spam law passes, and the spammers do move offshore?

I would say that a good 80% of the spamming population will, after a few prosecutions, find themselves unwilling to leave their home country and move to a foreign place in order to continue spamming. After all, wholesale relocation to a foreign society is hard work. So IMO, they'll move on to other pursuits and leave the email spam racket.

However, it is possible that the most motivated spammers themselves will pack up their bags and physically leave the US. This is where concentrating on the spam bureaus themselves becomes a dead end, and concentrating on their customers, the companies using the bureaus, is useful. Read the CAUCE FAQ:

Because most spam advertises goods or services offered by US-based entities (for example, get-rich-quick schemes and quack medical remedies being sold out of someone's basement), we advocate anti-spam laws in which the focus is not where the email came from but on whose behalf the spam was sent. If the law applies to the advertiser -- the entity profiting from the activity -- it doesn't matter where the spam originates.

The FAQ also raises this very good point:

Second, the reach of US law outside the borders of the US is tenuous at best, however that fact does not negate the need for or effectiveness of laws against those in the US. It can be very difficult to bring a murderer to justice in the US if they escape abroad, but no one could seriously argue that this fact means domestic murder laws are unnecessary or irrelevent. Spam isn't comparable to murder, but if our judicial system means anything, the same principles of justice must apply.

Dead right.

spam anti-spam filtering

New Federal Anti-Spam Law Passed

Spam: Federal Anti-Spam Law Passes Congress (Anne Mitchell):

This source also said that the bill in its ultimate (and by now presumably passed) version was significantly tighter and more pro-consumer than the version which passed the senate and went to the house earlier this month. That's good. On the other hand, it still doesn't go nearly as far as the CA law did in many ways.

Still, one must be pragmatic - it doesn't really matter if it's better or worse than the CA law, right now, because it is (will be) the law. If we have to have a Federal law, and if it has to pre-empt the states, then this one at least has some positive aspects to it.

spam anti-spam filtering

New Federal Anti-Spam Law Passed

Federal Anti-Spam Law Passes Congress (Anne Mitchell):

This source also said that the bill in its ultimate (and by now presumably passed) version was significantly tighter and more pro-consumer than the version which passed the senate and went to the house earlier this month. That's good. On the other hand, it still doesn't go nearly as far as the CA law did in many ways.

Still, one must be pragmatic - it doesn't really matter if it's better or worse than the CA law, right now, because it is (will be) the law. If we have to have a Federal law, and if it has to pre-empt the states, then this one at least has some positive aspects to it.

spam anti-spam filtering

Small arms and radioactive waste

Politics: Hey, Sarge, Why Are They Shooting At Us with American Guns? (Three-Toed Sloth).

An interesting article, with one central thesis that had never occurred to me before; why should exports of guns, automatic weapons, and landmines be as free and easy as they are now?

In recent weeks, small arms have brought down several U.S. helicopters in Iraq, killing dozens of soldiers. Given the historically unprecedented military strength of the American armed forces, it doesn't make a whole lot of sense to be flooding the world with weapons that could someday be used in guerilla warfare -- arguably the only kind of war that an enemy can successfully wage against the U.S. military.

Sanchez cited Afghanistan as a perfect example of this phenomenon. 'No sale of weapons is ever completely safe,' he said, 'as yesterday's allies become today's terrorists.'

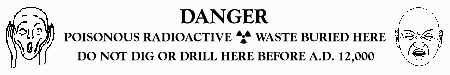
Environment: excerpts from Markers to Deter Inadvertent Human Intrusion into the Waste Isolation Pilot Plant (via NTK). Eek! Check this out...

ireland security terrorism

XmlStarlet, and lots of stuff

XML: XmlStarlet: 'a set of command line utilities (tools) which can be used to transform, query, validate, and edit XML documents and files using simple set of shell commands in similar way it is done for plain text files using UNIX grep, sed, awk, diff, patch, join, etc commands.' Sheer genius!

SCOvEveryone: Humorix: 'PROVO, UTAH -- Nearly two hundred humor writers, fake news reporters, and tongue-in-cheek columnists descended on SCO's headquarters yesterday to protest the company's continued slide into unreality.'

'Humor writers have very active imagination. But none of us -- absolutely none of us -- could ever have imagined the kind of ludicrous and inconceivable things that SCO has decided to pursue,' explained a reporter for the New York Times, the world's leading source of spurious news. 'You simply can't make this stuff up... a fact which represents a great hardship on humorists everywhere.'

(thanks Ben!)

Ireland: some beautiful pics of Dublin in Autumn from Diego Doval.

Books: Hari Kunzru rejects the John Llewellyn Rhys award, since it is sponsored by two notoriously anti-immigrant newspapers, the Daily Mail and the Mail on Sunday:

both 'pursue an editorial policy of vilifying and demonising refugees and asylum-seekers ... As the child of an immigrant, I am only too aware of the poisonous effect of the Mail's editorial line. The atmosphere of prejudice it fosters translates into violence, and I have no wish to profit from it. ... The Impressionist is a novel about the absurdity of a world in which race is the main determinant of a person's identity. My hope is that one day the sponsors of the John Llewellyn Rhys prize will join with the judges in appreciating this.'

Well said! (via Oblomovka)

Health: University of Chicago healthcare 'stories of shame'. A shockingly widespread situation in the US, as far as I can tell. For non-USians wondering what all the fuss is about, have a read of this and it'll become clear. At the same time, the US government spends more per capita on healthcare than Sweden does. Figure that one out...

python ireland amazon

Orwell on Tea

Drink: George Orwell: A Nice Cup of Tea (Evening Standard, 12 January 1946)

If you look up 'tea' in the first cookery book that comes to hand you will probably find that it is unmentioned; or at most you will find a few lines of sketchy instructions which give no ruling on several of the most important points. This is curious, not only because tea is one of the main stays of civilization in this country, as well as in Eire, Australia and New Zealand, but because the best manner of making it is the subject of violent disputes.

(thanks Leon!)

ireland funny history

Power failure -- Unix v Windows war as usual

OSes: /.: NERC Releases Interim Report on Aug 14th Blackout. 'part of the blame for the big fizzle of 2003 lies with a failing SCADA system, GE's XA/21 power management system. 'Not only did the software that controls audible and visual alarms stop working at 2:14 p.m. EDT, but about a half hour later, two servers supporting the emergency system failed, too.' According to the product specs, it is a Unix system with X Windows.''

However, further reading through the comments throws up this gem, which notes that the 'software that controls audible and visual alarms' and the 'two servers' noted above were all Windows systems. The comment author ties this to Blaster worm activity causing DDOSes on the monitoring networks.

Interesting!

security linux coding

DVDRentals.ie, and a Russian 'The Running Man'

Ireland: A while back, I posted 'Room for an Irish Netflix', which plugged the idea of opening a version of the Netflix concept for Ireland. Well, over on the taint.org QT forum, JCorbett says: ' DVDRentals.ie is what you're looking for!'

Sure enough, it looks pretty good -- 20 eurons a month, and a reasonable selection (considering they just started).

But it limits how many DVDs you can get out in a month to 8. IMO, that's unnecessary -- nobody can watch DVDs and turn them around through the postal system that quickly!

Also, the browsing interface is lousy -- I'd suggest licensing some kind of metadata from IMDb or similar, so people can get third-party reviews, comments, 'my favourite action movie' lists, that kind of thing.

Can't tell much more, as the FAQ page doesn't work on Mozilla/Firebird for some damn reason.

Sick: Anger as contestants hungry for money go begging on TV (Irish Indo) (via forteana):

A reality television show in which 12 young Russian contestants have to scrounge, beg and even steal to win a pension for life, is being filmed in Berlin.

In a city already struggling with bankruptcy and large numbers of asylum-seekers, police and residents have been quick to condemn Golod, Russian for 'hunger'. The contestants live in a container without money or food to survive; none of them speaks German. 'Golod' is proving a huge hit with Moscow television viewers, thousands of whom tune in at nine each evening to find out how Karina, Anastasia and 10 other photogenic contestants are faring on the mean streets of a foreign city.

Spam: Latest Pew Internet report on spam. Pew Internet surveys are very good. This one notes that '25% of America's email users say they are using email less because of spam. Within that group, most say that spam has reduced their overall use of email in a big way.'

Mafia: A mafia hacker tells his story to Wired (Simson Garfinkel via FoRK).

ireland video netflix

Terriblismophile

Green: WorldChanging.com brings a new word:

The Renaissance Italians had a term, 'terriblisma,' by which they meant the strange, gratified awe one feels when beholding dreadful disasters and acts of God from afar. The term may be six hundred years old, but the sentiment could not be more contemporary. In fact, terriblisma is a quite native 21st Century aesthetic.

So there it is -- I'm a terriblismophile. (That's probably not a valid word, combining Italian and Greek, but hey...) Judging by this entry, marathon-running blogger Maciej Ceglowski may just be one too.

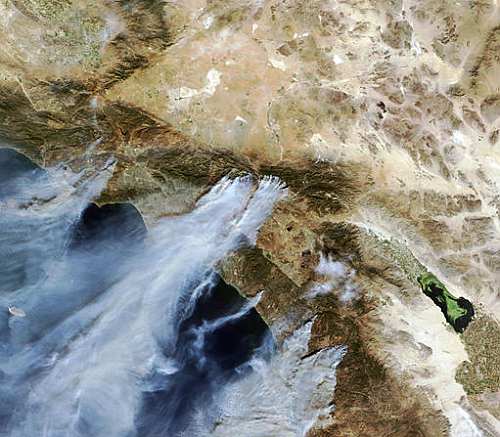
One of the things on my to-do list has been to see a live volcano; still haven't managed it yet. Then, possibly, a tornado. I've also been meaning to type in and post a couple of snippets from Mike Davis' Ecology of Fear (and judging from that book, a tornado in SoCal may not be out of the question). Also, the surreality of the wild fires was pretty enjoyable from my comfy well-out-of-danger's-way vantage point. No question -- I'm a terriblismophile.

disasters environment bizarre

How to link without PageRank

Spam: Given the latest spammer trick, clone blogs, there's been some discussion of how one can link to another site, without actually conferring Google PageRank to them.

Here's a good way -- instead of using the traditional href:

    link

use a Javascript link, like so:

    link

This works, as long as the viewer uses Javascript, and it won't be handled by Google as giving PageRank points. Perfect for use in referrer log listings, for example.

web google spam

The blues lives

Music: Delta Force (The Observer) -- you couldn't make this up:

'I ask T-Model if I can hear him play. 'Let's go,' he says and we get into his big blue 1979 Lincoln Continental and drive across the railroad tracks to a corner house in a part of Water Valley I have never seen before. An old man with one eye and no teeth is in a wheelchair on a rotting front porch, trying to attach a prosthetic leg to his stump.

'Hey Pete!' yells T-Model. 'Y'all got any elec-quickery up in there? We fixin' to play a little music.' 'Hey bluesman, you come on. We got electric,' says Pete and then his leg falls off with a clatter. 'I ain't never gonna get used to this damn fool leg.'

music usa funny

A question for the Florida DMA

Spam: DMA meeting to address spam (South Florida Biz Journal):

The DMA recently announced its support for e-mail self-regulatory guidelines, including:

.... 4. Marketers should not acquire e-mail addresses surreptitiously through automated mechanisms without the consumer/customer's informed consent.

So, my question is: how exactly does a consumer provide 'informed consent' to having their e-mail addresses acquired 'surreptitiously through automated mechanisms'?

spam anti-spam email privacy law security

Various Monday Morning quickies

Anthems: The Chechen Nation Anthem. This has got to be the scariest anthem I've ever heard, what with the she-wolves whelping and what not.

Spam: MAPILab.com: Microsoft Outlook 2003 Spam Filter: Under the hood. Exhaustive!

Wired News: U.K. Plans to Extradite Spammers. Can't see how this'll work, given that spamming just isn't seen by prosecutors as a high-cost crime. (Found via SpammerHunters.com).

Food: Blooper proves bum deal for Sharwoods (Guardian): 'When Sharwoods launched its latest product range earlier this month, it promised the 'deliciously rich' sauces based on a traditional northern Indian method of cooking would 'change the way consumers make curry'. What it failed to foresee was that 'bundh' in Punjabi has an altogether less savoury meaning

  • the nearest English translation being, to put it bluntly, 'arse'.'

(Thanks Lean!)

Plus, a bonus: a brief history of advertising mistranslations, some doubtless ULs.

Patents: MS Office 2003 XML Reference Schema Patent License (via patents at aful dot org):

Microsoft may have patents and/or patent applications that are necessary for you to license in order to make, sell, or distribute software programs that read or write files that comply with the Microsoft specifications for the Office Schemas.

ireland food funny security google gaming uk law

Audio Lunchbox

Music: Audio Lunchbox -- let's just quote the key parts of the FAQ:

  • Audio Lunchbox is the premiere digital download destination for the best new independent music.
  • ALL of the music on Audio Lunchbox is DRM-free. There are no technology imposed usage restrictions on the files you download. You can listen to the files you download however you like as long as it's for your own personal use.
  • Every track on Audio Lunchbox is available in two formats: MP3 and Ogg Vorbis.
  • Browsers known to work with our service include Internet Explorer, Netscape, Mozilla, Opera, Safari, Galeon, Epiphany and Konqueror.
  • Anyone in the world can download tracks from us.

Good answers!

The music isn't quite there yet -- all I can find is current LA favourites, Death Cab for Cutie, but I can wait. For now, it'll go alongside Epitonic as a good source of decent MP3s; and I hope the selection builds up well...

music drm mp3 linux

WorldChanging.com

Environment: WorldChanging.com. Bruce Sterling writes:

'Worldchanging' is very much the same work the Viridian movement has been doing since 1998, only now (thanks God!) it's being done by a relatively organized team of capable activists instead of by some wacky novelist in his spare time! So go make them famous. Do it now.'

The Viridian movement is Bruce's baby, best summed up, I reckon, as 'electronic green'.

Anyway, WorldChanging.com is a full-blown MovableType weblog, RDF and all, frequently updated and smartly written. Sign up!

ireland climate-change politics

The Next Thing After the Hummer

Vehicles: Gulf War Vehicles Hit L.A. Freeways (LALA Times):

'The Humvee ambulance is to the SUV what the standard Humvee was to the jeep. The taller canopy allows for an entire extended family of 8-10 persons to sit comfortably. So it conserves energy even if it gets just under 6 miles per gallon. As with the Humvee, bottled bubbly water fits snugly in the racks on the back of the vehicle. Beach blankets and umbrellas can also be attached to the vehicle's shell for easy extraction and use.

The Abrams' hybrid tank weighs in at a sturdy three tons and gets just over two miles per gallon. The treads have been scaled back, the barrel has been removed and the turret has been smoothed out. The front window has been expanded and the plexi-glass top hatch doubles as a door and sun roof. Crash tests show the Abrams to be first-rate.'

Related:
New Humvee Spans Two Lanes of Traffic
.

funny driving energy

On Copy Protection and DRM

Security: Dan Bricklin writes:

As I pointed out in 'Copy Protection Robs The Future', the only reason I have a copy (of VisiCalc) that can still work is that someone kept a 'bootleg' uncopyprotected copy around. The original disks may not have worked on a Longhorn machine. Just copying the files from the original 5 1/4" floppy to a 3 1/2" one that would fit in today's machines certainly would result in a non-working copy, because of copy protection. We will regret 'Digital Restriction/Rights Management' in the future.

Here's the essay he mentions: Copy Protection Robs The Future:

Copy protection, like poor environment and chemical instability before it for books and works of art, looks to be a major impediment to preserving our cultural heritage. Works that are copy protected are less likely to survive into the future. The formal and informal world of archivists and preservers will be unable to do their job of moving what they keep from one media to another newer one, nor will they be able to ensure survival and appreciation through wide dissemination, even when it is legal to do so.

Tying in nicely with The Long Now Foundation and the importance of the public domain.

copyright piracy law history

MS loses to Linux in Thailand

Linux: MS loses to Linux in Thailand Struggle (LinuxInsider):

The people's PC project, formally known as the ICT PC Project, revolutionized the Thai PC market, and its effect is being felt around the region. The Ministry of ICT aims to sell 700,000 PCs and 300,000 notebooks in the first year of the project. To make the PCs affordable, the government has insisted that computer makers offer the machines at fire-sale prices -- $250 for PCs and $400 for notebooks, including the software.

The government did invite Microsoft to participate in the project, but the company initially refused to lower its prices. Microsoft has a long-standing policy of charging the same prices throughout the world, which could help explain the widespread piracy in developing markets like Thailand, where the average annual income is about $7,000. Charging Thai consumers nearly $600 for Windows/Office is the equivalent of charging U.S. consumers $3,000.

... Microsoft's newly appointed regional general manager, Andrew McBean, no doubt having consulted Redmond, offered to supply the ICT PC Program with the Windows/Office package for a mere $37 -- a price cut of 85 percent.

Looks like the Linux-based machines are popular, too:

The rock-bottom prices -- and easy financing terms -- generated enormous interest in the ICT PCs. An estimated 35,000 people showed up at a Bangkok convention center where the machines were launched. Some people even camped overnight to sign up for the program. By August of this year, Thai consumers had snapped up 300,000 ICT PCs.

aws hardware amazon

Guinness IS good for you, again

Beer: Irish Independent: Now ads can't say it but you always knew it -- Guinness IS
good for you
:

One pint of Guinness a day can reduce the risk of blood clots that cause heart attacks, according to new research presented at the annual meeting of the American Heart Association in Orlando, Florida.

... Scientists investigating the health benefits of drinking beer found that stouts like Guinness worked much better than lager. They said dark beers were packed with anti-oxidant compounds called flavonoids which help reduce damage to the lining of the arteries. ... For maximum benefit a person would need to drink just over one pint of Guinness a day.

My grandfather was 'prescribed' a bottle of Guinness per day by his GP, to lower cholesterol and blood pressure. Mind you, that was in '70s Ireland ;)

dublin guinness ireland history funny

(Don't) Give Peas A Chance

History: This year's archives are open, revealing lots of goodies from WWII. Here's a good one via the BBC: 1940 'peas bomb plot' on palace:

German saboteurs claimed they were planning to attack wartime Britain using exploding cans of processed peas, according to secret files. The MI5 documents show that three men who landed on the southern coast of Ireland in 1940 were found with four bombs hidden inside cans labelled 'French peas'.

.... The three agents were landed by dinghy near Cork, but their exploits were shortlived. Their tactic, of asking the first person they met if they could be taken to the IRA, did not work.

The man took them to the police instead.

... The files show a close relationship between the Irish and British authorites, despite Irish neutrality. MI5 knew of the arrests and saw transcripts of the interrogations almost immediately.

ireland history dublin food politics

Perforce and Half-Life - together at last!

Software: I'm a huge fan of Perforce, the best SCM system I've ever used; it thoroughly kicks the ass of ClearCase, CVS, RCS et al.

I'm also a fan of Half-Life, one of the few first-person-shooter games on the PC platform to provide a reasonably good plotline.

However, until now, they've remained separate; how do you reconcile source-code management and blasting alien invaders? Presenting P4HL:

Does SCM ever start to seem flat and two-dimensional? Have you ever felt the urge to browse depot history while beating up on your friends with a crowbar? Then check out P4HL, a fully 3D depot browsing interface built on the Half-Life engine.

graphs open-source linux

Guinness IS good for you, again

Irish Independent: Now ads can't say it but you always knew it -- Guinness IS
good for you
:

One pint of Guinness a day can reduce the risk of blood clots that cause heart attacks, according to new research presented at the annual meeting of the American Heart Association in Orlando, Florida.

... Scientists investigating the health benefits of drinking beer found that stouts like Guinness worked much better than lager. They said dark beers were packed with anti-oxidant compounds called flavonoids which help reduce damage to the lining of the arteries. ... For maximum benefit a person would need to drink just over one pint of Guinness a day.

My grandfather was 'prescribed' a bottle of Guinness per day by his GP, to lower cholesterol and blood pressure. Mind you, that was in '70s Ireland ;)

dublin guinness history ireland funny algorithms

Exploding Monitors pt. II

Hardware: This weblog is jinxed!!

That's the only explanation I can come up with. The day before yesterday, I blogged about exploding monitors and various halt-and-catch-fire software instructions. Last night, my monitor made a popping noise, emitted a faint burning-plastic smell, and shrank the display into a thin stripe down the middle of the screen.

Great. It's dead as a doornail -- I'm working from Catherine's iBook for now. Quite a step down from the lovely 21-inch CRT. Argh :(

BTW, needless to say, I wasn't running any scary apps -- not even Freedom: First Resistance -- the only possible display-hosing culprits were Firebird, KDE, ExMH or gvim ;)

hardware software web

SCO madness continues

SCOvEveryone: I haven't a clue what's going on here:

... SCO would probably provide customers with financial incentives and discounts to migrate to SCO Unix, other vendors' Unix, and what he referred to as 'other proprietary operating systems' but probably Windows.

open-source malware software linux

SCO madness continues

I haven't a clue what's going on here:

... SCO would probably provide customers with financial incentives and discounts to migrate to SCO Unix, other vendors' Unix, and what he referred to as 'other proprietary operating systems' but probably Windows.

open-source software malware linux

Shock Horror -- Do-Not-Call's Gaping Loophole Exploited

Spam: So in the past 2 weeks, I've been called 3 times to 'take part in a survey'. That's compared to prior history before the do-not-call law took effect, which was absolutely no survey calls before on this number -- but plenty of telemarketing calls.

Of course, I'm sure these surveys are all companies keen to get my considered opinion, rather than phone-spam scum exploiting one of the blindingly obvious loopholes in the federal do-not-call list legislation. Sure.

BTW, that loophole seems to be there due to an oversight issue -- it seems the FTC doesn't have jurisdiction over telephone surveyors. However, this page notes that the FTC staff are prepared to prosecute callers who attempt to subvert the act:

For example, if a survey call asks a consumer if he or she would be interested in purchasing a type of service or merchandise, and that information then is used to contact the consumer to encourage such purchases, the survey call is considered telemarketing and subject to the Do Not Call restrictions.

Which is all well and good, but I'm not going to hang around for 10 minutes of 'what long-distance company do you use?' in order to differentiate 'good' surveys from 'bad' ones; I'll just hang up straight away.

Sport: Ben forwards this story -- the US baseball team has failed to qualify for the next Olympics. Yes, baseball. And no, I didn't know that other countries had genuine baseball teams.

spam privacy anti-spam data-protection law

Shock Horror -- Do-Not-Call's Gaping Loophole Exploited

So in the past 2 weeks, I've been called 3 times to 'take part in a survey'. That's compared to prior history before the do-not-call law took effect, which was absolutely no survey calls before on this number -- but plenty of telemarketing calls.

Of course, I'm sure these surveys are all companies keen to get my considered opinion, rather than phone-spam scum exploiting one of the blindingly obvious loopholes in the federal do-not-call list legislation. Sure.

BTW, that loophole seems to be there due to an oversight issue -- it seems the FTC doesn't have jurisdiction over telephone surveyors. However, this page notes that the FTC staff are prepared to prosecute callers who attempt to subvert the act:

For example, if a survey call asks a consumer if he or she would be interested in purchasing a type of service or merchandise, and that information then is used to contact the consumer to encourage such purchases, the survey call is considered telemarketing and subject to the Do Not Call restrictions.

Which is all well and good, but I'm not going to hang around for 10 minutes of 'what long-distance company do you use?' in order to differentiate 'good' surveys from 'bad' ones; I'll just hang up straight away.

Sport: Ben forwards this story -- the US baseball team has failed to qualify for the next Olympics. Yes, baseball. And no, I didn't know that other countries had genuine baseball teams.

law spam privacy uk

Clay Shirky on Complex Software Systems

Software: Shirky on the Semantic Web. Great snippet:

it turns out that people can share data without having to share a worldview, so we got the meta-data without needing the ontology. Exhibit A in this regard is the weblog world. In a recent paper discussing the Semantic Web and weblogs, Matt Rothenberg details the invention and rapid spread of 'RSS autodiscovery', where an existing HTML tag was pressed into service as a way of automatically pointing to a weblog's syndication feed.

About this process, which went from suggestion to implementation in mere days, Rothenberg says:

Granted, RSS autodiscovery was a relatively simplistic technical standard compared to the types of standards required for the environment of pervasive meta-data stipulated by the semantic web, but its adoption demonstrates an environment in which new technical standards for publishing can go from prototype to widespread utility extremely quickly. ...

This, of course, is the standard Hail Mary play for anyone whose

technology is caught on the wrong side of complexity. People pushing such technologies often make the 'gateway drug' claim that rapid adoption of simple technologies is a precursor to later adoption of much more complex ones. Lotus claimed that simple internet email would eventually leave people clamoring for the more sophisticated features of CC:Mail (RIP), PointCast (also RIP) tried to label email a 'push' technology so they would look like a next-generation tool rather than a dead-end, and so on.
Here Rothenberg follows the script to a tee, labeling RSS autodiscovery
'simplistic' without entertaining the idea that simplicity may be a requirement of rapid and broad diffusion. The real lesson of RSS autodiscovery is that developers can create valuable meta-data without needing any of the trappings of the Semantic Web. Were the whole effort to be shelved tomorrow, successes like RSS autodiscovery would not be affected in the slightest.

Another good line: 'There is a list of technologies that are actually political philosophy masquerading as code, a list that includes Xanadu, Freenet, and now the Semantic Web.'

web history coding

Belkin's Brain-damage, and Bye-bye Public Domain

Spam: The Reg reports that a Belkin Router software upgrade hijacks HTTP connections to spam the browser with ads. Here's a screenshot of the ad page. Here's a USENET post bemoaning the situation, and the followup from a Belkin PM.

This is amazing; a working piece of network infrastructure has been effectively modified to:

  • replace the expected HTTP responses with spam 'for your convenience'
  • do this once every 8 hours until told to stop
  • report serial numbers, IP addresses and software revisions back 'home' as part of this

And, of course, web browsing is not the only thing that runs over port 80.

So, it's a router that inserts spam into your packets, whether you want it or not, due to a software upgrade; and if you want the bugfixes in that upgrade, you get the spam whether you want it or not. And, that spam could break quite a bit of legitimate port 80 traffic, such as automated download tools that aren't a full web browser, for example. And the spam is unannounced on the download page, or in the change log. I'd hope that's pretty serious under consumer-protection law... it certainly should be.

Copyright: In case there was any doubt that Sonny Bono and Jack Valenti wanted to remove the legal concept of the public domain, check this quote from the Congressional record:

(Mary Bono): Actually, Sonny wanted the term of copyright protection to last forever. I am informed by staff that such a change would violate the Constitution. I invite all of you to work with me to strengthen our copyright laws in all of the ways available to us. As you know, there is also Jack Valenti's proposal for term to last forever less one day. Perhaps the Committee may look at that next Congress.

Wow. More via an Eldred-related site.

security google spam

Real-time DNS blocklist accuracy figures

Spam: DNS blocklists are the oldest means of spam-blocking, and are still exceedingly useful; nowadays, many of these are fully automated systems, using proxy-detection algorithms and sensing patterns in mailer behaviour indicative of spam.

A few months back on the ASRG list, there was a discussion of DNSBL accuracy; I posted some SpamAssassin figures, based on our 'mass-check' tests, but noted that they were computed using current DNSBL contents against a corpus of saved mail, so due to the time delta, were not 100% representative.

These figures are a lot better. Since August, I've been collecting real-time DNSBL hit data on my mail, as it is delivered at my SpamAssassin installation. In other words, it's live accuracy data -- it's using just what the DNSBLs had listed at scan time.

(DNS blocklist accuracy figures continued...)

Note, however, that it's still incomplete:

  • some DNSBLs were not measured; these are just the default DNSBL list in SpamAssassin 2.60, excluding RCVD_IN_NJABL_DIALUP (which I had to remove because I can't parse out accurate data).
  • it's only 1 person's hand-classified mail.
  • SpamAssassin tests more than just the 'delivering' SMTP relay; it'll also look backwards through the headers, at earlier relays, to catch spam sent via mailing lists. This is different from what's used with most traditional DNSBL-supporting systems.

But the results should still be quite useful.

The time period covered:

  • Thu, 21 Aug 2003 17:11:30 -0700 (PDT)
  • Sat, 25 Oct 2003 23:11:52 -0700 (PDT)

Recap of the fields:

  • SPAM% = percentage of messages hit that were spam
  • HAM% = percentage of messages hit that were spam
  • S/O = Spam/Overall = Bayesian probability of spam
  • RANK = artificial ranking figure, ignore this!
  • SCORE = default SpamAssassin 2.60 score
  • NAME = name of test. Figuring out the exactly DNSBL should be pretty obvious ;)

OVERALL%   SPAM%     HAM%     S/O    RANK   SCORE  NAME
21839     1993    19846    0.091   0.00    0.00  (all messages)
100.000   9.1259  90.8741    0.091   0.00    0.00  (all messages as %)
5.989  59.0567   0.6601    0.989   1.00    2.25  RCVD_IN_BL_SPAMCOP_NET
3.869  37.7822   0.4636    0.988   0.96    1.10  RCVD_IN_DSBL
0.751   8.2288   0.0000    1.000   0.95    4.30  RCVD_IN_OPM_HTTP
1.964  20.2709   0.1260    0.994   0.95    1.10  RCVD_IN_NJABL_PROXY
0.659   7.1751   0.0050    0.999   0.95    0.64  RCVD_IN_NJABL_SPAM
0.614   0.0000   0.6752    0.000   0.94   -0.10  RCVD_IN_BSP_OTHER
0.050   0.5519   0.0000    1.000   0.94    4.30  RCVD_IN_OPM_SOCKS
0.027   0.3011   0.0000    1.000   0.94    4.30  RCVD_IN_OPM_WINGATE
0.119   0.0000   0.1310    0.000   0.94   -4.30  RCVD_IN_BSP_TRUSTED
0.939   9.7341   0.0554    0.994   0.94    4.30  RCVD_IN_OPM
1.081  10.9383   0.0907    0.992   0.93    1.52  RCVD_IN_SORBS_SOCKS
1.062  10.7376   0.0907    0.992   0.93    1.27  RCVD_IN_SBL
0.229   2.4084   0.0101    0.996   0.93    1.10  RCVD_IN_SORBS_MISC
0.618   6.3221   0.0453    0.993   0.93    1.10  RCVD_IN_SORBS_HTTP
0.595   5.9709   0.0554    0.991   0.92    4.30  RCVD_IN_OPM_HTTP_POST
0.078   0.7526   0.0101    0.987   0.90    2.60  RCVD_IN_SORBS_ZOMBIE
0.815   7.5263   0.1411    0.982   0.89    1.39  DNS_FROM_RFCI_DSN
3.594  24.8369   1.4613    0.944   0.81    2.55  RCVD_IN_DYNABLOCK
1.685  11.4400   0.7054    0.942   0.78    0.10  RCVD_IN_RFCI
0.380   2.4586   0.1713    0.935   0.75    1.31  RCVD_IN_NJABL_RELAY
6.182  33.9689   3.3911    0.909   0.73    0.10  RCVD_IN_NJABL
10.422  44.4054   7.0090    0.864   0.63    0.10  RCVD_IN_SORBS
0.037   0.1505   0.0252    0.857   0.54    2.80  RCVD_IN_SORBS_WEB
2.344   4.1144   2.1667    0.655   0.17    0.00  RCVD_IN_SORBS_SPAM

anti-spam dnsbls spam spamassassin

Super-absorbent diaper danger

Blogs: Mimi Smartypants, very funny woman that she is, has become a very funny doting mother:

Similarly, recently she finally fell asleep in my arms and I soon caught the faint scent of urine, but I stuffed that thought way down deep into my brain, where the Syrup Of Denial runs thick and sticky, because I just could not deal with the possibility of waking her up during the diaper change. So my daughter slept in her own urine all night, or at least she slept through the bit that was not sucked up by the scarily absorbent diapers they make nowdays. (Seriously, what the hell is in there? I keep having nightmares that the superabsorbent gel will actually start to absorb moisture out of the baby itself and there will just be a dried-up husk in the crib in the morning.)

science ireland privacy pregnancy

My new .sig awaits

Open Source: The FREE, 0% APR, Better Sex, No Effort Diet: Howard Strauss, Princeton's manager of technology strategy and outreach (no less!) takes aim at free software in their 'Syllabus' magazine. He launches a few ad hominems while he's at it:

These folks are some of the same great people who are supposed to be working for you anyway, plus a smattering of teenagers too young to work at Redmond, hackers, virus creators, and a menagerie of others with whom you will feel great pride in entrusting your IT infrastructure.

Given that Princeton's OIT uses SpamAssassin, I guess that means he reckons I, and the other developers, are 'teenagers too young to work at Redmond', or 'virus creators'. Thanks muchly, Princeton!

It sounds like a joke, but I actually think he's serious. My recommendation: he needs to take a job in the software-development side of
such companies as 'Microsoft, IBM, Sun, or even Blackboard' to see how well the commercial software development methodology really works. Hint: from the outside, you don't hear the half of it ;)

Oh -- regarding 'teenagers too young to work at Redmond': this /. comment is worth noting.

spam spamassassin anti-spam

Room for an Irish Netflix

Net: So it seems Kerry Packer has announced a Netflix-like service in Australia, Homescreen.

In essence, you pay a flat fee per month, log on to a website, select a whole batch of DVDs, and they post the first 3 out to you. You can keep them as long as you like, then post them back in pre-paid envelopes; once they arrive at the nearest depot, they post out the next 3 on your list.

This works very well -- in the form of Netflix at least. I can vouch for the coolness of this; pretty much everyone I know who has a DVD player has joined Netflix. It's just great having 3 DVDs on-hand for whenever you feel like watching one.

Of course, it requires that the serivce have a decent selection of goods, including some good 'classics'. From the sounds of things, Homescreen may be failing on this point.

Also, it requires a reliable postal service. But if they can do it in the US, they can certainly do it in Australia or any European country ;)

And I'd bet Ireland has a whole huge DVD-player installed base, given the oft-quoted factoid that there are more PlayStations per capita in Ireland than any other country outside of Japan.

Irish entrepreneurs -- get cracking! ;)

ireland netflix video broadband

The self-aggrandization prize goes to Craig Venter

Science: I'm the human genome, says 'Darth Venter' of genetics (Observer).

Craig Venter, the controversial geneticist who led private industry's decoding of the human genome, has revealed a startling secret. The genome - unravelled two years ago - is his.

To the surprise of scientists, Venter has admitted that much of the DNA used by his company, Celera Genomics, as part of this decoding effort came from his cells. The news has annoyed his colleagues, who claim that Venter subverted the careful, anonymous selection process they had established for their DNA donors.

I missed this story when it came out, but it's a biggie. Instead of mapping the genome of a scientifically-chosen representative, we have the genome of an egomaniac CEO, who spent the entire project self-aggrandizing and attention-seeking.

Just as well the publicly-funded, international Human Genome Project was around to keep them honest for the most part...

Some more choice quotes:

'It doesn't surprise me. It sounds like Craig,' said Nobel laureate James Watson, co-discoverer of the structure of DNA.

As to his reasons for his actions, Venter was unequivocal. 'How could one not want to know about one's own genome?' he said. Neither was he fazed about accusations of egocentricity. 'I've been accused of that so many times, I've got over it,' he said.

Celera's science board was not so understanding. 'Any genome intended to be a landmark should be kept anonymous. It should be a map of all of us, not of one, and I am disappointed if it is linked to a person,' said board member Arthur Caplan.

He added that the drive to sequence the human genome was an opportunity for personal glory as well as scientific discovery. Venter's action emphasised the first motive.

ip patents law

Herring Fart Chat

-----BEGIN PGP SIGNED MESSAGE----- Hash: SHA1

Science: Fish farting may not just be hot air (New Scientist):

Biologists have linked a mysterious, underwater farting sound to bubbles coming out of a herring's anus. No fish had been known to emit sound from its anus nor to be capable of producing such a high-pitched noise.

... Three observations persuaded the researchers that the FRT is most likely produced for communication: Firstly, when more herring are in a tank, the researchers record more FRTs per fish. Secondly, the herring are only noisy after dark, indicating that the sounds might allow the fish to locate one another when they cannot be seen. Thirdly, the biologists know that herrings can hear sounds of this frequency, while most fish cannot. This would allow them to communicate by FRT without alerting predators to their presence.

-----BEGIN PGP SIGNATURE----- Version: GnuPG v1.2.2 (GNU/Linux)
Comment: Exmh CVS

iD8DBQE/qThjQTcbUG5Y7woRAgEOAKDBmfaPgFrrGwTIndzQXJpQvoJGQwCcDyMa qkAWXoutn5Ki64fTK05emHA=
=E1La
-----END PGP SIGNATURE-----

science funny nature

Jody -- still going strong

Spam: I just got another Jody spam; 40 points this time, and featuring the very latest in spam fashion, a .biz URL.

It's amazing! The 'Jody' fake testimonial crops up in 9060 results on the web and 78600 results on USENET. The oldest spam Google Groups has with this text was posted back on 26th May 1998, which makes it 5 and a half years old by now. (Check it out for some classic period ASCII art, misspellings, and LOTS OF SHOUTING!!!!)

Last time I posted about it, Ben actually tracked down a 'Mitchell Wolf M.D., Chicago, Illinois' -- Jody's supposed spouse. Presumably he's retired on the the 'USD 147,200.00 every 45 days' that Jody was amassing from her 'hobby', though. ;)

spam anti-spam history

Sampler Victorious

Ireland: The best programme on Irish TV, by far, is Sampler. It's a great magazine series covering Ireland's underground scenes, with several nice scoops, including being the only set of film cameras around for the police brutality that made the May 6th 2001 Dublin 'Reclaim the Streets' protest infamous. Great soundtrack, too.

Naturally, it's also had a long and illustrious history of no support from RTE, who just seem to hate the whole idea and would prefer they just had a nice, non-controversial chat show instead.

Well, Sampler just won 'Best Special Interest Programme' at the Irish Film and Television Awards. Nice one! (Not that you'd know it from the IFTA website, which hasn't updated the awards pages in 2 years. -- update: Simon points out I'm looking at the wrong site: the real one is here.)

Disclaimer: Luke, the producer, is a good mate of mine. But it's still
a great programme. ;)

Go take a look! Episodes 2 to 5 are online in full, in RealVideo format -- and encoded at a pretty decent bitrate.

ireland dublin awards politics

Justin the Scoopist

Timeliness: w00t! I blog about Jason Salavon, and 4 days later Boing Boing and plasticbag.org both pick up on it. (and rightly so.)

It gets better -- then there's this posting about the EVACS e-voting system, and a week later, Wired News cover it!

... OK, I'm totally exagerrating the latter one. Obviously Wired News go into a lot more detail and do a bit more research. ;) In fact, it's a very good article; here's a killer quote from Software Improvement's Matt Quinn, the lead engineer on EVACS:

Quinn ... says he is 'gob smacked' by what he sees happening among U.S. electronic voting machine makers, whom he says have too much control over the democratic process.

It has been widely reported that Ohio-based Diebold Election Systems, one of the biggest U.S. voting-machine makers, purposely disabled some of the security features in its software. According to reports the move left a backdoor in the system through which someone could enter and manipulate data. In addition, Walden O'Dell, Diebold Election System's chief executive, is a leading fundraiser for the Republican Party. He stated recently that he was 'committed to helping Ohio deliver its electoral votes to the president next year.''

'The only possible motive I can see for disabling some of the security mechanisms and features in their system is to be able to rig elections,' Quinn said. 'It is, at best, bad programming; at worst, the system has been designed to rig an election.'

'I can't imagine what it must be like to be an American in the midst of this and watching what's going on,' Quinn added. 'Democracy is for the voters, not for the companies making the machines.... I would really like to think that when it finally seeps in to the collective American psyche that their sacred Democracy has been so blatantly abused, they will get mad.'

But he says that the security of voting systems in the U.S. shouldn't concern Americans alone.

'After all, we've all got a stake in who's in the White House these days. I'm actually prone to think that the rest of the world should get a vote in your elections since, quite frankly, the U.S. policy affects the rest of the world so heavily.'

e-voting nsa security politics elections funny voting

At Home with the Fuhrer

Bizarre: Given some historical context, it's funny how absolutely insane this sounds: Guardian: At Home with the Fuhrer.

My discovery was an article headlined 'Hitler's Mountain Home' - a breathless, three-page Hello!-style tour around Haus Wachenfeld, Hitler's chalet in the Bavarian Alps. In it, the author, the improbably named Ignatius Phayre, tells us that 'it is over 12 years since Herr Hitler fixed on the site of his one and only home. It had to be close to the Austrian border'. It was originally little more than a shed, but he was able to develop it 'as his famous book Mein Kampf became a bestseller of astonishing power'.

The great dictator, it seems, was quite the interiors wizard: 'The colour scheme throughout this bright, airy chalet is light jade green. The Führer is his own decorator, designer and furnisher, as well as architect... has a passion about cut flowers in his home.'

And he is seldom alone in his mountain hideaway, as he 'delights in the society of brilliant foreigners, especially painters, musicians and singers. As host, he is a droll raconteur... '

Oh, and look who's practising his archery in the garden: 'It is strange to watch the burly Field-Marshal Göering, as chief of the most formidable airforce in Europe, taking a turn with the bow-and-arrow at straw targets of 25 yards range.'

And on it gushes, all accompanied by various photos of Hitler and friends admiring the view, examining plans for the house, and one delightful shot of Adolf relaxing on a deckchair with 'one of his pedigree alsatians beside him'.

Next time you read an over-excited 'inside the home of' article, bear in mind that the subject might be a psychopathic dictator bent on world domination and mass murder.

(The article then descends into a convoluted mess of copyright claims and counterclaims, BTW, in case you're interested. But the bizarre stuff is what got me ;)

politics ireland history google

Sampler Victorious

The best programme on Irish TV, by far, is Sampler. It's a great magazine series covering Ireland's underground scenes, with several nice scoops, including being the only set of film cameras around for the police brutality that made the May 6th 2001 Dublin 'Reclaim the Streets' protest infamous. Great soundtrack, too.

Naturally, it's also had a long and illustrious history of no support from RTE, who just seem to hate the whole idea and would prefer they just had a nice, non-controversial chat show instead.

Well, Sampler just won 'Best Special Interest Programme' at the Irish Film and Television Awards. Nice one! (Not that you'd know it from the IFTA website, which hasn't updated the awards pages in 2 years. -- update: Simon points out I'm looking at the wrong site: the real one is here.)

Disclaimer: Luke, the producer, is a good mate of mine. But it's still
a great programme. ;)

Go take a look! Episodes 2 to 5 are online in full, in RealVideo format -- and encoded at a pretty decent bitrate.

ireland dublin politics

Needs more thought

Politics: Nelson Mandela banned from visiting the US. oops! But they've fixed it:

The good news is that the United States government has removed Nelson Mandela, Tokyo Sexwale and Sidney Mufamadi from its list of global terrorists. The bad news is that the removal is only for the next 10 years. ....

'To make an exception for those who struggled against apartheid would require congress to change the law, and that would be a very lengthy process,' (Virginia Farris, the public affairs spokesperson for the US embassy in Pretoria) said.

Via Wendy M. Grossman, who reckons myself and the other SpamAssassin guys are Mrs. Beeton. ;)

politics us-politics government

Ho hum

Spam: I just received a spam containing this (HTML tags made readable by translating angles to round brackets):

Subject: Re: ZR, the master walked

(BODY bgColor=#ffffff) (font color=white) hellgrammite vocabularian distaff cardamom curvilinear pyhrric whizzing fruition canvasback maritime calcareous byline peddle cautionary smooch detain deadwood thrash centaur hurd coruscate confession bloom damsel gallon downtown morphine respirator psycho consolidate nee boycott (/font) Ban(/neve)ned C(/elmsford)D Gov(/validate)ernment d(/staccato)on't wan(/goat)t m(/embank)e t(/trident)o s(/logjam)ell i(/constantine)t. Se(/falloff)e N(/judson)ow - (then a link, finally!!) (font color=white)neuroses aghast mazurka ribose architectural tranquillity heterosexual custom coquette mauritius downgrade croydon mechanist devious nh lange circumscribe infancy drool between foppish momentous doug induce (/font)

What a mess. Regardless, SpamAssassin gave it a 17.4 and autolearned it as spam ;)

spam anti-spam web

Spam load and Hallowe'en

Spam: The volume of spam continues to rise inexorably. Brightmail are now estimating that 54% of all mail messages are spam.

Nowadays, my personal mail account is getting about 70 a day, rising to over 200 a day at the weekends. It's getting tiresome; pretty much all of it gets marked as spam and diverted, but I still have to wade through it 'just in case', and to build the corpus. I guess I need to extend my .procmailrc to divert high-scoring spams somewhere I can check even less frequently ;)

That's not the really annoying thing, though. I use tagged addressing when I publish my email address, most of the time. It works very well to identify spam sources overall, and divert 'dead' addresses that are getting spam, into the spamtraps. That's the plus.

But the curse of writing spam filters is that you need a good archive of spam; and one of our SpamAssassin corpus guidelines is to attempt to trim out duplicate spams where possible. Many spammers will wind up sending more-or-less identical spam messages, modulo random subject lines, hash-busters, etc., and with (let's say) 8 tagged addresses in their lists, I'll get 8 copies of that spam, and have to pay a little bit of attention to trim it down to 1 copy for the corpus.

Damn spam-filter development! All this corpus building is hard work ;)

BTW, note how spam load rises at the weekends; (Tim Hunter, Paul Terry and Alan Judge of eircom.net also noted this in their paper presented at LISA '03 yesterday ;). There's a good reason -- spammers attempt to deliver their spam while abuse staff are not at their desk. Same thing applies in the network security world; many of those attacks have taken place over a US holiday weekend.

Hallowe'en: best too-late idea for a hallowe'en costume: 'Top Gun GWB' in his flight suit. In the end, I played half of the 'Dr. Frankenstein and Monster' pair (I was the monster, as C really is a scientist, and computer 'science' doesn't count). Best costume seen: a very impressive onnagata kabuki player.

anti-spam spamassassin smtp

Spam load and Hallowe'en

The volume of spam continues to rise inexorably. Brightmail are now estimating that 54% of all mail messages are spam.

Nowadays, my personal mail account is getting about 70 a day, rising to over 200 a day at the weekends. It's getting tiresome; pretty much all of it gets marked as spam and diverted, but I still have to wade through it 'just in case', and to build the corpus. I guess I need to extend my .procmailrc to divert high-scoring spams somewhere I can check even less frequently ;)

That's not the really annoying thing, though. I use tagged addressing when I publish my email address, most of the time. It works very well to identify spam sources overall, and divert 'dead' addresses that are getting spam, into the spamtraps. That's the plus.

But the curse of writing spam filters is that you need a good archive of spam; and one of our SpamAssassin corpus guidelines is to attempt to trim out duplicate spams where possible. Many spammers will wind up sending more-or-less identical spam messages, modulo random subject lines, hash-busters, etc., and with (let's say) 8 tagged addresses in their lists, I'll get 8 copies of that spam, and have to pay a little bit of attention to trim it down to 1 copy for the corpus.

Damn spam-filter development! All this corpus building is hard work ;)

BTW, note how spam load rises at the weekends; (Tim Hunter, Paul Terry and Alan Judge of eircom.net also noted this in their paper presented at LISA '03 yesterday ;). There's a good reason -- spammers attempt to deliver their spam while abuse staff are not at their desk. Same thing applies in the network security world; many of those attacks have taken place over a US holiday weekend.

Hallowe'en: best too-late idea for a hallowe'en costume: 'Top Gun GWB' in his flight suit. In the end, I played half of the 'Dr. Frankenstein and Monster' pair (I was the monster, as C really is a scientist, and computer 'science' doesn't count). Best costume seen: a very impressive onnagata kabuki player.

anti-spam spamassassin smtp

Tim Bray on Dublin

Ireland: 'The weather is bloody this time of year, the traffic is worse, but it's a fine town.' Agreed!

So I met up with SpamAssassin Dan, SpamAssassin Theo, and POPFile author John Graham-Cumming yesterday, down in San Diego -- much spam stuff was discussed.

Great to meet up -- not so great to miss the last train back to Irvine to my own inability to correctly read a timetable, and have to drag Dan and Theo out that way. oops, sorry guys! Not so smart, but at least we got to carry on the discussion for an hour or two more...

ireland dublin barcamp

IBM attempting to patent the 'wallet'

Patents: New Scientist reports that IBM have applied for a patent on "an electronic password 'wallet' that securely stores all your passwords, with overall access via a single password. The wallet pops up on screen whenever you are asked for a password. You enter the master password and the wallet then answers the online request by pasting in the appropriate password for that site."

This should be familiar to anyone who's used Mozilla's Form Manager feature, which fits the patent claims perfectly. That page notes that the Mozilla feature was created in 1999, just under 3 years before the patent application. Let's hope the USPTO remember to do a Google search this time!

patents security uspto linux

Statistical Art

Art: Jason Salavon: Selected projects, 1997 - 2003.

Salavon operates by taking data from various sources (DVDs of late-night talk shows, homes for sale in various states, MTV's 10 Greatest Music Videos of All Time, Playboy centerfolds, etc.), then statistically combining them and converting that into another image, movie, or whatever.

The results are excellent. Check out Homes for Sale and Every Playboy Centerfold, The Decades (normalized).

I remember somebody asking me what I thought 'computer art' (sic) should be like, after I dissed yet another lame pixellated Photoshop/Flash thingy. Now I have something to point at ;) I'm well impressed.

art images video

Patents and Innovation, via slashdot

Patents: Slashdot gets a lot of stick for cluelessness. Now and again, though, you find well-presented arguments you won't read elsewhere. Try these:

An excellent summary of James Burke's book, The Day the Universe Changed; I haven't read it, but it sounds good. Reportedly, there's a section covering a period in British history when patent law was extended to cover 100 years; 'Like copyright today a person could not extend on a process developed on the day of their birth - they and their children (and even many of their grandchildren) would be dead long before the patent expired.'

Meanwhile, Germany refused to respect these terms, and their industry flourished -- 'a backwards agrarian society became an industrial powerhouse that far exceeded the capabilities of the British industry they 'stole' from, within a working lifetime.'

Details of how Lowell, Massachusetts became an industrial-era milling powerhouse through the US 'stealing' British patents: 'an English immigrant, Samuel Slater ... had worked his way up from apprentice to overseer in an English factory using the Arkwright system. Drawn by American bounties for the introduction of textile technology, he passed as a farmer and sailed for America with details of the Arkwright water frame committed to memory.'

Games: GameChronicles on the GTA:VC - Scarface connection. A nice summary of all (or at least, most) of the Scarface homages in the game.

patents swpats history ip law uspto

Freedroid

Games: Commodore 64 old-timers may remember Andrew Braybrook's classic Paradroid, easily one of the best games for that platform, and a classic by any standards. Here's a copy of the Zzap! 64 review from 1986. Many thumbs up, and the bottom line was that Paradroid ranked as 'THE classic shoot-em-up'.

Paradroid trivia: in the days before .plan files, Zzap! 64 published a development diary by AB! Here's the birth of one of the game's key mechanisms, the 'transfer game':

Tuesday May 21: An average morning's contemplation until ...ZAP WHIZ POW ! An idea for a game within the main one, fighting for control of a new robot. Instead of just a graphical sequence showing the takeover of a new robot, why not have to play for it, you against the robot's brain? Base it on logic circuits and use some existing routines. A whole new game segment in a small space!

Cool.

The authors' company, Graftgold, has a website, detailing its history. Sadly, it maps the decline of the 80's-style small games company, and ends on this note: 'I would recommend the games industry to anyone wanting an exciting career buts its certainly not an easy ride. Most publishers we worked with either went bust, sold out or simply did not publish the game to our expections despite tight contracts. The trouble is the developer does their bit first then the publisher can choose the level to do their bit. Unless you can get real commitment by way of big advances you cannot rely on a publisher.'

Shame. Anyway. I'm not the only Paradroid fan out there -- it seems a bunch of fellow enthusiasts have come up with FreeDroid, a homage to Paradroid which seems to be evolving into an RPG! It's quite impressive -- the gameplay is virtually identical to the original. Fedora Linux users can install it using apt-get install freedroid.

BTW, related: here's two attempts at a canon for computer gamers, at costik.com and the Ludologist (of which I've played 121). What I find interesting about them is how clearly one is American and Apple-II-based and the other European and Commodore-64/Amiga-based. Stay tuned for the third, Spectrum-based canon. ;)

gaming games history

More on the ACT EVACS E-Voting System

Voting: Nathan Cochrane mailed in some great tidbits about the ACT EVACS e-voting system. (thanks!)

First off, this Debian-news posting notes some snippets from an Age article by Nathan; Here's some longer excerpts. It features some great quotes: 'the only platform that provided robustness and voter confidence was GNU Debian Linux, with all source code released under the General Public License (GPL).'

And this one:

'Classical voting systems, notably the Australian paper ballot, are designed precisely on such anti-trust grounds,' Jones said. 'We simply assume from the start that each and every participant in the system is a partisan with a vested interest in doing everything possible to help his or her favorite candidates.'

He said paper and pencil voting systems, such as that first used in Victoria in 1858, meet this test. Electronic voting does not.

This letter to LWN notes: 'You might be interested to know that some of the work on this project is being done by 'big name' open source people, including Andrew Tridgell (aka Mr Samba), Dave Gibson (orionoco wireless LAN driver), Martin Pool (apache), and Rusty Russell (netfilter and other gross kernel hacks)', and links to the code's CVS repository!

It seems those guys performed the work on behalf of a Canberra open-source consultancy group, Software Improvements; Here's the product brochure.

This posting to iRights gives a few more details.

It all looks like an excellent job all 'round, as far as I can see.

e-voting security voting politics

On Pay-Per-Mail

Spam: Lee Maguire on pay-per-mail schemes. A great read -- recommended to anyone who has given thought to this system.

It's usually the fear of the odd overlooked gem that has rendered anti-spam techniques impotent. A salutation from a long lost friend with the subject 'Hi', an important business mail sent out-of-hours from the kid's computer, that domain renewal reminder. Most people would apply no charge on the things they want to read, and a bajillion dollars on spam. And if there's mail you don't want to read but have to? Chances are you're being paid to read them already - get back to work.

SoCal: an amazing satellite picture of the wild fires, courtesy of NASA's Earth Observatory.

spam anti-spam gmail botnets security

More on the ACT EVACS E-Voting System

Nathan Cochrane mailed in some great tidbits about the ACT EVACS e-voting system. (thanks!)

First off, this Debian-news posting notes some snippets from an Age article by Nathan; Here's some longer excerpts. It features some great quotes: 'the only platform that provided robustness and voter confidence was GNU Debian Linux, with all source code released under the General Public License (GPL).'

And this one:

'Classical voting systems, notably the Australian paper ballot, are designed precisely on such anti-trust grounds,' Jones said. 'We simply assume from the start that each and every participant in the system is a partisan with a vested interest in doing everything possible to help his or her favorite candidates.'

He said paper and pencil voting systems, such as that first used in Victoria in 1858, meet this test. Electronic voting does not.

This letter to LWN notes: 'You might be interested to know that some of the work on this project is being done by 'big name' open source people, including Andrew Tridgell (aka Mr Samba), Dave Gibson (orionoco wireless LAN driver), Martin Pool (apache), and Rusty Russell (netfilter and other gross kernel hacks)', and links to the code's CVS repository!

It seems those guys performed the work on behalf of a Canberra open-source consultancy group, Software Improvements; Here's the product brochure.

This posting to iRights gives a few more details.

It all looks like an excellent job all 'round, as far as I can see.

e-voting security voting elections politics

More pics of the wild fires, and going for a SONGS

SoCal: some great pictures from Derek Balling down in San Diego. Check out those skies!

Nukes: Great! The OC Weekly reports 'the much-maligned San Onofre Nuclear Generating Station (SONGS) has finally gotten some recognition -- but probably not the kind it wants: it now ranks (third) among the U.S. facilities most likely to suffer a meltdown, according to the Union of Concerned Scientists, a scientific group that monitors nuclear safety.'

A serious meltdown at SONGS would result in a massive release of radioactivity that could immediately kill more than 100,000 people in South County and northern San Diego County and ultimately cause hundreds of thousands of cases of cancer and genetic defects.

That's 15 miles away from me, fact fans. Mind you, having grown up directly west of Sellafield's discharge pipes, I'm used to a bit of radioactivity ;)

power history coding

It's the end of the world as we know it...

SoCal: Wild fires are raging throughout Southern California.

Last night, I was reading J. G. Ballard's Millenium People (thanks Lean, it's great!) outside on the balcony, when the Santa Ana winds whipped up suddenly, blowing hot and dry and laden with ash -- then the coyotes started howling.

It felt very much like the end of the world... freaky stuff.

Everything is covered in ash; the air smells of wood smoke; the sun is a minute cent-at-arm's-length red disc; everything is lit in a very odd reddish-orange tint. And the nearest fire is 30 or so miles away. I'd hate to see what they're like up close...

Somehow I missed all this in Australia... I hear Sydney was like this for a week over Christmas that year.

Some links:

politics climate-change hiking

It's the end of the world as we know it...

Wild fires are raging throughout Southern California.

Last night, I was reading J. G. Ballard's Millenium People (thanks Lean, it's great!) outside on the balcony, when the Santa Ana winds whipped up suddenly, blowing hot and dry and laden with ash -- then the coyotes started howling.

It felt very much like the end of the world... freaky stuff.

Everything is covered in ash; the air smells of wood smoke; the sun is a minute cent-at-arm's-length red disc; everything is lit in a very odd reddish-orange tint. And the nearest fire is 30 or so miles away. I'd hate to see what they're like up close...

Somehow I missed all this in Australia... I hear Sydney was like this for a week over Christmas that year.

Some links:

politics climate-change hiking

Worst album covers ever

Funny: C sends along a few classic album covers taken from this site. Here's my favourites:

There's plenty more...

music mp3 filesharing piracy

Worst album covers ever

C sends along a few classic album covers taken from this site. Here's my favourites:

There's plenty more...

music mp3 filesharing piracy

Tentacle Porn has a long and illustrious history

Japan: The Guardian: Melbourne row over art 'porn':

'Police in Australia have investigated pornography claims against an art gallery which exhibited a painting drawn from a 19th-century woodcut by the Japanese artist Hokusai.

The painting, The Dream of the Fisherman's Wife, is by an Australian, David Laity, and is valued at £5,400. It is being shown in a Melbourne gallery. Like the 1814 original, it depicts a woman copulating with an octopus.

Katsushika Hokusai was an influential Japanese painter and woodcut designer in the 18th and 19th centuries -- more info and pictures here. (There's a great exhibition of his work on at the Chester Beatty Library in Dublin right now, which is where I caught it.)

He coined the term 'Manga' to describe a collection of sketches. Who knew he also came up with the totally bizarre 'tentacle porn' subgenre of anime?

art history funny

E-Voting: ACT's open-source e-voting system

Voting: I've pointed to this before, but I use taint.org partly as a searchable database of annotated bookmarks, so -- for reference -- here's the Australian Capital Territory's EVACS system, an entire, open-source e-voting system:

EVACS is the computer system that provides for electronic voting and electronic counting for ACT Legislative Assembly elections. It provides for counting according to the Hare-Clark electoral system rules set out in the Electoral Act 1992.

EVACS was written using Linux open source software to ensure appropriate transparency. A copy of the source code is available in a zip file (127 kb). The source code for the casual vacancy module is in a separate file (38 kb). For more information contact Software Improvements.

Still not perfect -- it uses electronic ballot stations, instead of paper ballots -- but it does support paper ballots. And it's open source; note the keyword above -- 'appropriate transparency'. They said it, not me ;)

e-voting security ireland

Tentacle Porn has a long and illustrious history

The Guardian: Melbourne row over art 'porn':

'Police in Australia have investigated pornography claims against an art gallery which exhibited a painting drawn from a 19th-century woodcut by the Japanese artist Hokusai.

The painting, The Dream of the Fisherman's Wife, is by an Australian, David Laity, and is valued at £5,400. It is being shown in a Melbourne gallery. Like the 1814 original, it depicts a woman copulating with an octopus.

Katsushika Hokusai was an influential Japanese painter and woodcut designer in the 18th and 19th centuries -- more info and pictures here. (There's a great exhibition of his work on at the Chester Beatty Library in Dublin right now, which is where I caught it.)

He coined the term 'Manga' to describe a collection of sketches. Who knew he also came up with the totally bizarre 'tentacle porn' subgenre of anime?

art history funny

SF film tip: 'The Revolution Will Not Be Televised'

Movies: Inhabitants of San Francisco! Or people nearby who fancy watching a great documentary! According to the SFGate.com Morning Fix, the Castro theater will be showing the amazing documentary The Revolution Will Not Be Televised between Oct 24-30.

I've blogged this before, but quick recap: it's an incredible movie documenting what happened in the Venezuelan Presidential Palace on April 11th 2002, when President Hugo Chavez was briefly deposed by a coup d'etat. It covers the entire period, and amazingly has pretty-much full access to everything that Chavez, his cabinet, and his loyal soldiers did and said. A sample:

'On the day of the coup, we only began realising what was actually going on when the state TV signal was cut. Up until then, people had been shot and there was a terrible sense of confusion, but still the reality of what was taking place hadn't exactly sunk in. Then later that night, the media started saying that Chavez had fled to Cuba and that he had resigned, when in fact he was in the palace -- and so were we. It became clear then that something very calculated and sinister was unfolding.'

Really, it's well worth watching. Due to its comments on the actions, and spin, of the current US administration, Harry Knowles reckons it'll never get a public release in the US outside a film festival (and I'd agree) -- so you're going to have to watch it in a lefty theater or nothing.

(BTW the website needs some work though -- it uses the horrible 'reinventing the scrollbar' DHTML trick, urgh.)

politics privacy us-politics

On 'Intellectual Property'

Patents: One thing that gets pretty confusing when one investigates the whole patents/open-source/copyright protection field, is the nature of the term Intellectual Property.

What's called 'IP' consists of three parts: copyright, patents, and trademarks. This extract from Harvard's 'Intellectual Property in Cyberspace' series notes:

In the eighteenth century, lawyers and politicians were more likely to refer to patents and copyrights as 'monopolies' than they were to refer to them as forms of 'property.' ... Thomas Jefferson was the most prominent adherent of this view, but many others shared his attitude to varying degrees. ....

Another, more general manifestation of the same trend has been the growing power of the phrase 'intellectual property.' Before the Second World War, use of the phrase as shorthand for copyrights, patents, trademarks, and related entitlements was rare. Since that time, it has become steadily more common. n105 Today, it is the standard way for lawyers and law teachers to refer to the field.

Why does the popularity of the term matter? The answer ... is that legal discourse has power. Specifically, the use of the term 'property' to describe copyrights, patents, trademarks, etc. conveys the impression that they are fundamentally 'like' interests in land or tangible personal property -- and should be protected with the same generous panoply of remedies. ....

Regrettably, the pleas by Cohen and a few others that judges jettison the concept of 'property' and frankly confront the public policy implications of protecting certain kinds of information fell largely on deaf ears. The 'propertization' of the field continued -- and is now well-nigh complete.

It's common to read commentary by outsiders -- journalists especially -- who conflate all three forms of 'IP', and therefore assuming that all three should be considered as 'equal' to physical property. In other words, they fall into this trap.

In reality, a trademark should have much more protection than a patent; copyright over 'bits' is not the same thing as physical ownership of atoms; the concept of the public domain is a whole lot different between 'things' and 'bits'; there's a difference.

To this end, this disclaimer from the UN World Summit on the Information Society is very significant; they've recognised these issues.

This working group has come to recognize that the term 'intellectual property rights' carries bias and encourages simplistic overgeneralization. Therefore this working group does not carry the name IPR. In particular, this group does not endorse the legal school of thought, which advocates that productions of the mind shall be treated in a similar way as real estate property. This legal doctrine implicitly backs the concept that copyrights should last for ever.

Nice work! (thanks to Russell McOrmond and Seth Johnson for noting it.)

ip patents law swpats copyright

Meld for graphical merging

Software: Great LWN weekly edition last Friday; not only is there a very nice article about SpamAssassin, debunking the 'open spam filtering rules considered harmful' myth, but there's a great tool tip: Meld, a new graphical merging tool.

Basically, when you have two pieces of text, and want to merge them together into one, you need a merge tool. This is a tricky job; most people just get the tool to stick them all in one file, CVS-style, and try to figure it out visually. It's fraught with problems.

Hence the idea of using a GUI to ease the task. There have been other graphical merge tools before; I know of the proprietary one bundled with ClearCase, and tkdiff. However, both of these just aren't very good -- it's quite simply too hard to figure out exactly what direction which piece of text came from.

Looks like meld is a fantastic effort to fix this; take a look at the screenshots. The key is the approach they've taken of having a drawable area in the middle between the two differing texts; this is used for lines and graphical indications of what came from where. It really seems to work, from what I can see.

spamassassin anti-spam software

Dodgy computer games studies

Science: A lab rat writes up a report on his participation in two psychology studies on 'Video Game Violence' and 'Violence In the Media.'

Sadly, it seems clear that the video-game violence study will return biased results due to flawed test conditions.

Of the three games played, the most violent -- a first-person shooter -- was modified, either through incompetence or deliberate tweaking, to use frustrating control settings and a high level of difficulty; whereas the least violent -- a sim game -- was set up with all the defaults and automatic help enabled.

In my experience, frustration, in any task, has a direct correlation with anger levels. So a frustrating game, violent or not, will probably give more aggressive responses in a violence measurement -- hence the FPS game above will almost definitely be cited as 'inciting violent emotions'.

Bad scientists! No doctorate!

PS: hmm, I wonder if the paper will document the exact configuration
of the games?

Linux: Happy birthday, KDE! I love it. Most recent discovery: the excellent support for printing in KDE 3.1 using the kprinter GUI.

gaming games history coding

Control your life support via the Internet!

Security: Romania Emerges As Nexus of Cybercrime (AP). Contains this glorious nightmare scenario:

BUCHAREST, Romania - It was nearly 70 degrees below zero outside, but the e-mail on a computer at the South Pole Research Center sent a different kind of chill through the scientists inside.

'I've hacked into the server. Pay me off or I'll sell the station's data to another country and tell the world how vulnerable you are,' the message warned.

Proving it was no hoax, the message included scientific data showing the extortionist had roamed freely around the server, which controlled the 50 researchers' life-support systems.

One question: why was an internet-connected computer controlling the life support systems? eeek.

internet security ireland web malware politics

Control your life support via the Internet!

Romania Emerges As Nexus of Cybercrime (AP). Contains this glorious nightmare scenario:

BUCHAREST, Romania - It was nearly 70 degrees below zero outside, but the e-mail on a computer at the South Pole Research Center sent a different kind of chill through the scientists inside.

'I've hacked into the server. Pay me off or I'll sell the station's data to another country and tell the world how vulnerable you are,' the message warned.

Proving it was no hoax, the message included scientific data showing the extortionist had roamed freely around the server, which controlled the 50 researchers' life-support systems.

One question: why was an internet-connected computer controlling the life support systems? eeek.

internet security ireland web malware politics

Compare and Contrast

Politics: Eli Lilly wants it both ways. First off pro-free-market:

Not many U.S. companies would put 'maintenance of free market' at the top of their worry list, but the pharmaceutical industry has genuine reasons for concern.

But then, anti-free-market!:

Starting immediately, if a Canadian wholesaler tries to order more Lilly product than Lilly's estimate of what is appropriate for Canadian use, 'they will not be able to have it,' Smith said.

patents health ireland

Secsed-up

Humour: Data::Secs2 -- canoncial string for nested data. A format for representing nested data structures in accordance with SEMI E5-94, Semiconductor Equipment Communications Standard 2 (SECS-II), apparently pronounced "'sex two' with gusto and a perverted smile."

The manual page goes on:

In order not to plagarize college students, credit must be given where credit is due. Tony Blair, when he was a college intern at Intel Fab 4, in London invented the SEMI SECS standards. When the Intel Fab 4 management discovered Tony's secsification of their host and equipment, they elected to have security to escort Tony out the door. This was Mr. Blair's introduction to elections which he leverage into being elected prime minister. In this new position he used the skills he learned at the Intel fab to secsify intelligence reports on Iraq's weopons of mass distruction.

'Secsed-up', surely!?

funny algorithms nsa security politics us-politics privacy law

Using a Web of Trust to stop spam

Spam: Been thinking about a distributed 'web of trust' approach to fighting spam.

Combine those with another key point -- that we do not need PKI, crypto, or any other changes to identify senders in current SMTP -- and it could be done today, I think.

Why we don't need crypto to identify an SMTP sender

Every email message delivered via SMTP across the internet will contain these headers:

  • the From line
  • one or more Received headers

Traditionally, whitelisting uses just the From line, which is vulnerable to spoofing. SpamAssassin used this up to version 2.3x. Spammers started spoofing mails where 'From' was the same as 'To', and since most people had themselves in the whitelist, that worked. boo.

In 2.3x or 2.4x, we added code to extract the IP addresses from the Received headers, and use a combined token -- ( from_address, ip_address ) -- as the sender's address.

(In fact, we use just the top 24 bits of each IP to deal with situations like DHCP or dialup pools, where a relay may get a different IP every now and again. That's close enough, at least.)

This is much harder to forge without doing a full-scale TCP spoofing attack; which is why the SpamAssassin auto-whitelist generally works well.

So basically, to identify someone strongly enough to provide a spam fix in plain old vanilla current SMTP, gen up a string containing their 'From' address, along with all the /24 masks of the IP addresses found in the 'Received' headers.

Remove your relays' IP addresses, and you have an unspoofable ID for that person's SMTP traffic. Any spammer who wants to spoof that, will have to compromise their mail server (or a server in the same /24). That's not cost-effective for spamming.

Note that whitelisting based on that is effectively what the SpamAssassin auto-whitelist does. But for that to be more useful than the AWL, it has to extend over the internet to those people your friends haven't corresponded with yet; ie. it's got to be distributed.

(If you would like to comment on this scheme, I'd prefer if you could post comments at this QuickTopic forum.)

anti-spam spamassassin spam email smtp

Using a Web of Trust to stop spam

Been thinking about a distributed 'web of trust' approach to fighting spam.

Combine those with another key point -- that we do not need PKI, crypto, or any other changes to identify senders in current SMTP -- and it could be done today, I think.

Why we don't need crypto to identify an SMTP sender

Every email message delivered via SMTP across the internet will contain these headers:

  • the From line
  • one or more Received headers

Traditionally, whitelisting uses just the From line, which is vulnerable to spoofing. SpamAssassin used this up to version 2.3x. Spammers started spoofing mails where 'From' was the same as 'To', and since most people had themselves in the whitelist, that worked. boo.

In 2.3x or 2.4x, we added code to extract the IP addresses from the Received headers, and use a combined token -- ( from_address, ip_address ) -- as the sender's address.

(In fact, we use just the top 24 bits of each IP to deal with situations like DHCP or dialup pools, where a relay may get a different IP every now and again. That's close enough, at least.)

This is much harder to forge without doing a full-scale TCP spoofing attack; which is why the SpamAssassin auto-whitelist generally works well.

So basically, to identify someone strongly enough to provide a spam fix in plain old vanilla current SMTP, gen up a string containing their 'From' address, along with all the /24 masks of the IP addresses found in the 'Received' headers.

Remove your relays' IP addresses, and you have an unspoofable ID for that person's SMTP traffic. Any spammer who wants to spoof that, will have to compromise their mail server (or a server in the same /24). That's not cost-effective for spamming.

Note that whitelisting based on that is effectively what the SpamAssassin auto-whitelist does. But for that to be more useful than the AWL, it has to extend over the internet to those people your friends haven't corresponded with yet; ie. it's got to be distributed.

(If you would like to comment on this scheme, I'd prefer if you could post comments at this QuickTopic forum.)

anti-spam spamassassin email spam smtp

That Forbes Article

Open Source: Forbes: Linux's Hit Men.

The dispute, which was leaked to an Internet message board, offers a rare peek into the dark side of the free software movement--a view that contrasts with the movement's usual public image of happy software proles linking arms and singing the 'Internationale' while freely sharing the fruits of their code-writing labor.

(Here we go again -- the old 'free software is communism' line, cf. the 'Give Communism A Try!' / Nazi Penguin posters SCO made up earlier this year.)

The article goes on to bemoan how software companies who write proprietary extensions into GPL-licensed software, have to comply with the terms of the license.

It's all a bit of an obvious dig -- but I am looking forward to the follow-up article -- that's the one where the author bemoans how commercial software companies send out their 'enforcers' to extort money from companies who don't bother paying the royalties and runtime license fees their licenses require.

PS: Hmm, 'software prole' -- maybe I'll adopt that in the same way
Suresh has adopted 'lower-middle-class Unix sysadmin':

The other title came from a spammer who asked Ramasubramanian what she'd done that made him report her to her ISP.

'I gave her a standard set of links and information on why spam is bad, and took the time to explain all this to her. She then asked me what I did for a living. When I replied that I was a Unix administrator at an ISP, she blew up and said, 'I thought you were a successful businessman and marketer, but you are only a lower-middle-class Unix sysadmin. Don't you dare talk to me like this!!!''

Oh look, Suresh has a journal, too; I never realised. Cool.

open-source software politics

SCO's no-show invoices

SCOvLinux: GrokLaw: Groklaw's Open Letter Linked to SCO's Backing Off Invoicing.

'SCO Group Inc is backing-down from threats to invoice organizations running Linux while extending SGI's compliance deadline.

'A company spokesperson said yesterday SCO's plan to invoice organizations, on the basis that Linux illegally contains SCO code, had changed following what he claimed was success of its UnixWare licensing program. . . .

'Members of the open source community warned SCO last month in an open letter they would initiate civil action under anti-fraud and consumer protection statutes.'

My take: 'What? You mean extortion through fraudulent invoicing is illegal? Oops, call the mail room!'

BTW, anyone who hasn't read the GrokLaw Open Letter to SCO yet, really should. It's a great summary of all the many points where SCO is wrong.

law spam patents

MS on Choice

Music: This is great. Microsoft's general manager for the Windows Digital Media division, Dave Fester, on iTunes for Windows:

If you use Apple's music store along with ITunes, you don't have the ability of using the over 40 different Windows Media-compatible portable music devices. When I'm paying for music, I want to know that I have choices today and in the future.

Oh, the schadenfreude. (I wonder how many MP3-compatible portable music devices there are?)

music drm mp3 ireland linux software internet

AdvogatoDay

Tech: So, I just looked at NTK; it has a brief bit about Bram Cohen 'having solved content distribution, (announcing) he was now tackling other simple problems: reputation systems, version control and perhaps after lunch the NP-complete set.'

Hmm, interesting! Let's take a look at his diary -- and what do I find but a whole load of entries on using trust metrics against spam. Bugger. Looks like I have my weekend reading cut out for me.

Also notable: Advogato has added native RSS support, which makes this pretty pointless; and they've also added an XML-RPC interface. Expect to see taint.org entries getting copied up there soon, as a result. ;)

anti-spam spam community planet weblogs

Uptown, Downtown and Midtown

Language: AussieInAmerica on {up,down,mid}town:

Something that is common here in Atlantic Canadian and northeast American small cities is to refer to the CBD (or city centre/downtown) as 'uptown', especially if coming to the city from its environs. BUT... once I am 'uptown' , I would then refer to my location as 'downtown'. In other words, 'uptown' is the city centre/ CBD only if you are not there yet. 'Uptown' becomes 'downtown' once you arrive there. AND, since many smaller cities have one main street that leads in and out, if you head out of 'downtown' up that street you are going 'uptown'. Follow? It works for us and I can't recall any confusion.

(Author:) Hmm, I'm glad you folk have got it sorted out! I am reminded of Grover's existential crisis on Sesame Street as he was coming to grips with 'here' and 'there'. Every time he pitter-pattered over to 'there', it turned into 'here'.

Great site. Some pretty good Strine, too -- 'Jeggoda Sinny?' really is a common query!

language languages usa

Spamcop and 'Al-Quada', sitting in a tree

Humour: The null device reports a spam entitled, 'julian haight funds terrorists b alqoswmw l lgng'.

Julian haight spamcops CEO is rumoured to have conections with Al-Quada, one of the most disruptive terrorist orginisations on earth. hes specialty is cyber terrorism. which disperses highly needed homeland security funds by rendering multi million dollar industrys unprofitable.

haights main motive is the perversion of American free enterprise.

Oh, the poor spammers! One comment quotes Samuel Johnson: 'patriotism is the last refuge of a scoundrel'.

Also present is some lovely pictures of Carlton, with trams, greenery, grey skies, and that distinctive turn-of-the-century Aussie architectural style. A couple of years ago, I lived just around the corner in North Melbourne; looking at those photos, it seems like I could just pop out the front door and walk through it all on the way down to the Vic market. They thoroughly evoke day-to-day just-outside-the-CBD Melbourne.

spam anti-spam history

Spamcop and 'Al-Quada', sitting in a tree

The null device reports a spam entitled, 'julian haight funds terrorists b alqoswmw l lgng'.

Julian haight spamcops CEO is rumoured to have conections with Al-Quada, one of the most disruptive terrorist orginisations on earth. hes specialty is cyber terrorism. which disperses highly needed homeland security funds by rendering multi million dollar industrys unprofitable.

haights main motive is the perversion of American free enterprise.

Oh, the poor spammers! One comment quotes Samuel Johnson: 'patriotism is the last refuge of a scoundrel'.

Also present is some lovely pictures of Carlton, with trams, greenery, grey skies, and that distinctive turn-of-the-century Aussie architectural style. A couple of years ago, I lived just around the corner in North Melbourne; looking at those photos, it seems like I could just pop out the front door and walk through it all on the way down to the Vic market. They thoroughly evoke day-to-day just-outside-the-CBD Melbourne.

spam anti-spam history

iTunes adding indie tunes

Music: Indie Labels Debut At iTunes Music Store: 'I happened to notice a Thievery Corporation release from Eighteenth Street Lounge Music in the 'Just Added' section...doing some more exploring, I found releases from Matador (Interpol, Pizzicato Five) and Nettwerk (BT) as well.' (thx Karlin !)

Hmm -- that's good news for iTunes, but pretty bad news for EMusic. Those labels are all very well-represented on EM.

Wonder if I can run iTunes under Wine?

ireland music mp3 linux filesharing

Recycling - Australia has it right

Environment: The Irish Times reports:

The State is facing a waste crisis that is threatening to bury the country, according to the Minister for the Environment, Mr Cullen. He said yesterday every person in this State was now producing 700 kg of household and commercial waste a year.

'That is three times more than they do in the Netherlands. If this continues, the figure will rise to two tonnes per person by 2015,' he said.

Landfills in six out of 10 regions in the country had less than three years capacity left, yet people were producing enough waste to cover every single town in Ireland. 'We have to change. Doing nothing is not an option,' Mr Cullen said.

Well, duh. So what have they done? They've setup a website, raceagainstwaste.com, with a page on recycling replete with techie details of how recycling works, then suggesting such gems as 'if they do not already run one, suggest to your local authority that it considers starting a plastics recycling scheme.'

Brilliant. I'm sure they'll listen. Nice delegation, Mr Cullen!

In the meantime, apparently 92.2% of the 'waste stream' is sent to landfills instead of recycling.

I'm not just knocking here -- the amazing thing about recycling is that it's been done right elsewhere. All this wheel-reinvention is totally superfluous. Here's the details on Victoria, Australia's kerbside recycling system; it's pretty simple.

Each household gets 1 large basin-type plastic tray thing, in which you can put washed, unsealed, recyclable plastic containers. You tie up bundles of recyclable paper into another pile when you leave out the rubbish. And finally, you get a wheelie bin for the rest; stuff that really is rubbish. The bin guys then keep the 3 types of rubbish separate when they pick it up.

Yes, it takes a little bit of time to wash the plastic containers and tie up the paper into bundles. But nobody minds; they're doing the right thing! It's a hell of a lot better than chucking the lot into a single container and hoping that some expensive machine at the far end can sort it all out again.

It's also better than the current Irish and US systems, where we're expected to bring certain kinds of trash to a centralized drop-off point ourselves. First off, this is very impractical unless you've got a car to do it in -- and sufficient motivation to do so; and secondly, the bulkiest rubbish -- packaging, paper and plastic -- is not included, just glass.

ireland climate-change carbon

The Bin Tax

Over the past few months, Dublin has seen increasing resistance to newly-introduced rubbish-removal charges, or as they're being called, 'the bin tax'.

The charges are:

  • levied in addition to the 'local services' charges in income tax,
    • which already cover rubbish removal.
      • 80 Euro to 150 Euro per annum currently, with one government report suggesting that they could rise to 635 Euro per annum.
      • a flat fee per year, regardless of quantity -- so there's no incentive to recycle or compost your rubbish to bring that down.
      • not tied to any recycling initiative. The rubbish is still heading for a landfill, in most regions.
      • a flat fee for everyone, regardless of income. So the better-off pay exactly the same amount as a welfare recipient. (There is a waiver of 75 Euro for welfare recipients, but it's discretionary and reportedly not always granted).

The last point is key -- UK residents may be reminded of a similar flat-rate tax introduced by Thatcher in the 80's... and we all know how that ended.

The result is that a large number, 75% of the population in the affected areas, have taken the course of non-payment of the charges.

There's been lots of organised protest throughout Dublin, with constant picketing outside bin depots. Joe Higgins TD (a member of the Dail, the Irish parliament) and County Councillor Clare Daly have spent three weeks in jail so far, due to protesting on this issue.

Now, things are really starting to heat up -- reportedly, the bin workers are starting to support the campaign, refusing to cross protest lines and refusing to drive lorries from depots if protesters are present. In some depots, they have even joined the picketers!

It's not all good though -- yesterday, national news shocking footage (SMIL) of a protester being dragged for several hundred feet by a speeding van.

This one's getting interesting.

ireland dublin politics

Snippets

Bits: BarbieOS, a cutdown version of Debian from Mattel. Really. 'BarbieOS 1.0 is the result of almost a year's worth of marketing research into what pre-adolescent girls want in a mobile Linux solution aimed at being a desktop replacement.' (via Ben)

Great site -- also has US.BLAST.D Worm Wreaks Havoc on US Post Office, Mail Delivery Halted ('Until a patch can be created by Microsoft and deployed by the MCSEs who maintain the nation's critical infrastructure, President Bush has urged all Americans to lock in a safe or a drawer all of their pens, pencils, stamps, white paper and envelopes so that they cannot be exploited by the virus and used to write out more copies of itself.'

-- and An Open Letter from RIAA President Hillary Rosen to Music Pirates Everywhere ('Currently an RIAA-backed online service known as Pressplay allows users to subscribe for $18.95 a month to a small library of popular works and listen to them via half-quality audio streams if they have broadband connections. Users may download 10 songs a month to burn to CDs if they wish. Pressplay exclusively supports the Windows Media Audio format, and therefore each song benefits from active scripting support, expiration dates, copy protection and proven Microsoft security. With embedded scripts, each song can also enhance the user experience by opening web pages featuring more music they might like to buy. After only 8 months online and a strategic partnership with AOL, Pressplay currently boasts more than 100 subscribers and is growing every day.')

Spam: Bayesian comment filter for Movable Type, nifty. Pity it's still using the Paul Graham method, which is not so hot. (thx Antoin!)

music mp3 piracy filesharing drm p2p

The Funniest Thing I've Read

Humour: Guardian Talk: The Barefoot Doctor, live online. This is the funniest thing I've read in months -- thanks Tom!

(Background: 'The Barefoot Doctor' is the 'healer' who writes for The Observer Magazine on 'wellbeing, alternative therapies and medicines and ways to cope with modern life'. Everything can apparently be healed through kidney massage and a few essential oils.)

Q: A case study, Mr Barefoot: my bus has crashed - I've got a compound fracture in my right leg, the bone is sticking out from under the skin and is wedged into the 'Used Tickets' receptacle, my skull has had a good old thump against the seat in front and is impersonating a boiled egg after the first thump with the teaspoon, and my ribs have been broken into bits like a packet of smokey bacon crisps someone has stood on.

What herbs and aromatic oils would you recommend?

Doc: you may jest - however, aromatic oils or potions can be extremely effective in speeding the healing process eg - manuka honey,lavender, marigold etc - thanks for bringing it up

Q: oooh good answer. yes i'm going out to buy some manuka honey right away. what do you do with it, is it nice on toast?

lavender, marigolds? is he opening a kitchen department?

Q: My unfortunate friend received a quite severe beating in the street a few days ago and has since been passing blood in his urine, in copius amounts.

Can recomend any effective massage oils for my friend? Its quite urgent because he's beginning to talk incoherently about bright lights, can't move and fainting.

Thank you, 3000

(... snip several hundred similar hilariously bitchy 'questions'... Barefoot Doctor disappears for a while...)

Q: Where is he? Maybe the Barefoot Cab Driver who learnt to drive by karmic chanting has driven into a tree -- or can't find first gear?

(BTW the real 'barefoot doctors' were a different kettle of fish entirely; 'part-peasant, part-doctor' commune-level health workers in revolutionary China.)

funny health history

For Reference: Why Greylisting Sucks

Spam: I've been meaning to collate a page about why I don't like greylisting. My previous posting is relatively useful, but it needs an update, so here it is:

First off, every single message is delayed until a database match is found for the combination of sending IP, envelope-from and envelope-to. As Alan Leghart pointed out, 'So...we punish everyone in the world, and hope that a delay of one or more hours is considered 'acceptable'? Maybe some people already expect a mail to take several hours to reach a recipient. In that case, you need to fix your mail server.'

Secondly, large mailing lists that use VERP (generating keyed From addresses for each mail for good bounce-handling) will require manual whitelisting for each list, or each host.

Yahoo! Groups, for example,
uses VERP for all its lists, and also will not retry delivery if the first attempt fails.

There's even buggy SMTP servers that do not support retrying, believe it or not.

(Once again, as for many spamfilter designs, the unusual SMTP clients are the 'edge cases' that cause the most trouble.)

Manual whitelisting == work == what spam filtering is trying to reduce == bad.

Thirdly, and most seriously, it assumes spammers would never introduce retries into their spam-tools if it took off. Tempfailing, what this is based on, is effective right now because spamtools don't retry. But every proposed spam solution has to consider what would happen if every server admin in the world implements it, and spammers then want to subvert it.

For a spamtool to retry, it just needs to track 4xx responses, and if it encounters one, save these items of data:

  • From, To addrs and HELO string used
  • proxy IP used (btw proxies are almost never shut down successfully, so the spammer can generally assume this can be reused next time)
  • random seed used to generate random hashbuster tokens etc., so the body text matches

That's really not a lot of data -- 64 bytes per address that requires a retry. Then, an hour or more later, do the retry.

So, IMO, 'greylisting' will work fine in the short term, until it becomes reasonably common -- then the spamtool developers will start adding retry code.

Then we're back to square one -- except some legit mail takes much longer to get delivered, and the bandwidth wasted by spam has doubled, due to all those retrying spams. That's not really progress.

anti-spam spam spamassassin smtp email

The Funniest Thing I've Read

Guardian Talk: The Barefoot Doctor, live online. This is the funniest thing I've read in months -- thanks Tom!

(Background: 'The Barefoot Doctor' is the 'healer' who writes for The Observer Magazine on 'wellbeing, alternative therapies and medicines and ways to cope with modern life'. Everything can apparently be healed through kidney massage and a few essential oils.)

Q: A case study, Mr Barefoot: my bus has crashed - I've got a compound fracture in my right leg, the bone is sticking out from under the skin and is wedged into the 'Used Tickets' receptacle, my skull has had a good old thump against the seat in front and is impersonating a boiled egg after the first thump with the teaspoon, and my ribs have been broken into bits like a packet of smokey bacon crisps someone has stood on.

What herbs and aromatic oils would you recommend?

Doc: you may jest - however, aromatic oils or potions can be extremely effective in speeding the healing process eg - manuka honey,lavender, marigold etc - thanks for bringing it up

Q: oooh good answer. yes i'm going out to buy some manuka honey right away. what do you do with it, is it nice on toast?

lavender, marigolds? is he opening a kitchen department?

Q: My unfortunate friend received a quite severe beating in the street a few days ago and has since been passing blood in his urine, in copius amounts.

Can recomend any effective massage oils for my friend? Its quite urgent because he's beginning to talk incoherently about bright lights, can't move and fainting.

Thank you, 3000

(... snip several hundred similar hilariously bitchy 'questions'... Barefoot Doctor disappears for a while...)

Q: Where is he? Maybe the Barefoot Cab Driver who learnt to drive by karmic chanting has driven into a tree -- or can't find first gear?

(BTW the real 'barefoot doctors' were a different kettle of fish entirely; 'part-peasant, part-doctor' commune-level health workers in revolutionary China.)

funny health life

For Reference: Why Greylisting Sucks

I've been meaning to collate a page about why I don't like greylisting. My previous posting is relatively useful, but it needs an update, so here it is:

First off, every single message is delayed until a database match is found for the combination of sending IP, envelope-from and envelope-to. As Alan Leghart pointed out, 'So...we punish everyone in the world, and hope that a delay of one or more hours is considered 'acceptable'? Maybe some people already expect a mail to take several hours to reach a recipient. In that case, you need to fix your mail server.'

Secondly, large mailing lists that use VERP (generating keyed From addresses for each mail for good bounce-handling) will require manual whitelisting for each list, or each host.

Yahoo! Groups, for example,
uses VERP for all its lists, and also will not retry delivery if the first attempt fails.

There's even buggy SMTP servers that do not support retrying, believe it or not.

(Once again, as for many spamfilter designs, the unusual SMTP clients are the 'edge cases' that cause the most trouble.)

Manual whitelisting == work == what spam filtering is trying to reduce == bad.

Thirdly, and most seriously, it assumes spammers would never introduce retries into their spam-tools if it took off. Tempfailing, what this is based on, is effective right now because spamtools don't retry. But every proposed spam solution has to consider what would happen if every server admin in the world implements it, and spammers then want to subvert it.

For a spamtool to retry, it just needs to track 4xx responses, and if it encounters one, save these items of data:

  • From, To addrs and HELO string used
  • proxy IP used (btw proxies are almost never shut down successfully, so the spammer can generally assume this can be reused next time)
  • random seed used to generate random hashbuster tokens etc., so the body text matches

That's really not a lot of data -- 64 bytes per address that requires a retry. Then, an hour or more later, do the retry.

So, IMO, 'greylisting' will work fine in the short term, until it becomes reasonably common -- then the spamtool developers will start adding retry code.

Then we're back to square one -- except some legit mail takes much longer to get delivered, and the bandwidth wasted by spam has doubled, due to all those retrying spams. That's not really progress.

anti-spam spam spamassassin smtp email

KDE patch, and my cat

Linux: So, I like being able to move windows around using the keyboard very quickly. In particular, one nifty feature of Sawfish was corner.jl, a Sawfish lisp snippet which 'provides functions to move a window into a screen corner.'

Some background: my desktop layout is essentially divided into 4 corners (e.g. 4 xterms in a 'one in each corner' layout), or 2 sides (e.g. mail reader on the left, web browser on the right), depending on the size of the windows.

Using corner.jl, one could just throw the mouse into any part of a window's area, hit a key, and the window would move where you wanted it.

I've since moved to KDE, and missed that functionality. So a while back, I reimplemented it as a patch to kwin. Here it is, and bug 65338 is the KDE bug entry tracking it as a feature request.

Not much traction in persuading the KDE folks to apply it, but hey, that's open source for ya. The patch will always be around anyway ;)

Pets: My cat brings me presents.

Specifically, today he brought me a mouse's liver and left it on the doorstep. At least I think it's a mouse's liver; the scale seems right. No sign of the rest of the mouse, though...

This is with no less than 3 bells on his collar; I don't know how he does it, unless it's simply that the rodents round here are just not used to the concept of predation.

BTW, the mouse's liver wound up flushed down the toilet.

linux kde gnome

Getting Postfix to use an SSH tunnel for outgoing SMTP

Given all the fuss over blocking dynamic IPs due to spam, I've long sent outgoing SMTP via my server (which lives on a static IP). I download my mail from that using fetchmail over an SSH tunnel, and have done for a while. It's very reliable, and that way it really doesn't matter where I download from -- quite neat. Also means I don't have to futz with SMTP AUTH, IMAP/SSL, Certifying Authorities, or any of the other hand-configured complex PKI machinery required to use SSL for authentication.

However, I've been using plain old SMTP for outgoing traffic, by just poking a hole in the access db for the IP I'm on. A bit messy and generally not-nice.

So I decided to make it sensible and deliver using SMTP-in-an-SSH-tunnel. In the same SSH tunnel, in fact ;) With Postfix, it turned out very easy -- here's how to do it:

Add this option to the SSH commandline in the SSH tunneling script (I'm presuming you have one ;):

-L 8025:127.0.0.1:25

That'll port-forward port 25 on the remote system to port 8025 on localhost, so that if a connection is made to port 8025 on localhost, it'll talk to port 25 on the remote host. Std SSH tunneling there.

Now for Postfix -- add this to /etc/postfix/main.cf:

default_transport = smtp:localhost:8025

This means that Postfix will always use SMTP to localhost on port 8025 for any non-local deliveries.

Run service postfix reload (cough, Red Hat-ism) and that's it! A whole lot easier than I was expecting... Postfix rocks.

smtp anti-spam email spamassassin

SPF again

Spam: Craig is publishing SPF records. Worth noting that I've been publishing SPF records for jmason.org for a month or two, even though the protocol hasn't even stabilised yet -- working on the 'if you build it, they will come' approach ;)

Anubis looks great; I've been meaning to hack up something like that. Nifty!

spamassassin spam anti-spam

'It will solve starvation among shareholders, but not the developing world'

Science: EU broadside at GM firms' 'lies' (Ananova):

'They tried to lie to people, they tried to force it upon people ... it is the wrong approach and we simply have not accepted that and European citizens have not accepted it. You simply cannot force it upon Europe.

'So I hope they have definitely learned a lesson from it and especially when they now try to argue that this will try to solve the problems of starvation in the world. After all, why didn't they start with such products, so they could prove to the world that this was exactly what they were interested in doing?

'It will solve starvation among shareholders, but not the developing world unfortunately.

That's the EU Environment Commissioner, Margot Wallstrom, launching a broadside against 'US biotech companies', accusing them of 'forcing' unsuitable GM technology onto Europe.

Ouch.

It's interesting to note that much of their biotech companies' tactics seem to work well in the US, but overseas, the tactics play out predominantly as blatant strong-arming, astroturfing support, and being 'economical with the truth', as the phrase goes.

Some rethinking of their strategy might be helpful -- although really, IMO, some thought as to how to make their products relevant to consumers, instead of money-spinning for their shareholders, might work best of all. Making some moves towards the much-vaunted 'solving starvation in the developing world' might just be the best way to that.

climate-change uk ireland

'It will solve starvation among shareholders, but not the developing world'

EU broadside at GM firms' 'lies' (Ananova):

'They tried to lie to people, they tried to force it upon people ... it is the wrong approach and we simply have not accepted that and European citizens have not accepted it. You simply cannot force it upon Europe.

'So I hope they have definitely learned a lesson from it and especially when they now try to argue that this will try to solve the problems of starvation in the world. After all, why didn't they start with such products, so they could prove to the world that this was exactly what they were interested in doing?

'It will solve starvation among shareholders, but not the developing world unfortunately.

That's the EU Environment Commissioner, Margot Wallstrom, launching a broadside against 'US biotech companies', accusing them of 'forcing' unsuitable GM technology onto Europe.

Ouch.

It's interesting to note that much of their biotech companies' tactics seem to work well in the US, but overseas, the tactics play out predominantly as blatant strong-arming, astroturfing support, and being 'economical with the truth', as the phrase goes.

Some rethinking of their strategy might be helpful -- although really, IMO, some thought as to how to make their products relevant to consumers, instead of money-spinning for their shareholders, might work best of all. Making some moves towards the much-vaunted 'solving starvation in the developing world' might just be the best way to that.

climate-change uk science

Firing Automatic Weapons Upwards Considered Harmful

Humour: BBC: Serbia wedding guests 'down plane'.

Guests at a wedding in central Serbia have apparently shot down a small aircraft by mistake.

They were celebrating in the traditional way - firing off shot after shot into the air above the wedding party. Unfortunately, there was a two-seater aircraft flying overhead. One eye-witness told reporters the plane was shot in the left wing.

oops!

Spam: Spammers try fooling filters with digital signatures (ZDNet). oh look, they quote myself and Theo ;)

funny safety spam anti-spam

BitTorrent and Google's IP

Tech: Sam Ruby on Foo Camp. Foo camp sounds cool; a little bit circle-jerky, but still interesting. But that's not what I wanted to write about -- the thing I wanted to mention was BitTorrent; it just struck me recently -- one key thing about BT that makes it great is that it's designed by the UNIX philosophy -- make one tool that does one thing very well, and make it pluggable, so it can be used by other things easily.

It doesn't have a GUI to search for torrents -- the user does that in their web browser, mail, by swapping notes on napkins, whatever. It just does P2P file transfer very very well -- and that's file transfer of some file or another, hence legality issues around P2P are side-stepped. BT is cool.

Patents: Cluetrain on patents:

Well, Google is (jm: going after patents). And the VCs are paying for it. Hell, some of them insist on it. That's what I gathered last night, while schmoozing at the opening evening at PC Forum. First, Larry Page, Google's founder and CEO, told me he hates patents and would rather not deal with them as an issue at all. Then Google board member and lead VC John Doerr surprised a small gaggle of patent skeptics (including Page, Dave Winer and myself) that he loved patents. Patents are one of the things that make America great, he said, and went on to insist that they encourage innovation, cure cancer, raise the dead, and bring peace in our time. (Or something like that. Whatever, he likes patents a lot). So don't expect Google to abandon their hunt for patent lawyers anytime soon.

Listening to John, I began to think one problem is that just caring about patents puts your mind inside the system, where it gets stuck to intellectual flypaper. Or worse, political flypaper.

copyright piracy filesharing law networking ip

SMTP Sender Authentication

Spam: SMTP Sender Authentication, by David Jeske of Y! Groups (pointer from Jeremy.

Schemes similar to this -- calling back to a sending server to verify that a mail was really sent via that host -- have been proposed before in several venues, the most high-profile and public being the ASRG list. Here is a message I sent to that list in April 2003 discussing a few of those schemes:

  • J C Lawrence's 'forward chained digital signatures' on Received headers
  • William at elan.net's 'complex callback verification requirying full message tracking server functionality with dns extensions'
  • Russ Nelson's Q249
  • Our own 'porkhash'

I still like this style of system, I think, but in terms of deployability and simplicity, I'm supporting Sender-Permitted From for now -- which similarly forces senders to use registered relays for a given SPF-supporting domain, but using DNS as the protocol and IP addresses as the hard-to-forge identity component.

Another bonus of SPF is that it's simple, easy to implement, has *running code* out there now, and is being pushed strongly by a pragmatic and sane driving person (in the form of Meng Weng Wong). It's not always easy in the anti-spam field to find a solution like that ;)

BTW, SPF also, similarly, breaks envelope sender forging. However, I agree, this is one egg that has to be broken to help stop spam (or at least force spammers to use their own domains and IPs.)

anti-spam smtp email spamassassin

SMTP Sender Authentication

SMTP Sender Authentication, by David Jeske of Y! Groups (pointer from Jeremy.

Schemes similar to this -- calling back to a sending server to verify that a mail was really sent via that host -- have been proposed before in several venues, the most high-profile and public being the ASRG list. Here is a message I sent to that list in April 2003 discussing a few of those schemes:

  • J C Lawrence's 'forward chained digital signatures' on Received headers
  • William at elan.net's 'complex callback verification requirying full message tracking server functionality with dns extensions'
  • Russ Nelson's Q249
  • Our own 'porkhash'

I still like this style of system, I think, but in terms of deployability and simplicity, I'm supporting Sender-Permitted From for now -- which similarly forces senders to use registered relays for a given SPF-supporting domain, but using DNS as the protocol and IP addresses as the hard-to-forge identity component.

Another bonus of SPF is that it's simple, easy to implement, has *running code* out there now, and is being pushed strongly by a pragmatic and sane driving person (in the form of Meng Weng Wong). It's not always easy in the anti-spam field to find a solution like that ;)

BTW, SPF also, similarly, breaks envelope sender forging. However, I agree, this is one egg that has to be broken to help stop spam (or at least force spammers to use their own domains and IPs.)

anti-spam smtp email spamassassin internet

Iraq: guerrilla tactics planned from the start?

Iraq: Parallels with Vietnam becoming ominous for US commanders (Irish Times, subscriber-only). An interesting view on the situation Iraq:

US commanders in Iraq now believe that during the invasion, lower-echelon Iraqi troops mounted a token defence against US armour and air power while thousands of Republican Guard members went to ground in order to wage a prolonged guerrilla war during the subsequent occupation.

As the current attacks evolve in sophistication and momentum, US troops believe that the current phase of the war is not an ad-hoc development, but part of a pre-planned strategy designed to frustrate US plans to rebuild Iraq.

Further indicators as to the source of the insurgency lie in the weaponry and tactics employed. US convoys and patrols are repeatedly attacked with IEDs configured as roadside bombs along with RPG strikes. ... It is believed that the plastic explosives and RPGs were released from military stores in the run-up to the invasion and pre-deployed among the population for a war of attrition.

Wounding rather than killing the enemy is a classic feature of this type of war of attrition. By wounding as many enemy troops as possible, the guerrilla army ties up the resources of the occupying force as it seeks to evacuate and treat its personnel.

The architects of the current attacks recognise that it is far more expensive for the US to medically evacuate and treat injured soldiers than to simply process them for burial. For the insurgents, the psychological effect of their attacks is greatly enhanced with families and politicians in the US confronted with mutilated and disfigured soldiers returning from Iraq.

It would appear that the war in Iraq did not end on May 1st. It simply entered a new phase designed to render Iraq ungovernable.

No 'US commanders' are named, so it's all off-the-record.

Humour: on a lighter note, BBC Radio 4's Loose Ends, recorded in the Spiegeltent in Dublin last weekend, featuring 'writers Anne Enright and John Arden, Desmond Guinness of the Irish Georgian Society, comedian Dara O'Briain, Chieftain Paddy Moloney and Loose Ends regular Emma Freud.'

terrorism politics us-politics radio

Iraq: guerrilla tactics planned from the start?

Parallels with Vietnam becoming ominous for US commanders (Irish Times, subscriber-only). An interesting view on the situation Iraq:

US commanders in Iraq now believe that during the invasion, lower-echelon Iraqi troops mounted a token defence against US armour and air power while thousands of Republican Guard members went to ground in order to wage a prolonged guerrilla war during the subsequent occupation.

As the current attacks evolve in sophistication and momentum, US troops believe that the current phase of the war is not an ad-hoc development, but part of a pre-planned strategy designed to frustrate US plans to rebuild Iraq.

Further indicators as to the source of the insurgency lie in the weaponry and tactics employed. US convoys and patrols are repeatedly attacked with IEDs configured as roadside bombs along with RPG strikes. ... It is believed that the plastic explosives and RPGs were released from military stores in the run-up to the invasion and pre-deployed among the population for a war of attrition.

Wounding rather than killing the enemy is a classic feature of this type of war of attrition. By wounding as many enemy troops as possible, the guerrilla army ties up the resources of the occupying force as it seeks to evacuate and treat its personnel.

The architects of the current attacks recognise that it is far more expensive for the US to medically evacuate and treat injured soldiers than to simply process them for burial. For the insurgents, the psychological effect of their attacks is greatly enhanced with families and politicians in the US confronted with mutilated and disfigured soldiers returning from Iraq.

It would appear that the war in Iraq did not end on May 1st. It simply entered a new phase designed to render Iraq ungovernable.

No 'US commanders' are named, so it's all off-the-record.

Humour: on a lighter note, BBC Radio 4's Loose Ends, recorded in the Spiegeltent in Dublin last weekend, featuring 'writers Anne Enright and John Arden, Desmond Guinness of the Irish Georgian Society, comedian Dara O'Briain, Chieftain Paddy Moloney and Loose Ends regular Emma Freud.'

politics us-politics terrorism

Happiness measured

Science: Fantastic article in New Scientist volume 180 (4 Oct 2003), covering how science is beginning to identify the keys to a happy life, and perform studies measuring people's happiness.

That's a subscribers-only link unfortunately, but I'll excerpt a few choice snippets:

First off, money:

Can money buy happiness? The short answer is, yes - but it doesn't buy you very much. And once you can afford to feed, clothe and house yourself, each extra dollar makes less and less difference. ... In the past half-century, average income has skyrocketed in industrialised countries, yet happiness levels have remained static (see Graph). It seems absolute income doesn't make much difference once you have enough to meet your basic needs. Instead, the key seems to be whether you have more than your friends, neighbours and colleagues.

Looks:

First the bad news: good-looking people really are happier. When Diener got people to rate their own looks, both with and without make-up, there was a 'small but positive effect of physical attractiveness on subjective well-being'.

But don't compare your looks with what the media puts out:

In a new study, Laurie Mintz and her colleagues from the University of Missouri-Columbia found that women who saw advertisements featuring lithe and flawless young models for just one to three minutes rated their own bodies more negatively and showed an increase in depression. Mintz was alarmed how quickly the women's self-esteem was undermined. And she believes people are becoming more dissatisfied as new technology allows the media to create ever more unrealistic images.

Mintz recommends less drastic steps to contentment: avoid unrealistic media images; understand that such pictures are airbrushed and 'Photoshopped' to perfection; appreciate your body for what it does rather than how it looks.

Friends:

It is hard to imagine a more pitiful existence than life on the streets of Calcutta or in one of its slums, or making a living there as a prostitute. Yet despite the poverty and squalor they face, such people are much happier than you might imagine. 'We think social relationships are partly responsible,' says Diener.

And a global comparison:

The latest global analysis of how levels of satisfaction and happiness vary from country to country shows that the most 'satisfied' people tend to live in Latin America, Western Europe and North America. Eastern Europeans are the least satisfied.

... There is plenty more about national happiness levels that has researchers scratching their heads. One of the most significant observations is that in industrialised nations, average happiness has remained virtually static since the second world war, despite a considerable rise in average income (see Graphic). The exception is Denmark, where people have become more satisfied with life over the past 30 years - no one is quite sure why.

and the effects of consumerism:

A growing number of researchers are putting the static trend down to consumerism. Survey after survey has shown that the desire for material goods, which has increased hand in hand with average income, is a 'happiness suppressant'.

One study, by Tim Kasser at Knox College in Galesburg, Illinois, found that young adults who focus on money, image and fame tend to be more depressed, have less enthusiasm for life and suffer more physical symptoms such as headaches and sore throats than others (The High Price of Materialism, MIT Press, 2002). Kasser believes that people tend to embrace material values when they are feeling insecure (retail therapy, anyone?). 'Advertisements have become more sophisticated,' says Kasser. 'They try to tie their message to people's psychological needs. But it is a false link. It is toxic.'

Lots of good bits. Pity it's subscribers-only!

society life climate-change

EMusic is dead

Music: All good things must come to an end. EMusic has been bought out by some bunch called 'Dimensional Associates', and will no longer offer its excellent download service; instead you're limited to a measly 40 MP3s per month. (For context -- last time I downloaded some listening material was on Monday, and I picked up about 80 MP3s in a single sitting.)

They've shut down their message boards; third-party discussion groups are filled with wailing and gnashing of teeth; and worst of all, I can't even download the remaining stuff on 'My Stash' (the downloads-to-do list) because they're overrun with rats deserting the sinking ship. (no reflection on the rats -- I'm one myself.) Either that, or they've just turned them off; which is annoying as I had lots of music lined up to download when I got a chance.

This is very bad news -- Apple's iTunes is full of crappy music, Mac-only, and DRM-crippled; Rhapsody is Windows-only and DRM-crippled; there's really no other legal MP3-download option.

I guess I'll just have to go back to buying 1 or 2 CDs every few months when I'm buying stuff from Amazon (which I do nowadays anyway, in addition to EMusic) and just listening to the radio in general instead.

Thanks anyway, EMusic, for introducing me, helping me get into, or helping me rebuild my collection of such great music as:

  • Ladytron
  • Lemon Jelly
  • Belle and Sebastian
  • TRS-80
  • Yo La Tengo
  • Pepe Deluxe
  • Layo And Bushwacka
  • Asian Dub Foundation
  • The Pixies
  • Stereolab
  • Johnny Cash
  • Future Sound of London
  • Freq Nasty
  • Matmos
  • Cornershop
  • Thievery Corporation
  • Cocteau Twins

It was great while it lasted.

Ah well, I guess I'll save a tenner a month, which I can put towards the GameFly subscription...

music drm mp3 linux piracy ireland filesharing ip

Spammer 'Cloaking Devices'

Spam: Cloaking Device Made for Spammers (Wired).

'Try to find the real IP,' he said. 'This host is in rackshack.net, the most antispam ISP.' A traceroute to the site indicated that it was being hosted on a computer apparently using cable modem service from Comcast.

It's using DNS trickery and a set of reverse proxies. This is standard practice among a small number of the upper echelon of spammers these days.

Of course, many of the techniques used to do this -- such as the subversion of Wintel PCs on cable modem networks -- are highly illegal, so the spammer/crackers are heading deep into jail-time territory.

I'm really posting this because of this entry at Boing Boing, in which Cory notes: 'I'm pretty skeptical about the untraceability of these systems -- I suspect that rather, they are resistant to some tools, not resistant to others, and not hard to write new tools to uncover.'

They're untraceable from where we're standing -- these are compromised machines. The only way to trace from that machine onwards, is for the abuse staff of those machines' ISPs to help out, or to get hold of the machine itself. This is not so easy -- which is why the spammers do it.

(I would have posted this as a comment on BB!, but they've stopped accepting comments, as noted previously. grr)

Anyway. As time goes on, the development of Wintel spamware-installing worms, and hands-on cracking of Unix servers to install trojans (PDF), is becoming more and more common. There's definitely an increasing crossover between spammers, virus-writers and crackers, as the Wired News article notes.

This is very much illegal activity under existing computer crime laws, and much more serious than whatever the anti-spam legislation out there considers spamming to be. Maybe the big spammers are going increasingly 'all-out', given that the lawmakers are finally giving the anti-spam laws some teeth...

spam anti-spam security

USPTO 'chime in' with tips for EU's patent laws

Patents: While I was reading LWN's excellent writeup on the results of the EuroParl patent vote, I came across this very worrying snippet:

Readers in the United States may be interested to know that the U.S. government has chimed in with opposition to article 6a, which states that patents can not be used to block interoperability.

Sure enough, it links to an FFII page noting

'the US' believes that conversion between patented file formats should generally not be allowed without a license, and therefore demands deletion of Art 6a.'

'the US' is in quotes because FFII reckon that evidence suggests that this is the US Mission's IPR representatives forwarding the text direct from the US Patent Office, since the USPTO is an agency of the Dept of Commerce.

.... 'It is part of a US Government 'Action Plan' to 'promote international harmonisation of substantive patent law' in order to 'strengthen the rights of American intellectual property holders by making it easier to obtain international protection for their inventions'. This plan has been promoted aggressively by top officials of the US Patent Office in international fora such as WIPO, WSIS and OECD as well as through bilateral negotiations.'

BTW, that is exactly the wording used in the USPTO's 21st Century Strategic Plan paper. FFII go on to comment on their letter, including this note:

'The US' is propagating conventional wisdom such as 'the more patents the more property, the more property the more innovation', which is in sharp contrast to consensus of all serious scholars of software economics, as expressed in numerous studies conducted in the USA and in reports by the US Academy of Sciences.

Moreover, 'the US' has been ignoring the voice of its own software industry, which is, as shown by last year's FTC hearings, characterised by 'continued animosity against software patents' and whose major players, including such companies as Adobe, Oracle and Autodesk, all opposed software patentability at the USPTO hearing of 1994. The same USPTO which is ghostwriting this paper in the name of 'the US' today proceded to legalise program claims shortly after the 1994 hearing, thereby completely ignoring the voice of the US software industry.

One comment on the LWN story notes: 'as the United States is seeking to rewrite European law to their
agenda, what steps can European Citizens take to help turn the USPTO agenda around into something approaching the spirit of the US Constitution and those who wrote it?'

A good question.

eu us security patents swpats law

Mekong Naga fireballs

Odd: Naga fireballs: Timing still a mystery for scientists (Bangkok Post):

Methane and phosphine, a mix of phosphorus and hydrogen, were found in waterways near the Mekong. These gaseous substances were believed to cause the fiery balls, researchers said, though they were not sure exactly how or why they occur. Plant and animal remains release methane as they break down which probably combines with chemical fertiliser, containing phosphorus nutrient, used on farms in the area, to cause the fireballs. The soil in the riverbed is rich with the element.

However, the occurrence of crimson balls also required energy and microbes, which researchers cannot explain.

Mr Saksit called inexplicable aspects of the display a miraculous event while Mr Pinit predicted the study would cause him more headaches. He still did not know why the fireballs tended to emerge only on the full moon night of the 11th lunar month every year.

Laos to 'cash in' on Naga fireballs (The Nation):

Authorities from Vientiane Municipality's Pak Ngum district and the Lao National Authority have prepared sites along the banks of the Mekong River and its tributary, the Nam Ngum, for tourists to view the fireballs rising from the currents tomorrow night, an official said yesterday.

Pak Ngum, where the Nam Ngum river meets the Mekong, is located some 50 kilometres south of the Laotian capital and opposite Nong Khai's Phon Pisai district. Although it has no hotels, residents are willing to provide home stays for tourists, said an official at the Pak Ngum district office.

Spam: CNET removes anti-spam software 'made by spammers' (The Reg). oops!

science odd travel anti-spam

Diebold voting machines, DMCA, Michael Moore

e-Voting: Wired has an absolutely mind-numbing list of issues with the security of Diebold voting machine procedures, including passwords printed in manuals which the staff can take home, that same password being reused for multiple systems including the on-site machines at polling stations, tamper-resistance measures being omitted, poll supervisors hired without background checks, bicycle locks being used to secure voting machines, one shared key used to 'secure' the memory cards, etc.

'The election process is mainly based on trust,' Ginnold said. 'We trust that poll workers are not going to be tampering with them.'

It's simply insane to replace a known-good voting system (even if it's just First-Past-the-Post instead of Proportional Representation, but that's another issue) with a quick hack like this, IMO.

Please vote anyway, if you're a CA citizen. And not for the fondling meathead, naturally.

DMCA: EFF: Unintended Consequences: Five Years under the DMCA. An incredible list of cases where the DMCA was used unfairly to restrict competition, research, or fair use, some of which I didn't even know about. For example, I didn't realise that the International Information Hiding Workshop Conference will no longer hold conferences on US soil after Professor Ed Felten was threatened over their SDMI paper.

Politics: Michael Moore on how to talk to your conservative brother-in-law. MM may play to the gallery now and again, but sometimes, he's a genius:

Paying workers more money makes you money!

Dear brother-in-law, when you don't pay people enough for them to take care of life's essentials, it ends up costing you and everybody else a lot of money. When you pay your employees more money, what do you think they do with it? Invest it in stocks? Hoard it in offshore accounts? No! They spend it! And what do they spend it on? The stuff you make and sell! If you pay people squat, or lay them off, they can't buy your stuff. They become a drain on the economy; some turn to crime, and when they turn to crime, it's your Mercedes they want, not some junker Oldsmobile in their poor neighbour's driveway.

Science: IgNobel prize winners 2003, including a prize for the nation of Liechtenstein for renting out the entire country for 'corporate conventions, weddings, bar mitzvahs, and other gatherings'.

e-voting security ireland voting elections nsa politics funny

Idyllwild and Language Trivia

Life: so myself and C took a one-night-only trip up to Idyllwild this weekend, hiking up to that rock formation and camping overnight. Great fun.

The rock is called 'Suicide Rock'. It's good to see morbid naming is international, but I should note that the prize for best placenames has to go to Victoria, Australia's Mount Buggery, though.

(I drove past Mt. Buggery last year, and, disappointingly, it seems they've renamed it on the official maps. But the other 'I can't believe we're still crossing this bloody mountain range and haven't made it to Melbourne yet' placenames still exist.)

Language: Riverbend blog notes interesting trivia in passing: Winnie the Pooh, in Arabic, is 'Winnie Dabdoob'.

Open Source: GROKLAW on the WSIS fiasco earlier this summer. Briefly, the WSIS -- the World Summit on the Information Society -- came out with a position pro-open-source, and quite a few large companies seemed to say 'eek!' and promptly lobbied as hard as they could to give that line a vasectomy.

Interestingly, they did the same to the spam-related positions, cutting 'a number of proposals, including prosecution of spammers' down to a watery 'take appropriate action on spam at national and international levels'. Snore. Fantastic work, guys.

Weblogs: When did Boing Boing stop taking comments? (looks) seems to be around about this entry of Sep 10. As far as I can see, this is the last comments page.

Shame -- I'm with Jeremy on this one.

Dublin: is this entry, by London's 3W the real winner of the competition to design the new U2 studio in Dublin's Sir John Rogerson's Quay?

history uk gaming funny google

Booting Linux

Linux: so it seems one of the GNOME guys wants to rewrite the rc.d boot script system in Python. Eek!

Games: Someone has broken into Valve Software's network and stolen the source code for Half-Life 2 -- shacknews:

  • 1) Starting around 9/11 of this year, someone other than me was accessing my email account. This has been determined by looking at traffic on our email server versus my travel schedule.
  • 2) Shortly afterwards my machine started acting weird (right-clicking on executables would crash explorer). I was unable to find a virus or trojan on my machine, I reformatted my hard drive, and reinstalled.
  • 3) For the next week, there appears to have been suspicious activity on my webmail account.
  • 4) Around 9/19 someone made a copy of the HL-2 source tree.
  • 5) At some point, keystroke recorders got installed on several machines at Valve. Our speculation is that these were done via a buffer overflow in Outlook's preview pane. This recorder is apparently a customized version of RemoteAnywhere created to infect Valve (at least it hasn't been seen anywhere else, and isn't detected by normal virus scanning tools).

Insanely bad news for Valve. :(

security hacks malware

Florida State Government Spammed Me!

Spam: Well, this is just incredible. I've just been spammed by a .gov domain -- myfloridahousemail.gov.

The irony of my first .gov spam coming from Florida is inescapable.

The message came from an IP address registered to State of Florida/Dept. of Management Services, bldg 4050 esplanade way suite 115d, Tallahassee, FL 32399-0950 US. That address looks genuine. It really does look like it came from the Florida House of Representatives.

And it was sent to a spamtrap which is on a few spammer address lists, but has never been a genuine user address. And, obviously, I don't live in Florida ;)

Read the spam here.

spam anti-spam smtp

Another bad USPTO software patent

Patents: MS patents 'phone-home' failure reporting.

There's a catch, in that it's not just plain old 'phone home', as seen in probably a hundred products since 1960 -- they've added a 'match the reported error messages against a db of known issues on the server side' step. So that's vaguely inventive -- well, no, it's totally obvious, but at least nobody I can think of off the top of my head has done that before. (Well, I lie, it sounds a bit like KDE's crash reporting tool which does a similar search before reporting a bug.)

The notable comment, though, is
this:

There is a significant institutional culture issue that has a strong influence on how the Office functions that took root several decades ago and has, regretfully, increased, monotonically, over time. The management attitude, in a nutshell, is that patents aren't 'examined', they are 'processed'. The examination process is driven by production 'goals'; to be rated in the key rating category of 'Production Goal Achievement' as 'fully successful' you must have at least 95%; less than that you are marginal; less then 90% you are 'unsatisfactory', meaning your entire rating is 'unsatisfactory' meaning a '90 day letter' to get it 'fully successful' else you are fired. Also there are other time related requirements to meet, such as no amended application pending more than two months without an action. Persons get fired (yes, this does happen) almost always for low production or exceeding time limits for actions, almost never for improperly allowing claims.

Great.

Tech: It seems it's stunningly easy to rip off GPRS customers. Another well-designed system I don't think.

patents swpats patenting coding uspto linux

Another bad USPTO software patent

MS patents 'phone-home' failure reporting.

There's a catch, in that it's not just plain old 'phone home', as seen in probably a hundred products since 1960 -- they've added a 'match the reported error messages against a db of known issues on the server side' step. So that's vaguely inventive -- well, no, it's totally obvious, but at least nobody I can think of off the top of my head has done that before. (Well, I lie, it sounds a bit like KDE's crash reporting tool which does a similar search before reporting a bug.)

The notable comment, though, is
this:

There is a significant institutional culture issue that has a strong influence on how the Office functions that took root several decades ago and has, regretfully, increased, monotonically, over time. The management attitude, in a nutshell, is that patents aren't 'examined', they are 'processed'. The examination process is driven by production 'goals'; to be rated in the key rating category of 'Production Goal Achievement' as 'fully successful' you must have at least 95%; less than that you are marginal; less then 90% you are 'unsatisfactory', meaning your entire rating is 'unsatisfactory' meaning a '90 day letter' to get it 'fully successful' else you are fired. Also there are other time related requirements to meet, such as no amended application pending more than two months without an action. Persons get fired (yes, this does happen) almost always for low production or exceeding time limits for actions, almost never for improperly allowing claims.

Great.

Tech: It seems it's stunningly easy to rip off GPRS customers. Another well-designed system I don't think.

patents coding swpats uspto patenting ip

Shark Sandwich

Comedy: some Spinal Tap snippets:

  • a review of a live performance, noting the demise of the band's own Web-based music downloading service, Tapster -- David St. Hubbins is quoted saying 'they shut down Tapster out of force of habit.'
  • Derek Smalls notes regarding Tapster, 'It has to start with saying, 'look we're worried about being ripped off', so we started TAPSTER ourselves...so we're ripping ourselves off. If a problem comes up, we'll sue ourselves and we'll pocket the difference.' (guess this was before the aforementioned shutdown.)
  • The A-Z of Spinal Tap: 'For U2's Popmart tour, the show's designer Willie Williams and the band decided the group should emerge from a giant lemon.' ... 'The Edge comes down from the stairs, and to start his guitar he has to kick a switch on his foot-pedal. Well, he ended up on his hands and knees, feeling around for the pedal. Later he said to me, 'There I was at the debut, the premiere opening night, and this voice came into my head: I'm Derek Smalls.''
  • So, as mentioned in the movie, Nigel and David grew up in Squatney, East London. But did you know that Derek Smalls grew up in Nilford -- 'a 'very small, very wretched, very dire little place' on the River Null, near Wolverhampton. Also known as Nilford-on-Null.'

funny music filesharing mp3

Spammers Now Relaying via SMTP AUTH

Spam: A nasty new development -- spammers are now exploiting closed relays to send spam, by brute-force attacking their SMTP AUTH interfaces. SMTP AUTH is a system used to allow legitimate mail server users to send outgoing mail securely, by authenticating them first. ( sample documentation here.)

This ROKSO file indicates one spammer's modus operandi:

These relays were abused using SMTP AUTH. That is, the spammer supplied a valid username/password pair to the server, was authenticated, and therefore granted permission to send mail anywhere. Such attacks are therefore successful only when weak passwords are used. This spamhaus constantly scans the net to find abusable servers to use in subsequent spam runs. All brands of servers (sendmail, exchange, mdaemon, rockcliffe, etc) are equally targeted, as long as they support SMTP AUTH. The attacker tries several username/password pairs - such as with 'admin/admin' - following a certain pattern and hoping to find a combination that lets him in.

An analysis done in july 2003 has shown that a total of 276 combinations are attempted (of course new ones can have been added in the meanwhile): Usernames: webmaster, admin, root, test, master, web, www, administrator, backup, server, data, abc each with the following passwords: username, username12, username123, 1, 111, 123, 1234, 12345, 123456, 1234567, 12345678, 654321, 54321, 00000000, 88888888, admin, root, pass, passwd, password, super, !@#$%^&* as well as with a blank password.

MDaemon users beware! The account creation tool of recent versions of MDaemon defaults the password to the account name. If the default is accepted, the account will be open to be exploited by this spamhaus.

Incredible. There's no way at the SMTP/IP level to tell that this relay was compromised; blacklisting will definitely cause collateral damage in response; so content analysis is pretty much necessary, as far as I can see.

And in another worrying development: it turns out that the latest Outlook worm, W32.Swen, doesn't bother trying to randomly generate usernames etc. or send via SMTP directly. Instead, it asks the user for their username, password and SMTP server!

anti-spam smtp email spam spamassassin backscatter

Spammers Now Relaying via SMTP AUTH

A nasty new development -- spammers are now exploiting closed relays to send spam, by brute-force attacking their SMTP AUTH interfaces. SMTP AUTH is a system used to allow legitimate mail server users to send outgoing mail securely, by authenticating them first. ( sample documentation here.)

This ROKSO file indicates one spammer's modus operandi:

These relays were abused using SMTP AUTH. That is, the spammer supplied a valid username/password pair to the server, was authenticated, and therefore granted permission to send mail anywhere. Such attacks are therefore successful only when weak passwords are used. This spamhaus constantly scans the net to find abusable servers to use in subsequent spam runs. All brands of servers (sendmail, exchange, mdaemon, rockcliffe, etc) are equally targeted, as long as they support SMTP AUTH. The attacker tries several username/password pairs - such as with 'admin/admin' - following a certain pattern and hoping to find a combination that lets him in.

An analysis done in july 2003 has shown that a total of 276 combinations are attempted (of course new ones can have been added in the meanwhile): Usernames: webmaster, admin, root, test, master, web, www, administrator, backup, server, data, abc each with the following passwords: username, username12, username123, 1, 111, 123, 1234, 12345, 123456, 1234567, 12345678, 654321, 54321, 00000000, 88888888, admin, root, pass, passwd, password, super, !@#$%^&* as well as with a blank password.

MDaemon users beware! The account creation tool of recent versions of MDaemon defaults the password to the account name. If the default is accepted, the account will be open to be exploited by this spamhaus.

Incredible. There's no way at the SMTP/IP level to tell that this relay was compromised; blacklisting will definitely cause collateral damage in response; so content analysis is pretty much necessary, as far as I can see.

And in another worrying development: it turns out that the latest Outlook worm, W32.Swen, doesn't bother trying to randomly generate usernames etc. or send via SMTP directly. Instead, it asks the user for their username, password and SMTP server!

anti-spam smtp spam email

find-hidden-word-text - read hidden text in Word docs

find-hidden-word-text - a command-line UNIX tool to ease the task of discovering hidden text in MS Word documents.

More specifically, it is an implementation of Method 2 from Simon Byers' paper, Scalable Exploitation of, and Responses to Information Leakage Through Hidden Data in Published Documents.

In other words, it'll display just the hidden text (if any exists) in Word docs. Go forth and discover accidental leaks!

security unix privacy

Art-Market, ArtPrice, Servergroup, Groupe Serveur etc. spamhaus

So a few months ago, I setup a cookie-producing mailto honeypot page at foojlist.php.

Well, I just got the first bite -- and it's a live one. It's our old friends at artprice.com. They're a French spamhaus, operating from Saint-Romain-au-Mont-d'Or, France, and reports claim that it's all the work of one guy -- Thierry Ehrmann.

There's lots of reports in USENET, and here's their SBL listing, noting 'extremely intense french spam source.'

This posting to NANAE notes that Colt France are not responding to complaints about them, either -- but notes that 'in France collecting e-mail addresses with the intention to send commercial mails without permission of the holders can be punished by law (article 226-18 of the Code Pe'nal - up to 5 years of prison or 300.000 euro)'. Interesting!

Full details of the spam, and the access_log entries from their web-scraper's accesses, are attached.

Here's the spam:

Received: from mail1.artmarket.com (mail1.artmarket.com [194.242.43.183])
by dogma.slashnull.org (8.11.6/8.11.6) wixh ESMTP id h8SLJZV12710
for < ( email addr deleted ) @fooj.jmason.org>; Sun, 28 Sep 2003 22:19:35 +0100
Date: Sun, 28 Sep 2003 22:19:35 +0100
Message-Id: ...
From: A  R  T ...
To: < ( email addr deleted ) @fooj.jmason.org>
Subject: [adv] 1700 - 2003  Story of the Art Market
MIME-Version: 1.0
Content-Type: text/html;    charset=iso-8859-1
Content-Transfer-Encoding: 8bit
<HTML><HEAD>
<TITLE>Artists search engine by Artprice TM - copyright Artprice.com</TITLE>
<META http-equiv=''Content-Type'' content=''text/html; charset=iso-8859-1''>
<META name=''UNSUB'' content=''<!--26398522_1-->''>
<META name=''ROBOTS'' content=''NOINDEX''>
</HEAD>
<BODY bgcolor=''#FFFFFF'' text=''#000000''>
<TABLE cellspacing=''0'' cellpadding=''0'' align=''center'' border=''0''>
<TR> 
<TD><IMG src="''http://web.artprice.com/img/affil.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/search.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/fs.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD><A" href="''http://www.artistbiography.com/''><IMG" src="'http://web.artprice.com/img/bio.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/sig.gif''></TD>
<TD><A" href="''http://web.artprice.com''><IMG" src="'http://web.artprice.com/img/Home.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/G.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ps.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD><A" href="''http://web.artprice.com''><IMG" src="'http://web.artprice.com/img/Home.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/I.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/sig.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/fs.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/I.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B>A</B></TD>
<TD><IMG src="''http://web.artprice.com/img/map.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B>R</B></TD>
<TD><IMG src="''http://web.artprice.com/img/HelpBlack.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/search.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/AMI/AMInsight.gif''></TD>
</TR>
<TR>" 
<TD><IMG src="''http://web.artprice.com/img/Shop.gif''></TD>
<TD><A" href="''http://web.artprice.com/corporate/EN/Visite/pages/nb.htm''><IMG" src="'http://web.artprice.com/img/HelpBlack.gif'" border=''0''></A></TD>
<TD align=''center'' bgcolor=''#FF0000''><B>T</B></TD>
<TD><IMG src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/today.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/E.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/F.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B>P</B></TD>
<TD><IMG src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/search.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Shop.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/F.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/G.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Home.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/today.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/D.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/F.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/sig.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/A.gif''></TD>
</TR>
<TR>" 
<TD><IMG src="''http://web.artprice.com/img/Mediums/B.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/D.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/G.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/H.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/I.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B>R</B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/I.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Account.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B>I</B></TD>
<TD><IMG src="''http://web.artprice.com/img/contact.gif''></TD>
<TD><A" href="''http://web.artprice.com/corporate/EN/Visite/pages/3818.htm''><IMG" src="'http://web.artprice.com/img/HelpBlack.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/I.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/today.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B>C</B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/L.gif''></TD>
</TR>
<TR>" 
<TD><IMG src="''http://web.artprice.com/img/Mediums/D.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B>E</B></TD>
<TD><IMG src="''http://web.artprice.com/img/map.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B>C</B></TD>
<TD align=''center'' bgcolor=''#FF0000''><B>O</B></TD>
<TD align=''center'' bgcolor=''#FF0000''><B>M</B></TD>
<TD><IMG src="''http://web.artprice.com/img/Shop.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/G.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Home.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/search.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/sig.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Home.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/fs.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/contact.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/I.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/contact.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ps.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/H.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Account.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/search.gif''></TD>
</TR>
<TR>" 
<TD><IMG src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/B.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/bio.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Shop.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Account.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/today.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/affil.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Account.gif''></TD>
<TD><A" href="''http://www.artprice.net''><IMG" src="'http://web.artprice.com/img/map.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/B.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/L.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/F.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/bio.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Shop.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/B.gif''></TD>
<TD" align=''center''><A href="''http://www.art-online.com''> </A></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Home.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ps.gif''></TD>
</TR>
<TR>" 
<TD><IMG src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/F.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/fs.gif''></TD>
<TD><A" href="''http://www.americanartists.com/''><IMG" src="'http://web.artprice.com/img/bio.gif'" border=''0''></A></TD>
<TD align=''center'' bgcolor=''#000000''><B><FONT color=''#FF0000''>A</FONT></B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/B.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Home.gif''></TD>
<TD><A" href="''http://web.artprice.com/corporate/EN/Visite/pages/arch02.htm''><IMG" src="'http://web.artprice.com/img/HelpBlack.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/Shop.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/affil.gif''></TD>
<TD" align=''center''><B><FONT color=''#FF0000''>R</FONT></B></TD>
<TD><IMG src="''http://web.artprice.com/img/sig.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Account.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/I.gif''></TD>
<TD" align=''center''><B><FONT color=''#FF0000''>T</FONT></B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/affil.gif''></TD>
<TD><A" href="''http://web.artprice.com/corporate/EN/Visite/pages/3834.htm''><IMG" src="'http://web.artprice.com/img/HelpBlack.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/H.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Shop.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/search.gif''></TD>
</TR>
<TR>" 
<TD><IMG src="''http://web.artprice.com/img/bio.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ps.gif''></TD>
<TD" align=''center'' bgcolor=''#FF0000''><B><FONT color=''#000000''>M</FONT></B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/C.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/fs.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ps.gif''></TD>
<TD" align=''center''><B>A</B></TD>
<TD><IMG src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ps.gif''></TD>
<TD" align=''center''><B>R</B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/B.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/F.gif''></TD>
<TD" align=''center''><B>K</B></TD>
<TD><IMG src="''http://web.artprice.com/img/ps.gif''></TD>
<TD><A" href="''http://www.artprice.de''><IMG" src="'http://web.artprice.com/img/Home.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/Shop.gif''></TD>
<TD" align=''center''><B>E</B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/B.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ps.gif''></TD>
<TD" align=''center''><B>T</B></TD>
<TD><A href="''http://web.artprice.com/corporate/EN/Visite/pages/jb02.htm''><IMG" src="'http://web.artprice.com/img/HelpBlack.gif'" border=''0''></A></TD>
</TR>
<TR> 
<TD><IMG src="''http://web.artprice.com/img/contact.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/G.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/contact.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/map.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/affil.gif''></TD>
<TD" align=''center''><B>C</B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/D.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/sig.gif''></TD>
<TD><A" href="''http://www.13thcenturyart.com/''><IMG" src="'http://web.artprice.com/img/HelpBlack.gif'" border=''0''></A></TD>
<TD><IMG src="''http://web.artprice.com/img/Home.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/E.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/affil.gif''></TD>
<TD" align=''center''><B>O</B></TD>
<TD><IMG src="''http://web.artprice.com/img/Account.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/D.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/Mediums/J.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/ind.gif''></TD>
<TD" align=''center''><B>M</B></TD>
<TD><IMG src="''http://web.artprice.com/img/Mediums/I.gif''></TD>
<TD><IMG" src="''http://web.artprice.com/img/bio.gif''></TD>
</TR>
</TABLE>
<BR><BR><BR>
<TABLE" border=''0'' bgcolor=''#FFFFFF'' align=''center''><TR>
<FORM method=get action=''http://web.artprice.com/en/artistsearch.aspx''><TD>
<A href="''http://web.artprice.com''>
<IMG" src="'http://web.artprice.com/Img/B/artprice_140.gif'" align=''absmiddle'' border=''0'' alt=''artprice''></A> 
<INPUT type=text name=searcharti size=39>
<INPUT type=submit value=''OK'' style=''CURSOR: hand''>
<INPUT type=hidden name=l value=en>
</TD>
</FORM>
</TR></TABLE>
<CENTER>
<FONT size=''1'' face=''Arial''>
THE WORLD LEADER IN ART MARKET INFORMATION - WELT-LEADER IN KUNSTMARKT-INFOS
<BR>LEADER MONDIAL DE L'INFORMATION SUR LE MARCHE 
DE L'ART</FONT>
</CENTER>
<BR><BR><BR>
<BR><BR><BR>
<BR><BR><BR>
<BR><BR><BR>
<BR><BR><BR>
<BR><BR><BR>
<BR><BR><BR>
<TABLE cellspacing=''3'' background=''http://web.artprice.com/Img/B/pixBl.gif''>
<TR> 
<TD> <FONT face=''Arial'' size=''1''>
<b>To remove</b> your email: ...
please click below:<br><a 
href="'http://list.artaddiction.com/?m=(email_address_hidden)%40fooj.jmason.org'>
...
</a><br>
In" case the above link does not work you can go to<br>
http://list.artaddiction.com/<br>
or reply to this message as it is.<br>
Please allow us 72 H for your e-mail to be removed.<br>Thank you for your co-operation. </FONT></TD>
<TD><FONT face=''Arial'' size=''1''>
<b>Pour désinscrire</b> votre email : ...
cliquez ci-dessous :<br><a 
...
Si le lien ci-dessus ne fonctionne pas, vous pouvez aller sur :<br>
http://list.artaddiction.com/
<br>ou répondez svp à ce message sans en modifier le contenu.<br>
Votre désinscription sera effective dans les 72 H.<br>Merci de votre coopération. </FONT></TD>
</TR><TR><TD colspan=''2''><FONT size=''1'' face=''Arial''>En conformité avec la loi 
78-17 du 6/1/78 (CNIL), vous pouvez demander à ne plus figurer sur notre 
fichier de routage.<BR>
<IMG src="'http://web.artprice.com/img/LogoArtp_90.jpg'" border=''0'' align=''absmiddle''>IX 
:28<BR>
</FONT><FONT face=''Arial, Helvetica, sans-serif'' size=''1''>Artprice.com - Domaine 
de la Source BP 69 - F-69270 St Romain au Mont D'or - RCS : 411 309 198</FONT></TD>
</TR></TABLE></BODY></HTML>

And, after decoding the address it was sent to, here's the access_log entries the address was scraped with:

194.242.43.13 - - [26/Sep/2003:21:09:34 +0100] ''GET /foojlist.php HTTP/1.0'' 200 4066 ''-'' ''Art-Online.com 0.9(Beta)''

That's one line from their scraping run, during which they scraped every single page on spamassassin.taint.org, including tar and zip archives, CGI scripts, everything -- making 534 requests between 21:07:31 and 21:16:49.

spam gmail email

The Google File System

Boing Boing links to a paper on the design of the Google Filesystem, Google's in-house redundant-array-of-inexpensive-PCs cluster filesystem.

It's very, very nice -- and full of interesting tidbits about Google's architecture.

  • 'the system must efficiently implement well-defined semantics for
    • multiple clients that concurrently append to the same file. Our files are often used as producer- consumer queues or for many-way merging. Hundreds of producers, running one per machine, will concurrently append to a file. Atomicity with minimal synchronization overhead is essential. The file may be read later, or a consumer may be reading through the file simultaneously.'
  • 'The workloads also have many large, sequential writes that append data to files. Typical operation sizes are similar to those for reads. Once written, files are seldom modified again. Small writes at arbitrary positions in a file are supported but do not have to be effcient.'

A perfect example of traditional UNIX system design!

storage aws s3

You Might Be An Anti-Spam Kook If...

You Might Be An Anti-Spam Kook If... -- very funny list from Vernon Schryver, concerning the many Final Ultimate Solutions to the Spam Problem (FUSSP) (link via Raph).

Raph says he, too, has a FUSSP, but says 'I realize that using a trust metric to defeat spam, while probably effective, won't be easy.' Nevertheless, I'd be interested in hearing it, for one. Go on Raph, write it up! ;)

Funny: Whisky boss 'amazed' by spy interest: 'The boss of a tiny Scottish distillery says he is amazed to learn that US spies have been monitoring his whisky plant for weapons of mass destruction.'

spam anti-spam filtering

Ishkur's Guide

Ishkur's Guide to Electronic Music v2.0, via MeFi.

Not bad at all! It actually has 2 Congo Natty tracks listed -- even if it gets the name wrong for one of them ;) I'll nitpick, though; the categories around drum and bass, ragga jungle, jungle, and breakbeat are a bit randomly-connected together; they didn't really tie together that way at all IMO. And he randomly decided that hardcore should be renamed 'breakcore', created a new category for all that gabba shite, then called it hardcore. But hey... if you're going to try to make some kind of sense out of it, you have to break some eggs, and never mind -- there's lots of nice samples!

BTW I can't believe he lists Rob Hubbard's theme music to Zoids in the Techno/VGM category. Has someone really released that?

And in passing, I should note, the description for 'Not Trance' under 'Trance' is spot on. As are many of the other recent trance/house-related categories. And, alright, some of the recent d'n'b categories too...

music mp3 ireland

Happy 20th birthday, GNU!

20 years ago tomorrow, on 27th September 1983, the GNU project was announced:

Free Unix!

Starting this Thanksgiving I am going to write a complete Unix-compatible software system called GNU (for Gnu's Not Unix), and give it away free to everyone who can use it. Contributions of time, money, programs and equipment are greatly needed. ......

So that I can continue to use computers without violating my principles, I have decided to put together a sufficient body of free software so that I will be able to get along without any software that is not free.

Thanks to Ciaran O'Riordan for pointing this out!

linux free-software gnu open-source

I Say Risbubh

I keep getting this one, with a question about whether spammers can use it to get past filters:

Aoccdrnig to rceent rsceearch at an Birtsih uinervtisy, it deosn't mttaer in waht oredr the ltteers in a wrod are, the olny iprmoetnt tihng is taht frist and lsat ltteer is at the rghit pclae. The rset can be a toatl mses and you can sitll raed it wouthit porbelm. Tihs is bcuseae we do not raed ervey lteter by it slef but the wrod as a wlohe.

Firstly, it's a crock. That text is incomprehensible! Plus, it's not entirely truthful in its message -- try this variant, which really does make the 'rset' a 'toatl mses':

Aidnroccg to rceent rrceesah at a Biitsrh usvitrneiy ...

Or maybe it's just me who has to spend about 10 times as long trying to comprehend it. (Or maybe my font's too small. whatever...)

Secondly, every 'trick' that results in spammers embedding large up-front blocks of readable text in their mails, scrambling letters around like that, using l33t-sp3ak, i n s e rt i n gs p ac e s, 92384 adding lsdjfgk random foo words to viagra confuse filters, etc. etc. will do nothing but hurt them.

Bear in mind they make money from spam by making sales -- if they have to increasingly obfuscate their message to get through, their would-be 'customers' will not be able to read the messages, their sales will go down, and spamming will become unprofitable.

Remember: if the costs of spamming goes up (through effective filters, increasing complexity to evade detection, and legislation to prosecute them), and the returns go down, the spamming becomes unprofitable and more spammers will give up.

spam filtering anti-spam spamassassin backscatter

Good news on software patents

Great news from the European Parliament -- the good amendments have been passed and it looks a lot better. James Heald of FFII is quoted as saying 'the directive text as amended by the European Parliament clearly excludes software patents. It hangs together incredibly cohesively.'

Congratulations to our MEPs who grasped the highly technical nuances of the issue, and voted the right way, and to the groups who advised them so well. No congrats to me who went on holidays just before this vote. ;)

Now, all that remains is to ensure that the Council of Ministers also do the right thing; unfortunately FFII note that 'in the past, the Council of Ministers has left patent policy decisions to its patent policy working party, which consists of patent law experts who are also sitting on the administrative council of the European Patent Office (EPO). This group has been one of the most determined promoters of unlimited patentability, including program claims, in Europe.' Not encouraging.

Meta: still catching up and getting through the jetlag...

swpats patents software ip law open-source

Back

Back from a great week-and-a-half in Ireland. Lots of fun (and Guinness) was had, Luke and Lean were successfully married, Ireland is officially the most beautiful country in the world, weather was amazing, got to meet up with virtually everyone, and I'm now back at the computer catching up.

Of course, some git has joe-jobbed both myself and a mailing list I'm on, so there's thousands of bounce messages as a result and the server is slow as a wet week. Argh. But at least the SoBig onslaught has died down a bit.

Interestingly, I reported some spam to SpamCop a week or two before the joe-job. I wonder if the two really are connected -- ie. report spam, and the spammers will decode the listwashing tokens from their mails, figure out your email address, and add you to their 'enemies list'?

This is the first time I've reported spam to SpamCop in a long time, and the first joe-job I've been victim of. It seems like more than a coincidence, IMO.

spam anti-spam spamassassin

On hols

I'm in Ireland for my friends' wedding for the next week and a half, so blogging will be infrequent. ;)

ireland blogging dublin

Leni Riefenstahl, suing 12-year-olds and FFB

Leni Riefenstahl dead at 101 (CNN). Riefenstahl's Triumph of the Will, the 1934 Nazi propaganda film, is rightly famous -- it's technically excellent -- but became a millstone around her neck for the rest of her life. To my mind, this lesson illustrates that an artist (or scientist) can never divorce the work one does from that work's implications to society.

Music: 12-year-old sued for downloading music. ' 'I got really scared. My stomach is all turning,' Brianna said last night at the city Housing Authority apartment where she lives with her mom and her 9-year-old brother.' Way to go, RIAA.

Spam: Paul Graham: a spam filter that fights back. Basically auto-spidering URLs found in spam messages as a form of anti-spam DDoS.

abuse ip spam internet copyright

Microtution spam warning

Just received a mail from a bunch called 'microtution', looking to write a collaborative political weblog. More details here.

But hold on there -- this was an out-and-out spam, sent via an open proxy, using a spam tool, with faked headers, to a spamtrap address they scraped from one of my sites. Anyone considering helping out on this collaborative weblog might like to consider who they're helping.

The mail was sent from 213.176.81.230, direct to my MX, from 'Fredericka' <promiseman@promiseman.com>, Subject 'need help with political blog'.

spam anti-spam community

Penguinitis

Good interview with Samba's Tridge. He explains where the penguin mascot came from -- I never knew the linux penguin was in fact a fairy penguin! All those trips bringing visitors to Phillip Island while I was in Melbourne were not wasted then. ;)

Some time later Linus was looking for a mascot for Linux, and apparently the incident at the National Aquarium helped influence him towards choosing a penguin. If you go there now you will see a little plaque commemorating the fateful day when Linus caught 'penguinitis' from one of the fairy penguins in the enclosure (the 6ft one, of course).

linux animals open-source

ha ha ha ha

ThisIsLondon: 'David Blaine thought he was ready for anything. The US illusionist suspended in a glass box over London had prepared himself for 44 days of starvation, loneliness and boredom.

But there was one thing he had not planned for - Londoners.

... the prize for invention went to golfers who teed up with clubs on Tower Bridge and tried hitting the box with golf balls.'

funny london art

Back again

So I'm back -- I was up in Sunnyvale last week, on a work trip. Met up with Dan Kohn for the first time, which was great, and also had an impromptu SpamAssassin summit with Craig and Dan Quinlan -- and got to meet the newest arrival in the Hughes family, the very cute Evan Alice.

I was hoping to meet up with a few more people, but didn't quite organise it in the limited time there. Maybe next visit!

ObLAvBayAreaComment: Amazing how much better the drivers are up there, too. ;)

Still averaging about 68 SoBig.F virus mails, at about 100Kb each, for a total of about 7Mb per hour. That means my 'reject' mailbox is at 412 megs since Friday afternoon. Beats Charlie Strosser's figures ;)

It's all getting quietly bitbucketed, but the side-effects are still nasty. Take a look at this, for example; someone at adjv503ry3ec.ab.hsia.telus.net (142.59.69.220) has been spewing SoBig.F's at the FoRK list, using my address, non-stop for weeks. Argh.

Patents: Richard Allen MP tackles the thorny software patents issue. It's great being able to follow his thinking on these lines -- more politicians should consider starting a weblog along these lines. True transparency.

Much better than Arlene McCarthy's railing against 'The Misinformation Campaign ... by the Free Software Alliance', whoever they are... I particularly like this statement from her PR:

If we were to follow the demands of these lobbyists then we would be handing over inventions to US multinationals and getting no return on our R&D investments in the field of computer implemented inventions. This will sound the death knell for our brightest and best European inventors, whilst the US and Japan will demand licence fees from European companies for the use of their patents. Without patent protection there will be no financial incentive for our most creative industries to develop genuine inventions.

... but -- given that (a) software patents cannot currently be enforced in Europe, and (b) that 77% of the (currently-unenforceable) EPO software patents are registered already to non-EU companies, the only way for the US and Japan to 'demand licence fees from European companies for the use of their patents' would be if McCarthy's proposed directive was passed, allowing those patents to be enforced in the EU. Oops -- own goal!

VR: so I don't lose this, Jaron Lanier's 11 reasons why Virtual Reality has not yet become commonplace.

History: Came across the original SpamAssassin pre-release 'try it out' mail:

after quite of while of thinking about it, I've finally rewritten the spam filter I've been using for a while, and released it as free software.

It's called SpamAssassin, and it's a mail filter to identify spam using text analysis. Using its rule base, it uses a wide range of heuristic tests on mail headers and body text to identify spam, which it then tags for later filtering using the user's own mail user-agent application.

anti-spam spam smtp spamassassin email botnets security

Urban Design and Vogon Poetry

via Boing Boing, Stating the bleeding obvious: if you drive instead of walk, you get fat. Well, duh!

But the alternative is, if you walk or cycle instead of drive, you'll get killed. 'American pedestrians are roughly three times more likely to be killed by a passing car than are German pedestrians - and more than six times more likely than Dutch pedestrians. For bicyclists, Americans are twice as likely to be killed as Germans and more than three times as likely as Dutch cyclists.'

However, Irvine has some of the best cycling infrastructure (and weather) I've ever seen -- except nobody uses it, apart from the weekender recreational cyclists.

Can't figure out why -- I guess it's just a cultural thing; everyone drives, and people cycling or walking near some cars seems to give the drivers heart attacks. (Seriously. The other night, a driver honked and slowed to a crawl after spotting myself and Catherine walking along -- on the sidewalk, 10 feet from the roadway. And not making any sudden movements, either.)

As Kasia said, s/Connecticut//:

You can do all sorts of weird things in Connecticut suburbs, from walking your cat on a leash to painting tiger stripes on your car -- but strap a camera to your back and take out the two wheeler for a spin and you're the weirdest thing since the Keebler elves.

The EU Software Patent protest makes Indymedia. interesting intersection!

But I think they could have looked into the translation issues a bit more; 'software patents kill efficient software development' isn't exactly urgent enough ;) Also -- is the idea of the software patents song and mime a sort of 'stop patents through Vogon poetry' thing?

Baghdad Burning scraped RSS, via Sitescooper RSS feeds.

cycling safety health papers

Decent C String APIs

meanwhile, back in C-land...

strlcpy() - a replacement for strcpy() and strncpy(), with some very nice performance figures.

I usually use snprintf() to do this, but even that has differint semantics between platforms which needs workarounds. Plus the perf numbers regarding strlcpy() are nice. Plus it's BSD-licensed. (Found via Linux Weekly News.)

In passing, it's worth noting that strncpy() imposes a pretty hefty performance hit (4x - 10x in tests there), due to a wierd specified behaviour; it NULs out unused parts of the buffer! ouch.

See also MS' strsafe APIs. However, the code for that is available only on Windows, which makes it pretty much useless for most C code I'd be writing, and they note 'performance hits'.

coding optimization programming

Vendor liability in US spam law proposal

Good presentation by Anne Mitchell, ex-Habeas CEO, now of ISIPP -- 'False Positives: the Baby in the Bathwater' and 'Putting the Responsibility for Spam where it Belongs: The Case for Vendor Liability' (PDF, 317KiB). Note this bit:

  • In June of 2003, ISIPP's Anne Mitchell worked closely with Senator John McCain's office to help develop and draft legislation which would hold vendors liable for advertising in spam.

  • This legislative draft was introduced as an amendment to the Burns-Wyden CAN-SPAM Act, and adopted by committee as part of the bill. Vendor liability is now part of the Burns-Wyden bill.

  • The proposed legislation makes liable any vendor who advertises in spam which violates the general provisions of the law.

  • Exceptions are made if the vendor truly did not know, and could not have been reasonably expected to know, that their information would go out in spam.

That could be interesting.

spam anti-spam law botnets security

Time Traveller Spammer caught

Wired: Turn Back the Spam of Time. An article about the time-travel spammer, now fingered as Robert 'Robby' Todino:

The anonymous e-mail offered $5,000 to any vendor capable of promptly delivering a collection of far-fetched gadgets for conducting time travel. Among the mysterious devices sought by the message's author were an 'Acme 5X24 series time transducing capacitor with built-in temporal displacement' and an 'AMD Dimensional Warp Generator module containing the GRC79 induction motor.'

He's genuinely interested, it seems -- but has a few psychological difficulties. (Thanks to Gary Stock for spotting it.)

spam botnets anti-spam

Brehon Law, Pepys' rival, and some really bad food

2 history lessons today: Dervala writes about the Brehon Laws of ancient Ireland. Dervala's weblog has become a great source of smart reading material, and is firmly on my daily list.

History: The Electronic Telegraph: Code-breaker reveals a diarist to rival Pepys (via forteana). Not quite as saucy as old Sam, though; he was a Puritan. Shame.

mmm, brains Food: The World's Worst Food, courtesy of Joe McNally via NTK. A bit short of the traditional brain/tongue/tripe dishes however. (Relevant: low grade meat products, urgh.)

SCOvEveryone: Economist interview with Darl McBride of SCO. Interestingly, it notes 'in 1998, Mr McBride himself won what he calls a 'seven-figure settlement' by suing his employer at the time, IKON Office Solutions (who, he says, had breached contract by urging him to move to an office outside Utah).' Nice! However, the SCO management page doesn't mention that, for some reason... (Link)

Date: Fri, 29 Aug 2003 09:45:13 +0100
From: "Martin Adamson" ...
To: ...
Subject: Code-breaker reveals a diarist to rival Pepys

The Electronic Telegraph: Code-breaker reveals a diarist to rival Pepys

(Filed: 29/08/2003)

A Puritan's journal written in cryptic shorthand to foil the King's men paints a vivid picture of 1600s London, reports Will Bennett

A remarkable million-word account of life in late 17th century England which is as vivid as Samuel Pepys's diary has been transcribed by experts after lying largely forgotten for more than three centuries.

A specialist code-breaker was brought in to crack the shorthand that Roger Morrice, a Puritan minister turned political journalist, used in part of the diary to stop the King's agents reading it.

While Pepys's often hedonistic diary was long regarded as the most detailed record of life in Restoration England, Morrice's more strait-laced Entring Book gathered dust in a little-known British library.

The Entring Book was acquired by Dr Williams's Library in London, which specialises in the history of English Nonconformist churches, in the early 18th century and it remained there until a few years ago.

Then a team of academics based at Cambridge University launched a project to transcribe the diary, which covers the years 1677 to 1691 and presents an entirely different view of late 17th century England from that of Pepys.

Now the transcription has been completed and six volumes of Morrice's well-informed account of a turbulent period during which England was ruled by three different monarchs will be published in 2005.

About 40,000 words of the diary were in code and the team, led by the Cambridge academic Dr Mark Goldie, brought in an expert in 17th century shorthand to reveal for the first time what Morrice had written.

"At that time you could be arrested for sending newsletters and information around the country and so he did not want Charles II's and James II's agents to see what he had written," said Dr Goldie.

The shorthand expert, Dr Frances Henderson, from Oxford, not only cracked the code but discovered the names of some of Morrice's contacts, whose names he had written in cipher to protect their identities.

Then, as now, journalists had government sources, and Dr Henderson found that Morrice got much of his information from a man called Collins, an official at the Privy Council who was prepared to leak information to him.

As a convinced Puritan, Morrice was extremely critical of what he saw as the moral laxity of Restoration England. He described Tunbridge Wells, then a fashionable spa patronised by royalty, as "the most debauched town in the kingdom".

With evident approval, he reported the reaction of Ben Haddi Mor, the Moroccan ambassador to London, when some Englishmen urged the diplomat to "receive a whore into his bed".

"He said to our great rebuke and shame, 'My religion forbids whores, does not yours?'," wrote Morrice. "He said 'that when I come home I shall then be counted a liar in my own country for my master will not believe me that so many ladies came open-faced with bare breasts to see me'."

In the winter of 1683-84 the Thames froze so hard that coaches travelled across the ice, an ox was roasted and bullbaiting and other sports were held on the river's surface.

"The concourse and all manner of debauchery upon the Thames continued upon Lord's day and Monday the 3rd and 4th of this instant," wrote Morrice disapprovingly.

Morrice used one of his sources to get information about the birth of James Stuart, the Catholic heir to James II and later the Old Pretender.

"The child was a large full child in the head and the upper parts but not suitably proportioned in the lower parts," wrote Morris scathingly, appalled by the prospect of another Catholic monarch.

However, just a few months later Prince William of Orange's troops marched into London and installed the Protestant Dutchman as William III.

Morrice wrote that women "shook his soldiers by the hand as they came by and cried, 'Welcome, welcome, God bless you, you came to redeem our religion, laws, liberties and lives' ".

ireland food law security politics funny

Voight-Kampff and Plugins

an SF free-sheet has applied the one test that really matters to the current SF mayoral candidates:

Is a particular candidate human or an insidious replicant, possessed of physical strength and computational abilities far exceeding our own, but lacking empathy and possibly even bent on our destruction as a species?

It's the Voight-Kampff Test. No, not the band, this one. The results are hilarious:

TW: You're in a desert walking along in the sand when all of the sudden you look down, and you see a tortoise, Tom, it's crawling toward you. You reach down, you flip the tortoise over on its back, Tom. The tortoise lays on its back, its belly baking in the hot sun, beating its legs trying to turn itself over, but it can't, not without your help. But you're not helping. Why is that, Tom?

Tom Ammiano: That's interesting. I don't know. I'm a republican?

(thanks Ben!)

Patents: The W3C has set up a new list to evaluate ways to work around the Eolas patent on plugins, which, after all, are part of the HTML specification.

Good. I never liked plugins anyway, always playing loud music, halting the browser while they start up, or crashing the lot with their buggy spyware code. Good riddance! Now we can get back to the sensible 'helper application in a separate window' paradigm ;)

politics funny us-politics

Download Caps: Pay To Receive Viruses

Many non-US-based broadband systems impose a download cap -- a limit on how much data a customer can download in one month. In some of the Irish ISPs' cases, it's 3Gb of data per month, with hefty per-Mb charges after that.

Well, here's something. I filter my mail for viruses and spam on my server, and divert the viruses off to a side folder. I just checked, and that folder contains 1 gigabyte of virus data, received since SoBig.F started up last week.

Given that most users don't have a colocated server to divert their viruses on, and therefore would have had to download that 1 gigabyte of virus mail before their virus scanner got to take a look -- that's a hefty third of the download cap gone, due to a virus.

I wonder if Eircom, Telstra down under, and the other capping ISPs, will be giving their customers refunds as a result?

(BTW, by contrast, I only received 10 megs of spam.)

anti-spam spam botnets security ireland malware internet

And you thought it couldn't get crazier

This is absolute insanity. Let's say you're buying a car, and you're checking out what will work out best, between an SUV and a fuel-efficient hybrid, money-wise. Let's check the options:

Unbelievable.

But don't worry -- there'll be plenty of gas to run the SUVs, since the US is checking the possibility of pumping oil from Iraq to Israel. (That's assuming the entire Arab world doesn't turn into a seething pit of 'told you so' hatred as a result, but hey....)

As Yoz says, 'How To Blow Up The Middle East In One Easy Step':

yozlet: They saved the game before they did this, right? Right?

Bilskirnir: Two US senators responsible for MPAA regulation may be up for lucrative $US1.15 million jobs as lobbyists with the same organisation:

'It's obscene for Tauzin and Breaux to be in the running for the MPAA, the fattest media lobbying job in Washington, while advocating in Congress on behalf of companies that control the MPAA,' said Robert McChesney, Professor of Communications at the University of Illinois at Urbana-Champaign. 'It tends to confirm what the vast majority of Americans have suspected - relaxed media ownership rules are an X-rated exercise in power and influence.'

As Nathan points out, an analogue of non-compete agreements, for would-be politicians-turned-lobbyists, would be a good way to deal with this one.

Tech: in more calming news: Dell Patents 'Reboot and See If That Fixes It' Technical Support Process (BBSpot via Craig).

climate-change politics us-politics

Wow

BBC to create the BBC Creative Archive. This is insanely cool. Danny O'Brien has written a fantastic overview, so read that for more details. But check out this quote:

I believe that we are about to move into a second phase of the digital revolution, a phase which will be more about public than private value; about free, not pay services; about inclusivity, not exclusion.

In particular, it will be about how public money can be combined with new digital technologies to transform everyone's lives.

That's BBC Director General Greg Dyke totally 'getting it'. So cool.

internet copyright ip piracy

Italy now opt-in-only, SoBig.F phones home

Heads up for all the businesses out there sending mail to European customers -- the EU E-Privacy Directive is now coming into force. Italy is the latest country to implement it; so businesses mailing Italian customers or prospects may wish to make sure that they abide by these rules:

  • Companies may send direct marketing email only to customers and subscribers who have given their prior consent to receiving such, either by subscribing explicitly or by providing their details during a prior transaction, such as a purchase.

  • Forged headers and other means of disguising or concealing the sender's identity is illegal.

  • All messages must bear opt-out details as well.

  • Apparently, in the Italian rendition, senders may also 'collect' addresses but must immediately give the user a clear opportunity to opt-out at that point -- but as far as I know this isn't in the core EU directive.

Similar laws will be coming in all over Europe, so USian senders should really pay attention: opt-in -- it's not just a good idea, it's the law (in Europe at least ;).

Malware: It sounds like SoBig.F is about to call home for new code (scroll down to 'Downloading Functionality'). This is not good. :( Block port 8998/udp.

SoBig.F, the assorted bounce messages from forged SoBig.F mails, the assorted replies from autoresponders and list admin software from forged SoBig.F mails, and (of all things) user complaints about the forged mails (argh! surely they know they're forgeries by now!) are really driving me up the wall. As I check my mail, there's at least 400 of these messages this morning alone.

IP: Lessig lays into USPTO director: 'If Lois Boland said this, then she should be asked to resign.' ... 'That someone who doesn't understand them is at a high level of this government just shows how extreme IP policy in America has become.'

spam law anti-spam eu ireland privacy data-protection sms

Slammer crashed nuke power plant safety systems for 5 hours

Slammer worm crashed nuclear power plant safety systems for 5 hours (SecurityFocus).

Humour: BBspot: SpamAssassin Unveils New HomeAssassin Product for Unwelcome Visitors.

Aside: I wonder if the team behind NPR's Day to Day program realise how close that name is to the classic Chris Morris/Armando Ianucci UK fake news programme, The Day Today. Hopefully there'll be less sports reports from Alan Partridge on the NPR version...

security anti-spam spam bbc

More SCO: the Vegas show in full

a must-read: Bruce Perens posts and then demolishes the Las Vegas slideshow comprehensively, demonstrating that one of the code snippets SCO showed did in fact date from 1973, not 1979; and the other snippet was a clean-room reimplementation based on the published specification for the Berkeley Packet Filter, and the SCO code most likely came from the BSD-licensed implementation.

That raises two points: 1. the SCO 'pattern-recognition team' need to go back to Google school; 2. why didn't the SCO implementation of the BPF code maintain the legal copyright attribution text it was supposed to include, so they would have noticed this when out 'recognising' 'patterns'?

I'm looking forward to this getting to court eventually...

copyright law ip open-source

Open source not welcome - USPTO

USPTO seeks to block WIPO open source meeting.

(WIPO) is not the place for discussions about 'open source' software (...) a senior U.S. official argued on Monday. Reviewing the original mission of the World Intellectual Property Organization (WIPO), said Lois Boland, the U.S. Patent and Trademark Office (PTO) acting director of international relations, it is 'clearly limited to the protection of intellectual property. To have a meeting whose primary objective is to waive or remove those protections seems to go against the mission.'

Boland was referring to a July request by a group of scientists, academics, open-source advocates and others for a meeting at WIPO on 'open and collaborative projects,' including open-source software. The WIPO secretariat initially replied favorably to the idea.

Well, that's a shame. Let's hope WIPO reconsider, because it really would be an interesting idea to have everyone involved talking about this stuff.

open-source patents swpats

Holidays

Did you know that George W has spent more days of his presidency on vacation than any president in recent history, and is currently in the middle of a month-long extravaganza worthy of a French public sector worker?

Don't mind me, I'm just jealous and missing Eurohols. (factoid via the SFGate morning fix)

I am speechless yet again.

Malware: The SOBIG.F deluge continues. No, not the virus itself; the various AV scanners around the world, telling me that some machine on the internet forged a message with my address. Accordingly, here's a set of SpamAssassin rules to catch them; write a procmail rule to detect that in the resulting X-Spam-Status header and divert.

spam anti-spam hacks spamassassin

The Irish 419 scam

FROM: UNIVERSAL STAKES LOTTERY, IRELAND. (forwarded by Rick Kleffel on the forteana list)

SCOvEveryone: so SCO showed some 'evidence' of code-copying from SCO to Linux -- problem is, it's code from UNIX v7, written around 1978/79; the code was released in BSD UNIX, rereleased by SCO/Caldera themselves under a BSD license later, and versions appear in textbooks under public domain. In other words, the SCO 'pattern analysis' team who found this 'copied code' didn't realise that this source had been released long ago -- even by their own company, no less. ho hum, good luck prosecuting based on that. next!

Blogs: Malte, one of the SpamAssassin dev team, now has a weblog too -- and with a better translation of the 'W32.Blaster caused the blackout' theory too. ;)

From: "James" ...
Date: Mon Aug 18, 2003 4:15:40 AM US/Pacific
To: ...
Subject: Congratulation! ( Please acknowledge this mail asap)

FROM: UNIVERSAL STAKES LOTTERY
IRELAND. REF NUMBER: 014/060/532 BATCH NUMBER: 762901-PCD03

Sir/Madam,

We are pleased to inform you of the result of the Lottery Winners International programs held on the 3rd of July, 2003. Your e-mail address attached to ticket number 27522465896-6453 with serial number 3772-554 drew lucky numbers 7-14-18-23-31-45 which consequently won in the 2nd category, you have therefore been approved for a lump sum pay out of 2,000,000 (EUROS ) (TWO MILLION EUROS)

CONGRATULATIONS!!!

For security purpose and clarity, we advise that you keep your winning information confidential until your claims have been processed and your money remitted to you. This is part of our security protocol to avoid double claiming and unwarranted abuse of this program by some participants. All participants were selected through a computer ballot system drawn from over 20,000 companies and 30,000,000 individual email addresses and names from all over the world. This promotional program takes place every year. This lottery was promoted and sponsored by eminent personalities like the Sultan of Brunei. We look forward to your active participation in our next year USD50 million slot. You are requested to contact our clearance office to assist you with the claim and transfer of your winnings fund into your instructed account by acknowledging the receipt of this mail with the email address below.

Email address: ...

Note that, all winnings must be claimed not later than one month. After this date all unclaimed funds will be null and void.

Please note in order to avoid unnecessary delays and complications, remember to quote your reference number and batch numbers in all correspondence. Furthermore, should there be any change of address do inform our agent as soon as possible. Congratulations once more and thank you for being part of our promotional program. NOTE: YOU ARE AUTOMATICALLY DISQUALIFIED IF YOU ARE BELOW 18 YEARS OF
AGE.

Sincerely yours,

James Clark.

(Lottery Coordinator)

spam anti-spam ireland security spamassassin

Monday morning quickies - gifts patented

FFII have discovered that Amazon.com have received a patent from the EPO 'which covers all computerised methods of automatically delivering a gift to a third party'. It seems to cover Amazon's 'One-Click' ordering system, as well.

Wierd: Tiny town to reek of sex. Don't get excited -- it's only moth pheromones. (via Peter Darben on the forteana list.)

Medical slang, including:

  • ATS: Acute Thespian Syndrome
  • Departure lounge -- Geriatric ward
  • DBI: Dirtbag index (calculated by the number of tattoos on the body multiplied by number of recent missing teeth, to estimate days without a bath)
  • NFN: Normal for Norfolk
  • Pumpkin positive: When you shine a penlight into the patient's mouth and his brain is so small his whole head lights up
  • PFO: Pissed, fell over
  • Scepticaemia: What doctors develop with experience

And -- finally! -- an explanation for that ER term:

  • Stat: Immediately, shortened from the Latin statim

Linux: GrokLaw on SCO and Sun's Linux indemnification FUD. Well worth a read -- especially the bit where Mr. GrokLaw finds an old SCO contract that does include indemnification terms. Indemnification, that is, with some pretty serious get-out clauses and stings in the tail.

Weather: Mont Blanc closed due to record heatwave. 'This year, for the first time since its conquest in 1786, the heatwave has made western Europe's highest peak too dangerous to climb. Mont Blanc is closed. The conditions have been so extreme, say glaciologists and climate experts, and the retreat of the Alps' eternal snows and glaciers so pronounced, that the range -- and its multi-billion-pound tourist industry -- may never fully recover.'

Food: Cooking for the Mafia. 'Conrad Gallagher was the highest flier in the gaudy firmament of New Ireland. A Michelin star at the age of 26, and a swank restaurant, called Peacock Alley'. Not too long afterwards, things had not gone so well -- he was in the Brooklyn Detention Centre. Pretty terrifying article -- a US jail is not one of the nicest places in the world...

Spam: The Howard Dean election campaign ran into a wrinkle last week -- and pretty soon was apparently 'joe-jobbed'. This one is going to get interesting, if the Dean campaign follow up, as joe-jobbing an election campaign is in violation of federal election law, and is apparently taken quite seriously.

Reminder: keep an eye on Spamvertized.Org for the latest news in political spam!

health linux uk funny

'Who Wants to be a Millionaire' walkthrough

Wow -- this guy won $250,000 on WWTBAM, and blogged it up, in excruciating detail. (His 'Phone a friend' friend also details his experiences, too). It sounds terrifying...

Hacking: Real-life UNIX disaster recovery.

Commuting: Guardian: A Life Inside meets commuter hell. The author of 'A Life Inside' is a convicted felon, undergoing a gradual release from prison; recently he's been permitted to commute to a day job outside the big house.

'I've had a good run, I suppose. More than a year of almost incident-free commuting.' -- until this episode, where one of those space invaders -- the type who is perfectly happy to push you out of the way to make themselves comfortable -- arrives...

I leaned farther away. Soon my back was hurting. Hang on a minute, I thought. I've paid the same as him for this seat. I was entitled to sit up straight. So I did. Back came the elbow. I wasn't budging. And so battle commenced.

A glance at his computer revealed little activity. He was obviously too preoccupied with trying to make me budge. I was determined to resist this blatant act of aggression. I couldn't help thinking it would never happen in prison - not without ensuing combat. I thought about my pal Toby Turner. This laptop lout was lucky he wasn't sitting next to him in his heyday. I could just imagine Toby's reaction to the elbow treatment.

Paying no heed to the mass of silent bystanders, my shaven-headed friend would have been on his feet in a flash. 'Do you know how many fuckin' anger management courses I've done?'

'Er, no,' his startled tormentor would stutter.

'Six fuckers!' Toby would yell, 'and I still ain't passed!'

work funny linux

Flash Mobs hit Ballyhoo

The latest interweb craze, 'Flash Mobs', have hit Ballyhoo, according to The Ballyhoo Examiner:

'There was about 15 of them, and they went around the shop muttering 'carriages' or 'cabbages', I'm not quite sure which' .... Brendan says he himself would be 'game on' to take part in the next one, as long as it isn't in his own employers' this time, or a bank.

Art: Size does matter, Jamaicans decide (Guardian):

Two naked 7ft-high bronze figures - a male and a female - looking skywards on a dome-shaped fountain embossed with Bob Marley's lyrics 'None but ourselves can free our minds'. But according to the statue's critics the artist is too light-skinned, the male figure is too generously endowed, and both are, well, too naked. .... Another writer ridiculed Renaissance sculptors for being not generous enough. 'Just because Europe's classical statues had small penises, ... does not mean Jamaica must follow suit.'

SCOvEveryone: Groklaw forwards an interesting theory: Does SCO Unixware 7.1.3 contain substantial portions of SuSE Linux Enterprise Server 8 -- including the GPL'd device drivers? The author writes:

It is my belief and opinion that SCO has indeed borrowed engineering concepts and methods from their association with UnitedLinux. Many of these new features and the remarkable similarity with SLES 8 did not occur until after they started to participate in UnitedLinux and since these features were available to SuSE customers before SCO's involvement I am inclined to believe that SCO's engineering team has been influenced or tainted by the Linux development process. I cannot say if UnixWare 7.1.3 or SLES 8 share common code; as I said I am not a source licensee. I feel these issues need to be investigated further.

funny art linux sco

Referrer Spam Again

More referrer spam stuff. As Mark states in the comments here, it seems that the referrer-spamming is using real browsers run by real people -- no bots, no proxies.

The spammers create HTML pages which contain an IMG tag, using one of our pages in the SRC attribute. This causes the user's browser to attempt to download the page -- giving the correct referrer URL -- but it's not particularly visible to the user -- since it's a HTML page, not an image. All they're likely to see is a 'broken image' icon, and more likely the image is hidden anyway using a hidden div or width=0 height=0 attributes.

Anyway, I took a look at the HTML for those sites. Interestingly, all of them use a distinctive HTML style, with a redirecting frame and some Javascript to load the following pop-up ad:

http: //pb. xxxconnex. com/pb.phtml? d=aporndomain.net &sc=EXPN &ip=9999999999 &c=preview

Where 'aporndomain.net' is a porn domain, not necessarily always the same one as you're viewing, and '9999999999' is a 10-digit number. This then loads a frameset containing another random popunder ad from a load of domains. It also throws a few hidden ones into the corner, loads them as pop-unders, loads a javascript timer to open new ones occasionally, etc. etc. etc. As you close 'em, new ones open, and so on. Glad I don't run IE ;)

I would bet these guys, xxxconnex.com -- or one of their customers -- are the ones behind the referrer-spamming as a result. Their WHOIS info states they are:

Admin, Domain  info@webfinity.net
1E Braemar Ave
Unit 19
Kingston 10, WI N/A
JM
876-357-8404

Interestingly, that phone number and address also shows up in ROKSO as well, listed under domain registrations controlled by the 'Dynamic Pipe / Webfinity / Python Video' spam gang, ie. one of the biggest sources of porn spam out there. They're diversifying it seems!

Based on some suggestions on Kasia's weblog, I think I now have a good comeback -- still working on this though.

spam security phishing

The Cluetrain List

Chuq van Rospach has a great idea -- instead of a do not spam list, an I am your customer, not your asset, and quit treating me like one list:

Where do-not-spam lists are useful (and ought to be mandatory) are third party sales and rentals. Any time someone buys or rents a list, that list has to be filtered against the do-not-spam list. If you're on it, you fall out of the transfer. that would include any time that information moves from one company to another, the do-not-spam restrictions apply. (ditto, IMHO, for phone and other personal information. I'll go further, actually. I think there ought to be a generic 'do not sell me as an asset' list, preventing transfer of personal information of any kind without permission. Or more correctly, a I am your customer, not your asset, and quit treating me like one list.

Great idea. Really, the resale of contact information for marketing purposes sounds fantastic to marketers -- but as The Story of Nadine demonstrates, it only takes two years for the contact information to be sold (via a chain of increasingly dodgy operators) from DeliverE, a subsidiary of Excite to horse bestiality porn spam.

spam anti-spam data-protection email privacy ireland law

Involuntary Park at Porton Down

Amazing! Porton Down is the UK's center for research into chemical and biological weapons, and has been since 1916. Not the nicest place you could think of -- by a long shot.

Well, it turns out that the massive no-go buffer zone around Porton Down, existing for 87 years, has preserved 'the largest remaining continuous tract of chalk downland in Britain'. 'The farming revolution of the 20th century, the development, the tourism, have all passed it by.' 'The disrupters are the large-scale inputs of chemicals, the pesticides, herbicides and artificial fertilisers that are the essence of intensive farming. At Porton Down, these have never arrived.'

As a result, it's now an amazing wildlife heritage site. Quite hard to get to see it -- but good to know it's there! Thanks to Bruce Sterling for forwarding this along the Viridian list.

Reminds me of something I heard about Chernobyl -- since the area around it is heavily irradiated, and therefore a no-go area for humans, it's become a de-facto wildlife refuge (even if half of the animal inhabitants are sterile as a result.)

food tourism funny

'International blacklists' absurdity

OK, this is very stupid.

----- Transcript of session follows -----
... while talking to mail.(elided).com.:
>>> RCPT To:<zzzzz@(elided).com>
<<< 591  The mail server you are SENDING FROM is listed on an
international blacklist. Send your questions to
blacklist-admin@(elided).net
554 5.0.0 Service unavailable

The mailserver in question is dogma.slashnull.org, 212.17.35.15. It's never been on a blacklist. However, it does live outside the US -- in Ireland, to be exact.

So it appears (from the wording) that someone is actually filtering their mail feed and blocking all mail from Ireland. Hello!? It's worth noting, in passing, that I strongly doubt that blocking all mail from Ireland (a) reduces your spam load one iota or (b) accomplishes anything apart from pissing off Irish people. Ah well, not my problem...

SCO: In other news, Ben sends on this Pinky and The Brain rendition of the SCO-vs-the-world saga from Nicholas Petreley -- worth a titter. Given that SCO are now sending invoices to Linux users, including charging 32 bucks for embedded developers -- who almost definitely are not using Read-Copy-Update and that kind of absurdly-high-end code -- it's pretty accurate.

Malware: The latest Windows worm, coming to a system near you; make sure ports 135-139, 445 and 593 are blocked, if you really have to run Windows for some reason. The worm's author includes this notable text string: billy gates why do you make this possible ? Stop making money and fix your software!!

Iraq: Amazing postmortem of the Iraq war. Summary: absolutely inept on the Iraqi side. 'The only order I got was to dismantle my airplanes -- the most idiotic order I ever received.'

ireland law data-protection spam anti-spam privacy mail internet

Monday Morning Quickies

The Dublin Flash Mob. All went off very well, from the sounds of it. However, this picture contains some wierdness -- who the hell is that guy, second from the left, who's stolen my haircut circa 2 years ago?! Those are my sideburns, give 'em back!

(ObSoCalJoke: they tried to organise a flash mob in southern CA, but couldn't find anywhere with a big enough parking lot for all those single-occupant SUVs. Ba-dum-tish!)

Telecoms: The Communications Workers of America union have released some figures on Verizon's profit margins etc. Interesting to note some figures -- like they charge 4 dollars for call waiting, a service which costs them 0.82 of a cent to provide -- that works out at a 48,680% profit margin, which must be nice. In addition, Verizon use 'splitters', which result in a copper pair being unusable for DSL -- just like Eircom do in rural Ireland. Interesting to note that, even after deregulation, LLU and general introduction of competition, the same problems still arise.

Science: BBC: Scientific research put under spotlight. Terrible article from the Beeb, who should know better.

Basically the article pins some of the blame for recent absurd claims of scientific breakthroughs, like the Raelian's claims they cloned a human, on the peer review process.

What they're missing is that, in most cases of these absurd claims, the research had not been peer reviewed -- instead a press release was put out in advance. Peer review remains the most effective way to demolish bad science. However, the news media shows no sign of being willing to sit around and wait for other scientists to analyse the latest claims, before publishing them.

Spam: Salon: Meet The Spam Nazi. More on the bizarre story of the Jewish leader of a Nazi party, who now peddles 'make penis fast' pills.

Politics: Ian 'Freenet' Clarke says he's leaving the US.

Linux: I've given up on blogging the SCO-v-everyone thing, it's getting too absurd. GrokLaw is covering it much better than I could anyway. Plus: You say po-TAY-to, I say po-TAH-to.

Movies: I concur with Waider -- Pirates of the Caribbean is great. Best summer blockbuster in years; Hollywood can still pull off a good big movie now and again (by using young directors it seems). Buckle those swashes! Aarrr!

ireland filtering dublin tech

Long-chain Monomers

PR-otaku -- I've just got to buy Pattern Recognition, it looks amazing.

Just finished Nickled and Dimed: On (Not) Getting By in America, by Barbara Ehrenreich; a great read, although pretty grim. (thanks mum!)

books scifi economics

New Favourite Band

Music: I've just stumbled across Ladytron on EMusic a couple of weeks ago, and they've totally taken over my playlist.

They're kind of over-cool electro stuff in the style of Air, but with much more in the way of 80s-style synth noises. Massively over-cool: it seems the name is from a tune from Roxy Music's first album, this interview has them namechecking 'The Andromeda Strain' and 'Logan's Run', and virtually every tune is heavily Kraftwerky.

Still, I'm hooked... one note though: IMO, the first album, 604, is much better than the difficult second. AudioGalaxy seems to have a copy of ' Play Girl' from 604 -- give it a listen.

Recommended tracks: I'm With The Pilots and Discotraxx -- Paco! is worth a listen too, it includes the theme tune to Are You Being Served, believe it or not. ;)

music ireland mp3

X-ray specs

NYT: What's in Iraq rumor mill?

BAGHDAD As a U.S. soldier peered out of a passing tank, a young engineering student and a retired accountant contemplated one of the more common questions on the streets of Baghdad: Did the soldier's wraparound sunglasses give him X-ray vision?

'With those glasses, he can definitely see through women's clothes,' said the engineering student, Samer Hamid. 'It makes me angry. We are afraid to take our families out on the street.'

Date: Thu, 07 Aug 2003 16:07:41 +0100
From: "Martin Adamson" ...
To: ...
Subject: What's in Iraq rumor mill? X-ray vision and air-conditioned

vests


> >From the New York Times

What's in Iraq rumor mill? X-ray vision and air-conditioned vests

John Tierney/NYT The New York Times

Thursday, August 7, 2003

BAGHDAD As a U.S. soldier peered out of a passing tank, a young engineering student and a retired accountant contemplated one of the more common questions on the streets of Baghdad: Did the soldier's wraparound sunglasses give him X-ray vision?

"With those glasses, he can definitely see through women's clothes," said the engineering student, Samer Hamid. "It makes me angry. We are afraid to take our families out on the street."

The retired accountant, Hekmet Tinber Hassan, smiled and said it was a baseless rumor, just like the widespread story that Saddam Hussein had been secretly working for America and was now at a CIA safe house. "I do not believe Saddam is in America," Hassan said. "I heard he went to Tel Aviv."

Just as truth is the first casualty of war, urban legends seem to be the first creation of a military occupation, especially when the cultural gap is as wide as it is here. After life under Saddam, people here are accustomed to conspiracy theories and ready to believe the worst about anyone in power.

Of course, Americans have been circulating their own kinds of legends, starting with the fantasies a few months ago that the occupying troops would be peacefully welcomed by a country of grateful flower-waving citizens. There have been more guns than flowers.

In the urban legends flourishing here, the soldiers triumphed thanks to Saddam's treachery and to U.S. technology. The legend about the X-ray sunglasses may have evolved from reports about the soldiers' night-vision goggles, or maybe just from the imposing Terminator image of the soldiers.

Compared with the residents, who cope with the fierce heat by staying in the shade and dressing in light clothes and sandals, the soldiers have the look of robotic aliens as they patrol in the midday sun wearing combat boots, helmets and armored vests.

Some Iraqis say the troops take special pills that keep them cool, but the most common theory is that they have portable air-conditioners - usually said to be inside the vests, but sometimes placed in the helmet or even the underwear.

"There is fluid circulating throughout the underwear," said Hamid, the engineering student. "I am not sure of the exact mechanism, but we all know the Americans have very sophisticated technology."

Aadel Delli, the owner of a food market in central Baghdad, said he did not believe the air-conditioned-uniform stories, which he attributed to popular doubts about Americans' capacity for discomfort. "Most Iraqis thought the American soldiers would be gone by now because they could never stand the summer in Iraq," he said.

Soldiers have tried dispelling the myths about their gear by letting Iraqis touch their vests and try on their glasses, but some legends will not die.

"I let a kid put on my sunglasses, and he was still convinced they had X-ray vision," said Sergeant Stephen Roach, a soldier from Lufkin, Texas "He kept saying to me, 'Turn it on, turn it on."'

When they are not peering through women's clothes, the male soldiers are said to be groping underneath the clothes during searches at checkpoints, supposedly provoking some of the attacks on soldiers. (Never mind the absence of evidence for this theory.)

Other versions of the ugly-American stories have the soldiers drinking beer inside their tanks near mosques. They have been accused in the Arab press of using pages from the Koran for toilet paper and of giving children candy packets containing pornography.

The rumors became so numerous that Al Sabah, a new daily paper run by Iraqis with financial backing from the Coalition Provisional Authority, the U.S.-run administrative organization, printed a supplement debunking them. "It will take awhile for people to reject the conspiracy theories," said its editor, Ismael Zayer. "Under Saddam, people had to depend on rumor because they could not trust the media."

Frustration seems to feed many of the rumors. Why would the builders of smart bombs and X-ray sunglasses take longer to restore power than Saddam did after the 1991 Gulf War? The Americans must be withholding electricity as revenge for the attacks on soldiers.

For all the frustration, there remains some admiration for the occupiers, as seen on teenagers like Zahra Thaer, 13, who was wearing a new pair of wraparound sunglasses. "These are the latest style," she said. Did she believe the soldiers' glasses gave them X-ray vision?

"I am not so sure about their sunglasses," she said. "But I know about the helmet. Inside each helmet is a map showing the soldier the location of every house in Iraq. My friends at school told me about it."

The New York Times

privacy algorithms open-source

DE Technology's patent hits Oz

Nathan Cochrane writes in The Age: 'Opponents of a Canadian company's patent to tax online transactions believe they can stop it before it is granted by the Australian patents office.' This is the DE Technologies patent I blogged about before, which they hope to license under some hefty terms; 'annual licence fees of $US10,000 ($A15,324) each, plus 1.5 per cent a transaction and $0.11 cents each time a document, such as an invoice, is generated.'

At FightThePatent.co.nz, they note that the NZ government plans to amend its patent law to make it much harder to file such patents in future. They also link to another Age article which says the patent has already been granted in Oz as of 'February of this year, according to IP Australia'.

An Aussie tech executive called Matthew Tutaki is planning to try and have it quashed. The situation can be followed on FightThePatent.co.nz. Unfortunately, in turn it seems DE Technologies are planning to fight back.

patents uspto law swpats linux ireland ip

Who buys stuff from spammers?

Good Wired article on the subject:

A security flaw at a website operated by the purveyors of penis-enlargement pills has provided the world with a depressing answer to the question: Who in their right mind would buy something from a spammer? An order log left exposed at one of Amazing Internet Products' websites revealed that, over a four-week period, some 6,000 people responded to e-mail ads and placed orders for the company's Pinacle herbal supplement. Most customers ordered two bottles of the pills at a price of $50 per bottle.

And check this out for bizarre:

An investigation ... last month revealed that Bournival's mentor and business partner is Davis Wolfgang Hawke, a chess expert and former neo-Nazi leader who turned to the spam business in 1999 after it became public that his father was Jewish.

spam scams botnets

filtering Mailman's admin queue with SpamAssassin

Several MailMan mailing lists I run have been really painful to admin, due to spam overload combined with Mailman's pretty crappy 'pending messages' admin interface, which goes like this: scroll down to each message, select 'discard' radio button, scroll to next, select 'discard' radio button, repeat until wrists hurt.

Thankfully, waider has saved my lists from oblivion. this script, given the list URL and the admin password, will log in to the admin interface, get the list of pending messages in the queue, scan each one using Mail::SpamAssassin (of course ;), and ditch the spam.

It just cleaned out 182 spams from one list, leaving all of 7 valid requests in the queue. Beautiful!

Dublin: Stefan Geens posts an IrishBroadband success story. See, it really works!

anti-spam spamassassin smtp

SCO suggestion

Derek has an interesting suggestion for IBM:

Grab a controlling interest, tell the senior management to sod off, tell the employees to clear out their cubicles, and clear up any hint of IP confusion by selling to IBM for $1 all intellectual property, and then dissolve the corporation entirely with their 50.1% voting share.

IBM has to be careful not to actually buy the company, but strictly be a majority shareholder, making decisions that are in the majority of the shareholders' interests, even if the other 49.9% of the shareholders vehemently oppose them. :-)

Golden parachutes for senior execs? Good luck getting them from that non-existent corporation, and since IBM never actually 'bought' the corporation, it's not liable for any contracts/debts/etc. SCO may have incurred. It gets all the benefit of running SCO and none of the downside.

Gotta say, I like it. ;)

ibm work amazon ip

Drop bears and Subgenii

The fearsome Drop Bear is detailed in this forwarded snippet from the forteana list.:

Drop bears are often mistaken for koalas, and to all but a trained naturalist, the differences are minor. They have even been reported to imitate the sleepy demeanor of their genetic cousins, probably as a sort of behavioural camouflage, and roughly one third of all drop bear related fatalities occur when a well-meaning tourist tries to pose with one for a souvenir photograph.

More here. Thankfully I managed to avoid these creatures while camping through Victoria last year -- only just about though.

In other news: a great SFWeekly feature on Hal Robins, aka. Dr. Howland Owll of the CotSG.

Date: Wed, 06 Aug 2003 07:42:52 +1000
From: Peter Darben ...
To: Forteana List ...
Subject: The secret is finally out

While ploughing through the rapidly growing pile of Dungeon/Polyhedron magzines on my desk I found this little gem

----- (for the d20 Modern Gaming System from Dungeon/Polyhedron June, 2003)

Drop Bear

Although the Australian government officially denies the drop bear's existence, these bloodthirsty relatives of the peaceful koala are the bane of Australia's parks and forests. Named for their preferred of attack - hurtling down from the shelter of trees onto the heads of unsuspecting prey

  • drop bears are responsible for dozens of deaths each year, and the number

climbs with each passing year.

Drop bears are often mistaken for koalas, and to all but a trained naturalist, the differences are minor. They have even been reported to imitate the sleepy demeanor of their genetic cousins, probably as a sort of behavioural camouflage, and roughly one third of all drop bear related fatalities occur when a well-meaning tourist tries to pose with one for a souvenir photograph.

The internal government conspiracy to disavow the existence of drop bears relates to Australia's recent tourism marketing. They certainly can't sell visitors on the idea of coming to Australia if the visitors knew they were going to be savaged by vicious wild animals masquerading at cuddly koalas. Though the Australians themselves are aware that certain chemical repellents such as Aeroguard are effective in discouraging drop bear attacks, forestry service rangers are forbidden by law from explaining exactly why they so heartily recommend it. But as the drop bears' natural food source, rabbits, are gradually reduced in population, it is only a matter of time before the drop bears turn to more plentiful prey : man.

[nerdish gaming stats omitted]

-----

peter

science home bears

SCO, etc., etc. (fwd)

Someday, Ben will set us up the blog, and there will be much rejoicing. In the meantime, I can only quote this one in full, as he hits it on the head:

OK, I know you find this the most boring thing ever and would prefer to find new ways of air-conditioning your chipsets, but, come on! The human drama is nigh Shakespearean.

This guy is pretty good:

http://radio.weblogs.com/0120124/

But, really, RHAT's filing stands alone. It's a thing of beauty, as 27-page legal filings go. They give them both barrels; failing business, FUD, insider stock dumping ...

http://lwn.net/images/ns/rh-complaint.pdf

ben

patents swpats law

Trustic is down

Trustic: 'We regret to inform you that we are no longer taking registrations and will soon be closing the service. We have determined that the system as it currently is designed will not achieve the level of accuracy that we require, and an inaccurate system is worse than no system.'

'The DNS blocklist will remain for a couple of weeks, but it has been configured to never return a match. Please reconfigure your mail servers to not query the blocklist.'

That's a shame...

anti-spam dnsbls spam

P2P and open proxies

Joe St. Sauver's excellent presentation on open proxies has been updated. Interesting snippet: Morpheus 3.2 -- the filesharing app -- is shipping with proxy support. P2P Networks Try to Throw RIAA Off Their Trail (AtNewYork.com):

Morpheus will offer its users the option of connecting to its network via a public proxy server (define). A proxy server acts as an intermediary between two Internet users so that one user does not know the identity of the other. Morpheus won't be hosting the proxy servers but will instead direct users to a 'worldwide network' of public proxies.

iMesh apparently may also include this support, too, in an upcoming version.

music mp3 networking p2p

press! and a whole load of quickies

Wired: Finding Bad Spam Delights Geeks:

When freelance Web developer Joe Stump first installed the e-mail filtering program SpamAssassin, he and a friend started a competition. Each day, the two would look through their junk e-mail and try to find the missive that SpamAssassin had assigned the highest score.

'It was always a little contest between the two of us,' says Stump. 'We were always trying to tweak and modify the settings to get it just right. I finally won the contest when I got a spam with a score of 43.'

The points system has really been popular -- as Joe Stump says -- 'geeks love numbers'. Screengrabs of the SpamAssassin website on Sky News, ABC, and now this! (thanks to Tim Schutte for the pointer.)

Linux: Wonder what the Ximian guys are blogging about? Ha ha, very funny.

Mark Pilgrim: How to install Windows in 5 hours or less.

Tim O'Reilly on parallels between OSS and the mainframe days. 'We so often trace our antecedents back simply to the Unix heritage, or the Lisp hacker heritage. But when I've talked to IBM old-timers, they make clear just how many of the social dynamics and collaborative software development paradigms of the early mainframe era resemble the open source tradition.' Interesting...

Humour: Chris recently set us up the blog -- and kicks it off with this SCO 419 parody: 'I AM MR. DARL MCBRIDE CURRENTLY SERVING AS THE PRESIDENT AND CHIEF EXECUTIVE OFFICER OF THE SCO GROUP, FORMERLY KNOWN AS CALDERA SYSTEMS INTERNATIONAL, IN LINDON, UTAH, UNITED STATES OF AMERICA. I KNOW THIS LETTER MIGHT SURPRISE YOUR BECAUSE WE HAVE HAD NO PREVIOUS COMMUNICATIONS OR BUSINESS DEALINGS BEFORE NOW.' On the roll!

anti-spam spam challenge-response

C64 demos

ah, Donncha reminisces about the Commodore 64 demo scene.

I was involved too, around 1987, coding demos as 'Mantis' for XS -- a pretty little known group. I wrote 2 really great demos, Rhaphanadosis, and another name I can't quite remember ;), but they don't seemed to have survived, which is a shame...

history commodore commodore-64 c64

Excellent hoaxing lads

So it seems that P45.net were behind some classic hoaxes in the Irish media recently, including the Monaghan-Iraq story:

The New York Monaghan Association has issued a strong statement of support for the US military campaign against Iraq. This is despite being unable to carry their usual banner in the New York St Patricks Day Parade because of similarities between an outline map of Monaghan and Iraq.

Busaras comes clean, and Daev kindly remembers to provide 1 page that links to 'em all ;)

ireland politics media

Techie tip: cooling Athlon XP CPUs

so Athlon XP CPUs run pretty hot at full speed all the time, and my PC makes lots of noise as a result. I have a temperature-sensitive CPU fan, so reducing the CPU temp will reduce noise, too.

A while back, I came across this doc, the Athlon Powersaving HOWTO, which contains a great tip -- namely a way to put the processor in 'STPGNT Mode' (Stop Grant Mode), which disconnects it from the FSB and turns off parts of the CPU when not in use.

It works perfectly, in most respects, although the Ensoniq 5880 onboard sound chip goes crazy when it's active, as it can't deal with the changed timings from the CPU. But when I'm playing music, I can't hear the fans anyway ;)

The details -- to keep it brief, just take a look at the commands for my chipset as described here. I'm using ACPI in the kernel anyway, since I'm using software suspend-to-disk as well.

hardware linux power

Lessons from history

I've been reading Crooked Timber recently; a good literate weblog. Today's interesting post, from Kieran Healy: Frustration is not a Strategy. Well worth a read for some context on today's Middle East, and the fundamental problem with those 'kill 'em all' proposals that keep cropping up from the hawks.

Blogs: Nathan Cochrane, Aussie journalist for The Age and writer of a very interesting weblog -- has won quite a lot of money on a TV gameshow! I think the term is 'goodonyamate', if I recall correctly ;)

(Pity he couldn't have fixed the BlogShares listing first though.)

internet blogging web ireland

Clueless spam quotes and free transport

NYT: Diverging Estimates of the Costs of Spam. The article points out how the analyst company estimates of the cost of spam widely diverge. That's reasonable -- in fact, that's analysts for you. Some great data in there, too.

But then we get to this glorious quote:

Peter S. Fader, a marketing professor at the Wharton School who has studied e-mail, says the research firms' estimates vastly overstate the actual cost of spam. ... He also argues that the computers and networks that are being installed to deal with spam will be a powerful resource for processing legitimate e-mail, once spam filters and economic Darwinism tame the spam epidemic.

'Spam, although it is a bad thing per se, is fostering the growth of the e-mail infrastructure,' he said.

Yeah -- in the same way that arson 'fosters the growth' of the firefighting infrastructure. Wow.

Ireland: I've just heard about the 'no fares' day of protest by CIE's unions. It seems the unions, rather than closing up shop for the day as would be traditional, decided to take a much more consumer-friendly approach; instead of shutting down the normal public transport services, they ran them for free. Genius.

RTE reported that 'tens of thousands of people' travelled for free, and Iarnrod Eireann said that 'there has been a notable rise in passenger numbers on some inter-city trains to Dublin as people take advantage of free travel.' Now that's an effective way to strike...

spam anti-spam email microsoft filtering google ireland

Spam and Secondary MXes

So for the past few weeks, I've been getting a lot less spam -- like about 1/3 to 1/4 of the normal volume -- to my jmason.org account.

I didn't have a clue why; occasionally I mused that some spam gangs must have figured out that I needed all that spam to develop SpamAssassin, and cutting down on my volume would mean that I'd have to schlep stuff out of the spamtraps (which is a bit of a chore), so they'd unsubscribed me to cause some minor hassle ;)

In reality, what had happened was that my old secondary MX -- which was secondarying for me because nobody had gotten around to updating it -- had finally been updated, and was no longer accepting mail for jmason.org. So I had only one MX, and the erstwhile backup was bouncing anything it saw, immediately.

Lots of spamtools relay spam via the secondary MX -- not sure why, we think it's working on the assumption that secondaries are less likely to have effective filters.

So basically a good 2/3 to 3/4 of my spam was being sent to a machine that immediately bounced it ;)

The upshot: if you get a lot of spam, and don't really care if you might occasionally lose real mail if your primary MXes are down, you could always set up a 'fake' secondary MX record. The spamtools will happily attempt to send spam to you via that machine (which may not even exist), and then give up after the first bounce -- missing you entirely.

Big caveat: I wouldn't suggest this for situations where your mail delivery needs to be reliable, though. Primary MXes do go down occasionally ;)

anti-spam spamassassin smtp spam email

Referrer spam not via proxies

So a little more investigation shows that the massive numbers of IPs spamming my referrer logs (like 1000 different IPs every day), are not open proxies as I at first thought; I tested 130, and none had any of the well-known proxy ports open.

My current guess is that they're malware, such as those 'ad banner spyware' programs, and the makers of that software must be doing deals with spam companies to set up the spyware to periodically load URLs in order to referrer-spam for the spam bureau's customers.

In this case, all the spammed URLs are owned and registered by one porn operation, which is either operating from Switzerland (according to the tech contact info) or Los Angeles (according to the DNS info in whois). (More likely the latter.)

All the IPs doing the spam page loads, are running on Windows XP and Windows 2000 systems as far as I can see, with ports 1025 and 5000 open, so alternatively, maybe they're trojaned... but there doesn't seem to be any good evidence indicating that. (those ports are reasonably innocuous.)

Anyone got any ideas? Here's some sample access_log lines for 100 IPs, gzipped, if anyone wants to check them out.

spam anti-spam security web

open proxy referrer spam again

Googlebot using open proxies? Somehow, I doubt it. An interesting snippet from the access logs again. (Some details rewritten to avoid boosting PageRank.)

220.73.165.14 - - [25/Jul/2003:04:42:14 +0100] "GET /someurl/foo HTTP/1.0" 2147483647 0 "http://www dot gay-sex-men dot net/" "Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1)"
220.73.165.14 - - [25/Jul/2003:09:04:17 +0100] "GET /someurl/foo HTTP/1.0" 2147483647 0 "http://www dot gay-sex-men dot net/" "Mozilla/4.0 (compatible; MSIE 5.0; Windows 98; DigExt)"
220.73.165.14 - - [25/Jul/2003:09:15:28 +0100] "GET /someurl/foo HTTP/1.0" 2147483647 0 "http://www dot baitbus dot ws/" "Mozilla/4.0 (compatible; MSIE 5.0; Windows 98; DigExt)"
220.73.165.14 - - [25/Jul/2003:09:18:11 +0100] "GET /robots.txt HTTP/1.0" 200 130 "-" "GoogleBot"
220.73.165.14 - - [25/Jul/2003:09:27:57 +0100] "GET /someurl/foo HTTP/1.0" 2147483647 0 "http://www dot blowjobs-cumshots dot net/" "Mozilla/4.0 (compatible; MSIE 6.0; Windows 98)"
220.73.165.14 - - [25/Jul/2003:13:18:04 +0100] "GET /someurl/foo HTTP/1.0" 2147483647 0 "http://www dot hot-legs dot info/" "Mozilla/4.0 (compatible; MSIE 6.0; Windows 98; Win 9x 4.90)"

spam google security web

Some Fortean snippets

Some excellent 'oddly enough' stories:

  • Giant dog-eating catfish dies: a story mourning the death of Kuno, a 5-foot-long catfish living in the lake at Volksgarten Park in Moenchengladbach, Germany. It's presumed he died due to a local heatwave and the resulting low water level. 'Kuno became a local celebrity in 2001 when he sprang from the waters of the lake to swallow a Dachshund puppy whole.' I had a run-in with giant catfish before; mind you, a bit nearer to their natural habitat, and with less pet ingestion involved.

    Catfish are in the news it seems; this NYT editorial is relevant, if a bit depressing. 'The next time a ... delegation sets off to preach the dogma of free trade abroad, poor nations would be within their rights to thumb their noses.'

  • Yahoo! India: Holding severed head in place, he defied death: van driver has road accident, then: 'His head almost severed, blood oozing and eyes popping out, Balram was in a dazed state when the accident took place... He, however, kept his head attached to his body with some cloth. When no one came to help him, he drove his own vehicle for 30 km to reach a nursing home in Agra.' Now that's grit!

  • More sex than splendour on academy's Aztec holiday: 'When Andrew Humphrey entered a competition run by the venerable Royal Academy to win a week experiencing Aztec culture first-hand, he might have expected a genteel tour of the ruins around Mexico City, perhaps taking in the famous floating gardens of Xochimilco. Instead, he found himself tasting contemporary Mexican culture at a notorious adults-only resort with nudity, a 'sexy pool' and 'adult' shows.'

(All picked up via the forteana mailing list BTW.)

wildlife animals home dublin

Soldiers in Iraq, and Vipul

The Killer Elite (Rolling Stone):

The twenty-two-year-old driver, Cpl. Joshua Ray Person, and the vehicle team leader, twenty-eight-year-old Sgt. Brad Colbert -- both Afghan War veterans -- have already reached a profound conclusion about this campaign: that the battlefield that is Iraq is filled with 'fucking retards.'

Later on:

Captain America, the platoon commander who is almost universally disrespected by the enlisted men, seems to deal with the stress by rising to a state of jabbering incoherence. Up by the bridge there are four enemy dead scattered under the eucalyptus trees, along with piles of munitions -- RPGs, AKs and hand grenades. Captain America runs back and forth, picking up their weapons, hurling them into the nearby canal and screaming at the top of his lungs. No one knows what he's screaming about or why, but as another officer who came upon this scene later concluded, 'Whatever he was doing, he was not being in command.'

Fantastic series of articles, well worth a read. (Found on stuff.) Similar to this, here's an unauthorized weblog from a soldier on duty in Iraq -- the inside story.

Spam: Good article by Vipul on spam filtering, at MIT Tech Review:

Here's a list of three rules (created after the most important features of e-mail) that anti-spam software should strive to follow:
  • 1) Ability to send and receive e-mail from a stranger. (Whitelisting, payment systems, and challenge/response break this rule.)

  • 2) Ability to send and receive pseudo-anonymous e-mail. (Domain-based authentication breaks this rule.)

  • 3) E-mail should be free. (Payment systems break this rule.)

He said it. Killing off several useful legit uses of email, just to fix spam, is no good. Looks like he's started writing his blog-like thing too, again, so I'll be adding that to my 'roll (assuming it stays updated! ;) No RSS yet though...

history coding security

Great paper on Diebold e-voting systems

Great report auditing the security features of the Diebold e-voting systems. Summary: what security?

  • despite using relatively 'smart' smartcards, they don't actually get those cards to perform an authentication task; they're just used as 'dumb' memory cards, and there's no central online database of valid card IDs. Plus, the same write password is used for all smartcards.

    So they really might as well have used formatted floppy disks ;) Duplicating cards (a card is a voting opportunity, 'vote early, vote often') would be pretty easy, from the sounds of it.

  • amazingly, the software does not record the 'voter serial number' that appears on the card, when a voter casts a vote. So again, duplicating the cards is trivial. Bizarre.

  • all that is required to extract the PIN from an administrator card is a smartcard reader; the PIN is immediately sent in the clear as soon as the card is inserted and the terminal-card protocol initiates.

  • for storage on the internal writable media, between voting and the final upload operation, the logs and votes are encrypted using single DES in CBC mode, with a single shared initialization vector. IMO this is not a big deal as far as I can see, as that's only stored on the hardware; and if someone can read/write to that, they can subvert the WinCE OS anyway.

Then the kicker:

  • the votes are then decrypted before being sent in the clear over a dialup internet connection.

The mind boggles.

security chip-and-pin banking

Nathan Barley v. Chris Morris

The Guardian reports that fake-news genius Chris Morris is collaborating on a new show with Charlie Brooker:

This has led to persistent rumours on internet talkboards and gossip sites that the show will be based around TVGoHome's character Nathan Barley.

Barley, the star of a fictional TVGoHome docusoap, is a loathsome public school educated, Hoxton-dwelling new media type, obsessed with gadgets and extreme sports.

But given Morris's fondness for windups and spoofs, this could just as easily be a red herring.

Apparently, Morris and Brooker have collaborated before on smaller segments. Whatever it is, I'm all for it. Fact times Importance equals News!

Gross: The Indian 'fly boy' has doctors baffled. 'Doctors carried out a cystoscopy to clear the boy's urinary tract, but the treatment has failed because two more flies emerged out of his penis on Monday.' (aaargh)

funny tv media uk

Referrer Spam Gets Smarter

So, it seems the referrer-log spamming is getting worse. The earlier attempts all used a limited set of IPs; probably the real source machines.

However, the latest crop are now relaying through open proxies. Out of a sample size of 10 random IPs, every one was a proxy listed in the OPM blacklist.

The URLs being spamvertised are all pr0n; lots of .ws and .biz hits with pretty colourful names. Take a look here, under any of the top 5 hits. They're outnumbering the legit hits by about 20 to 1.

BTW, it's now pretty clear the practice of referrer-spamming is intended to gain Googlejuice; plenty of other sites have noticed it too. It's worth noting that in my case, it won't work -- my log pages are all off-limits to the Googlebot for quite a while, but the referrer spammers haven't figured this out yet...

Some notes:

  • the spamvertized URLs include perlcoders.com, openproxies.com,
    • cgifactory.net, so steer clear of those sites.
  • the User-Agents are randomised, similar to spamware's randomised X-Mailer headers. Some samples include:
    • Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; MSN 6.1; MSNbMSFT; MSNmen-ca; MSNc00; v5m)

    • Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; SC/5.10/1.14/Telenor; .NET CLR 1.1.4322)

    • Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1)

    • Mozilla/4.0 (compatible; MSIE 6.0; Windows 98; Wanadoo 5.6)

      My guess is they just took a large list of legit user agents, and used that.

  • I've now left them a few little surprises ;)

spam anti-spam google

Spam Gallery, and Fusors

The Field Guide To Spam, by Dr. John Graham-Cumming of POPFile; seems to be a continuation of his 'Spammer's Compendium' talk at the Spam Conference. Lots of examples of filter-evasion tricks used in spam, with a brief description, example, and categorization.

Worth noting some SpamAssassin dogma here: these may seem to be a good way to evade filters. However, since they are tricks that spam uses, and non-spam mail does not, they then make excellent spam signatures -- and the spammers effectively just give us yet another way to identify their spam. ;)

Hacking: Fusor.net is a community of mad scientists amateur fusion researchers, building nuclear fusion devices in their garages and basements. They're not quite self-sustaining yet, but they're definitely working on it.

In the meantime, some pretty pictures of poissors, buggle jets, and fusion stars here. Thanks to Mr. FoRK for posting a link to this... amazing.

anti-spam spam hacks

Missing the point

Gary Robinson points to an announcement of a new music service, BuyMusic.com -- the announcement notes 'users of the service will not necessarily have the freedom afforded customers of ... iTunes ... to transfer the music purchased to multiple computers and portable devices, or to burn it to compact discs.'

How do companies like this get funding? Surely it's obvious that people are not going to sign up for services where they are stuck with crippled DRMware, and don't actually get to own what they buy. 'Here's a car. Oh BTW -- you're only permitted to drive this within 5 miles of your home, it'll conk out if you go any further.'

I suppose it's hardly surprising, but BuyMusic.com informs me that my browser and OS are not welcome, in a surreal throwback to 1999. Ho hum, I'll stick with EMusic, thanks...

In other news, I've just signed up for a mailing list called geowanking. Official: best name ever!

music ireland mp3 drm apple linux internet security

GTLD Nameserver has corrupt data - again

There were some reports on the SpamAssassin-talk mailing list today, that all queries to the now-defunct orbs.dorkslayers.com DNSBL zone are now returning a true result.

Thomas Mechtersheimer pointed out the culprit: it turns out that b.gtld-servers.net, one of the top-level DNS global TLD servers ( run by Verisign, as far as I can see), is returning 65.246.50.11 for every query for a name that does not exist under the .com and .net zones. That includes second-level names, and anything under a nonexistent second-level name.

Take a look. a.gtld-servers.net is returning the correct NXDOMAIN results, b.gtld-servers.net is blissfully sending all this traffic to some poor UUnet dialup ;)

dig 242.110.40.68.orbs.dorkslayers.com. @a.gtld-servers.net.
;; ->>HEADER<<- opcode: QUERY, status: NXDOMAIN, id: 27661
dig 242.110.40.68.orbs.dorkslayers.com. @b.gtld-servers.net.
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 52998
242.110.40.68.orbs.dorkslayers.com. 15 IN A     65.246.50.11
dig 4905893958xc98gdf9g8945.com @a.gtld-servers.net.
;; ->>HEADER<<- opcode: QUERY, status: NXDOMAIN, id: 9454
dig 4905893958xc98gdf9g8945.com @b.gtld-servers.net.
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 42344
4905893958xc98gdf9g8945.com. 15 IN      A       65.246.50.11

Update: It's been fixed, as of about 1200 PDT.

anti-spam spam security dnsbls

Linux and MS: WinCE now customizable

Whoa: 'This spring, Microsoft dropped the price of Windows CE and completely opened its embedded operating system to developers, allowing them for the first time to not only view and modify CE, but also sell products that incorporated the customized code.'

Really? So WinCE developers can modify and then rebuild and sell WinCE with code changes? That's a big deal. It's kind of unavoidable, though. That close to the metal is virtually impossible without source IMO.

coding open-source software

Most-mailed story ever?

this story has been mailed 120 times since it was posted on Yahoo! UK at 11:30 AM GMT yesterday. Which is it? Yep, it's 'masturbating may protect against prostate cancer', premiered at New Scientist. Most mailed/blogged story ever, I'd guess!

For some reason I didn't post this to the blog on Wednesday when it came out, instead posting it to another list. But talking about it with some mates last night, they noted this snippet:

The team speculates that infections caused by intercourse may increase the risk of prostate cancer. 'Had we been able to remove ejaculations associated with sexual intercourse, there should have been an even stronger protective effect of other ejaculations,' they suggest.

Interesting!

health ireland safety

Arlene McCarthy letter analyzed on patents list

In case you're trying to reconcile Arlene McCarthy's public words, about how the proposed EU legislation helps block software and bizmeth patents, and the FFII's public words saying the opposite, here's a helpful email thread cross-posted between the Patents list at AFUL.org and the free-sklyarov-uk list.

Also, Hartmut Pilch notes a prior letter which as yet remains unanswered; 'All she has until now ever done is to send out standard answers to unspecific letters from concerned (and possibly naive-sounding) software developpers. Whenever someone tries to ask her more specific questions, there is no response at all. However documenting the fact that there is no response may also help. So please remember the public letter and point demand a response at every opportunity.'

The Financial Times has an article (paying subscribers only, but that link excerpts a part) which makes clear the difficulties. 'oftware protection regulations across EU member states should be harmonized while also allowing software developers to carry on without the threat of patent searches and litigation hanging over their heads. He argues that the EU directive's wording is opaque: The proposal lists computer implemented inventions as patentable, but this definition fails to establish whether it refers to software algorithms or inventions whose usability is dependent on software. Cane also notes that it is harder to see parallels in software invention and physical invention, and argues that there are few truly novel software inventions because most software is based upon prior work carried out by other people.' (thanks to Gary Robinson for the link)

patents swpats law ireland linux security history eu

I Hate Windows

So I had to edit a Word doc. Left it for a few minutes, the network connection died, so I tried to save it somewhere else.

Foolishly, I did this by hitting File->Exit, knowing (ha!) that I could save it on the way out. All well and good -- until something in Word decided it required the old copy of the doc to save the new one -- even though that was in memory, since I could scroll around it etc. (it wasn't a very long doc).

So it refused to let me save until I restored the network connection. I couldn't be bothered doing that, so I hit Cancel on that 'please restore the net connection' dialog, assuming it'd let me just cut and paste the text, which is all I wanted. Guess what it did? That's right, it just exited, taking the unsaved doc with it. Argh.

I've learned my lesson. Next time, I'll stick with trusty (and sane) Vim. At least it knows how to do an Edit File UI, even if it's not quite as pretty (or featureful).

linux google history

Over-zealous spam filters, pt. xxix

Neil Gaiman writes about how, for several months, mail to his publishers, DC Comics, was intermittently disappearing into a black hole. Eventually, the culprit was found: AOL-TW's spam/virus filters. Any mail containing the word 'Sandman' -- ie. the name of the comic he writes for DC Comics -- was being filtered silently, without notifying either the sender or recipient. Wow. His editor's computer guy reported:

I've been informed that the reason why there was a delay in the delivery of this message was because one of several keywords were found within the message. In particular, the word 'SANDMAN' was found several times. This has been a telltale sign of one or more computer viruses, so the message was set aside to be investigated by a WB security person.

(Via Crypto-Gram)

spam botnets security anti-spam

'Outside the Master Plan'

A good OCWeekly article about Irvine Meadows West -- UC Irvine's trailer park. The trailer park brings a little grit to UCI, and -- bonus! -- is apparently a good, fun place to live. Super-cheap too, at 130 dollars a month.

Unfortunately it's going to be closed and replaced with a parking lot:

To the students, many completing their doctoral theses, the trailer park is their private refuge from the master-planned sterility beyond. They see the housing department's decision to raze the park not as a bow to parking pressures, but a calculated strategy to destroy something 'outside the master plan'--a phrase that's become the residents' motto.

ireland funny property

NZ e-commerce sites getting business-method patent shakedown

The New Zealand Herald reports that 'internet retailers nationwide are banding together to fight a Canadian company's demands for them to pay up or be shut down.' A Montreal-based company called DE Technologies has 'written to several e-commerce operators demanding licensing fees for use of international e-commerce processes.'

The affected ISPs and e-commerce companies are banding together to fight the patent. The NZ Ministry of Economic Development is quoted as saying 'This is a commercial matter. If people wish to dispute the validity of the patent there are mechanisms in the Patents Act (1953) for them to seek to have the patent revoked'. However, one company has received legal advice indicating that an attempt to have the patent overturned could cost up to NZ$150,000, and some background on the FightThePatent site indicates that there may also be only 12 days (or so) from today to do so.

DE Technologies' news page gives an interesting angle on their activities in NZ. It seems Ed Pool, the CEO of DET, believed in 2001 that it was 'an insult to call it a business process. To this day, no one has been able to duplicate this design.' However, it seems that by 2003, at least 40 NZ-based e-commerce outfits have now figured out the details, because that's how many legal letters his lawyers have reportedly sent. One such letter demanded a $US10,000 signing fee, a 'royalty rate' of 1.5% on every transaction, and 11 US cents for each document generated.

Worth noting that the patent has also been granted in Singapore and the US -- where it apparently caused a public outcry and was raised on the Senate floor as an example of a 'bad patent', before it was granted anyway.

patents law swpats ireland uspto linux

Giant NYC Cube Becomes Giant NYC Rubik's Cube

Astor Cube: 'One of the most prominent landmarks in the East Village in Manhattan is a statue of a giant steel cube. The cube was built at Astor Place in 1968, and has stood there ever since. (jm: apparently it's called 'The Alamo' by Tony Rosenthal.) .... in true All Too Flat style, we decided the plain black cube would look nicer as the world's largest Rubik's Cube!' (link via MemeFirst)

art new-york funny

Evan Alice Hughes

Congrats to Craig and Erica! Sounds like there was quite a lot of work involved for Erica -- ouch -- but the end result looks very cute.

Good choice of name, too -- my friends Tom and Colette will be tickled by this one, given that they've named their son 'Evan', and their daughter 'Alice' ;)

life cute kids

Quick Links

Tube Rules -- lessons in London Underground etiquette. My favourite: don't wear massive backpacks.

Dave Malone on broken time-sync software. It seems Tardis, the popular Windows time-syncing software, used HTTP to get a trustworthy timestamp. OK, that's pretty bad -- using TCP/IP against a webserver to try and get a usable time -- it'll be several seconds off in most cases, and is pretty suboptimal in general.

But at least they set up their own server, instead of glomming off someone else's bandwidth and CPU, right? Nope -- they used a server at maths.tcd.ie, along with only 2 others worldwide. And they used GET. And they didn't send a User-Agent header. And the server wasn't even a public time server since 1996 anyway.

All seems well now -- Dave instituted a policy of returning '1999' as the date, and hopefully everyone has noticed by now. ;)

internet privacy http ireland security web networking open-source

Finns Scratch Heads Over N.Korea Porn Claim

Yahoo!: Finns Scratch Heads Over N.Korea Porn Claim:

HELSINKI (Reuters) - Finnish officials were at a loss to explain an allegation made on Thursday by a U.S. official that North Korea has been caught trying to sell pornography in the small Nordic country. 'It sounds strange. It sounds wild,' an official at the Foreign Ministry told Reuters.

U.S. Ambassador to Australia Tom Schieffer made the comments earlier on Thursday to the National Press Club in Canberra, saying North Korea was using a 'mafia-like' business model to make up a revenue shortfall when the Soviet Union collapsed in the early 1990s.

Found on MemeFirst, which looks like a pretty nifty site. Now to see if I can rig up RSS for it. One of the MemeFirst culprits seems to be Stefan Geens, who also has a blog; he reviews 'How The Irish Saved Civilization' in fine style, comparing the annotations of the medieval Hibernian monks to blogging. hmm...

He's stuck in Dublin, right now, trying to figure out a way to get hold of some bandwidth. I wish him luck.

ireland funny politics

Techie Details on The Reverse-Proxy Spam Trojan

Scary stuff -- the techie details of the trojan discussed in the NYT article today -- Reverse-Proxy Spam Trojan - Migmaf (LURHQ):

LURHQ was able to obtain a copy of the trojan - detected from suspicious activity originating from a VPN user on a firewall on a network we monitor. What we found was the trojan was not a webserver at all, but instead: a reverse proxy server. Instead of hosting the content on the victim's computer, the spammer instead maintained a 'master' webserver. We have dubbed this trojan 'Migmaf'.

spam security anti-spam

Snopes: Urban Legends Urban Legend

Brilliant. From this week's b3ta newsletter via the forteana list comes this work of one-liner UL genius:

Snopes conspiracy: ' Snopes was set up in early 1995 by the CIA as a way to debunk popular conspiracy theories, Companies and individuals can now pay to have their urban legend denied on the site, a prime beneficiary being Richard Gere.'

Spam: Hackers Hijack PC's for Sex Sites (NYT). Good article about a (suspected) Russian spam ring using hijacked PCs and reverse proxies to host spamvertized websites.

Ceramics: Anyone who's been following the IRTF's Anti-Spam Research Group mailing list recently, will have come across Mark McCarron's 'proposal' regarding an anti-spam system that has something to do with everyone paying 5,000 UKP, ditching end-to-end SMTP, stopping any non-human-initiated e-mail, and energy from the Pyramids of Giza (I think).

Surprisingly enough, The Reg wrote some unkind words, and now Mark exercises his right to reply. Unmissable, mainly for the details of his reign of terror during school and his 'jack of all trades' abilities.

Great fun, in a kind of 'watching a car-crash' way.

spam anti-spam google security

PI vs IP, and FIT

Nathan Cochrane meets the Aussie Privacy Commissioner:

We're talking about a serious privacy vs piracy debate. On the piracy debate we're talking about management of Intellectual Property (IP). I am a person with Personal Information (PI) and if that is taken away, it is an invasion of my privacy. I would like to hear these people (IP owners) making such a lot of noise about piracy of IP talk about the protections of PI -- then they would have some credibilty. There's a pretty ugly asymmetry in the debate. Both sides need to grow up a bit and be a bit more respective of both sides of the argument.

(Nathan:) For my part, I chipped in that I think it hypocritical that IP owners will kick in my door if they suspect I am stealing their IP, but to steal my PI is just a 'business case'.

I like the 'PI' concept. Perfect timing, given this report on the new ATTBI/Comcast 'Transition Wizard'. Check out this insanity:

Any Comcast user that actually installed the Transition Wizard has given Comcast permission to do the following;
  • 1) arbitrarily open and read your email without your knowledge and/or consent

  • 2) perform a credit check on you and then share that info with whomever they choose

  • 3) Perform firmware upgrades to your cable modem at their discretion, regardless of who owns it.

    You also agreed not to participate in any future class action suits that may be brought against Comcast for whatever reason. You agreed to this and more when you clicked on the 'I Agree' button during the initial installation phase.

Mind you, the actual text isn't posted, so take it with a grain of salt.

Code: Danny's notes on the FIT testing OSCon talk -- that's running a test suite as a Wiki. Interesting, but I have to think about how practical it is in general. Demo here, more complex demo here.

internet filtering filesharing piracy ireland politics uk copyright

Good tech-politics blog

Nathan Cochrane has a weblog. He's a clueful journo who writes about technology for The Age, the Melbourne newspaper -- thumbs up for that; I read plenty of The Age during my sojourn in Melbourne, it's the best newspaper in Oz. (Plus it recommends using Sitescooper and Plucker in their Handheld Howto page, so that's always going to get a +1 from me ;)

But anyway, a very clueful weblog; lots of good journalism straight from the source. Recommended.

LinMagAU.org: Integrating SpamAssassin with MailMan. I really must get around to getting our server upgraded to MailMan 2.1 so we can apply this; I have one list that's getting about 5-10 spams a day, and even with 'subscriber posting only' set, MM 2.0's admin interface is very clunky for dealing with that.

Does anyone know if there's a usable tool to automate Mailman admin BTW? Or give it a good UI?

spamassassin anti-spam email smtp

Corn Syrup, Paid-For RSS, and P45.net

When you move from one country to another, you often notice some details of the taste and texture of the local foodstuffs. For example, pretty much everything in Thailand tasted slightly fishy to my western tastebuds, due to their widespread use of nam pla, a fermented-fish sauce seasoning.

In the US, there's a very definite gooey texture and strong sugary flavour which crops up in lots of foodstuffs -- right down to salad dressings and soft drinks. Eventually I figured it out -- it's corn syrup, which isn't really used at all in Europe. According to this review of Fat Land, here's why it's everywhere:

According to Critser, a leading journalist on health and obesity, America about 30 years ago went crazy sowing corn. Determined to satisfy an American public that 'wanted what it wanted when it wanted it,' agriculture secretary Earl Butz determined to lower American food prices by ending restrictions on trade and growing. The superabundance of cheap corn that resulted inspired Japanese scientists to invent a cheap sweetener called 'high fructose corn syrup.' This sweetener made food look and taste so great that it soon found its way into everything from bread to soda pop. Researchers ignored the way the stuff seemed to trigger fat storage.

The book's thesis seems to be that corn syrup and palm oil are largely to blame for the obesity epidemic. A quick google shows up this LA Times story which covers the book in more detail:

'High-fructose corn syrup is a really low quality, really cheap sugar,' the 38-year-old (Robyn) Landis says dismissively. The syrup starts out as cornstarch, which is then made sweeter by converting some of its glucose to fructose; the more fructose in the end product, the sweeter it is. 'It is not something our bodies should be dealing with. It's completely unnatural.' She also objects to the fact that high-fructose corn syrup turns up in unlikely places, such as ketchup, baby food and baked beans. 'Even chocolate tastes more like sugar than chocolate when it is sweetened with high-fructose corn syrup,' says Landis ...

... Dr. George A. Bray, an obesity researcher and professor of medicine at Louisiana State University Medical Center, also singles out high-fructose corn syrup because the meteoric rise in its consumption closely parallels the jump in obesity rates. 'Nothing else in the food supply does this. It's a very, very striking relationship.'

... Ironically, fructose, which is also known as fruit sugar, was once considered a healthier, 'more natural' alternative to sucrose, that is, old-fashioned table sugar, because of its presence in fruit. In addition, diabetics thought it was healthier for them because it does not raise insulin or blood sugar levels as high as glucose does. However, animal studies and preliminary human studies have found that a high-fructose diet leads to some of the same health problems that are rampant among overweight Americans, including insulin resistance and elevated triglyceride levels, a marker for heart disease.

(I still plan to get my teeth into a corn dog pretty soon though ;) Gotta get that low-grade meat product fix!)

RSS: Ben Hammersley points at this really wierd posting from Adam Curry. Points and laughs, in fact.

As far as I can see, AC wants development of (N)echo to stop, because he dropped 10,000 dollars getting a year's paid placement in the Radio Userland aggregator, or something like that. Well, that was a smart investment. I'm sure all the people thinking about (N)echo are dropping tools right now, accordingly. ;)

Ireland: P45.net now has MT blogs. Cool.

food health usa rss

RID-Spam, The Grauniad, E-Voting

The RID-Spam Act chugs through Congress. This one's very much toothless; according to CAUCE, it's not actually anti-spam really -- CAUCE says:

(it is) 'a gross misnomer to call them 'anti-spam.' 'Anti-consumer,' sure. 'Pro-spam,' even. But not 'anti-spam.''

Amazingly, DMcC notes that it may even de-fang the stronger state laws if it gets passed. Wow.

And check out this quote from the CNet story:

Rep. Bob Goodlatte, R-Va., defended the bill's opt-out approach. Goodlatte said that of the physical junk mail he gets, 'maybe 10 percent of it is something that I have some interest in. For that reason alone I think an opt-out approach is the best solution here.'

Good for him. The way he's talking there, he's looking forward to receiving 700,000 mails per year that 'he has some interest in'. Earth calling Goodlatte -- direct email is not the same as physical junk mail. There's a fundamental economic difference -- with email, the recipient pays. That means you cannot compare the volumes so simplistically. Just say no to One Bite Of The Apple!

US Politics: Rod notes this story: The Guardian coming to the US. Excellent! I think that's a fantastic idea, and they'll clean up.

Consider this -- the only large-circulation print media that (a) people over here read, and (b) had the nerve to really treat the war in Iraq critically, as far as I know, are those two flaming-red anarchosyndicalist rags, the Economist and the Financial Times. (Not only are they not even written in the US, they're quite conservative by Euro standards.) The US media needs more liberal voices.

Actually, I'm exagerrating heavily here. As Craig has pointed out before, the Christian Science Monitor is a pretty good paper, with some critical journalism -- and one with a great story behind it's provenance to boot.

But the Guardian has a pretty much wide open field all the same -- here's hoping they can get the distribution side sorted out.

E-Voting: Some good comments on this Slashdot story regarding e-voting systems.

  • The Brazilian legislature mandated a retrofit 'of 3% (some 12,000 machines) to produce a paper ballot that the voter could peruse and deposit in a box for recount (the first large-scale use of the 'Mercuri Method').'

  • Georgia noted that the e-voting systems 'were all very flashy and glitzy, but all had severe problems with security and/or usability. We eventually decided to run a pilot program in last year's off-year election and try out 5 of the most promising machines in a real-world election. The final winner will be used across the state in 2004. No more hanging chad, but I think we are going to have a whole new set of problems to deal with.'

anti-spam spam filtering

the melting-pot that is blogs.linux.ie

Just taking a look around blogs.linux.ie to see who's set us up the blog recently; here's the results:

  • unfortunately quite a few folks seem to have got bored and left off around mid-April. Ah well.

  • Quite a few lively blogs to add to the blogroll.

  • There's also a burgeoning population of teenage Malaysian blogs, bizarrely enough! planet_aiie, whoelse and corexified. Big slipknot fans it seems.

  • Malaysia's not alone in this -- here's a Jamaican guy. Must be the flag on the favourites icon; green and gold on a black background -- that's more linux.jm than linux.ie. ;) Unfortunately for my patois, he stopped updating in April. Sufferation! Oh well, I'll just have to stick with the Sizzla for my lessons.

  • a Phillipino blog, too!

Just figuring this one -- it seems linux.ie is free and easy to set up a blog at, doesn't have ads, and does decent RSS with full <content:encoded> blocks. All in all, that makes it a pretty good blog platform when you think about it. Fair enough!

blogs ireland irishblogs meta blogging

Consumer groups, open source etc. call on WIPO to discuss open projects

WIPO DG asked to convene meeting on open and collaborative projects to create public goods:

In recent years there has been an explosion of open and collaborative projects to create public goods. These projects are extremely important, and they raise profound questions regarding appropriate intellectual property policies. They also provide evidence that one can achieve a high level of innovation in some areas of the modern economy without intellectual property protection, and indeed excessive, unbalanced, or poorly designed intellectual property protections may be counter-productive. We ask that the World Intellectual Property Organization convene a meeting in calendar year 2004 to examine these new open collaborative development models, and to discuss their relevance for public policy.

I hope this gets somewhere; it'll be interesting to see what the World Intellectual Property Organization has to say officially about open source, the Human Genome Project, the world wide web, and other unencumbered projects of this type.

open-source eu work

Weekend Roundup

Had a very nice long weekend -- big BBQ and watching the fireworks on Friday, some bodyboarding and bodysurfing on Sunday. Very relaxing. Now back to work. :(

Ben Hammersley notes 'the All Time Perfect Daily Mail Story': Asylum Seekers Eat Queen's Swans:

A major investigation has been launched by Scotland Yard into claims that the Queen's swans are being stolen in their hundreds by gangs of asylum-seekers who are cooking and eating them.

The probe comes after a group of men were caught red-handed by police in an east London park. The asylum seekers were barbecuing a duck and officers found two dead swans, ready to be roasted, concealed in bags.

A police spokesman said today: We are appealing for information over the disappearance of swans. There have been incidents of swans being killed, and it appears to be the work of eastern European gangs.

It's a classic of the genre -- combining (a) the queen, (b) cute animals (c) fear of immigrants. That covers all the bases except one. Oh, here it is, bingo! -- it's not entirely true:

Yesterday Scotland Yard stated: 'There is no police report.' While there is concern fuelled by a drop in the swan population, the police spokeswoman added: 'There appears to be a perception that this may be attributable to Eastern Europeans. We stress we have no evidence of this.'

A police spokeswoman ... added that, despite some efforts, they could not back up published claims that asylum-seekers had been caught in east London barbecuing a duck with dead swans concealed near by 'ready to be roasted'. Andy Fisher, head of the wildlife investigation unit, appeared equally baffled. 'I don't know where they have got that from - not the Metropolitan Police.'

It's clearly silly season time again.

Quick Iraq roundup: some photos from Baghdad from Gee, another Iraqi blogger (Gee not in the irish slang sense BTW!); MI6 chief was the BBC's source for 'sexing-up' allegations (Observer).

Also, Guantanamo Bay's military tribunals are hitting the non-US news media again, now that the death penalty has been raised as a possibility. These Observer and Guardian stories note, regarding the two British citizens who've been imprisoned for 18 months (one for 12 months in Bagram airbase): 'If this treatment happened for an hour in a British police station, no evidence gathered would be admissible'.

Next, A left-wing US soldier blogs from Baghdad.

the iraqi's who are working for the u.s....doing what ever task we throw at them...are not to upset with us...some of them have family members in the states and they hope that someday they will be able to join them...they don't hate america at all...and they are conscious enough of what is really going on to make their own decisions...they think that we really are trying to help...they are afraid of the 'militants' because when ever the 'militants' show up and attack us in their neighborhoods we end up destroying everything...many of the guys say that they chase the 'militants' out with any weapons they have...they are just trying to get by...they fear that the 'militants' are using horrible tactics to enlist more support...they are using our retaliation against us...for every home...or car...or newsstand...or coffee shop we destroy trying to protect ourselves another 'freedom fighter' is born...

He talks about Chomsky, links to Michael Moore -- so of course, the neo-con warbloggers reckon he doesn't exist. ;)

Totally down with the new pronunciation of RSS BTW. Waiting for the dust to settle. ho hum.

Finally, Fergus Cassidy, Sunday Tribune tech journo, has a website. Good reading...

ireland dublin funny uk politics history

Over-honest Slogans

my mate Luke passes on this gem:

I was driving along behind a plumber's van today. The van was emblazoned with signs saying that the plumber was a sewers and drains expert. Along the rear bumper of the van was the company's slogan:

'Your shit is our bread and butter'

I am not making this up.

funny business advertising

Senderbase and Alexa

SenderBase is a cool site which lists email traffic volumes for specific senders and organisations.

This will make for some very cool spam tests. As you can see, several of the top ten sending domains are ISPs that, shall we say, may have a few 'issues' with customers' open proxies. They're scattered in amongst the Yahoo!s and Hotmails ;) Then there's a couple of well-known domains that, let's say, have a habit of appearing on the SBL.

Well, not quite as practical, but useful nonetheless, is Alexa's 'traffic detail' feature for the web.

Very nifty; a log-scale graph of traffic as measured by pageviews from Alexa's toolbar, and you can pick 2 sites and compare their hitrates. For example, according to this, SpamAssassin is bigger than Jesus ;)

Thanks to 'Mr. FoRK' on the FoRK list for this URL...

security anti-spam botnets web

Patents: the SSLeay workaround

during this ongoing European software patents thing, I was reminded of a comment I heard a while back from a pro-patent guy.

He was around in the bad old days of SSLeay's patent woes. SSLeay, like many cryptographic products in the 80's and 90's before the RSA and other patents expired, was in a legal grey area due to patent issues. To quote the 'Is This Legal?' section of their FAQ:

That is one of the hard questions on which there is as yet no clear answer. You need to read quite a bit of information to draw your own conclusions - and then go and talk to a lawyer. Again this document is my opinion and as such should be treated in that light - reality could be quite different to how I happen to see things :-).

In short:

  • outside the USA there should be no problems
  • inside the USA RSA hold patents over the RSA algorithms, however if you use RSAREF (which SSLeay can link to) then non-commercial use is probably okay. For commercial purposes you need to talk to RSA to license one of their toolkits (BSAFE) or come to some other licensing arrangement with them.
  • IDEA may be a problem inside Europe and RC4 inside the USA; both can be removed with a simple compile-time option or you can licence the IDEA algorithm.

Eventually, RSA relicensed their algorithms to be freely usable. Thankfully IDEA could be avoided by using alternative algorithms in the SSL transaction, so it wasn't a biggie; most SSL users just switched it off. Finally, the RSA patent finally expired -- so nowadays SSL is commonplace, and using SSL to protect security is a lot easier than it used to be.

Anyway, I'm diverging here... the relevance is this mail from Hartmut Pilch discussing the current euro-swpat proposal. He reckons even the SSLeay defense -- saying 'do not download this software in these countries unless you get these licenses' -- would not work with the current proposal:

To make this clearer: according to the CEC proposal, you still risk being sued even if you only publish a program and warn people 'please do not execute unless you have obtained a license from XXX'.

patents swpats law uspto ireland coding patenting linux

SARS -- back in the fall?

SARS special report: Too soon to celebrate (New Scientist).

There are also suspicions that the first outbreak in the southern Chinese province of Guangdong stopped so abruptly because of the onset of summer. The SARS virus does not survive well in a hot environment, and if most transmission is due to people touching contaminated surfaces, higher temperatures would have reduced transmission.

If the season, rather than human intervention, was the main reason for the end of the outbreak, SARS could return with a vengeance in the autumn. That is what happened with the 1918 influenza pandemic, which killed tens of millions. Fortunately, SARS is far less infectious (so far).

papers china viruses

Debra Bowen: 'MS killed useful CA spam law'

'Let There Be Spam!':

COMMITTEE TAKES CUE FROM MICROSOFT, KILLS NATION'S TOUGHEST ANTI-SPAM PROPOSAL

SACRAMENTO - Urged on by Microsoft, the Assembly Business & Professions Committee today unceremoniously killed SB 12 (Bowen), a measure to create the country's toughest anti-spam law by requiring advertisers to get permission from computer users before sending them unsolicited ads ...

'Does anyone other than the eight members of this committee who either voted 'no' or took a walk on the bill really believe Microsoft has any interest in getting rid of spam?,' wondered California State Senator Debra Bowen (D-Redondo Beach), the author of SB 12, following the bill's defeat. 'Trusting Microsoft to protect computer users from spam is like putting telemarketers in charge of the do-not-call list. Microsoft uses a megaphone to tell everyone how much it hates spam at the same time it's working overtime to kill truly tough anti-spam laws. Why? Microsoft doesn't want to ban spam, it wants to decide what's 'legitimate' or 'acceptable' unsolicited commercial advertising so it can turn around and license those e-mail messages and charge those advertisers a fee to wheel their spam into your e-mail inbox without your permission.'

wow ;) She's not pulling any punches there...

spam anti-spam law filtering

A 'pay-to-email' patent

The concept of a 'pay-to-mail' scheme -- charge people to send you mail -- is patented, it seems. Good, I never liked it anyway ;)

A method and apparatus for determining whether a party sending an email communication is on a list of parties authorized by the intended receiving party. If the sending party is not on the list of authorized parties, an electronic billing agreement is emailed to the sending party indicating a fee that will be charged to the sending party in return for the message being provided to the intended receiving party. Preferably, the present invention is implemented with Internet communications and utilizes a security protocol to enable the electronic transaction to be transacted in a secure manner.

Date: Tue, 01 Jul 2003 15:00:09 -0400
From: "Bob Wyman" ...
To: ...
cc: "'Yakov Shafranovich"' ...
Subject: RE: US Spam patents: Partial list

A new, spam-related, US Patent was issued today. It is a continuation in part of US Patent 6,192,114 which is on the first list of patents I posted to this group.

See: http://patft.uspto.gov/netacgi/nph-Parser?patentnumber=6587550

US Patent 6,587,550 METHOD AND APPARATUS FOR ENABLING A FEE TO BE CHARGED TO A PARTY INITIATING AN ELECTRONIC MAIL COMMUNICATION WHEN THE PARTY IS NOT ON AN AUTHORIZATION LIST ASSOCIATED WITH THE PARTY TO WHOM THE COMMUNICATION IS DIRECTED

Abstract A method and apparatus for determining whether a party sending an email communication is on a list of parties authorized by the intended receiving party. If the sending party is not on the list of authorized parties, an electronic billing agreement is emailed to the sending party indicating a fee that will be charged to the sending party in return for the message being provided to the intended receiving party. Preferably, the present invention is implemented with Internet communications and utilizes a security protocol to enable the electronic transaction to be transacted in a secure manner.

------------------------------------------------------------------------

Inventors: Council; Michael O. (186 Hurt Dr., Cordele, GA 31015);
Santos; Daniel J. (3525 Roswell Rd., #721, Atlanta, GA 30305) Appl. No.: 783340 Filed: February 14, 2001


Asrg mailing list ... https://www1.ietf.org/mailman/listinfo/asrg

spam email privacy anti-spam security

When Good Games Go Bad

Wired: Hackers Put 'Bane' in Shadowbane:

'Then we realized that somehow an insane god had taken control of our world and was out to kill us all.'

The population of an entire Shadowbane town was forcibly moved to the bottom of the sea, where they drowned. City guards turned feral and attacked town residents. Mobs of never-before-seen superpowerful creatures, seemingly spontaneously spawned from the ether, began to prowl the streets unchecked, killing characters in the most painful way possible.

games gaming hacking

Audioscrobbler

Audioscrobbler is cool. Check it out -- this is its log of my xmms listening habits, neatly cross-linked and referenced. (The cheesy 'Liberty X' listens were Catherine, I swear.)

Anyway, AS is a bit like Napster's 'explore other person's music collection' feature, which was cool for picking up recommendations -- but this one is based on actual plays, and without the link to a service that the RIAA would want to see shut down ASAP. ;)

It can come out with some pretty bizarre results -- for example, 'people who listen to Thievery Corporation also listen to Radiohead', according to this. Mind you, that's probably correct...

Prediction: I'll wind up being top of the list for listening to Acen's tunes by the end of 2 weeks. That's the plan at least ;)

music mp3 ireland filesharing linux internet drm

Spam filters and FTC's 'Do Not Call' list

Wired News: Yahoo! Spam Filter Thwarts FTC:

Consumers who used Yahoo Mail e-mail accounts to register for the Federal Trade Commission's new do-not-call service were met with an ironic twist Friday -- Yahoo's spam filter intercepted confirmation messages sent from FTC servers.

'Our tests showed that Yahoo's spam filter was automatically sending the confirmation messages from the do-not-call list into users' bulk-mail folders,' said NetFrameworks co-founder and CTO Eric Greenberg. 'The irony of it is that the spam filter is blocking the very thing that's supposed to help you stop getting spam over the phone.'

FWIW, I signed up, without any hitches.

As noted elsewhere, their mail-sending systems were massively overloaded -- an insane quantity of people were also signing up at the same time, from what I've heard.

But a day later, the confirmation message eventually came through, and got run through my 'dogfood' SpamAssassin 2.60 installation. That gave it -5.2 points. Not bad, considering they didn't have reverse DNS records for the machines sending the mails out ;) (update: they do now, btw.)

In case you're wondering, the tests it hit were: BAYES_00,CLICK_BELOW,DATE_IN_PAST_12_24,NO_REAL_NAME. Pretty respectable, really. Aside: that message getting a BAYES_00 match is impressive, given that (a) that Bayes db was initialized entirely from auto-learned mails, no hand-training; and (b) I'd never received a mail from the Do Not Call registry operators before.

Tamales: this is cool -- San Francisco's boozy culture paid homage last night to 'The Tamale Lady':

Tonight, Zeitgeist will swell again for Ramos' 50th birthday party. There, San Francisco filmmaker Cecil B. Feeder will premiere his mini-documentary 'Our Lady of Tamale,' featuring 30-second songs submitted by dozens of San Francisco musicians.

Isn't that nice. Ben says it went well. Somehow or other we missed her tamales last time we were up, but I'll be sure to get one next time...

anti-spam spam challenge-response

Closed Hardware, PDAs etc.

BoingBoing with a cautionary tale. When you buy a HipTop Sidekick from T-Mobile, you're not really buying it in the way you'd imagine -- instead, you get to hold it while they operate the software, as far as I can see. As of this week, T-Mobile are going to remotely erase the games that were included with the device, because they are 'no longer supporting' them. And tough luck to Sidekick owners.

As BB sez:

Who owns your Sidekick? T-Mobile does, apparently, even if you spent full retail on it (I dropped 250 dollars on mine). You need T-Mobile's permission to install software on their device. T-Mobile will, from time to time, decide to erase software from your device. And when you stop subscribing to their service, T-Mobile will delete all your data forever, without giving you any mechanism for moving it off the device (and without giving you the ability to design a tool that would let you do this).

I don't really get it -- I mean, this is the reason Palm platforms won in the handheld arena for so long; the user's control over what they can install, the developer's freedom to write new apps for the users to install, and the (comparatively) open aspects of their SDK and protocols so that it can be sync'd to by lots of desktop apps.

Competing with all the other PDAs, based on hardware or UI alone, isn't enough -- unless you're Apple with the iPod. Surely the Sidekick OS developers get this? (Maybe what happened is the OS developers get it -- but T-Mobile don't.)

Talking of the iPod -- Gary Robinson notes that Pixo, the vendor of the OS software used on Apple's iPods has just been bought -- by Sun. It seems Pixo nowadays sells server-side Java thingies, which seems wierd for a developer of OSes for handheld platforms -- until you read this article from January 2002, which reports that Apple and Pixo were at loggerheads anyway, due to contractual difficulties, and that Pixo had given up on embedded-OS work, due to a shortage of clients.

Anyway, I wonder if Apple got a licensing deal that gave them the source and allows them to update the Pixo OS themselves, if Sun decide to drop that product. (Given that Pixo themselves turned around and set the company in a totally oblique direction, I'd reckon it's likely.)

Spam: Rod says the National Do Not Call Registry has launched. Sign up here -- but wait a while first, it's massively overloaded right now...

hacking phones gaming

Cocaine-laced Euros

German euros 'full of cocaine' (BBC):

Almost all euro banknotes circulating in Germany contain traces of cocaine, German researchers say. ... 'Nine out of 10 banknotes show clearly measurable amounts of cocaine,' Professor Fritz Soergel of the Institute for Biomedical and Pharmaceutical Research in Nuremberg was quoted as saying by Reuters news agency.

... The concentrations of cocaine on Spanish euro notes were almost a hundred times that of what was recorded in Germany; ... Professor Soergel said that his team was 'almost knocked flat' by results of yet another recent study in Barcelona.

ireland science statistics banknotes cocaine drugs fraud privacy

Search Engine Optimisation

Tom Coates on search engine optimisation. Summary: they don't work; smart search engines realise you're trying to game them, and will ignore or penalise your site as a result. The correct answer is to provide interesting/good/linkworthy textual information, and keep superfluous eye candy at a sensible level. I agree with his essay, FWIW.

Personally, I reckon Google deserve a lot of credit for turning the web around, from a flashy, Flash-laden animated DHTML blinky-blink medium, back into one where text is king. Once it got recognized that Google used titles, h1 tags, and other semantic markup as key metadata, and that the gimmicky stuff is unindexable, the never-ending slide into flashy blinky-blink land was halted. Phew!

Aside: Labour MP Tom Watson has a weblog?! Wow. He'd get my vote straight away, no matter what his policies were -- that's transparency ;)

Interesting -- so does Liberal Democrats MP Richard Allen. This is really amazing. He even links to SpamAssassin as part of a discussion on the All-Party Internet Group's spam summit to be held on July 1st!

It's worth noting that his comment here notes that the APIG concept seems to be leaning towards prosecution of spamvertised products; advertise via spam (sent by you or by a 'spam outsourcing' company), and you're liable. A very sensible approach, as long as they can avoid the danger of malicious spammers spamvertising a product without that company's permission -- a la what happens regularly to SpamCop and SpamHaus.

google uk news

Twenty Questions AI

Play 20 questions against an AI. Very cool; it got 'artichoke heart' and 'volcano' for me, the first within 30, the second within 20. It also whinged about a few questions I'd 'answered inconsistently' on the first one (well, they were stupid questions ;)

Log in as an anonymous user to try it out.

art music technology

QuickThread

Marc Canter blogs about QuickThread, one of the new services at Steve Yost's QuickTopic.

It's a great concept. Want to take a thread offline, or share it as a dedicated forum of its own, without losing the concept flow? Just select all the context messages, forward as attachments by mail to the QT site, and it'll create a new thread with that context intact. Totally simple. (see the Pictures).

Science: In this interview with Matt Ridley at edge.org, Matt notes:

... There's another phenomenon going on too, which is equally important and which again people in these kinds of debates over human nature have missed. ... behavior affects genes. It doesn't change the code of the gene, and it doesn't change the encoded genome ... what I'm talking about is changing the expression of genes through things you do in your life.

(for example:) ... When you're under stress, the physiological result is that cortisol increases in your body and has a lot of effects. Cortisol is a transcription factor; it actually alters the expression of certain genes. It does so largely in the immune system, which results in the suppression of immune activity.

Wow. I never realised hormones could have that effect. Good article, as usual...

web science health

'My Wife, Jody'

Incredible. The text 'My wife, Jody' has appeared, reliably, in spam for the last 5 years -- I just got one today. (I haven't actually seen one in my inbox for a while, though, since the chain letters that copy it generally get pretty high scores -- this one hit a respectable 48.2 SpamAssassin points, no less.)

Here's the text it appears in:

MORE TESTIMONIALS

'My name is Mitchell. My wife, Jody and I live in Chicago. I am an accountant with a major U.S.Corporation and I make pretty good money. When I received this program I grumbled to Jody about receiving 'junk mail'. I made fun of the whole thing, spouting my knowledge of the population and percentages involved. I 'knew' it wouldn't work. Jody totally ignored my supposed intelligence and few days later she jumped in with both feet. I made merciless fun of her, and was ready to lay the old 'I told you so' on her when the thing didn't work. Well, the laugh was on me! Within 3 weeks she had received 50 responses. Within the next 45 days she had received total $147,200.00 ........ all cash! I was shocked. I have joined Jody in her 'hobby'.'

Mitchell Wolf M.D., Chicago, Illinois

It's amazing that the chain letter is never changed, given that for the last few years they are all sent using spamware applications, so the senders must have some techie know-how.

I wonder if there's a real Mitchell Wolf M.D. in Chicago, and what he'd think of 5 years of faked testimonials using his name?

spam anti-spam filtering challenge-response

Some snippets

Maciej covers some ground I've been wondering about, comparing his experiences with the French state system and that here. Definitely worth reading, and I'm looking forward to tomorrow's.

Oops! NZ channel 'TV3 has apologised after a graphic labelling US President George W. Bush a 'professional fascist' flashed up during its primetime news.'

Henry Farrell writes about homesickness, quoting Dante. It's such a great quote, I'm going to just reproduce it here:

These are of course silly things to get worked up about; but it's a universal experience for expatriates to miss the little things as much (if not more than) the greater ones. Dante, who was exiled from Florence, speaks of how

You shall leave everything you love most dearly:
this is the arrow that the bow of exile
shoots first. You are to know the bitter taste
of others' bread, how salt it is, and know
how hard a path it is for one who goes
descending and ascending others' stairs.

He's talking about two things here. First, as an exiled Florentine, he doesn't like salty bread. Florentines don't use salt when baking (the result, as far as I remember, of an extended period when the Pisans cut off their salt supplies), so that their bread tastes like blotting paper to non-natives (I lived in Florence three years: my advice to outsiders is to order pane Pugliese in the local bake shops when possible). Second, spiral staircases in Florence tend to curve around the opposite way from staircases elsewhere. Dante's main point is unassailable; as an exile, you feel longing for the small and unexceptional parts of daily life in your home country, and a quite extraordinary degree of comfort whenever you find them again. Which is why my fridge is now stocked up with Kerrygold.

travel ireland history politics

NetFlix patents the DVD library

So NetFlix have patented their business method; that is, subscribing to video/DVD rentals -- where instead of being charged per disc, you are charged a monthly fee and can keep the rentals indefinitely without late fees. Patent here. Now, NetFlix is a very cool service, I've really been enjoying it. But this patent is a bit nasty.

Think about it: what's difficult about the NetFlix setup? Is it thinking up the concept for how the business works, as described in the patent?

Or is it executing the details, setting up efficient shipping infrastructure, tracking, billing, stock management etc., efficiently enough to make a profit?

Bad news for these companies, who are now infringing:

  • GameFly, which is the NetFlix model applied to games.
  • GreenCine, a more indie- and anime-oriented DVD site.

As one commenter on the /. story noted, 'imagine if McDonalds had patented the drive-thru'.

patents swpats uspto ireland linux health

Hakim Bey

Interesting -- some thinking about the net, blogs, etc. on Biroco.com meanders into a mail from Hakim Bey:

(...) I'm utterly not responsible for the plethora of Netishness that coagulates around my work. Personally I never 'uploaded' a word. Others do it, mostly without my permission and w/out even bothering to inform me. Some of it isn't even mine - forgeries & often dis-info are rife. The Net is a pathology.

I not only don't own a computer - I've 'taken agin' 'em' & have become a cyber-curmudgeon. Basically I'm only interested in things that don't have websites. I refuse - or rather am incapable of - compensation for the demise of the physical world (you know what I mean) by losing myself in 'the terminal state of screenal involution' to quote a line that came in-somnia last nite.

Joel goes on to say:

Most who have read Hakim Bey seem to imagine that he regards the web as a TAZ (Temporary Autonomous Zone), but in fact he doesn't, since the physical component is missing, virtuality is not physical, at most all the web can be is an organisational mouthpiece for a TAZ but not a TAZ in itself. I agree with him, but myself, despite chucking my TV in the bin over a decade ago and Zen wanderings away from this medium, I got ensnared in the web nonetheless and do sometimes wonder whether it is indeed 'compensation for the demise of the physical world'. We'll see, at present I regard it as a curious assemblage project and a potential widening out of creativity.

internet censorship web security

'The Goblin'

Observer: Russia's cult video pirate rescripts Lord of the Rings as gangster film. This sounds hilarious -- although I bet New World (iirc?) aren't so happy about it...

They call him the Goblin. He is the new toast of Russia's massive pirate video industry, his films sought all over Moscow. The trick of his silver screen success is that the Goblin redubs Hollywood movies, using his own 'better' Russian alternative to the script.

A former senior police investigator from St Petersburg, Dmitri Puchkov began by making fresh translations to replace the appalling subtitles on pirated films. But now his cult following has found pan-Russian appeal, with a ground-breaking rewrite of the first two parts of The Lord of the Rings.

In a move that has taken the Russian pirate disk world by storm and infuriated traditionalists and copyright lawyers, Puchkov has completely changed the script, turning the 'good' characters, like Frodo, into bumbling Russian cops, and the 'bad' Orcs into Russian gangsters.

The new, irreverent version of The Lord of the Rings is set in Russia. Frodo Baggins is renamed Frodo Sumkin (a derivative from the Russian word sumka, or bag). The Ranger, Aragorn, is called Agronom (Russian for farm worker). Legolas is renamed Logovaz, after a Russian car company famed for its Ladas. Boromir becomes Baralgin, after a Russian type of paracetemol.

Gandalf spends much of the film trying to impress others with his in-depth knowledge of Karl Marx, and Frodo is cursed with the filthy tongue of a Russian criminal.

movies books film

2000 IT bosses say NO to EU software patents

FFII have issued a press release: '2000 IT bosses say NO to EU software patents, call for rejection of McCarthy software patent directive proposal':

A 'Petition for a Free Europe without Software Patents' has gained more than 150000 signatures. Among the supporters are more than 2000 company owners and chief executives and 25000 developpers and engineers from all sectors of the European information and telecommunication industries, as well as more than 2000 scientists and 180 lawyers. Companies like Siemens, IBM, Alcatel and Nokia lead the list of those whose researchers and developpers want to protect programming freedom and copyright property against what they see as a 'patent landgrab'.

Reminder: there's only 7 days left before the plenary on June 30th, so if you're European, write to your MEP backing FFII's position. Full text here.

swpats patents eu software open-source ireland

NZ flatulence tax outrages farmers

BBC: NZ flatulence tax outrages farmers:

New Zealand's farmers have criticised a proposed tax on the flatulence emitted by their sheep and cattle. The move is part of the Wellington government's action to meet its commitments under the Kyoto Protocol on global warming.

Scientists estimate that methane emitted by farm animals is responsible for more than half of the country's greenhouse gases.

Flatulence from cows, sheep and other ruminants is a serious environmental problem, accounting for about 15% of worldwide emissions of methane - one of the most potent of greenhouse gases.

climate-change ireland carbon

My Thoughts on 'Greylisting'

'Greylisting', as described here, has received a lot of attention recently. However, I don't think it's a goer; here's why:

  • Firstly, as Alan Leghart pointed out on the SpamAssassin-talk list:

    This method proposes to delay EVERY SINGLE MESSAGE until a database match is found for sending IP, FROM, and TO. So...we punish everyone in the world, and hope that a delay of one or more hours is considered 'acceptable'?

    Read his message for a sample typical daily scenario which shows how bad this can be. Maybe some people already expect a mail to take several hours to reach a recipient. In that case, you need to fix your mail server. Even the 300Mhz SpamAssassin spamtrap server gets through mail faster than that, and it's seeing an absurd mail load ;)

  • Secondly, many VERPing mailing lists and newsletters will need manual whitelisting. Requiring manual intervention == work == what spam filtering is trying to reduce == bad.

  • Thirdly, it assumes spammers would never introduce retries into their spam-tools if it took off. Tempfailing, what this is based on, is effective right now because spamtools don't retry. But every proposed solution has to consider what would happen if every server admin in the world implements it, and spammers then want to subvert it.

    IMO, 'greylisting' would work fine until the spamtools start retrying, then we're back to square one -- except some legit mail takes a long time to get delivered, and the bandwidth wasted by spam has doubled due to all those retrying spams.

anti-spam spam smtp spamassassin botnets security filtering

EU Patents -- heavy on the spin

Sounds like the pro-swpat lobby has taken an interesting tack in their PR; IDG's Infoworld reports that:

The European Parliament is likely to support a law that permits software patents but limits their application to inventions that have a technical effect outside of just a computer program. A program could only be patented if it runs in conjunction with some sort of device such as an intelligent household appliance or a mobile phone.

But bizarrely, that's exactly what the proposal does not suggest, and that's exactly what the anti-swpat lobby want it to suggest! Totally, totally wierd.

swpats patents law linux uspto ireland software patenting

Software patents update: plenary in 10 days time!

Despite heavy opposition from a coalition of European SMEs and the Greens/EFA faction of the European Parliament, and despite 2 committees suggesting large amendments, Arlene McCarthy's pushed the patent 'reform' through the JURI committee of the European Parliament. It is now going to be debated in an EP plenary in 10 days time. It seems likely there'll be a vote on adopting it then, too. We're being railroaded here. :(

If you are a European and bothered by software patents, now is the time to write to (or even email) MEPs asking them to oppose this directive; it's the 'proposed software patentability directive as amended by JURI' (COM(2002)92 2002/0047).

The letter should support the Eurolinux and/or Green position.

I've already received one reply, from Nuala Ahern, a Green MEP for Leinster, who's happy to take the Greens/EFA line (and responded very quickly, all credit to her!). But the question is, who else among the Irish MEPs is likely to vote on this issue -- and how do we effectively lobby in such a short time?

Some background links:

Anyway, if it passes it's not the end of the world, according to Karl Lenz; I'm not sure I agree with his conclusions though ;)

ireland patents swpats eu politics law linux dublin

Leftie TV in the US, and the GIF patent

So I caught Frontline on PBS last night. At last, some leftie TV that isn't The Daily Show! ;)

It covered -- in excruciating detail -- something I'd been wondering about; the massive cost (to end users) of healthcare and prescription medication in the US. The program nicely demolished the 'but all that money is needed for R&D' line.

Bottom line: the US drug companies are making 18-22% profit, and they're not letting go of that. (The median for the Fortune 500 is 3.3%.)

That's pure profit -- not going back into R&D or similar. The breakdown of the biggest revenue sinks averaged across the sector, at the end of the program was: 22% profit, 18% advertising and marketing (one conglomerate in particular spent more on marketing than Pepsi), a couple more aspects of the process, and then, 4th or 5th on the list, 11% of that revenue makes it to research and development.

This should be a huge issue here, but isn't. I can't figure it out.

Patents: Kuro5hin has a nice wrap-up of the GIF patent story, now that the patent has finally expired (excerpt: 'Unisys does nothing'). But what's this? It's still extant in Europe, not expiring until a year from now? Great example of the EPO allowing software patents to be registered, even though they're not legal in Europe.

Mind you, it's irrelevant now, as (thankfully) Jean-Loup Gailly and Mark Adler wrote the gzip compression algorithm, and gave it to the GNU project. Since then, gzip has now spread into every tool and virtually every platform that might possibly need compression.

patents swpats health open-source ip

George Galloway Papers Were Forgeries

CSMonitor:

On April 25, 2003, this newspaper ran a story about documents obtained in Iraq that alleged Saddam Hussein's regime had paid a British member of Parliament, George Galloway, $10 million over 11 years to promote its interests in the West.

An extensive Monitor investigation has subsequently determined that the six papers detailed in the April 25 piece are, in fact, almost certainly forgeries.

The CSMonitor is usually a pretty good paper I hear, and their decision to print this retraction on their front page is a nice sign. But it's worth noting that it took 2 weeks -- not until the UK's Daily Mail retracted their story, citing that they had determined their documents were forged -- before the Monitor thought to check out the letters' credibility.

And check this out for gullibility:

Smucker recalls that it was the general who brought up George Galloway's name first at their initial meeting. After the reporter indicated an interest, the general said he knew where those documents were, and that he could have them for Smucker in 24 hours. Smucker says Rasool told him that one of his neighbors, who left Baghdad to attend a Shiite pilgrimage in Karbala, held the documents.

Upon Smucker's return the next day, the general showed him the Galloway documents as well as the boxes of others on various subjects. After hiring the neighbor, Smucker left with the boxes.

'I had no knowledge that the general received any of the 800 dollars, though now that I know the documents are forgeries, I have my suspicions,' says Smucker. 'At the time I was operating on the premise that these were entirely authentic.'

Suuuure!

security spam uk hacking nsa

The Windows Find Setup Wizard

Joel writes about a canonical Windows UI mistake: 'unequivocally the most moronic 'wizard' dialog in the history of the Windows operating system. This dialog is so stupid that it deserves some kind of award. A whole new category of award.' It is, of course, the Find Setup Wizard dialog:

The first problem with this dialog is that it's distracting. You are trying to find help in the help file. You do not, at that particular moment, give a hoot whether the database is small, big, customized, or chocolate-covered. In the meanwhile, this wicked, wicked dialog is giving you little pedantic lectures that it must create a list (or database). There are about three paragraphs there, most of which are completely confusing. There's the painfully awkward phrase 'your help file(s)'. You see, you may have one or more files. As if you cared at this point that there could be more than one. As if it made the slightest amount of difference. But the programmer who worked on that dialog was obviously distressed beyond belief at the possibility that there might be more than one help file(s) and it would be incorrect to say help file, now, wouldn't it?

It's a great article; there's also some fantastic examples of stupid UI tricks that shouldn't be possible, like detachable menu bars. Read it here.

microsoft windows ui usability

Sitescooper and RSS

I did this a while ago, but I've been very busy in work and haven't had time to mention it. But it's worth doing some preliminary pointing at Sitescooper RSS.

Basically, I've added RSS output to Sitescooper, the venerable HTML-scraping script that can disassemble a news/blog/reading-material website efficiently, use a cache, log in, cope with redirects, figure out when stuff is new and when it's old, perform diffs, confuse you with copious regular expressions, etc. etc.

Sitescooper was originally oriented entirely towards display on a Palm; then new PDAs came out that could do good text or HTML display, so they're now supported too; and now, I'm no longer commuting and using an RSS aggregator instead for that kind of daily reading, so RSS is the natural next step.

Basically, what this means is that those annoying blogs that don't include the full text in the item block, or those websites you like that don't have an RSS feed -- make a site file, and scrape them into your aggregator yourself!

This code is present in the current Sitescooper CVS version; the only doco is really what's in that RSS directory on sitescooper.org.

If your interest is piqued, take a look...

rss feeds blogs scraping atom aggregation

Trademark craziness

rOD gets an email:

I found your web site, http://www.groovymother.com/archives/week_2002_10_20.html has a reference to a Clue-By-Four ™. Unfortunately, my company owns the trademark to that term, and I am in the process of bringing that product to market. My lawyers have told me that if you do not remove that reference, it dilutes my trademark.

I would much rather ask you politely to remove references to Clue-by-Four™ than have an ugly lawyerese letter sent via certified mail, etc.

WTF? Applied for in 1999, and it refers to a 'novelty toy, namely a foam rubber two-by-four shaped board'.

patents copyright funny law

Win4Lin

A glowing review of Win4Lin 5.0 from 'Open for Business'.

Gotta say, I use Win4Lin regularly, and it's totally flawless. I had a bit of difficulty getting it installed -- the installer didn't like my kernel for some reason, if I recall correctly, and I had to go grepping through the install script (!). But it's fantastic once it's running.

The really impressive thing is when it boots Windows (in a window on your Linux desktop) much faster than Windows boots natively on the same hardware ;) Still haven't figured out how it does that.

It does a nice job of a virtual network interface too; easier to admin than VMWare's fake-net-with-DHCP thing. It just insmods a new network module, with a new ethernet address, and that responds to arp requests alongside your 'real' Linux interface's address. Then all the control of IP address, network etc. is under Windows control.

I haven't found an app that doesn't work with it yet. (Mind you I hear Direct/X isn't supported yet fully, so most games are probably out.)

I've even used it to watch Quicktime movies -- which is pretty impressive when you consider that they're displaying to a (Win4Lin) framebuffer, which is then displayed to another (VNC) framebuffer, which then displays to the hardware.

linux networking coding aws ec2 http

IrishWAN National Conference

IrishWAN are holding a national conference:

IrishWAN the networking group with the goal of building a community owned and run island wide area network infrastructure, will be having a national conference in Limerick on Saturday 28th of June 2003.

There will be IrishWAN members from all across the country, with presentations about wireless technology, updates of activities in many areas, and presentations from Irish wireless suppliers.

Full text here.

Date: Thu, 19 Jun 2003 10:58:15 -0000
From: Robert Fitzsimons ...
To: ...
Subject: IrishWAN National Conference

IrishWAN National Conference

IrishWAN the networking group with the goal of building a community owned and run island wide area network infrastructure, will be having a national conference in Limerick on Saturday 28th of June 2003.

There will be IrishWAN members from all across the country, with presentations about wireless technology, updates of activities in many areas, and presentations from Irish wireless suppliers.

The conference is open to anybody who has an interest in building or using the IrishWAN network, and is an ideal opportunity for existing and new members to get together to talk about wireless technologies. There will be a 5 Euro charge at the door to pay for the room.

The conference will start at 12:00 and should finish up at 17:30 on Saturday 28th of June, the location will be The Two Mile Inn, Ennis Road, Limerick.

More up-to-date details and the agenda are available at <URL:http://www.irishwan.org/board/showthread.php?threadid=996>.

Hope to see you all there.

Robert Fitzsimons DublinWAN Chairperson ... http://wwww.irishwan.org/


ISOC Ireland members mailing list ... http://ireland.isoc.org/mailman/listinfo/members

ireland dublin barcamp

Unicode

Oops! Looks like 2-byte Unicode -- UCS-2, aka Unicode 1.0 -- will be running into trouble shortly; according to this and this on debian-i18n from back in 2000, several Asian charsets will shortly require 4-byte Unicode characters, which means using either UTF-8 or UCS-4. In particular, correct display of proper nouns in Japanese apparently requires use of the 4-byte planes.

Unicode 1.0 is used widely, in MS products and Java. Expect 'flag days' galore when this has to change.

Unicode 2.0 introduced a concept called a 'surrogate pair' to fix this; it's basically introducing multibyte characters into the supposedly fixed-width character-based UCS-2; so all those 'length == nchars' assumptions will break -- again. Argh.

Now I know why the Linux vendors are going for UTF-8 instead...

gmail funny security

MSN's Google-Killer

Maciej, Jeremy and Dave have all been blogging about this: Microsoft have unleashed MSNBOT, a new web crawler (judging by the robots.txt string, written in COBOL) which heralds their new search service which will topple Google.

My thoughts: dream on, guys.

What makes Google cool? Fast, accurate searches, and no ads. OK, MSN could do fast searching; that's doable, it's just a technical matter.

But what does the latter require? IMO, it takes very strong technical leadership, willing to resist any and every business unit that fancies dropping some cruddy ads on the front page; it's a cultural issue. This is especially tricky where ads (and money) are involved. Now go take a look at MSN.com. See what I mean? I rest my case.

google web spam

Here comes the science bit - evaporate!

New Scientist reports that 'cosmetics manufacturers are keen to appear cutting edge, and often blind consumers with scientific jargon. But buzzwords like nanocapsules - currently one of their favourites - could be their undoing.'

Scare stories about nanotechnology turning the world to 'grey goo' have led Caroline Lucas, Green Party MEP for South East England, to call for new regulations - and one of the targets she has in her sights is the cosmetics industry. Her website claims that 'thousands of women are acting as unwitting 'guinea pigs' for the cosmetics industry...with many products containing ingredients manufactured by 'nanotechnology'.'

Famous facial products, such as L'Oreal Plenitude and Lancome's Flash Bronzer Self Tanning Face Gel, do indeed contain billions of nanoscopic capsules designed to help the skin absorb the cream's active ingredients. Though there's not a goo-making nanobot in sight, Lucas claims to be 'horrified to find nanotech products sitting innocently in my bathroom cabinet'.

We wonder what she expected them to do to her. Drain the colour from her face and make it go all mushy?

open-source silicon-valley google

more on SCO v. IBM: 'All your base are belong to us'

Ben forwards a link to this Byte article, SCO: All your base are belong to us. His commentary:

One day I'll have a blogtastic dalymount.com, but for the moment, have you seen this priceless interview, in which SCO goes over the edge into complete barking insanity?

'We believe that UNIX System V provided the basic building blocks for all subsequent computer operating systems, and that they all tend to be derived from UNIX System V (and therefore are claimed as SCO's intellectual property).'

His emphasis. But let's face it, he's emphasising the right part ;)

So they now think they are owed money by every modern OS: that includes FreeBSD, Windows, Apple, presumably QNX, etc. etc. Linux was just the easiest one to start with, since the source is available and IBM (with their deep pockets) are closely allied with it. MS have already paid up for a SCO license, although many commentators see this as a means to support SCO in their anti-UNIX lawsuits.

In more detail, SCO claim to have full IP rights to several major components of any high-spec OS:

  • JFS (Journalling File System).
  • NUMA (Non Uniform Memory Access).
  • RCU (Read-Copy Update).
  • SMP (Symmetrical Multi-Processing).

Let's pick one there: RCU in Linux seems to have originated (at a glance) from code developed by Sequent for their DYNIX/ptx UNIX, which was an AT&T UNIX System V-based OS. Sequent ran into trouble, and were bought out by IBM. Later, patches to implement RCU were submitted by IBM from Sequent's code.

SCO now owns the AT&T UNIX System V IP; therefore SCO owns the RCU code in Linux -- even though Sequent developed it independently, on top of the System V base, as far as I can see. Hey, that's even more 'viral' than the GPL -- at least the GPL tells you in advance what mistakes you'd have to make for this to happen! ;)

In other words, it seems their POV is that, if any code came anywhere near other code that may have been part of the original AT&T codebase, it's now tainted with SCO's own 'viral license'. Absolutely insane.

It's unclear exactly how 'all subsequent computer operating systems' also infringe this viral license, but SCO reckon they do.

In the meantime, they don't seem to have realized that these kinds of over-broad claims are not looked on favourably under EU law; while they make cartooney threats in the US, they open themselves up to all sorts of anti-trust-type claims elsewhere in the world. But then, at this stage I don't think they plan to actually offer any products, or operate as a software company, so they probably don't really care about that.

To really muddy the waters, an ex-SCO employee has recently made allegations that SCO copied code from the GPL'd Linux kernel into their UnixWare product.

Ah, fireworks. Anyway.

For a kinder, gentler form of total insanity, check out the guidelines for forming 'inexplicable mobs' in Manhattan -- via bb. Totally cool.

open-source patents copyright

Software patent proposal passes

GREENS/EFA: Patent vote fails Europe's software programmers. Damn.

UK and German MEPs, in rejecting amendments to the report, have ignored the opinions of the Economic and Social Council, the Industry committee, the Culture committee, 140,000 people and 30 leading software scientists who signed two petitions to the Parliament, as well as the 95% of the European citizens who took part in a European Commission public consultation.

So I guess the next step is figure out who those MEPs were, and make sure they never get our votes again.

There's still time though: Mercedes Echerer MEP (Greens - A) notes: 'You can be sure that the report will have a very bumpy ride when it goes to plenary in September with one third of committee members in opposition.' We can at least try to let our voices be heard by the other two-thirds...

However, in some good Euronews: the Czech republic has passed a referendum on joining the EU.

eu ireland google open-source

More on Software Piracy figures

In response to this post regarding Ireland's piracy rate of 42%, Simon pointed out a possible flaw in the methodology on the forum;

'Although they could be comparing high software usage to negligible software sales in Ireland. Anyone with a half decent purchasing dept will buy from the UK or US to avoid ridiculous euro pricing. Compare prices on the Macromedia Store's shop, Studio MX in International English for $899 in the international store, $1133 in the UK store, or $1180 in the Euro store (all prices ex-taxes).'

So I took a look over the weekend. Here's the page on the survey. In the PDF, page 12-13, they describe the methodology. my comments:

  • 'To estimate software demand, IPR developed ratios for the amount of software installed on each PC. This was developed from market research on the U.S. market.' Do all markets really use the same software on their PCs? e.g. Asian markets will use text-entry apps, US markets will not.

  • 'the difference between software applications installed (demand) and software applications legally shipped (supply) equals the estimate of software applications pirated.'

  • 'Uplift factors' are applied to generalize software shipment data from the participating companies, first to the entire US industry, then to the world. 'These uplift factors include estimates for open-source software. For this study, IPR has assumed that open source software is free and not pirated.' eh, thanks ;)

    I'm not quite sure what this means, but I think it means that they make an estimate of how much of the software shipment data represents OS software, and then add that to the 'legally shipped' side.

  • 'IPR believes that certain software shipments in the data collected from participating companies are reported for one country, but the software is exported and used in another country. In order to account for this and to eliminate this effect from the piracy study as much as possible, net import estimates were developed on a country-by-country basis.'

    This covers Simon's point -- but it's not 100% clear, since those biases aren't listed. I wonder if it takes into account Ireland's paradoxical situation; while Ireland is (or was, at least) the world's top exporter of software, it's still cheaper for Irish users to import software applications from overseas ;)

Dublin: the new bridge just down the road from my house has finally been completed -- in time for Bloomsday it seems, since it's named after Joyce. Obligingly, the Dublin traffic camera operators have got a great night shot of it:

ireland piracy filesharing law internet filtering politics eu

Wind Farms

NYTimes via jwz: dude, you can't build a wind farm where it would mess up the view from the Kennedy Compound!

Cape Wind Associates hopes to build America's first offshore wind farm: 130 windmills, spaced a third to a half of a mile apart, across a shoal seven miles off the coast of Hyannis. Embedded in the ocean floor, each turbine would tower higher than the top of the Statue of Liberty's torch, its three 161-foot blades churning at 16 RPM. The wind forest promises to provide Cape Codders, on average, with 75% of their electricity, 1.8% of the total electrical needs of New England. (...)

Soon, the Alliance to Protect Nantucket Sound was filing lawsuits, mounting political pressure in Boston and Washington and, to bolster its legal case and maximize public anxiety, generating volumes of doomsaying critiques: (...) The yacht-club set opened its checkbooks, donating money and stock to cover the 100,000-a-month bills for rent, three full-time salaries, television and radio time, two lobbyists and three law firms. (...)

I think I may be one of a small number here, but I'm a huge fan of how wind farms look. It's a similar thing to seeing pictures of the space shuttle; gigantic technological structures are cool! Maybe that's just me though. ;)

climate-change power ireland

European Software Patent amendments contd.

Arlene McCarthy is the MEP proposing to amend the operations of the European patent office, and permit software patents in Europe.

Last week, the Guardian printed this story by Nick Hill and rms setting out the free software position on why software patents should be avoided.

Now, McCarthy's response:

We have an obligation to legislate not just for one section of the software industry who seeks to impose its business model on the rest of industry, which moreover is not 'free', but is actually a different form of monopoly by imposing a copyright licence system on users.

No comment...

patents swpats software open-source ireland

Software piracy figures - pass the salt

Hmm. The Irish branch of the BSA claims that the percentage of illegal software used in Ireland stood at 42 percent for 2002.

Does that mean 42 percent of all software running in Ireland is a pirate copy? I wonder if anyone ever audits this figures -- qui custodiet etc. The article continues:

'The lack of improvement on Ireland's piracy rate can be attributed to the proliferation of Internet piracy ... and a certain amount of apathy,' said Julian McMenamin, BSA Ireland chairman. 'But whatever the excuse, a piracy rate of 42 percent is appalling.'

Is internet piracy really that widespread in the workplace? I can imagine your typical 15-year-old firing up KaZaa or whatever, but is this really likely for your typical Irish IT staffer? I doubt it, to be honest.

And given Ireland's broadband woes, it'd probably be cheaper to hop in the car, drive to the local Compustore, and buy it over the counter, just to avoid paying those ISDN charges. ;)

Just to contradict the 'internet piracy' statement, in this story, McMenamin then states that 'a particular problem in Ireland was small and medium-sized companies purchasing a licence that is too small, or not upgrading their licence as their companies grow. An offending company might typically have a 10-user licence but allow 50 people to use the software.'

This is a hell of a lot more likely than the 'scary internet' bugbear, but I would still find it very hard to imagine that this is a uniquely Irish problem that could account for Ireland supposedly having nearly twice the rate of piracy of the UK (42% in Ireland vs. the UK's 26%).

While taking a look at the BSA site, I note that their automated tool, GASP, now exposes the illegal distribution and storage of copyrighted music, apparently: 'new features in GASP v6.5 include reports that show a complete listing of MP3 files on audited systems'.

I wonder if my collection of MP3s downloaded from eMusic.com, and ripped from albums I bought, would set off its alarms. Given that the MP3 format has no way to differentiate between pirated and non-pirated music, I would imagine so. False positives a go-go!

Patents: Eamon O'Tuathail's call for action against software patents. The vote of the Legal Affairs Committee of the EP was yesterday, apparently. Wonder how it went...

ireland filesharing filtering law internet politics piracy

Boca Raton's rep gets a battering again

The Miami Herald: Bogus Boca: the spa for spam:

Poor Boca. It's as if infamy has taken up permanent residence. Such a startling number of Boca Raton firms have been linked to fraudulent schemes.

The article then lists the past scams operated by Boca Raton firms; a mind-boggling list. It then notes the press Boca's been getting in the UK:

"Golden beaches, palm tree-lined streets, manicured golf courses and giant motor yachts moored at the marinas: Boca Raton in Florida is a millionaire's paradise. It's also the spam capital of the world.''

(Guardian story here).

spam anti-spam ireland

Cthulhu Quiz Fun!

I amAzathoth!

Known as the Blind Idiot God, the center of all cycles known as Azathoth is the great void itself, infinite creation and inescapable oblivion made one. The Great God is without ego, as it has been embodied in a seperate consciousness as Azathoth has cast off the curse of self-awareness. Surrounded by the host of flautist servitors, piping the songs of the unknowable, Azathoth is not to be known by his aspirants. That is the purpose of another God...

Which Great Old One are you?

funny fun scifi

ReVirt, Patents, and Spandex

ReVirt is very, very cool security functionality:

ReVirt (part of the CoVirt project) is a complete Linux-on-Linux virtual machine with replay capability: you can explore the state of the entire virtual machine at any point in the past. For example, if you discover an intruder, you can 'go back in time' to see how they broke in, watch the exploit in progress, and discover what was compromised. The overhead of virtualization and logging is only 15-30%, even for kernel-intensive applications.

Can't wait until this is stable...

Games: The Body Behind Vice City's Tommy Vercetti (Escape Mag): an interview with the guy who did the motion-capture for Vice City:

What advice do you have for any readers interest in doing motion capture?

... Stuff your Spandex mo-cap suit. That's the key.

Patents: SFGate: Inventors patent ideas to pre-empt their rivals: '(IP lawyer) Dennis Fernandez has come up with an idea for TV sets with built-in cameras and small screens that would let viewers talk to one another while watching a show. ... Fernandez has no intention of actually building such a device. But the idea is his -- and he has a certificate from the U.S. Patent and Trademark Office to prove it.'

And there was me thinking these things had to be non-obvious, and have novelty, to be patentable. :( What is the US PTO up to? And what's going to happen if the European Patent Office get their way?

I'm beginning to think a pro-bono collection of freely-licensable defensive patents, filed by the FSF or similar, is the only way to work around this brokenness.

patents law security coding databases storage swpats copyright

[IP] do read last Para. Time to correct the record re. the pillaged Museum in B (fwd)

Lost from the Baghdad museum: truth (Guardian). hmmm! It seems we've been had:

(In April, it was widely reported that) 100,000-plus priceless items were looted (from the Baghdad museum) either under the very noses of the Yanks, or by the Yanks themselves. And the only problem with it is that it's nonsense. It isn't true. It's made up. It's bollocks.

Incredible -- it seems (a) the museum was looted -- to a degree; the vast majority of 'missing' items had actually been moved into safe storage, and 'most of the serious looting was an inside job'.

And (b) the academics and journalists who reported '170,000 items ... stolen or destroyed' had been led by the nose by Dr Donny George, the museum's director of research. It just wasn't true:

Over the past six weeks it has gradually become clear that most of the objects which had been on display in the museum galleries were removed before the war. Some of the most valuable went into bank vaults, where they were discovered last week. Eight thousand more have been found in 179 boxes hidden 'in a secret vault'. And several of the larger and most remarked items seem to have been spirited away long before the Americans arrived in Baghdad.

George is now quoted as saying that that items lost could represent 'a small percentage' of the collection and blamed shoddy reporting for the exaggeration. 'There was a mistake,' he said. 'Someone asked us what is the number of pieces in the whole collection. We said over 170,000, and they took that as the number lost. Reporters came in and saw empty shelves and reached the conclusion that all was gone. But before the war we evacuated all of the small pieces and emptied the showcases except for fragile or heavy material that was difficult to move.'

This indictment of world journalism has caused some surprise to those who listened to George and others speak at the British Museum meeting. One art historian, Dr Tom Flynn, now speaks of his 'great bewilderment'. 'Donny George himself had ample opportunity to clarify to the best of (his) knowledge the extent of the looting and the likely number of missing objects,' says Flynn. 'Is it not a little strange that quite so many journalists went away with the wrong impression, while Mr George made little or not attempt to clarify the context of the figure of 170,000 which he repeated with such regularity and gusto before, during, and after that meeting.' To Flynn it is also odd that George didn't seem to know that pieces had been taken into hiding or evacuated. 'There is a queasy subtext here if you bother to seek it out,' he suggests.

journalism history art

Poland, and Irish Internet round-up

So, Poland just joined the EU - welcome! ;)

Meanwhile, time for a trawl through IrelandOffline news.

Boards.IE have had enough of crappy internet from the telcos -- they're hoping to launch an ISP. Given one company's continuing stranglehold over the Irish internet, they'll need every bit of luck they can get. Good luck guys.

And, in case anyone's swallowing that 'there isn't the demand' line, check this story out:

The story goes how Old Man Kennedy was getting his shoes shined back in '29 and the shoe-shine boy was telling him what stocks looked good and what didn't. Old Man Kennedy knew the game was up and it was time to get out of the market.

I got my hair cut this morning and the middle-aged man beside me was telling the barber how he had downgraded his ISDN line to get DSL but the DSL failed the test and now he's stuck with a normal line. The barber was asking him what company he applied through, told him of the others, asked how far from the exchange he was, told him where the exchange was (as he didn't know), said 'mmm, that'd be about 3km, as the crow flies. But it's not as the crow flies - it's the turns in the road and that.'

Now if my barber can give me the technical requirements for DSL and people are talking of stimulating demand, you have to realise that something fishy is going on.

Forfas delivers damning broadband report : 'Irish DSL prices for small businesses are about five to six times higher' than other European countries. Hmm, I wonder why the telcos are reporting a lack of demand.

IrelandOffline's Broadband - The Next Steps for Ireland document, which was presented to the Dail's Joint Committee on Communications last week. Conclusions:

  • Prioritise Wireless: 'it is no longer time for trials'

  • Increase Availability of Affordable Backhaul

  • Raise Public Awareness of Alternative Technologies

And how's about this for an Alternative Technology? Tethered balloons trialing in the North. Genius. The company is called Skylinc, and uses blimps flying at 1500m; each provides a coverage area of 80km diameter. The result is 'fibre rate service at DSL prices'; non-contended for 30,000 customers, with 1-10 MB/s throughput. I really hope they can pull this off....

ireland internet politics filtering data-protection privacy uk

Quantum Cryptography - up and running in Boston (fwd)

Wow. Things move pretty fast in the world of quantum crypto it seems; according to this IP mail, BBN have had a VPN protected using quantum cryptography up and running since December 2002.

Date: Mon, 09 Jun 2003 18:18:26 -0400
From: Dave Farber ...
To: ip ...
Subject: Quantum Cryptography - up and running in Boston

From: Chip Elliott ...
Date: Mon, 09 Jun 2003 16:51:09 -0400
To: ... ...
Cc: craig Partridge ... Chip Elliott ...
Subject: Quantum Cryptography - up and running in Boston

Dave, Bob,

Craig Partridge has forwarded me your message on the BBC's article on quantum cryptography. Indeed, quantum cryptography is much closer than most IP folks might think!

We've had an Internet protected by quantum cryptography up and running in our lab since Dec 2002. It's a full Virtual Private Network (VPN) protected by our own quantum cryptography apparatus running through dark fiber. This is a DARPA project, in collaboration with the BU Photonics Center and Harvard University Applied Physics Dept, and next steps will be a build-out in metro Boston to link our campuses.

We'll be announcing our work at SIGCOMM 2003 later this summer.

Cheers,

-- Chip

Chip Elliott Principal Engineer, BBN


You are subscribed as ... To manage your subscription, go to

http://v2.listbox.com/member/?listname=ip

Archives at: http://www.interesting-people.org/archives/interesting-people/

security internet networking law patents swpats

'A land where all the children smell of petrol'

The Observer's 'state of the union' report from Baghdad. Summary: total anarchy:

A hundred and fifty dollars or so for an AK-47, double that for a pistol because it's easier to hide. You can buy them rather easily from the street-markets. These are patrolled hourly by US forces whose job is to check for people selling guns. The traders get round this with diabolical cunning by looking at their watches and, once an hour, hiding all the guns. The liberating forces offered a cross-Baghdad amnesty a couple of weeks ago: the grand total of guns deposited was a magnificent none. ... If a silhouetted someone tries to wave you down, with a gun, in a long hot road full of heat-mirage and six-year-olds siphoning petrol, you have to choose: chances are it's a Bad Person so you keep the foot down, but if it's the Americans and you race past, they'll shoot at you, lots, because they're as scared as everyone else in this shambles of a city.

Then a classic story:

One night I visited a friend about a mile away, and foolishly stayed up talking, and ended up trying to get a late taxi home. Outside the hotel they shrugged, and then one brave young thing disappeared for a minute and came back carrying lots of guns and walked me through the blackout for 10 minutes until we came across a darkened little street party of severely scary drivers, the fat moon winking its light off a battery of gold teeth and metal teacups and, for all I'm really sure, recently bloodied scimitars. Not for 10,000 dollars, I was told. 'Ali Baba, Ali Baba,' they repeated. Some Iraqis get annoyed by this - the thief of the 1,001 Nights was Kuwaiti - but the verbal shorthand is fast and always works: the thieves are out, and have guns, and even though we have guns too we're not going to risk it. Are you mad? Where are you from?

I mention Scotland, and we have one of those extremely odd late-night conversations, this time about Mel Gibson. Apparently one of the very favourite films in Baghdad is Braveheart, because Saddam used to show it repeatedly, nightly, with furious subtitles, to demonstrate just what bastards the English were. I explain that few Scots have a television because most are still running around in woad, thanks to the English. We raise a happy toast - sticky, sweet tea - to the general fog of historical propagandising and the more specific idea of 'Freedom!'. Somewhere nearby - a mile away? A street away? - another stupid pop-pop gun battle breaks out, and they really won't take me home, and so I say I might walk, and they raise their teacups again and say you must be either very brave or very stupid, when the truth of course is that I am neither, but something else again relatively new to them, which is very quietly drunk. I bravely wake up my friend and sleep on the sofa.

politics journalism history

The secret city of London

The Times: The secret city is a great reservoir of urban myth. Great article about the urban legend fodder that is 'the city beneath the city'.

Date: Mon, 09 Jun 2003 15:19:37 +0100
From: "Martin Adamson" ...
To: ...
Subject: The secret city is a great reservoir of urban myth

The Times

June 09, 2003

The secret city is a great reservoir of urban myth

Richard Morrison

YOU know what worries me most about London? It's how the buildings stand up. It seems miraculous that they aren't wobbling like a contralto's bosom. So many tunnels, bunkers, sewers, stations and vaults have been dug beneath the capital that the famous clay on which London is built must now resemble a Swiss cheese. Last week the Post Office closed its Mail Rail, the underground train that sped our epistles from Whitechapel to Paddington, or vice versa, for 75 years. Most Londoners were vaguely aware of its existence. But what else is down there? The answer is that nobody knows the whole truth, and most of us don't know a hundredth of it. But that's fine with me, because in the absence of hard facts this secret city-beneath-the-city is a wonderful reservoir of urban myth. And that's much more entertaining.

Some things I do know. The Bank of England also has its own underground railway, presumably to cart sackfuls of dosh to fat cats in the Square Mile. So does Harrods, presumably to cart the sackfuls back to the Bank. Also lurking below ground are no fewer than 40 ghost stations: disused Tube stops, their eerily empty platforms briefly glimpsed from passing trains.

Or are they deserted? Some had -- perhaps still have -- very active afterlives, if rumour can be believed. The Down Street station, between Green Park and Hyde Park Corner, was used as an underground Cabinet Room during the war.

The never-officially-opened Bull and Bush, its entrance half-concealed on Hampstead Heath, is said to be the nerve centre controlling the floodgates that would be swiftly closed if the Thames ever broke into the Tube. But at one time it was also claimed to be the mysterious "Paddock", the Government's subterranean control room in the early 1940s. Two things fuelled this enduring urban myth: the reference in Churchill's memoirs to a bunker "near Hampstead" (which would be a strange description of the well-known bunker at Dollis Hill, near Neasden); and the odd story of a man, walking on the Heath during the war, who was startled to see the unmistakable figure of the great Winnie emerging from what seemed to be a bush.

What's certainly true is that some Tube stations were equipped at that time with deep-level "parallel" platforms, designed as bomb shelters on the understanding that London Transport would be allowed to convert them into express Tube lines later. Mysteriously, this plan was abandoned. Or was it? Again, urban myth declares that there is indeed a parallel, express Northern Line, but that commuters will never be allowed on it. It is reserved for when VIPs have to be whisked out of London quickly and stealthily. (The urban myth doesn't reveal what they would do when they reached Morden.)

As for these deep-level parallel stations themselves, their fates are equally intriguing. Eisenhower's secret wartime headquarters, a vast, 32-storey inverted skyscraper under Goodge Street Tube Station, is now used as secure storage -- allegedly for confiscated pornography, among other things. The fate of the wartime shelter under Chancery Lane Tube Station is even more intriguing. During the Cold War it was apparently converted into a very unusual telephone exchange -- one with a six-week supply of food, its own well, and 12 miles of tunnels extending across London. That would have withstood an atom bomb attack, but not an H-bomb, so it was scrapped. The saloon-bar experts tell me that something even vaster, deeper and spookier lies under Ludgate Hill. But the Chancery Lane "cavern" still remains off-limits.

So does the bulk of underground Westminster and Whitehall. Buildings such as the Ministry of Defence are said to resemble icebergs: seven-eighths below the surface, and all connected by a warren of tunnels stretching to Buck Palace, Charing Cross and God knows where else. Or so a man told me at a party.

Not all of underground London is secret. You can wade into the cathedral-like caverns of Joseph Bazalgette's sewers if you want. And some resolute aesthetes do, admiring what is said to be the world's best Victorian brickwork.

Unsurprisingly, however, there is no comprehensive map of subterranean London. Not in the public domain anyway. The engineers building the Jubilee Line Extension reputedly had to submit their proposed route under Parliament Square time and time again, never being told the reasons for its rejection, until by a process of elimination they found the one passage that (presumably) didn't send trains crashing into Blair's war room or MI5's interrogation cells.

But what's to become of the tunnel we do know about -- the now mothballed Mail Rail? Call me biased, but I think it should be converted into a dedicated cycle track, providing us Lycra loonies with a safe, fast, dry route across London. Either that, or it will have to become the world's longest, deepest bowling alley.

ireland maps london history dublin

SpamAssassin in Playboy

Jeremy Kister on the SpamAssassin-talk mailing list notes:

In an article written by Randy Cassingham, Randy describes 'why e-mail abuse should be a crime' and suggests ways to stop spam. His fifth suggestion states Ensure that your ISP is taking steps to combat the problem, such as installing SpamAssassin...

This is in Playboy July 2003 pg 53 (bottom). (and no, i usually dont read it for the articles ;) )

Plus a pretty good article in Forbes, too. A good news week for SpamAssassin...

anti-spam spam spamassassin

Security Issues

funny quote on the 'nmap in the Matrix: Reloaded' thing at the Reg:

But then, the film does take place in the future. Is (security analyst Michal Zalewski) surprised to see unpatched SSH servers running in the year AD 2199? 'It's not that uncommon for people to run the old distribution,' he says. 'I know we had a bunch of boxes that were unpatched for two years.'

security aws networking ec2

The Today Programme

The Today Programme on BBC Radio 4 has been my main news source for several months (at least since I moved to somewhere with decent broadband, and didn't have to contemplate getting up at unearthly hours to listen to it ;) .

In the past week or two, they've broken a major story, the 'sexing-up' allegations against the UK government's Iraq's Weapons of Mass Destruction dossier (yes, that's 'sexing-up'.)

There's transcripts of the interviews here and on the Times website (thanks to P O'Neill for the pointer to the latter). Well worth a read, if you enjoy hearing evasive politicians getting skewered by a skillful interviewer. ;)

politics uk media ireland society

Nice Guys Win

That's the message from Robert Sapolsky, professor of biological sciences at Stanford and neurology at Stanford's School of Medicine, from his studies of baboon behaviour in the Serengeti:

For the humans who would like to know what it takes to be an alpha man--if I were 25 and asked that question I would certainly say competitive prowess is important--balls, translated into the more abstractly demanding social realm of humans. What's clear to me now at 45 is, screw the alpha male stuff. Go for an alternative strategy. Go for the social affiliation, build relationships with females, don't waste your time trying to figure out how to be the most adept socially cagy male-male competitor. Amazingly enough that's not what pays off in that system. Go for the affiliative stuff and bypass the male crap. I could not have said that when I was 25.

A handful of (the baboons) simply walked away from it over the years. Nathaniel was one, and Joshua was another. They had the lowest stress hormone levels you've ever seen in male baboons, and outlived their cohorts. The fact that this alternative strategy is actually the more adaptive one is one of the good bits of news to come out of primatology in quite some time. If that's the future of primates, this planet is going to be in great shape in a couple of million years.

A great article, and pretty funny in places -- especially where he discusses the results of baboons' lack of a developed frontal cortex:

Even though there are tremendous individual differences among the baboons, they're still at this neurological disadvantage, compared to the apes, and thus they typically blow it at just the right time. They could be scheming these incredible coalitions, but at the last moment, one decides to slash his partner in the ass instead of the guy they're going after, just because he can get away with it for three seconds. The whole world is three seconds long--they're very pointillist in their emotions.

More at the Edge Magazine site.

science animals research

Bumper Stickers

My try-out SpamAssassin bumper stickers from BumperActive just arrived, along with a hand-written note stating that they taken the liberty of trimming them down for me -- nice touch ;)

The resolution isn't great, but then the source image wasn't either ;) Print quality, however, is a beaut. Recommended. Now to get sticking!

art history home

SCO's Hand-Waving Drags On

Ho hum... SCO staggers on. Snore. Quick links:

    • Analysts to SCO
    : 'don't drag us into this'. Also, a good quote from Linus: 'Quite frankly, I found it mostly interesting in a Jerry Springer kind of way. White trash battling it out in public, throwing chairs at each other.'
  • Some unintended side-effects in Germany: LinuxTag launches 'anti-competitive' suit, SCO shuts down their German website in response. (Mind you, I doubt it'd make any difference. I don't think they actually have any customers at this stage, so the only people who'd notice would be reading about it in the news sites anyway ;)
  • Slashdot roundup -- mostly worth reading for the top 2 comments ;)

  • arie.org's take on the issue.

  • spam funny anti-spam http web

    Dublin -- Apparently

    JA forwards a link to Veronica Guerin, the new movie by Joel Schumacher, based on the life of the eponymous Irish journo. It boasts this beaut on their official ad website:

    In the mid-1990s, Dublin was nothing short of a war zone, with a few powerful drug lords battling for control. ... Based on a true story, this powerful, emotional film from producer Jerry Bruckheimer (jm: oh no) ... and producer Joel Schumacher ... gives unique insight into a fascinating and complex aspect of the Irish conflict ...

    My emphasis. Oh dear oh dear oh dear. Somehow or other I must have missed all the warzone stuff... I wonder if they're confusing it with Bogota?

    ireland dublin movies drugs

    Salam Pax, P. K. Dick fan

    Slate with a fantastic article about Salam Pax:

    His latest post mentioned an afternoon he spent at the Hamra Hotel pool, reading a borrowed copy of The New Yorker. I laughed out loud. He then mentioned an escapade in which he helped deliver 24 pizzas to American soldiers. I howled. Salam Pax, the most famous and most mysterious blogger in the world, was my interpreter. The New Yorker he had been reading--mine. Poolside at the Hamra--with me. The 24 pizzas--we had taken them to a unit of 82nd Airborne soldiers I was writing about. ...

    I needed a new interpreter to fill the gap for two weeks or so, and the colleague mentioned that he had just met a smart and friendly guy named Salam. I quickly traced Salam to the Sheraton Hotel. Salam--this is his real first name--was sitting in a chair in the lobby, reading Philip K. Dick's The Man in the High Castle. I knew, at that moment, that I would hire him.

    ... we'll all be hearing more from Salam: He has signed up to write a fortnightly column for the Guardian, and he continues to blog. He also continues to be surprised by the reaction to his work. When he was told by the Austrian interviewer that his fans had begun making 'Salam Pax' T-shirts and coffee mugs, his response was frank--'Are you kidding?' Nobody is kidding. The coffee mugs are for real, and Salam Pax is for real.

    Thanks to Ben for another top tip. Ben, start a blog!

    journalism blogging iraq-war salam-pax

    'There is no reliable information'

    Karlin forwards a good round-up from Conor O'Clery, the Irish Times' Washington correspondent, on the WMD evidence issues:

    At one point during rehearsals at CIA headquarters in Washington for that speech, Mr Powell threw several pages into the air and declared: 'I'm not reading this. This is bullshit,' according to today's US News and World Report.

    The most overblown conclusions about Iraq's weapons of mass destruction came from a 'mini-CIA' set up in the Pentagon by the Defence Secretary, Mr Donald Rumsfeld, according to an army intelligence officer who told Time magazine: 'Rumsfeld was deeply, almost pathologically, distorting the intelligence.' ....

    A classified assessment of Iraq's chemical weapons by the Defence Intelligence Agency in September 2002, obtained by US News, stated: 'There is no reliable information on whether Iraq is producing and stockpiling chemical weapons ...'

    politics nsa google privacy law

    Shooting From The Crowd

    I meant to blog about this event back in April at the time, but never got around to it. Basically, towards the end of April, there was a demonstration in Falujah in Iraq, shots were (reportedly) fired from the crowd, and US troops opened fire, killing 2 and injuring 14.

    Well, Charlie Stross has saved me the bother ;) -- he's written a good summary of the historical precedent for this chain of events, and what resulted back then.

    politics security camping

    Challenge-Response: Patent Fireworks!

    A timely reminder for the European Commission, while it considers permitting software patents.

    In the US, software patents have been permitted for years, with hilarious results. Here's a good example.

    Back in 1997-98, spam was a minor irritant, but the practice of 'listbombing' (forge-subscribing one's enemies to lots of mailing lists) was more troublesome. As a result, several mailing-list manager programs like Majordomo added challenge-response to their subscription process; this is why, when you sign up for a list, you have to click on a link in the mail you get, to 'confirm' you really asked to be signed up. (Here's a mail detailing how LISTSERV had this feature in March 1996.)

    All very clever, and it solved the problem nicely.

    Some bright sparks then noticed this, and decided it was non-obvious somehow to apply this to spam filtering. They overlooked the prior art (more listed here) and registered some patents.

    Fast-forward to 2003, and we see that there are now no less than three pretty-much-identical anti-spam C-R patents which have been granted:

    Oops! Where's the popcorn?

    (Thanks to this posting from RFG for spotting this.)

    anti-spam spam funny

    Google News Censors Indymedia

    Google News has been forced to remove IndyMedia from Google News' feed of sources, by an email campaign.

    I'm in two minds about this -- I can see Google News' point. If an unmoderated feed allows crap like the Protocols of the Elders of Zion to get through, then GN obviously doesn't want that turning up in their 'news' search results. But removing IMC altogether seems suboptimal; I would assume the front page newswire -- or at least the features -- is a bit more moderated, and therefore trustworthy.

    Getting balanced news -- and that means lefty IMC along with neocon Fox -- is key, and Google News was doing a pretty good job up 'til that point.

    news web internet media

    Interview with nmap author

    a good interview with nmap's Fyodor on /. Snippet:

    1. During your time running Honeypots, you'll have seen a lot of compromised systems. Is there any incident that's really stuck in your mind because of the audacity of the attempt, or the stupidity of the person attempting the breakin?

    2. On the humorous front, one attacker was was running a public webcam during his exploits, so we were able to watch him crack into our boxes in real time :). I will resist the urge to link a screenshot. His rough location was determined when we noticed Mrs. Doubtfire playing on his TV and correlated that with public schedule listings. He was working with a Pakistani group, but was actually on the US East Coast.

      In the 'disturbing audacity' front, this year we found that a group of crackers had broken into an ecommerce site and actually programmed an automated billing-sytem-to-IRC gateway. They could obtain or validate credit card numbers by simply querying the channel bot! Expect a more detailed writeup soon.

    security credit-cards spam http privacy

    Depleted Uranium

    temporary politics break. ;) This story was big news in the UK a few weeks ago, but never made it into the news over here. Dr. Asaf Durakovic, a former US Army advisor, sent a team to Afghanistan to test civilians for uranium contamination after the war there:

    Without exception, every person donating urine specimens tested positive for uranium internal contamination. ... the donors presented concentrations of toxic and radioactive uranium isotopes between 100 and 400 times greater than in the Gulf veterans tested in 1999. (jm: also on average 26 times the maximum permissible level in the US)

    'If (the) findings are corroborated in other communities across Afghanistan, the country faces a severe public health disaster... Every subsequent generation is at risk.'

    Also, a very interesting interview with Major Doug Rokke, who worked on the cleanup procedures during the first Gulf War, dealing with DU and other contaminants.

    ireland funny uk

    Slashdot, and Electric Vehicles

    current /. poll: what SpamAssassin setting do you use? Cool! (but who are the nutters voting 'less than 0'?)

    Tech: Danny blogs about fuel-cell vehicles, linking to the DrivingTheFuture site. I met Doug Korthof of DTF a month or two ago -- a nice guy with a persuasive case, namely that electric vehicles work, and the current concentration on fuel-cell and hybrid vehicles is a diversionary tactic.

    The facts of the matter really are quite wierd, as the OC Weekly interview notes:

    • When (Doug) first got the (GM) EV1, the lease allowed for unlimited mileage. But the car came with something else: a defective lead-acid Delco battery that took a couple of trips to the mechanic to get replaced. GM wound up replacing all the Delcos with Panasonic lead-acid batteries. But there was an unanticipated consequence: the Panasonics got such dramatically better range than the Delcos that GM took all its EV1s that had not been leased off the market and forced existing drivers into new leases that did limit mileage.

    • Korthof experienced even better mileage with a nickel-metal hydride battery that allowed his 1997 Honda EV-Plus to run for 140 miles without a recharge. Honda took the car back in 2002 and junked it. No subsequent electric cars had nickel batteries, and Chevron Texaco Corp. since acquired the worldwide patent to nickel-metal hydride batteries, which the company is partly using to satisfy the burgeoning hybrid-car market.

    I took a look at the EV1 myself, and talked to Doug about the recharging system he uses. He recharges their 2 EVs directly from a plug socket in his garage, and with his house fitted with solar panels, it costs about 25 bucks a month to keep them charged. Of course, there's a lot of up-front cost to install the solar panels and buy the EVs, but IMO it would be worth it.

    A moot point anyway -- most EVs (with the exception of the Toyota RAV4-EV) can no longer be bought, even second hand. Instead, there's a recall in operation, and existing EVs are being recalled and dismantled. Even purely from a 'cool tech' POV, this is a shame.

    hardware ireland exploits

    e-voting in Ireland 'poses a threat to our democracy'

    Margaret McGaley has been investigating the Nedap/Powervote e-voting system that's recently come into use in Ireland, as part of her undergrad thesis, and the conclusion is not good: 'E-voting poses a threat to our democracy'. She goes on:

    I hope to mount a campaign over the next few months with the following goals:
    • to prevent the use of the Nedap/Powervote system in Irish elections,
    • to prevent the purchase of any more equipment or software from
      • Nedap/Powervote by the Irish government, and
    • to convince the government that any electronic voting system used in this country should be developed here, using formal methods and the Mercuri method, and should be open source.

    More info at the the report site.

    The Nedap/Powervote e-voting system is the one that the Irish government never bothered getting a copy of the source for, instead doing a basic under-NDA source audit. Reportedly, there were comments in the resulting review doc along the lines of 'The source code and comments for this section is in Dutch, so we're not sure exactly what it does'. And if that's not bad enough, it runs on WinCE, with the votes tabulated in an Access database. ;)

    Let's hope Nedap/Powervote use their election-fixing powers purely for good, and not for evil! ;)

    BTW, myself, I'm surprised the Irish government (a) went to a Dutch company for the technology to do this, and (b) didn't get hold of the entire system's components and source, or at least do a stronger audit, given their experience of imported computing devices including some 'bonus functionality' in the past.

    ireland voting e-voting

    Eurovision Scandal

    No, not the supposedly politically-motivated nul points for the UK, the much more scandalous way that RTE ignored democracy and the popular vote in favour of their own autocratic 'Star Chamber' jury. Outrage! Boo!

    'Voters had a five-minute slot in which to register their selections after all of the songs had been performed. Because Ireland was third of the entries to disclose its voting, the phone lines could not be kept open for any longer than the five-minute slot. Eircom, which operated the phone lines, had agreed with RTE' that it would collate all of the votes within nine to 10 minutes of lines closing. While the company fulfilled its obligation, RTE' decided to use a jury verdict rather than phone votes. ...

    (My emphasis.) Hmm... methinks the journo doth protest too much.

    Eircom said its decision not to charge voters for their calls was a goodwill gesture and should not be interpreted as an admission of failure on its part regarding its role in the voting. 'The system and the technology on our part worked as it should have on the night,' a spokeswoman said.'

    Aaaaah. I get the picture.

    ireland politics law

    GTA3: Vice City secrets

    Hmm. I don't remember spotting a tiki bar in GTA3:VC... must go searching when that VGA adapter turns up. ;)

    I've been repeatedly struck, while in California, what an incredible job the GTA3:VC designers did with the graphics and level design. It evokes so many visual aspects of US cities, perfectly, and this is pretty impressive when you consider they're a Scottish games house. This interview details how they did it:

    GS: Did you do any on-location studies of any areas to help with the design of Vice City? If so, where did you go, and how helpful was it?

    AG: After the near-death experience that was the development of Grand Theft Auto III, the entire team flew out to Miami to recover and soak in the atmosphere of the area. While the rest of the team sunbathed or propped up the News Bar, the ever-industrious art team headed out onto the baking hot Miami streets armed with digital cameras. We split up and covered every area we were interested in using for Vice City. The animation team armed with digital camcorders spent time examining exactly how women in bikinis and roller skates moved, and the city modelers braved both the seediest, scariest parts of Miami and got kicked out of all the best places. By the time we returned to sunny Scotland, we'd amassed countless hours of video and close to 10,000 digital photos. When scouting locations, we tried to get a cross-section of shots -- a good few were wide angle to remind us how the place fit together, and the rest were details to aid in modeling and texture usage. The guys in the New York office also sorted out some professional location scouts from the film industry for us who provided us with some really excellent locations for any areas we hadn't managed to get enough detail on. I can't imagine capturing the feel of a city without all this resource material, never mind actually spending time in the place. Sending the entire team rather than a few leads allows everyone to understand what it is they are trying to make. We couldn't have done it any other way.

    gaming games video

    PAL vs. NTSC: a maze of twisty turny passages

    A cautionary tale of consumer electronics regional lockdown follows. Hopefully Google'll pick it up and it'll help someone else in the same boat.

    So I brought my PS2 with me from Ireland, along with a few good games, figuring that it'd be cheaper, and simpler, to bring them and buy a few bits of converter hardware here, rather than buy the lot from scratch.

    How wrong I was. :(

    So I've already spent about 50 bucks on a step-up transformer to convert US 110v to the 220v my European PS2 requires. Of course, the European PS2 outputs in PAL rather than NTSC, and most US TVs, including my one, accepts only NTSC input.

    So the next step is a PAL to NTSC converter. Sounds like a pretty simple piece of equipment, right? Well, nope. Most pages out there that deal with this recommend either (A) buying a multi-region DVD player that'll convert PAL to NTSC on the fly -- which won't work for me, as I'm not looking to play DVDs per se -- (B) buying a converter like this one for about 280 dollars, (C) buying a new TV (even more expensive), or (D) buying a VCR that'll convert on the fly, like the Samsung SV-5000W, for about 350 dollars. (forget it, that's more than the price of the PS2!)

    However, there does seem to be another option: a PAL-to-XGA converter, allowing me to display the PS2 output on my PC's monitor. Still pricey at 152 dollars though.

    One more: I could just buy a new PS2 over here for 180 dollars and install a multi-region mod chip. But my soldering skills are rusty, and license-wise, it's iffy. :(

    Finally, though, the winning option seems to be this: Lik-Sang.com sell a PS2-to-VGA output converter box for about 50 dollars plus shipping. Given that the display quality is improved -- and my monitor is sharper and bigger than my TV anyway -- I think I'll go for this.

    tv hardware games

    LPR as a general spooling and queueing mechanism

    Good article on the use of LPR/LPD as a general-purpose distributed queueing mechanism for non-printing applications.

    I maintained PLP (the predecessor of LPRng , which the author uses) for a while, and this kind of thing was one of the main featuresets I wanted to enable.

    I know someone in (if I recall correctly) BASF was using it to generate movies, from frame-grabs individually LPR'd by a network of machines. As a result we had to add sub-second accuracy to the queueing; not sure if that made it into LPRng though ;)

    queueing languages data

    What Shall We Do With The Drunken Sailors

    The story of the U.S.S. Constitution and her drunkard sailors. A great story, so I forwarded it on, and what do you know, Ben debunks it thoroughly:

    What a load of bollocks.

    As to the alcohol detail, working it out on fingers and toes, it comes to over 3 gallons of liquor per person per day. 12 pints of rum would be a big day for me and I probably wouldn't want to get up and do it all over again the next day. And by day 100 ...

    But the big honking red flag here is that the US was at war with FRANCE, not Britain, at the time. Ponder for a moment the concept of a US ship (when the US Navy was brand new and very small) sinking this many British ships and, ahem, sailing up the Firth of Clyde to -- this gets good -- raid a distillery. I think some response from the Royal Navy would have been considered ...

    And the ship was launched on the 22nd, not the 27th.

    Of course, this wouldn't stop, oh, the SECRETARY OF THE NAVY from repeating it as fact!

    Ben, you should start your own blog.

    ireland funny history security

    Caelen and Barbara's Adventures

    Caelen and Barbara's travelogue from Luang Prabang just fills me with reminiscence for Laos -- I'd go back in a shot, it's an amazing country (well, for tourists at least, not sure about the folks living there).

    Also interesting to see that Caelen went for some minor surgery while in Bangkok. Great idea -- 150 bucks is a hell of a lot cheaper than you'd get it pretty much anywhere else, and the Bangkok hospitals that cater for tourists are, by all accounts, super-swanky. Great idea!

    thailand life hacks

    Small World

    wow, this is wierd.

    So I did a quick blog-hop, as you do. First, I visited Bernie's interim weblogs.com blog (thanks for the link B! BTW, this looks cool).

    From there, I hopped to Micheal O'Foghlu's site, and finally settled the question -- yes, he is related to Cormac O'Foghlu, who I used to work with ;)

    On to Sean McGrath's blog, where I came across an interesting link to DemoTelco -- a nifty site where anyone can set up a blog and write entries via SMS messages. Set up by a Dublin company, Newbay.

    Cool. To check it out, I took a look at one of the blogs on the 'most popular' sidebar, and what do you know -- it's Caelen King's foneblog!

    Lots of (er, frankly bizarre) pics of Caelen and Barbara. Given the shots of Euro coins and crappy Dublin weather, I guess they're back from their round-the-world trip, then...

    Sure enough, it notes:

    We are back in Ireland and back at work - Our Really Big Adventure is over

    Know that feeling. :( Still, at least they went to the bother of finishing up their travelogue. I think I'll take a read over that in full when I get a chance...

    ireland irishblogs web blogging

    The 'One Bite Of The Apple' Problem

    Ray Everett-Church of CAUCE writes regarding the latest US Senate anti-spam bill.

    This bill simply creates a set of baseline standards for truthfulness, which if the spammer can meet, they can send as much spam as they wish. This characteristic, common to all the leading spam bills, makes it a gross misnomer to call them 'anti-spam.' 'Anti-consumer,' sure. 'Pro-spam,' even. But not 'anti-spam.'

    Any legislation that permits all of America's estimated 23 million small businesses to legally send everyone at least one email cannot be considered anti-spam. And any bill that limits a consumer's recourse to clicking an opt-out link 23 million times isn't going to make our lives any better. By limiting enforcement to Attorneys General or the FTC, with no recourse for consumers, these bills virtually guarantee the status quo: extremely limited enforcement. Even the FTC and state AGs have said giving them more enforcement power without commensurate resources is a waste of time.

    A good example of why opt-out does not work as a basis for anti-spam action; it permits every single potential sender to still spam you once, in full legality -- what's been called the 'one bite of the apple' problem.

    Given that (as Ray says) there's 23 million small businesses in the US, that's a potential 23 million spams to your email address, and 23 million 'remove' requests you'd have to send to unsubscribe -- every three years, to boot. Full open letter from CAUCE here.

    anti-spam spam filtering

    Cat Murderer

    My cat has turned into a murderer. For the last week, he's been going out and bagging 1-2 wild animals per day; mostly rabbits, but some voles and a finch too.

    It's really wrecking my head. I don't have the nuts to kill a half-dead rabbit in cold blood, so I wind up leaving them in the bushes to die; and I'm sure that's exactly what happens to most of 'em. The other day I had to fish out a dead baby rabbit, put it in a plastic bag, and dump it in the bin.

    Maybe I should leave them out for the hawks. There's a pretty big peregrine and red-tailed hawk population around here.

    Alternatively, maybe some cat transformation sets would help... at least around the house: 'The cat which became a hood figure is likely to have a broom at any moment, and is likely to begin cleaning.'

    Bonus: via jwz:

    pets wildlife cats

    'Shooting The Messenger'

    Yoz does a great job rounding up some Plan For Spam links. First off, he links to a great essay, Shooting The Messenger, which nicely rebuts the idea that to deal with spam, we need an SMTPng. Recommended. (He goes a bit overboard with some hard-ass filtering recommendations at the end IMO, though...)

    Secondly, Yoz links to a couple more posts. The first is a friendly-fire incident involving the SpamCop DNS blacklists, illustrating the dangers of peer-to-peer 'this is spam' reporting. There's a related issue with the SpamCop DNSBL, in that it's over-sensitive; one report can sometimes be enough to get a site BLed, which is not good. The problems with SpamCop's hair-trigger thresholds are well-documented, and -- hopefully -- Julian will fix them soon.

    The second is a mail from John Gilmore to Politech. He says 'a simple rule for anti-spam measures that preserves non-spammers' freedom to communicate is: No anti-spam measure should ever block a non-spam message. But there isn't a single anti-spam organization that actually follows this rule.'

    Wrong. That's exactly the SpamAssassin angle. If the user says it's not spam, it's not spam -- and we have to figure out a way to get our scoring system to return that result, if at all possible. And yes, it gets it wrong about 0.1% of the time -- and that's why we never tell users to block, bounce or delete spam if at all possible; just mark it 'possible spam' and divert to another folder, and always let a human take a look to verify that decision.

    Given the nature of the spam problem, and the nuisance it poses to virtually everybody trying to use email, that's the best that can be done at this point.

    And yes, something has to be done. Spam is a massive problem. If it's not dealt with somehow, and kept out of our day-to-day inboxes, people will stop using mail. Before spam filters became ubiquitous, I talked to many casual internet users who (a) closed down their email address every 6 months to escape the flood, or (b) gave up reading their mail because of it. (And why did spam filters become ubiquitous?)

    It comes down to: what's better for the internet -- a mislabelled email in your 'spam bucket' folder -- or no email at all?

    anti-spam smtp email spam

    valid reverse DNS now required to mail an AOL user

    Given that something like 8.13% of of the hosts that have sent non-spam mail to me do not have reverse DNS information recorded, the fact that AOL have just switched this on as a requirement will be interesting:

    : jm ftp 1019...; dig aol.com mx
    aol.com.                3559    IN      MX      15 mailin-01.mx.aol.com.
    mailin-01.mx.aol.com.   92      IN      A       152.163.224.26
    ...
    : jm ftp 1020...; telnet 152.163.224.26 25
    Trying 152.163.224.26...
    Connected to 152.163.224.26.
    Escape character is '^]'.
    220-rly-za01.mx.aol.com ESMTP mail_relay_in-za1.6; Thu, 22 May 2003
    15:09:54 -0400
    220-America Online (AOL) and its affiliated companies do not
    220-     authorize the use of its proprietary computers and computer
    220-     networks to accept, transmit, or distribute unsolicited bulk
    220-     e-mail sent from the internet.  Effective immediately:  AOL 
    220-     may no longer accept connections from IP addresses which 
    220      have no reverse-DNS (PTR record) assigned.
    ^]
    telnet> q
    Connection closed.
    

    anti-spam spam filtering

    Breakthrough in photonics

    New Scientist: Alchemy with light shocks physicists:

    Claims of 'unexpected and stunning new physical phenomena' are rare in the abstract of a reputable scientific paper. But the latest report by photonics crystal pioneer John Joannopoulos and his group at MIT, soon to be published in Physical Review Letters, does not disappoint.

    The researchers document the ultimate control over light: a way to shift the frequency of light beams to any desired colour, with near 100 per cent efficiency. 'The degree of control over light really is quite shocking,' comments photonics expert Eli Yablonovitch at the University of California, Los Angeles.

    If the effect can be harnessed, it will revolutionise a range of fields - turning heat into light, for example, or prized terahertz rays. Right now, the only way to shift the frequency of a light beam involves sending an extremely intense light pulse - with a power of many megawatts or even gigawatts - along next to it.

    This interacts with the first beam and alters its frequency, but the technique is expensive, requires high-power equipment, and is generally pretty inefficient. But when Joannopoulos and his colleagues Evan Reed and Marin Soljacic investigated what happens when shock waves pass through a device called a photonic crystal, they discovered a completely unexpected effect.

    I'm just posting this because I like the word 'photonics' ;) But this is apparently really cool new tech.

    science research papers

    Escher Meets The Flower Show, Little Elves, and W3C on Patents

    BBC: How does Dyson make water go uphill? A very cool hack from a Dyson engineer for the Chelsea Flower Show -- an M. C. Escher-influenced water feature which gives the illusion that the water is flowing uphill.

    A set of four glass ramps positioned in a square clearly show water travelling up each of them before it pours off the top, only to start again at the bottom of the next ramp.

    It is a sight which defies logic, and has become probably the most memorable image of this year's show.

    Mr Dyson says his inspiration was a drawing by the Dutch artist MC Escher (he of Gothic palaces where soldiers are eternally walking upstairs, and of patterns where birds turn into fish).

    Privacy: Danny forwards this post which discusses what the poster calls the 'little elves' problem. Very good point and contains this great real-world example:

    Peter Wright in 'Spycatcher' ... describes one of the problems arising out of the Berlin Tunnel Operation thus: 'So much raw intelligence was flowing out from the East that it was literally swamping the resources available to transcribe (and translate) and analyse it. MI6 had a special transcription center set up in Earl's Court, but they were still transcribing material seven years later when they discovered that George Blake had betrayed the Tunnel to the Russians from the outset'.

    Funnily enough, I have the same problem -- a lack of processing power to deal with the raw incoming volume -- with my spamtraps from time to time. Now I can describe it in terms of 'little elves'.

    Patents: W3C announce patent policy. They've decided on Royalty-Free as a requirement, good news. TimBL's comments on the decision:

    Many participants in the original development of the Web knew that they might have sought patents on the work they contributed to W3C, and that they might have tried to secure exclusive access to these innovations or charge licensing fees for their use. However, those who contributed to building the Web in its first decade made the business decision that they, and the entire world, would benefit most by contributing to standards that could be implemented ubiquitously, without royalty payments.

    This decision on the W3C Patent Policy coincides almost exactly with the tenth anniversary of CERN's decision to provide unencumbered access to the basic Web protocols and software developed there, even before the creation of W3C. In fact, the success of technical work at the World Wide Web Consortium depended significantly on that decision by CERN. The decision to base the Web on royalty-free standards from the beginning has been vital to its success until now. The open platform of royalty-free standards enabled software companies to profit by selling new products with powerful features, enabled e-commerce companies to profit from services that on this foundation, and brought social benefits in the non-commercial realm beyond simple economic valuation. By adopting this Patent Policy with its commitment to royalty-free standards for the future, we are laying the foundation for another decade of technical innovation, economic growth, and social advancement.

    Quite. I remember seeing Mosaic for the first time -- my first thought was 'wow, it's like those commercial hypertext systems, but it's free'. Initially, the free-ness was a lot more important than the network transparency it also offered.

    There had already been several commercial hypertext systems, with expensive licensing terms. I'd only ever seen them bundled with other products (like the AIX documentation viewer) or used in kiosk systems.

    They pretty much foundered when HTTP and HTML became available. But there's no question to my mind that if CERN had made HTTP/HTML a commercial, licensed, or royalty-paying proposition, we wouldn't even be talking about the web (or should I say the 'WWW'?) nowadays.

    art history graphics

    The national 'Do Not Call' list

    (of the phone variety). I've been driven mad by telemarketers; one of the more irritating local innovations (thankfully 'sales cold calls' are pretty hard to operate with European privacy laws, so it wasn't a problem back home).

    Well, Congress over here recently passed a 'do not call' list, so you could ring up the maintainers and ask for your number to be added, and hey presto, no more phone spam. Well, CalPundit writes:

    The federal law doesn't cover banks, airlines or phone companies or calls made within a state.

    Wow. That's like saying 'the law doesn't cover calls made on a day ending in 'y'.' In my experience, those companies make 95% of the calls. Great.

    Think I'll stick with the tried-and-trusted 'ring through to answerphone during the afternoon and early evening' filter...

    DMCA: IP: Using treaties to lock in DMCA enforcement:

    On May 6, President Bush and Prime Minister Goh of Singapore signed the U.S.-Singapore Free Trade Agreement (the 'FTA'). President Bush has termed the FTA 'the first of its kind' - apparently meaning that it is the first free trade agreement between the United States and an Asian nation.

    But the FTA is also the first of its kind in another sense, as well. It is the first international trade agreement to demand that the signatories implement anti-circumvention provisions similar to those of the hotly controversial Digital Millennium Copyright Act ('DMCA').

    It's Naomi Klein meets Slashdot ;) Hopefully it'll be blocked though, since it has serious domestic results too:

    This step will have international, as well as domestic consequences: If Congress approves the FTA, it will not able to alter the DMCA without violating its obligations to Singapore.

    Of course, according to some correspondents, Ireland's copyright regime (reformed in 2000) quietly inserted its own DMCA provisions. Of course, nobody noticed, except for the legal lobbyists who were hoping this would happen. Doh. Is nowhere safe for freedom-to-tinker these days?

    data-protection spam security mobile privacy coding linux eu

    The 419ers Meet Their Match

    Scam-O-Rama: Absolutely incredible. These guys have taken the art of 419er-baiting to the ultimate extreme -- they're successfully extracting money from the 'Lads from Lagos':

    Wow. Also this IDG.NET story notes:

    There's an odd battle building in the dark alleys and byways of the Internet, being fought by diverse characters such as Dr. Sigmund Freud, Kris Kringle, the late Princess Margaret, a German-Hungarian gypsy called Hans Gneesunt-Boompsadazi, a Chinese restaurateur called Hu Flung Dung, and the Patagonian Liberation Front. ....

    In what is regarded as the Titanic of the genre ... three bogus explorers called Captain Stabbin, Lonslo Tossov and Ilichy Miracsky, in their equally fictitious boat 'The Lucky Lad', kept a gang of Lads on the run for several months with clowning exploits describing their supposed passage up and down the West African coast, failing to meet the Lads on several occasions for a variety of improbable reasons.

    Eventually the good captain pulled the plug on the reverse scam, informing the lads in no uncertain terms that they were 'mugus' -- a word used in Nigeria to denote an utter idiot.

    I came across this while looking for info on the practice of signing guestbooks as Mugu Guyman. One theory I've heard is that means a 419er has visited the guestbook, scraped the email addresses for 419 fraud, and it's a sign for other 419ers to keep away from those addresses as they're already 'taken'. As the quote says above, 'Mugu' is apparently a term meaning something along the lines of 'gullible idiot'. Most of the comments seem to support this:

    • 'me i done here mugu mugu off'
    • 'TOGO GUYMEN KEEP OFF FROM THIS SITE I DEY HERE LAGOS ?TOGO GHANA GUYMEN MUGU NO DEY HERE'
    • 'Avary good site pls all guyman keep off,oooooooooooooooooo.'

    Then, a few seem to indicate that it's a sign to other 419ers not to spam those addresses while a scam is in progress:

    • 'south africa, jo bong, mugu guyman kindly keep offoooooooooooooo someone have visitedooooooooooooooo and still waiting for reply ok'
    • 'VERY HICE ALL MUGU GUYMAN KEEP OFF IT HAS BEEN DONE PLEASE DON,T SPOIL JOB FOR I DONO DO ALL0000000000000000000000000000000000000'

    Dunno what all the oooooooooing is about though... ;)

    spam 419 scams fraud security

    Guinness Really IS Good For You

    New Scientist: The Last Word: 'Q: I have heard that it is possible to live on Guinness and milk alone. Is this true, or even partially true?'

    'A: This is not quite true. Guinness does contain many vitamins and minerals in small quantities, but is lacking vitamin C, as well as calcium and fat. So, to fulfil all of your daily nutritional requirements you would need to drink a glass of orange juice, two glasses of milk, and 47 pints of Guinness. -- Nigel Goodwin , University of Nottingham'

    No problem!

    food health funny ireland

    The 'Private Jessica Lynch' Spectacle

    Karlin posts a good story on the whole 'rescue of Private Jessica Lynch' story. Great quote:

    Further, British military Group Captain Al Lockwood, the British Army spokesman at central command in Iraq, says that the British could not believe the pandering way in which the US military dealt with the US media, culminating in the Lynch episode, and the gushing, unquestioning acceptance of same by the US media. 'In reality we had two different styles of news media management,' said Lockwood. 'I feel fortunate to have been part of the UK one.'

    Guardian story here:

    The American strategy was to concentrate on the visuals and to get a broad message out. Details - where helpful - followed behind. The key was to ensure the right television footage. The embedded reporters could do some of that. On other missions, the military used their own cameras, editing the film themselves and presenting it to broadcasters as ready-to-go packages. The Pentagon had been influenced by Hollywood producers of reality TV and action movies.

    One interesting result is that, while the US media (or TV at least) is happy to spew this pabulum, for some reason, these days, most other media outlets world-wide are a bit more likely to apply a critical eye, suspecting spin.

    No matter whether it's true or not, excessive media management (or filming of action movies ;) over flimsy stories is quickly exposed. This promulgates the impression world-wide that the wool is being pulled over the viewers' eyes, and that the source of the news is fundamentally telling fibs.

    history web nsa privacy internet

    SCO's strong-arm tactics

    In case you missed it -- SCO's letter to Linux customers. Executive summary:

    • open-source code development methodology bashing, to start with
    • SCO will 'suspend their own Linux-related activities', whatever they were
    • all users of Linux are vaguely threatened in a 'cartooney' fashion
    • 'Similar to analogous efforts underway in the music industry, we are prepared to take all actions necessary to stop the ongoing violation of our intellectual property or other rights.'

    Classy! And a bonus good point from a comment on this LJ article: 'According to this article, SCO Linux 4.0 contains version 2.4.19 of the Linux kernel. ... By the act of distributing the Linux 2.4.19 kernel, SCO has irrevocably released any and all of their intellectual property present in the 2.4.19 kernel under the (terms of the) GPL.'

    open-source linux ip

    Chris Horn back on top in Iona

    my ex-employers, IONA Technologies Announces Chris Horn as CEO -- again:

    In a series of further moves, Mr. Barry Morris, CEO since May 2000, Mr. Steven Fisch, COO, who joined the company in August 2002, and Mr. David James, Executive Vice President Corporate Development, who joined in 1997, have resigned.

    'The Board of IONA Technologies is responding firmly to the challenges and opportunities of the changed marketplace, to position the company for profitable growth and to take advantage of market opportunities through business and new product development. I want to thank Barry, Steven and David for their enormous contributions to IONA and I wish them well in their next challenges,' said Dr. Chris Horn.

    Good to hear it!

    amazon aws ireland

    Microsoft using cloak-and-dagger tactics to fend off Linux

    Ah, some good old-fashioned sleazy MS stuff:

    Chris O'Rourke, a Microsoft employee, described attending LinuxWorld, a trade fair in California, where he 'purported to be an independent computer consultant' working with several public school districts, according to an e-mail message he sent on Aug. 20, 2002. 'In general, people bought this without question,' Mr. O'Rourke wrote. 'Hook, line and sinker.'

    He said his goal was to glean intelligence about the competition. His guise, Mr. O'Rourke said, 'got folks to open up and talk.' Mr. O'Rourke did not respond to a fax and voice mail message seeking comment.

    Hilarious -- if you can't beat 'em, send in the clowns. Via the NYT.

    spam microsoft funny google

    Telecoms sans Frontieres

    Salam Pax blogs about an interesting NGO:

    I have heard today that a NGO called Communication sans frontiers has arrived in Iraq and will help. They will probably be doing what the Red Cross is doing, a center in Baghdad and a team moving around Iraq. The Red Cross has been moving its phone service, if you can call it that, around Baghdad. Two days for each district and they depend on the word of mouth to spread the news, usually they end up with huge lines and waiting lists but everybody is grateful. Many people have no way telling their relatives abroad how they are doing. A couple of Arabic TV stations, mainly Jazeera, has been putting their cameras in the street and allowing people to send regards to their relatives abroad, tell them they are OK hoping that they would be watching at the time. So what the Red Cross has been doing, and I think what Communication sans frontiers would ultimately be doing is much appreciated.

    According to this comment on the command-post.org blog, it's actually called Telecoms Sans Frontieres:

    Telecoms sans Frontieres has created a new humanitarian aid concept: the humanitarian telephone system. TSF's mission is to operate anywhere in the world, in the heart of military conflicts or in the wake of natural disasters, in order to enable the local population to simply say: I'm alive.

    Now there's a cool idea for any BOFHs who fancy doing some interesting volunteer work for a year... ;)

    aws privacy law data ireland

    Ali G in the NYT

    A classic Ali G moment, via Maureen Dowd in the New York Times (username: sitescooper/sitescooper):

    • YOUNG MAN: How does you make countries do stuff you want?
    • MR. BAKER: Well, the way you deal with countries on foreign policy issues . . . is you deal with carrots and sticks.
    • YOUNG MAN: But what country is gonna want carrots, even if it's like a million tons of carrots that you're giving over there----
    • MR. BAKER: Well, carrots -- I'm not using the term literally. You might send foreign aid -- money, money.
    • YOUNG MAN: Well, money's better than carrots. Even if a country love carrots and that is, like, their favorite national food, if they get given them----
    • MR. BAKER: Well, don't get hung up on carrots. That's just a figure of speech.
    • YOUNG MAN: So would you ever send carrots? You know, is there any situation----
    • MR. BAKER: No, no.
    • YOUNG MAN: What about if there was a famine?
    • MR. BAKER: Carrots, themselves? No.

    Beautiful.

    Initially, there were a lot of media reports in the UK and Ireland, about how negatively it was taken in the US; this interview with the director reckons that was rubbish put about by UK media:

    'I've got a theory about this: In Britain, we're no longer world leaders in anything. ... Yet the one thing we still maintain, and cling on to jealously, is that we've got the best sense of humour in the world. So we don't like the idea that people in other countries get our sense of humour. We prefer to cling to the idea that our comedy is too sophisticated for the Americans And yet the truth is rather different. If you look at sitcoms, with a couple of exceptions, all the best ones come from America, like Friends, Frasier, Seinfeld and so on.'

    'I actually think Americans get the undertones of satire almost better than the British. It can't be coincidence that the best comedies on our TV are all imported from America.'

    But then even the bad reviews never said that Ali G was too sophisticated, complaining instead that the satire wasn't subtle enough. Maybe the Americans are the more comedy-literate, after all.

    funny tv uk usa

    More on C-R

    TidBITS weighs in. They cover the issues very well, and also have noticed the problem that arises when a C-R system decides to challenge e-commerce notifications -- like your air travel e-tickets, for example.

    Found at Gary Robinson's blog, where he also links a couple of taint.org items, cheers Gary ;)

    Also, from /.: the House of Lords debates the etymology of 'spam'. Quite funny:

    Lady Saltoun of Abernethy: My Lords, do the Government have any plans to restrict unsolicited faxes? My fax paper is always being wasted by people who send me faxes I do not want. I do not know whether they could be called 'corned beef' or something, but I have had enough of them.

    Plus another anti-spam Senate bill, from Rep. W.J. 'Billy' Tauzin (R-La.) and F. James Sensenbrenner Jr. (R-Wis.). This one is apparently riddled with loopholes: 'this is yet another bill . . . attempting to get rid of the porn and the scams, but really clearing the way for legitimate companies to spam," said John Mozena, co-founder of ... CAUCE.'

    anti-spam spam email web privacy backscatter smtp data-protection

    The Perils of Challenge-Response hits PoliTechBot

    As I've said before, C-R is not an acceptable way, alone, to deal with spam. You're just pushing the work away from yourself, and onto your legitimate correspondents -- and you won't make any friends as a result. Things get worse when anything more complex than simple person-to-person mail intrudes, like internet mailing lists. (And come on folks -- that particular innovation is only 24 years old ;)

    Case in point this week: Declan McCullagh gets bitten:

    My reluctant conclusion is that C-R systems with flawed implementations have the potential to end legitimate mailing lists as we know them today.

    and Dave Farber says:

    If I start getting a flood of challenges from earthlink ipers that require my response I will most likely declare them SPAM and you will stop receiving IP mail.

    John Levine's follow-up is well worth a read, as he predicts massive (and trivial) whitelist exploitation by spammers to avoid C-R -- and then we'll be worse off than we were when we started.

    Finally, there's quite a funny quote in John's mail:

    A relatively easy to solve problem with challenge systems is that most of them are written by dimwits who don't understand the way that e-mail really works. In 1983 the 4.3BSD Berkeley Unix 'vacation' program correctly dealt with mail from lists and other mechanical sources, yet 20 years later I still see out-of-office replies from Lotus Notes and MS Exchange to list mail every day. (Is there really nobody at IBM or Microsoft who used 4.3BSD or knows the rules of thumb to recognize non-personal but legit mail?)

    I have often wondered that myself ;)

    anti-spam spamassassin backscatter challenge-response smtp email spam bounces

    Northern Ireland policing: imploding

    Wow, the policing situation in Northern Ireland is undergoing meltdown (again).

    First off, 'Stakeknife' has been named. He was a very high-up member of the IRA ('head of security for the IRA's northern command' apparently), and a double agent for the British Army's FRU division. The Sunday Herald coverage is here. This is seemingly due to some revelations by a double-agent turned whistleblower.

    He's not a nice character by all accounts:

    'It would be tantamount to being exposed as running a Latin American-style murder squad if the truth came out,' one said. Unlike Nelson, Stakeknife sometimes did the killings himself. He is also supposed to have arranged for republican targets to be in the wrong place at the wrong time so loyalist hit teams could 'take them out'. An intelligence source added: 'This guy was licensed to kill and he killed very many people -- or arranged their deaths.'

    So, last week, Castlereagh barracks -- where files on the agent were kept, and 'supposedly the most secure security force barracks in western Europe' -- was broken into by a team from British Army intelligence. From that article, it seems pretty brazen; they used army passes, went directly to the room where the papers were moved, knew that security teams were not operational, took exactly the right files, and left:

    One former FRU source said: 'There was no way it was paramilitaries -- they couldn't pull it off. The branch couldn't do it as they'd get spotted by their own pals in the RUC and MI5 just don't do rough stuff like this. There's no one except an intelligence corps CME team who could do this and there is no other motive for them doing it than protecting Stakeknife.'

    More NI stuff: Martin McGuinness transcripts: Cryptome again. Surprisingly interesting, mostly for the relaxed chats with Mo Mowlam!

    • Mo: 'Ahem, the second thing I was gonna say was that I was gonna go to AMERICA and if I've got it I'm still gonna go for a couple of days, this week. So I won't be around much and then I'm on two weeks holiday.'
    • MM: 'Right'.
    • Mo: 'So, it was really if there was anything, ahem?'
    • MM: 'Your holiday plans and mine are colliding then.'
    • Mo: 'I'm going 26th for two weeks'.
    • MM: 'So am I, 26th for two weeks.'
    • Mo: 'Your not going to TURKEY I hope?'
    • MM: 'No I'm going to Kerry.'
    • (Both laugh)

    ireland politics abuse

    EMusic again

    So I've signed up for EMusic. Just my luck -- with perfect timing, they've instituted a new download policy, whereby one has to use a proprietary download application -- and it doesn't work on Red Hat versions after 7.3; to quote their install instructions:

    The Linux version of the Download Manager 2.0 was developed for Red Hat 6.2, 7.3 and Mandrake 8.1. Any flavors of Linux outside of these may not support the EMusic Download Manager 2.0. If you are having issues, we recommend that you switch your Linux flavor or OS in order to download with the EMusic Download Manager 2.0.

    There's two workarounds: use the Red Hat 7.3 shared libraries for system libc and libnss, as described by John Anderson of genehack.org here; or apparently, a local proxy can be used as long as you use the IP address of the proxy in the emusicdlm app -- not the hostname.

    I'm conflicted now; I was about to go recommending this service to all and sundry, but

    • it really makes the Linux version a hell of a lot harder to run. (I hope they fix that, at least). Previously, it was simply 'right click to download', which is insanely easy and simple.

    • more worryingly -- in my experience, this kind of 'tightening up' is often symptomatic of a company running out of cash and spiralling 'round the plughole, IMO. :(

    On the good side, once I downloaded and set up the genehack hack^Wworkaround, it's now working perfectly.

    I've just downloaded an album from their service in about 3 minutes (at 400Kb/s), first try, and the tracks are all crystal-clear VBR MP3s. Now that's nice...

    (PS: -1 for whichever glibc genius decided to change the libnss API incompatibly.)

    music linux emusic

    Horrific - when botfly larvae attack

    Horror as maggots bore into game farmer's eye (Saturday Star, South Africa):

    'I was in the veld hunting with a group of foreign tourists when I felt something flick into my eye. I thought it was just a miggie but that evening my whole face started to swell,' he said.

    Spangenberg went to his doctor and was given eye drops but the swelling got worse. 'I started getting terrible migraines and at times I could see nothing but dark and light shadows out of my eye.'

    His doctor sent him to eye specialist Bruce Staples in Bethlehem who suspected that the Bot fly was responsible but initially couldn't spot the larvae - so he treated the inflammation.

    When Spangenberg came in again, Staples spotted the worms in the retina and managed to hunt them down with the laser. Staples said by that stage they had begun to pupate and started to run and hide when he went after them with the laser.

    This story notes that, in Africa at least, they generally attempt to infect sheep eyes rather than those of humans; but snopes has pictures (warning: extremely gross) from an earlier infestation in Honduras.

    Botfly larvae are horrible, horrible little creatures. Urgh. This combines two of my pet neuroses -- maggots and things happening to eyes -- I think I'm going to get sick...

    health animals wildlife

    for posterity: the FormMail advisory

    Myself and Ronald F. Guilmette co-wrote an advisory on vulnerabilities in FormMail. Here it is, archived from RFG's bugtraq posting:

    Anonymous Mail Forwarding Vulnerabilities in FormMail 1.9

    By manipulating inputs to the FormMail CGI script, remote users may abuse the functionality provided by FormMail to cause the local mail server on the same (web) server system to send arbi- trary e-mail messages to arbitrary e-mail destination addresses. Such e-mail messages may contain real or forged sender e-mail addresses (in the From: headers) entirely of the attacker's choosing. In some cases, the envelope sender addresses of such messages may also be set to arbitrary values by the attacker.

    I helped with a few cases where FormMail is vulnerable here, namely the injection of newlines attack.

    When this came out, I was in Australia, packing in preparation for a month-long camping trip around Victoria ;) The Lake Catani campsite at Mount Buffalo was amazing. (whoa, compare that page with this e-commerce monstrosity -- urgh)

    email anti-spam smtp security gmail spam

    UFO Roundup on Saddam's Alien Technology

    Saddam Hussein, or Mighty Morphin' Power Ranger? You decide:

    ... (UFO Roundup Middle East correspondent) Mohammed Daud al-Hayyat has a theory that the golden necklaces worn by Saddam and his son Qusay are protective devices given to them by the reputed Zarzi aliens. ...

    'People say that when they wear these necklaces, Saddam and Qusay have only to clasp hands, and the circle of light will appear,' Mohammed explained, 'The alien vortex will instantly transport them to safety. In this manner, they can create the circle without the Zarzi aliens being present.' ...

    'The latest rumor is that Saddam will shortly address the people of Iraq from an alien base on the moon! They say this will happen in four or five days.'

    Classic! Snipped from UFO Roundup, via the Forteana list; full extract here. (Link)

    Date: Fri, 09 May 2003 11:39:10 -0000
    From: "uncle_slacky" ...
    To: ...
    Subject: Re: FWD (UASR) 1958: A case of time travel in Montana

    --- In ... "Terry W. Colvin" ... wrote:

    UFO ROUNDUP Volume 8, Number 18 May 7, 2003

    You missed the best segment - the one about Saddam and the UFO:

    The Saddam video "is the talk of everyone in Baghdad," reported Ayesha al-Khatabi, a UFO Roundup Middle East correspondent. "But what is most puzzling is the mysterious golden necklace Saddam was wearing when the Azamiyah video was made. Qusay was wearing one, as well. Since Saddam is not known for wearing jewelry with his uniforms, my sources in Iraq cannot understand why he chose to wear it that day."

    Fellow correspondent Mohammed Daud al-Hayyat has a theory that the golden necklaces worn by Saddam and his son Qusay are protective devices given to them by the reputed Zarzi aliens.

    (Editor's Note: According to an urban legend, a UFO crashed in Iraq either during 1991 or 1998. Saddam granted the surviving aliens sanctuary, allowing them to live in either an underground base at Zarzi or at the centuries-old citadel at Qalaat-e-Julundi in the As- Zab as-Saghir (Little Zab) river valley in northern Iraq.)

    "People say that when they wear these necklaces, Saddam and Qusay have only to clasp hands, and the circle of light will appear," Mohammed explained, "The alien vortex will instantly transport them to safety. In this manner, they can create the circle without the Zarzi aliens being present."

    Two days after Saddam's appearance, "on April 11 (2003)," al- Azamiyah "was the site of a firefight between Iraqis holed up in a mosque and U.S. Marines hunting for leaders of Saddam's regime."

    Ayesha noted that "al-Azamiyah is primarily a neighborhood of Sunni Muslims, so Saddam Hussein knew he would be among friends when he appeared there."

    Also on Wednesday, April 9, 2003, according to ufologist Jose Escamilla, a cylindrical UFO was seen dodging American anti-aircraft bursts while flying over Baghdad.

    "I found a rod (cylindrical UFO) that zipped through anti-aircraft explosions over the city," Escamilla reported, "And this rod flew effortlessly and was not hit nor affected by the explosions in the air. Clear shot and it was moving very fast."

    Ayesha speculated that this "may have been the UFO that brought Saddam Hussein to al-Azamiyah earlier. The Escamilla video may actually show Saddam and Qusay leaving the city after their surprise appearance."

    On Wednesday, April 30, 2003, the ousted dictator created another stir when "a London-based Arabic newspaper published a handwritten letter purportedly signed by Saddam Hussein that called on Iraqis to rise up against American forces."

    Saddam "urged Iraqis to rebel against the 'infidel, criminal, murderous and cowardly occupier,' promised that people who collaborated with American-led forces would be punished and predicted that 'the day of liberation and victory will come."'

    "Faxed to the offices of Al-Quds al-Arabi, the letter was dated April 28, the date of Saddam's 66th birthday."

    "The newspaper's editor, Abdel Bari Atwan...said he had seen Saddam's signature before and believed the one on the letter was 'definitely' his."

    However, "U.S. officials were skeptical about the authenticity" of Saddam's letter and "are unsure whether Saddam survived two bombings that targeted buildings where he was believed to be, one at the outset of the war and one at the closing days."

    President George W. Bush, "speaking Sunday (April 20, 2003) at Fort Hood in Texas, said that if Saddam was alive, 'I would suggest he not pop his head up."'

    "In the last week, Iraqis say they have seen Saddam emerging from an underground tunnel in his hometown of Tikrit, riding in a taxi in the southern city of Basra and living in a former Sheraton Hotel in Baghdad."

    "'There have been more sightings of Saddam Hussein than of Elvis,' Rick Wiles, editor of American Freedom News, said."

    "Opinion is equally divided. Some people say Saddam is at Zarzi with the aliens," Mohammed Daud al-Hayyat added, "Others say he is at the underground base at al- Ouja, two kilometers (1.2 miles) north of Tikrit. The latest rumor is that Saddam will shortly address the people of Iraq from an alien base on the moon! They say this will happen in four or five days."

    history algorithms privacy nsa law security coding

    'Then they just drop off'

    The BBC reports on one animal-borne disease which I, for one, do not want to see making that zoonotic jump to humans:

    Gruesome VD hits Tanzania baboons

    Scientists are investigating a horrific new venereal disease which is affecting baboons in Tanzania. ... Male baboons are particularly badly hit by the new disease, says Elibariki Mtui from the African Wildlife Foundation in Arusha. 'The genitals kind of rot away, then they just drop off,' he said.

    health herd-immunity uk

    Salam's Back

    Good news -- Dear Raed is back on the air, in one piece!

    Let me tell you one thing first. War sucks big time. Don't let yourself ever be talked into having one waged in the name of your freedom. Somehow when the bombs start dropping or you hear the sound of machine guns at the end of your street you don't think about your 'imminent liberation' anymore.

    But I am sounding now like the Taxi drivers I have fights with whenever I get into one.

    Reactionary taxi drivers -- the same the world over ;) A fantastic read. So many details from the point of view of a 'normal' Iraqi on the streets. If you've been following the war and subsequent events, you can't miss it.

    politics blogs history

    IDF fires on British defense attache

    Israeli Defence Force fires on parents of injured British peace activist (Independent) (and the British defence attache to Tel Aviv): 'The parents of a British peace activist who was shot in the head by Israeli troops, came under fire themselves' ... (they) 'were in a British diplomatic convoy entering the town of Rafah in the Gaza Strip when Israeli soldiers at a checkpoint fired a shot'. 'The incident ... took place despite the Israeli Army being given notice of the journey on at least three occasions'. Incredible. More at the Guardian, too.

    grim-meathook-future meta politics

    SARS genome decoding 'couldn't have been done without mail'

    just got back from a super-quick booze-soaked weekend visit to Ben in SF. It was so good to visit a city once again, and get the opportunity to paint the town red, hit the bars, eat in plentiful cheap restaurants, and generally enjoy city life (which I've been missing massively since the move from Dublin). But now back in post-suburban Irvine to cope with the hangover.

    Also got to meet up with Komal, one of my co-workers up there -- which was cool. Unfortunately it was a super-speedy weekend whistle-stop tour though, so having a good social meet-up with all the guys will have to wait until the next visit. ;)

    Net: 'The Canadian scientists who broke the genetic code for SARS ... say they couldn't have done it without the Internet. ... The key to that collaboration was ordinary e-mail'.

    It also turns out the ProMED mailing list was the central point at which SARS reports were collated in the early stages, even despite evasion and cover-up by the Chinese state.

    So there you go -- as usual, SMTP is the killer app -- or in this case, a life-saving app! All the more reason to figure out ways to deal with spam and return SMTP to its top spot in the protocol pantheon.

    Good thing the FTC Spam Forum went so well, then. Sounds like there was unprecedented agreement between the non-spam folks, clear understanding of the issues by quite a few of the Washington denizens, and maybe even some good footage of the other side digging holes for themselves.

    Health: US, Asian Airlines Disagree on SARS. Me, I just wish the airlines would stop being so bloody cheap, and bring in more fresh air rather than recirculating. ;)

    Date: Sun, 04 May 2003 12:20:16 -0400
    From: STEPHEN JONES ...
    To: ... ...
    Subject: Internet is a good thing says Steve Jones clone

    Internet played a key role in decoding SARS genome, scientists say

    DENNIS BUECKERT

    OTTAWA (CP) - The Canadian scientists who broke the genetic code for SARS just weeks after the disease appeared say they couldn't have done it without the Internet.

    Scientists from the Michael Smith Genome Sciences Centre of the B.C. Cancer Agency say their achievement relied on rapid communication with scientists around the world. The key to that collaboration was ordinary e-mail, said Steven Jones of the Vancouver-based research agency in a teleconference Thursday sponsored by Science magazine.

    "Within a day of us having a press release announcing our participation in the sequencing we had an amazing amount of e-mail from scientists all around the world," Jones said.

    As soon as the sequence was decoded, the B.C. researchers posted it on the Internet.

    "People were, within minutes of that, able to download the sequence and analyse it in their own laboratories and their own computers," Jones said.

    "The Internet has had a profound impact on how this data has been shared and how scientists have collaborated."

    A short time later, researchers at the Atlanta Centers for Disease Control published the sequence of a coronavirus taken from another SARS patient.

    The genetic coding for the two viruses were virtually identical, boosting confidence that the coronavirus was in fact the causal agent.

    Now both sequences are posted on the World Wide Web for the benefit of researchers in many countries racing to find a reliable test for SARS, and a vaccine to prevent it.

    Scientists say the speed of the decoding was amazing.

    The first reports of the new disease came from China in November, and on March 13 cases were reported in Toronto and Vancouver. The sequences were posted on the net on April 15.

    By contrast, it took years to identify the agents behind diseases like AIDS and hepatitis C.

    Mel Crajdon of the B.C. Centre for Disease Control said all evidence points to the coronavirus as being the cause of SARS, despite some seemingly contradictory findings.

    Earlier this week Frank Plummer, who heads the National Microbiology Laboratory in Winnipeg, said he was puzzled by the number of people who show evidence of the SARS coronavirus but not symptoms of the disease.

    Crajdon suggested the apparent anomaly is due to imperfect understanding of how the disease presents itself, as well as lack of reliable tests for the presence of the virus.

    "I'm not surprised by the results that have been obtained to date and I think that they will rapidly improve," he said.

    More than 5,400 cases of SARS have been diagnosed worldwide, with at least 394 deaths. In Canada, there have been 23 deaths, all in the Toronto area.

    • - -

    On the Net:

    SARS sequences: http://sciencemag.org/features/data/sars

    SARS data: http://aaas.org

    SARS Comments: http://eurekalert.org

    ireland papers bugs

    Unicode, and how Java got it wrong

    Tim Bray is opening my eyes to lots of the itty bitty details of i18n with Unicode. I had very vague ideas about so many things he's writing here, so it's an educational read, especially this:

    In Java, characters are represented by the char data type, which is claimed to be a '16-bit Unicode character'. Unfortunately, as I pointed out recently, there really is no such thing. To be precise, a Java char represents a UTF-16 code point, which may represent a character or may, via the surrogate mechanism, represent only half a character. The consequence of this is that the following methods of the String class can produce results that are incorrect: charAt, getChars, indexOf, lastIndexOf, length, and substring. Of course, if you are really sure that you will never have to deal with an 'astral-plane' character, to the point of being willing to accept that your software will break messily if one shows up, you can pretend that these errors can't happen.

    To me, this feels just like deciding that you'll hever have to deal with more than 64K of memory, or a database bigger than 32 bits in size, or a date after December 31, 1999. What Hunter S. Thompson would call 'bad craziness.' I'll settle for 'shortsighted.'

    Wow, and there was I thinking Java had that sorted. If you ever plan to deal with 21st-century-style i18n (ie. using Unicode), you'd better read these articles.

    Spam: via BoingBoing, how to extract 500 bucks, painlessly, from telemarketers, under the TCPA. Not yet applicable to spam -- but who knows, maybe in a few month's time...

    Open Source: Colm MacCarthaigh caught Dell out a few months ago; turns out they were distributing a wireless AP, the Dell Truemobile 1184, which contained a modified Linux distro -- but were not distributing the source to the GPL'ed parts.

    Well, all credit to Dell. They've admitted their slip-up, resolved the problem admirably, and openly, and have shipped Colm a CD-ROM with all the GPL'ed source on it , which Colm has made available here . Mistakes happen, but it was nicely resolved.

    history security gmail

    EMusic.com vs. Apple

    a message on Dave Farber's IP list tipped EMusic.com as a little-known alternative to Apples new music store. So I took a look, and whaddya know, it's incredible! Here's the key points:

    • A fantastic selection of my favourite genres: roots reggae, dancehall, ambient and drum and bass. This is exactly the stuff you can't find on P2P nets nowadays, and it's not on Apple's store either. EMusic is not so hot for the top-40 stuff, but let's face it, I will never want to listen to Britney's latest anyway.

    • 'Try before you buy' 30-second track tasters, so you can listen to
      • the tune just enough to see if you like it before committing.
    • A flat monthly rate of 10 bucks, for 50 tracks a month.
    • Download as plain old un-DRM-encumbered MP3s. So it'll work fine on my Linux desktop, and pretty much any music-listening device you can possibly imagine for the next few years.

    Wow. I'm so signing up for this. I think in 10 minutes I've identified my next 6 months' listening material...

    music mp3 drm linux ireland ip software

    The 'Overseas Spammers' and 'Do Not Mail List' Fallacies

    Declan McCullagh: A modest proposal to end spam. Good article on Larry Lessig's 'spam bounties' proposal.

    Lofgren's plan won't give everyone who gets spammed new rights to sue (although spam victims may already may have some rights under state antispam or other laws). Instead, it states that people sending unsolicited commercial e-mail must label it with 'ADV:' in the subject line or run the risk of being sued by the Federal Trade Commission. If you are the first to report an unlabeled spam-o-gram to the government, you will get a bounty of 'not less than 20 percent' of the fine the spammer pays, assuming it can ever be collected.

    There are problems with this. As far as I know, the FTC is not having a problem collecting spam -- the figures I've seen (can't recall them right now) indicate that they get hundreds of megs a day. (Even the SpamAssassin.org spamtraps get over 100Mb a day.)

    The difficulty is chasing down the perpetrator, and prosecuting. That takes law-enforcement manpower, and that's just not there right now -- because, let's face it, spam is not a serious offence like rape or murder.

    Anyway, Declan says that the major problem is that the spammers are offshore:

    For one thing, an increasing percentage of it comes from overseas, and you can be certain that offshore bulk mailers will gleefully thumb their noses at Congress. Ken Schneider, chief technical officer of antispam company Brightmail, estimates that 30 percent to 50 percent of the spam his company tracks comes from outside the United States. 'It's a big number,' Schneider said. 'It's a global economy, and spammers are certainly taking advantage of it.'

    This is a frequent misapprehension. This is not the case. It's true that much spam is relayed through machines in Asia and South America, but the originators -- the people who are writing the spam and sending it to compromised relay machines and proxies -- are US-based. In fact, a vast quantity of 'em seem to be based in Florida. (This is the thing about country-code blacklists. In reality, if we could track a message all the way back to the origin, a state-code blacklist for FL would probably work much better ;)

    In other news from the same article:

    ... Sen. Chuck Schumer, D-N.Y., is expected to introduce a bill this week to create an national 'do not e-mail' list--an idea that the New Democrats touted earlier this month.

    OK, while I'm here, let's debunk 'do no mail' lists too. ;) 'Do not call' lists work well for telephones, since you typically have only one phone number. But for email:

    In summary, I'm not confident a 'do not mail' list could actually be operable.

    Finally -- The SBL's answer to the EMarketersAmerica.org SLAPP lawsuit.

    anti-spam spam spamassassin

    Unhappy Intelligence

    I've been trying to reduce all the anti-war stuff, since there's plenty of other sources for that and I reckon I'm boring everyone. But this story's a doozie -- US, UK intelligence agencies accuse Bush and Blair of distorting and fabricating evidence in rush to war:

    A high-level UK source said last night that intelligence agencies on both sides of the Atlantic were furious that briefings they gave political leaders were distorted in the rush to war with Iraq. 'They ignored intelligence assessments which said Iraq was not a threat,' the source said. Quoting an editorial in a Middle East newspaper which said, 'Washington has to prove its case. If it does not, the world will for ever believe that it paved the road to war with lies', he added: 'You can draw your own conclusions.' ...

    'The INC saw the demand, and provided what was needed,' he said. 'The implication is that they polluted the whole US intelligence effort.'

    nsa filtering politics terrorism privacy algorithms google news

    WWII's Campest Spy

    BBC: Wartime role of Queen's dressmaker. 'Details have emerged about the wartime activities of the Queen's dressmaker Sir Hardy Amies, who died last month aged 93.'

    Apparently, he served with the Special Operations Executive (SOE) in Brussels, liaising with the Belgian resistance. During this time, he organised a photo-shoot for Vogue magazine featuring members of the resistance movement posing for photographs!

    Seems he got away with it, though -- another officer writes in his file:

    'However, it is not for me to reason why, but no doubt the profile of Lt.Col Amies in the next issue of the Vogue will cause a flutter in many feminine hearts when they realise that their handsome couturier is, after all, the Scarlet Pimpernel of this war.'

    history uk funny clothing

    Threats close Kabul's Irish bar

    BlogStart:

    Booze: BBC: Threats close Kabul's Irish bar:

    Terrorism alerts have prompted the owners of Kabul's only bar to close down temporarily. The Irish Club has been a roaring success with correspondents reporting hundreds of drinkers inside at a time since it opened on Ireland's national holiday, St Patrick's Day.

    But the popularity of the bar, which is open only to foreigners in the predominately Muslim state, appears to have attracted the interest of terrorists, United Nations staff in the city said. ....

    Owners of the bar hope it will reopen next week, but its clientele is set to shrink after the UN banned its staff from going there for security reasons and other foreign aid organisations and diplomatic missions have issued warnings to their personnel. 'It's been placed off limits indefinitely after warnings that it could be the target of a terror attack,' said UN spokesman David Singh.

    Still, the owners say they'll do some renovation work while it's closed. Looking forward to the Beeb story about 'Kabul's Irish bar now boasts extensive beer garden and function room' next month...

    Spam: In other news, it seems AOL, Yahoo! and Hotmail are banding together to 'reduce spam'. This could be interesting.

    dublin ireland guinness funny

    A peek into a spammer's inbox, and 'targeting'

    Aardvark.co.nz: The Sound Of A Spammer's Laugh. Depressing reading. The article's has screenshot of two MMF-spam dropboxes -- here's one. It's full of mails from the spammer's victims. Upshot: make sure your friends know not to reply to spam -- and definitely not MMF spam. Mind you, if you're reading this blog, you and your friends are probably too smart for that anyway ;)

    Also: Brad Templeton on spam's 25th birthday; Brian Hayes in American Scientist. The latter has this nice (although wholly unscientific ;) graph of spam topics -- and it sounds like Brian's getting spammed by artmarket.com.

    That raises an interesting point. Spam is frequently trumpeted (by the spammers) as 'targeted'. What this often means, in reality, is that they've just randomly selected addresses and put them in a list as supposedly targeted for a given topic; or else run a Google search for a related term, and shoved a load of addresses from all pages found into a 'targeted' list.

    For example, my spam load includes:

    • Artmarket, above. I've never been known to buy art, apart from a few cheapo prints, and that was off-line.

    • The septic tank spammers. I have about 30 spams from the last 2 years flogging septic tanks. I don't even know what one looks like.

    • Turkish political spam. Don't have a clue. I went to Turkey on holiday once, but I never gave my email address to anyone ;)

    • the obvious stuff everyone gets: Japanese, Chinese and Korean spam. I can't even read the ideograms, let alone understand the written language.

    Plus the usual MMF, get rich quick, and porno spam. Not once have I seen a spam hawking DVDs of Koyaanisqatsi, classic breakbeat releases, or the new William Gibson novel -- now that would be targeting. But no...

    anti-spam spam filtering

    Amazon Web Services

    Tim O'Reilly: Killer Apps Share A Common Thread: Hacker Geeks.

    The really interesting bit in this is the discussion of the Amazon Web Services:

    Rob Federick, senior technology manager for Amazon.com, asked for a show of hands for those in the room who considered Amazon.com to be a retailer business and those who considered it to be a technology platform. O'Reilly was amongst the few who raised hands in support of the latter.

    It didn't start out that way. But Amazon soon discovered developers taking the Amazon interface and adding their own ideas. A 19-year-old developer from Romania, 'Catlin,' began designing store fronts that looked like the Amazon.com site, and then allowing other developers to download the source code for free.

    'We are allowing people to create and innovate in ways that Amazon.com cannot do on its own,' Federick said.

    This is incredibly significant, and shows how Amazon's leadership has a totally different vision compared to other online retailers. The others take the 'Altavista view' -- they want to lock their users 'in the trunk' as Dave Winer says; users stay on the retailer's site, aggregators and price-comparison engines are locked out, having to jump through hacky screen-scraping hoops, etc.

    In contrast, Amazon are more than happy to let other sites scrape their content using their web services, even if this could be used to show how other sites have lower prices, or possibly lose them sales. Wow. I'm sure that was hard to sell internally, but it's a great move.

    Spam: Reg: new spam trojan, called Proxy-Guzu. Yet another. :(

    amazon aws privacy

    Dublin Guinness to brew the Nigerian version

    Yahoo: Guinness brews up African recipe.

    DUBLIN (Reuters) - Guinness is brewing up an African-style version of its famous stout to quench the thirst of Ireland's growing immigrant population. Tests are under way to replicate Guinness manufactured in Nigeria at its St. James' Gate headquarters in Dublin. The African version of Guinness Foreign Extra Stout tastes sweeter and heavier than the traditional draught popular in the west, and is almost double in strength.

    A Guinness spokeswoman said the new brand was a result of consumer demand from Ireland's growing African population. 'This is the home of Guinness and so we're seeing if we can brew the African recipe here and produce it at St. James' Gate to the same recipe as in Nigeria,' she said. ...

    Guinness Foreign Extra Stout was first exported from Ireland in the 19th century to British colonies. The first Guinness exports to Africa were to Sierra Leone in 1827. The stronger alcohol content helped preserve it during the long sea journey.

    I can't wait to try it out. I used to continually overhear conversations on the bus between Dublin locals and Africans regarding whose Guinness was best -- time to settle the argument! ;)

    ireland dublin guinness food

    Luther Blissett, author

    Luther Blisset strikes again; the pseudonymous trickster anarchist collective from Bologna named after a West Indian footballer (it's all 'explained' in the manifesto) is still at work. Now they've written a swashbuckling bestseller historical novel called Q:

    Q has finally reached Britain, in Shaun Whiteside's zippy and rumbustious translation (Heinemann, £14.99). Set in Germany, the Low Countries and Venice between the 1520s and 1550s, it dramatises the bloody popular revolts that accompanied (and challenged) Luther's Reformation, and the Catholic undercover strategies that wrecked these radical movements. Imagine Umberto Eco's knack for the swashbuckling thriller-of-ideas crossed with an artful touch of the Le Carrés, and you have a fair idea of the novel's mood. ....

    Q works like a charm as a sordid, splendid period romp that painlessly informs its readers about the theological strife that splintered Europe (and the banking networks that re-connected it). Yet the reasons why a bunch of Bolognese stirrers shoud seize upon this theme soon grow clear. Effectively, their novel also operates as an allegory of Italian leftist politics since the Seventies. Out of the chaos of Utopian gambits and guerrilla provocations, in a murk of subterfuge, an elite plan for a 'new world order' emerges.

    Sounds great! Must remember to stick that in the wishlist.

    books history art

    Guantanamo Bay detainees including children

    Wierd. For the last two days, the PM news programme on BBC Radio 4 has been discussing the recent admission by (iirc) the US military commander in control of the Guantanamo Bay detention center, that there are several Afghani children who have been detained there, since the war in Afghanistan.

    This has elicited the reactions you'd expect from UNICEF, etc., seeing as it's in contravention of the UN Convention on the Rights of the Child.

    However, there's nothing on any English-language news pages I can find; just this Der Spiegel story, not even on the BBC news site itself.

    Update: Didn't look hard enough! Here it is. Also, the Irish Times reports:

    (General Richard Myers) responded sharply to questions about critical world reaction to the detention of three children, ages 13 to 15, at Guantanamo Bay in Cuba where the US military holds suspected al-Qaeda and Taliban members.

    'Despite their age these are very dangerous people,' he said. 'Some have killed. some have said they will kill again.'

    Defence Secretary Mr Donald Rumsfeld said the US was 'keeping them down there to keep them off the streets'.

    Hmm. On the BBC, the commander of the joint task force at Guantanamo, Major General Geoffrey Miller was interviewed; he said that the children had been press-ganged into fighting for the Taliban, and had been victims of abuse during that time. 'very dangerous people'?

    kids privacy politics

    'at teatime'?

    wtf? From the Red Hat 9 at(1) manual page:

    At allows fairly complex time specifications, extending the POSIX.2 standard. ... You may also specify midnight, noon, or teatime (4pm).

    time coding ireland algorithms

    US sugar industry threathens to kill off WHO

    This is quite simply insane:

    The sugar industry in the US is threatening to bring the World Health Organisation to its knees by demanding that Congress end its funding unless the WHO scraps guidelines on healthy eating, due to be published on Wednesday.

    The threat is being described by WHO insiders as tantamount to blackmail and worse than any pressure exerted by the tobacco lobby.

    In a letter to Gro Harlem Brundtland, the WHO's director general, the Sugar Association says it will 'exercise every avenue available to expose the dubious nature' of the WHO's report on diet and nutrition, including challenging its $406m (£260m) funding from the US.

    The industry is furious at the guidelines, which say that sugar should account for no more than 10% of a healthy diet. It claims that the review by international experts which decided on the 10% limit is scientifically flawed, insisting that other evidence indicates that a quarter of our food and drink intake can safely consist of sugar.

    Does anyone in their right mind think that a food intake consisting of 25% sugar makes any sense whatsoever?

    Food over here, BTW, has been really good compared to Ireland. We have a branch of Trader Joe's just down the road, which has supplied us with stacks of fantastic organic and/or healthy eats, for far cheaper than what the local supermarket charges for the usual pasteurised, added-sugar, added-salt crap.

    This is just as well, because that supermarket has some really nasty stuff; even the bread is sweet due to added sugar! yuck. (In passing, pet food peeve: pasteurised orange juice. Pasteurisation of fruit juice kills the flavour and texture, and is thoroughly pointless; with that much acid and sugar, there's no way any nasty bacteria can survive, assuming the juice is citrus and is fresh enough. But maybe that's the point; saleable while less fresh == longer shelflife == profit.)

    health ireland science papers research machine-learning food google

    Goodbye to Baghdad

    Goodbye to Baghdad (Guardian). Some good snippets:

    The information ministry and TV headquarters were obvious targets (for looters), but the wanton destruction of St George's church was unexpected. ... A man living next door to the church said Christians were seen as part of the regime.

    Tariq Aziz, after all, is a Christian. Also, this -- I knew it! --

    The US tanks that shot their way into the city have lost their menace. Children now go right up to the US soldiers, smile, and swear at them in Arabic, finding it hilarious that the troops think they are being friendly.

    And the politics of the Shia/Sunni divide:

    'The whole administration has been robbed and destroyed, except for those institutions which have been guarded by them (provisional Shia local government),' said the hospital director. He was transparently unhappy at having to take orders from the Shia clergy, but said America had left him no choice.

    'Without them, this hospital would have vanished. We have no civilian administration now. Until now America hasn't done anything for the civilian administration. They are just occupying us and doing nothing.'

    The doctor's dilemma raises a larger question. Did Bush go to war on Saddam Hussein's secular dictatorship to pave the way for an Islamist Shia regime bordering Iran? Because that is what is beginning to take root in Saddam City, and in other neighbourhoods of Baghdad. ....

    The new Shia assertiveness - whether through ambitions of religious government or the exuberance with which millions this week participated in a religious pilgrimage banned under Saddam - has horrified the Iraqi middle and upper classes, and the minority Sunni elite, which has been the traditional ruler of Iraq from the days of the Ottoman empire.

    Like the Americans, they have been slow to react these past two weeks, stunned by the speed with which the regime collapsed and mortified by the knowledge that millions have watched on TV as Iraqis laid waste to their own country, and history.

    politics us-politics journalism

    BBC chief attacks U.S. war coverage (fwd)

    BBC Director General Greg Dyke singled out for criticism the fast growing News Corp's Fox News Channel, owned by media baron Rupert Murdoch, and Clear Channel Communications, the largest operator of radio stations in the United States, with over 1,200 stations, for special criticism.

    'Personally, I was shocked while in the United States by how unquestioning the broadcast news media was during this war,' Dyke said in a speech at a University of London conference on Thursday.

    'If Iraq proved anything, it was that the BBC cannot afford to mix patriotism and journalism. This is happening in the United States and if it continues, will undermine the credibility of the U.S. electronic news media.'

    Dyke singled out Fox News, the most popular U.S. cable news network during the conflict, for its 'gung-ho patriotism,' saying: 'We are still surprised when we see Fox News with such a committed political position.'

    Good bits, via the IP list.

    ireland history news politics web

    SARS and Singapore

    (or humour?) Rod Liddle: How I was seized for my smoker's cough:

    Despite the almost total absence of SARS around here, the various governments are very worried, apart from the Singaporean government, which, I suspect, likes nothing more than imposing rigorous screening and quarantine programmes upon its somewhat cowed citizens and scrubbing everything down with disinfectant every five minutes. Stand on a street corner for too long in Singapore and you're likely to be sprayed with Dettol. But that was true long before SARS presented itself. ...

    We are still in the blame stage of this 'epidemic' and the blame shifts according to where you are and what the local government believes. A similar pattern of xenophobic mythology established itself during the early stages of Asian flu, Aids and the Ebola virus. Nasty, incurable diseases are almost always the fault of foreigners doing despicable, uncivilised things, usually with animals. Betcha there's a gruesome SARS film from Hollywood by the end of next year, with a heroic American doctor played by Ben Affleck, who saves Chicago, or something.

    Rod Liddle is very clearly on holiday.

    ireland uk science

    Spammers in the NYT again

    NYT: Internet Is Losing Ground in Battle Against Spam.

    'We have allowed these spam cops to rise out of nowhere to be self-appointed police and block whole swaths of the industry,' said Bob Dallas, an executive of Empire Towers, an e-mail firm in Toledo, Ohio, widely cited on antispam lists used by many Internet companies.

    'This is against everything that America stands for,' Mr. Dallas added.

    'The consumer should be the one in control of this.'

    Wow, way to shoot yourself down in flames. Without a spam filter to detect unsolicited bulk mail and differentiate from the solicited stuff from their friends and legit subscriptions, the consumer has control how, exactly?

    BTW, Empire Towers have a very impressive ROKSO listing. It says: 'Empire Towers (ET) is a hard-line stealth spamming operation whose spams are illegal in most US states. ET goes to elaborate lengths to hide spam origins and obfuscate URLs. They operate by obtaining multiple class C netblocks on multiple ISPs known for lax handling of spam complaints, the class Cs serving to make their account more valuable to the ISP so in theory harder to terminate.'

    spam anti-spam filtering

    'Internet advances not always pure tech' shocker

    Jason Kottke: Portal Wars II: When Search Engines Attack. He makes a great point (from Robert Morris at Etech 2002): while advances on the internet are typically heralded as tech-driven, in fact they're more often usability-driven. Examples:

    Mosaic was not an advancement in technology over TBL's original browser. Blogger is a highly-specialized FTP client. IM is IRC++ (or IRC for Dummies, depending on your POV).

    Dead right. Good tech, without the rough edges sanded down, and a degree of comprehensibility, is useless.

    Aside: I wonder if Robert Morris, IBM is any relation to Robert T Morris, the 1988 internet worm guy?

    internet web patents history swpats

    Evil Alarm Clocks

    It seems alarm clocks may be responsible for more than just waking you up at unfriendly hours of the day -- they may also make you hallucinate and imagine visitations from supernatural beings, according to Michael Persinger, a psychologist who's been investigating the effects of complex electromagnetic fields on the brain's perception. He says:

    As a human being, I am concerned about the illusionary explanations for human consciousness and the future of human existence. Consequently after writing the Neuropsychological Base of God Beliefs (1987), I began the systematic application of complex electromagnetic fields to discern the patterns that will induce experiences (sensed presence) that are attributed to the myriad of ego-alien intrusions which range from gods to aliens. The research is not to demean anyone's religious/mystical experience but instead to determine which portions of the brain or its electromagnetic patterns generate the experience.

    So it turns out that Horizon, the BBC science programme, has just shown an episode about Dr. Persinger's work. The transcript isn't up yet, unfortunately, but some mails on the forteana list make it sound like it'll be well worth a read when it is. (It'll be here, apparently.)

    One great find is this paper:

    'A left-handed Roman Catholic female adolescent with a history of early brain trauma reported nightly visitations by a sentient being. During one episode she experienced vibrations of the bed, an external presence along the left side that moved into her body, inner vaginal (not clitoral) and uterine sensations, and the sense of being impregnated by a force she attributed to the Holy Spirit. After the latter experience she felt an invisible baby superimposed upon her left shoulder. Analyses of the measurements for magnetic anomalies within her bedroom indicated an electric clock about 20 cm from her head while she slept. The complex form of the 4 microT magnetic pulses generated by the clock was similar to shapes that evoke electrical seizures in epileptic rats and sensitive humans.'

    Also worth noting that Richard Dawkins has little aptitude for religious feelings, even magnetically-induced ones!

    science bbc false-positives

    The Open Proxy Problem

    The Open Proxy Problem, a PowerPoint/PDF presentation shown at the Internet2 Members Meeting of April 9th 2003, by Joe St Sauver, Ph.D (Director, User Services and Network Applications University of Oregon Computing Center).

    Well worth a read if you're interested in network security or spam. Joe's done an astonishing job of researching every angle of the issue, from historical comparisons to 'blue boxes' circa 1971, the status of proxy servers to the Chinese government, and even a statistical analysis of proxy DNSBL overlap. (BTW, did you know that the New York Times was broken into via an open proxy?)

    censorship web security filtering anti-spam privacy

    Using VNC For Your Main Desktop

    I've just fixed my desktop machine (had to buy a new CPU, unfortunately, after the old one died during shipping).

    I then upgraded to Red Hat 9 (woo, very nice), switched to KDE for my desktop, and took a look at software suspend (because the machine is too noisy to leave on permanently in the corner of the living room).

    However, the latter won't work with my video card; instead, the machine reboots continually when resuming from suspend. Problem.

    A bit of thinking about the problem came up with a nifty solution... I'd heard of folks using a VNC server for their main desktop, in order to connect to it from any machine they found themselves near, and not be 'tethered' to one particular desktop machine. The same system also means I can run my desktop with a virtual display, and just 'connect' to this from the real one. Then, when I want to suspend, I can just kill off the X server, suspend, and start up a new one after resume.

    If you're curious about how to do this, read on...

    From: Justin Mason
    Subject: setting up a VNC desktop

    Software suspend won't work with my video card; instead, the machine reboots continually when resuming from suspend. Problem.

    A bit of thinking about the problem came up with a nifty solution... I'd heard of folks using a VNC server for their main desktop, in order to connect to it from any machine they found themselves near, and not be 'tethered' to one particular desktop machine. The same system also means I can run my desktop with a virtual display, and just 'connect' to this from the real one. Then, when I want to suspend, I can just kill off the 'hardware' X server, suspend, and start up a new one after resume.

    First, install xf4vnc. This gives you a VNC server that can use the 'Render' extension, and therefore display anti-aliased text efficiently. Installation of this is a bit of a manual job, unfortunately, since the author hasn't actually packaged it in any way. Not too hard though; just 3 copy commands; I don't think you actually need any files apart from the two in the xf4vnc-linux-i386 group.

    Create a file called ~/.xserverrc containing:

    :: /usr/local/bin/Xvnc-xf4vnc -depth 16 -geometry 1152x864 -deferupdate 10 :0

    Best to make the depth and geometry match your current display.

    Next, create a script called ~/bin/x containing:

    :: #!/bin/sh
    :: X :1 &
    :: sleep 4
    :: vncviewer -compresslevel 0 -quality 9 -fullscreen -display :1 localhost:0

    (ie. start an X display on :1, then display vncviewer to that display.) Don't forget to make it executable with chmod.

    Now, close your current X desktop, return to the console, and run startx to start a new one. This won't display; instead, it'll run GNOME/KDE/whatever using a virtual framebuffer. CTRL-Z and bg that process.

    Run the x script. It'll connect to your virtual desktop. That's it!

    You can now hit CTRL-ALT-Backspace to your heart's content. When your display is killed, the applications and desktop remain untouched. When you rerun the x script, it'll reconnect and nothing will have changed apart from the mouse pointer position. In fact, I just restarted my X server halfway through that sentence ;)

    Have fun!

    apple linux home

    Police chief says RUC cover-up may reach ministers

    Guardian: Ministers may be questioned over cover-up.

    The cover-up into security force collusion with loyalist murder gangs in Northern Ireland may have reached the highest echelons of the army and even government ministers, Britain's most senior police officer revealed yesterday. ...

    He said loyalist paramilitaries had been helped by RUC officers and members of a covert army squad, the FRU (force research unit), and that the cooperation between them included 'wilful failure to keep records, the absence of accountability, the withholding of intelligence and evidence, and the extreme of agents being involved in murder'.

    uk ireland law politics

    More RHL9 comments

    More comments on that RHL9 review... interesting to see that RH ran into the same Unicode problem we did with SpamAssassin -- namely that using Unicode charsets is horrifically slow compared to plain old ASCII. (This is the main reason we use ASCII internally in SpamAssassin.)

    Bootup Scripts and Unicode: All the text processing utilities, grep, awk, sort, etc all work significantly slower when using the Unicode UTF locale. To speed the bootup, in the /etc/rc.sysinit and other SysV scripts, because the configuration is using 7bit ASCII these utilities are now invoked with LC_ALL=C utility to force the C locale.

    (Also interesting to note who reported the bug, too ;)

    Other nice additions:

    • Keith Packard's xrandr, to resize and rotate an X screen on the fly.
    • redhat-config-(tab) to list all system config stuff from the commandline. At last, sensible naming for this stuff!
    • Debuginfo RPMs, to install debug symbols for your system libraries on-the-fly.
    • Subversion. (Although I'm a bit disappointed to read that svn doesn't improve on CVS' ability to do merges at all, which has drastically reduced my keenness to upgrade.)

    perl regexps spamassassin coding dfa optimization

    Red Hat 9, and POSIX ACLs

    Good techie review of RH9, thanks Padraig. I find this horrifically kludgy, though:

    Just a quick observation. The way text editors save files normally, is to create a new file with a temporary random name, and then move/rename the new file to name of the original. Using this technique, if the file being edited has ACLs, the ACLs will be lost. The Vim editor uses libacl to obtain the original ACLs, and then add them back after the save. It is important that other applications that save files in the same fashion are updated to use libacl.

    Bad bad bad. Shouldn't require application code updates like this. I think this is POSIX' fault. Mind you, according to acl(5), it looks like umask(2) and a concept of parent-directory-affecting-child-nodes'-ACLs seems to apply; so that improves matters a little.

    Still, I don't like the idea of changing something as fundamental as the system calls used to copy and update files in a filesystem, which hasn't changed in ~15 years on the UNIX platform. I am sure there'll be nasty side-effects. Maybe that's why the POSIX 1003.1e ACL standardization effort foundered ;)

    linux unix aws storage

    Afghanistan's First Irish Pub Opens

    You just can't get away from 'em. Irish bars, I mean.

    'The first public house in Afghanistan since the fall of the Taliban has opened - and it's Irish. The Irish Club opened on a secluded side street in the centre of Kabul last month - on St Patrick's Day.' ...

    'There are Afghan staff, of course, but they have all been given Irish names - Kevin, Jimmy, Michael, George - 'to protect them from possible retaliation' ...

    Fazel Ahmed Manawi, the deputy supreme court justice, said any Muslims found drinking at the Irish Club will be punished. 'We have got a lot of foreigners living in our country and unfortunately, this is a necessary thing for them,' he said.' (Full story)

    Date: Fri, 18 Apr 2003 09:36:01 +0100
    From: Joe McNally ...
    To: Yahoogroups Forteana ...
    Subject: Afghanistan - no end to the horror in sight

    http://www.irishnews.com/access/daily/current.asp?SID=431306

    Out with the Taliban, in with the craic

    THE first public house in Afghanistan since the fall of the Taliban has opened - and it's Irish.

    In Taliban times, a fully stocked Irish pub serving whiskey and cold beer in the heart of the ultra-Islamic country's capital would have been unimaginable.

    It still is for many Afghans, but the Kabul night-spot has been a life-saver for many expatriates working in the city.

    The Irish Club opened on a secluded side street in the centre of Kabul last month - on St Patrick's Day.

    There is no sign, and not even a number on the door, but in a country where terrorists are still a real threat, that is exactly the way the Irish owner Sean Martin McQuade wants it.

    "We wanted to keep a low profile, so we didn't advertise whatsoever," he said.

    "But people know where to find us. News travels fast by word of mouth."

    In a mock Tudor-style house behind the blank outer wall, immaculate Afghan waiters in black trousers, white shirts and black bow ties serve up beer for £1.25 and cocktails for £1.90.

    Customers - mostly aid workers, diplomats and journalists - crowd around a wooden bar topped off with green marble imported from Ireland.

    Afghan carpets are strewn about the floor. Posters for Guinness are tacked all over the walls. Small lanterns - handy during the sporadic power cuts - are placed on every table.

    "We are the first people to stick our necks out and say this can be a cosmopolitan city," Mr McQuade, who has worked as an engineer in Afghanistan for the last 11 years, said.

    He insisted that he had gone out of his way not to offend anyone and had sought the approval of a neighbourhood mullah to open the bar. In return, he promised to help rebuild the pot-holed road in front of the club and to help relocate an adjacent school to a bigger, better site.

    The bar is officially licensed by the state to sell alcohol - but only to foreigners. An Afghan bouncer keeps locals out, checking IDs and making sure patrons sign in.

    There are Afghan staff, of course, but they have all been given Irish names - Kevin, Jimmy, Michael, George - "to protect them from possible retaliation".

    The Taliban may no longer be in power, but Muslim conservatives continue to hold sway in Afghanistan.

    Fazel Ahmed Manawi, the deputy supreme court justice, said any Muslims found drinking at the Irish Club will be punished.

    "We have got a lot of foreigners living in our country and unfortunately, this is a necessary thing for them," he said.

    « Back -- Joe McNally :: Flaneur at Large :: http://www.flaneur.org.uk

    ireland politics dublin funny

    Venezuelan General: 'Proof Washington was behind coup'

    CBC.ca: Venezuela has Proof Washington was Behind Failed Coup, says General .

    The embassy also rejected allegations by governing party legislators that two U.S. military officials who visited the Fuerte Tiuna military base in Caracas the day before Chavez's ouster were helping coup leaders.

    The two officers spent two hours at the base April 11 to investigate information about troop movements, the embassy said. They left hours before Chavez was deposed. Two officers returned to the base April 13 for another evaluation of the situation.

    According to the Council on Hemispheric Affairs:

    Venezuelan and U.S. officials are investigating allegations that two high-level military officials from the U.S. embassy, including Army Lt. Col. James Rogers, were at Fuerte Tiuna military base the first night of the coup while Chávez was being held there.

    The U.S. embassy initially called the allegations 'pure rubbish.' A month after the overthrow, it issued a statement saying the two officials were at the base for two hours late Thursday afternoon, April 11, just before the coup unfolded that evening. They were checking reports of troop movements, the embassy said, and returned Saturday, April 13, during the coup to check the general situation.

    Ri-ight.

    The details of how the coup occurred are deepening suspicions of U.S. involvement among critics, such as Birns, who draw parallels to the 1973 coup in Chile. They contend that Chávez's overthrow was not the result of a 'spontaneous popular uprising' as the coup leaders, the U.S. government and Chávez opponents contend. Rather, they say, it was a highly orchestrated, carefully thought-out plan by a corrupt class of business, labor, media and military elites who are backed by the United States and who see Chávez's 'peaceful revolution' on behalf of Venezuela's impoverished majority as a threat to their privileges.

    'This is as classic as they come,' said William Blum, author of Killing Hope: U.S. Military and CIA Interventions Since World War II. In an April 27 interview with NCR, Blum said the CIA was 'not even embarrassed' to use its 'same methods all over again,' namely, helping to create a situation of chaos and violence that invites the military to step in.

    privacy us-politics algorithms

    reStructuredText v. EtText

    reStructuredText is apparently the new wave of text-based markup -- in the Python community at least. ;)

    It's basically a reworking of Zope's StructuredText, which -- like my own EtText, which is what this blog is written in -- is itself a reworking of Setext. Setext is an old Amiga smart-text format which I first encountered in the Plexus web server back in 1993. Plexus, BTW, was what HTTP server number 70-something ran.

    It's interesting. I'd been considering modifying EtText to use some StructuredText ideas, such as indentation indicating tag-nesting levels. But it looks like reStructuredText has got rid of that idea, and instead does what EtText does: ie. indentation indicates quoting. So it must have driven someone up the wall in that case.

    There's a reStructuredText primer here. Compare with EtText's quick intro. (gack, what is that font I'm using there? ;)

    Still, a few other nice ideas to steal ;) -- I like the idea of ending the paragraph with colon-colon to indicate that the next quoted block is a code sample in monospace format. hmm...

    text coding writing algorithms

    Ask Don Rumsfeld!

    the 'Ask Don Rumsfeld' simulator...

    Your question was:

    Any sign of those WMDs yet, Don?

    Answer:

    It might just be in the words one uses, and someone would then say, oh, my goodness, he thinks this and someone else thinks that. I am impatient. I probably will remain impatient. And if everything were being done absolutely perfectly, I probably would still be impatient. Our relationship with them is multi-faceted, it's political, it's economic, and clearly there are security implications.

    I guess anything's possible. I can't validate it. Oh, I think I'll leave that for the coming days and weeks. Now that I think of it, I shouldn't have mentioned it. So when we do the best we can and we pull all this information together, and we then say well that's basically what we see as the situation, that is really only the known knowns and the known unknowns.

    Maybe that is kind of idiosyncratic behaviour on my part but it seems quite rational to me and I think I will stick with it. And it's constantly a moving target. Well, you know, the United States has a wonderful record of humanitarian assistance, and caring about people, and participation in funding of medical activities, and food programs for people, and we're not against any religion. As a country, we're not against any race.

    It's just not knowable. We are looking for code words to describe a relationship that is in transition, I think, is a challenge. I don't have any good current information that would validate that story.

    us-politics funny politics

    Ways to pass the time on boring train journeys, pt.XVII

    A group of Russian train conductors needed hospital treatment after smashing their heads repeatedly against a train window to find out who had the strongest forehead.

    The conductors came up with the contest as a way of passing time on the 3,000 mile journey from Novosibirsk in Siberia to Vladivostock. The men were treated in hospital after stopping the train midway through the journey at the town of Vyazemskaya and demanding medical help, Pravda reports.

    Story filed: 08:48 Thursday 17th April 2003 (Ananova)

    funny travel health

    Record for most blocked host on the 'net

    Wow. I think this is the most blocklist hits I've ever seen in a mail... the open relay 61.159.235.36 is listed in a whole 19 DNS blocklists.

    • T_RCVD_IN_DEADBEEF (0.0 points) RBL: T_RCVD_IN_DEADBEEF RBL A check: found 36.235.159.61.bl.deadbeef.com., type: 127.0.0.2
    • RCVD_IN_NJABL (1.2 points) RBL: Received via a relay in dnsbl.njabl.org RBL A check: found 36.235.159.61.dnsbl.njabl.org., type: 127.0.0.9
    • RCVD_IN_OSIRUSOFT_COM (0.5 points) RBL: Received via a relay in relays.osirusoft.com RBL A check: found 36.235.159.61.relays.osirusoft.com., type: 127.0.0.9
    • RCVD_IN_UNCONFIRMED_DSBL (0.0 points) RBL: Received via a relay in unconfirmed.dsbl.org RBL TXT check: found 36.235.159.61.unconfirmed.dsbl.org., type: http://dsbl.org/listing?ip=61.159.235.36
    • T_RCVD_IN_WIREHUB_PROXIES (0.0 points) RBL: T_RCVD_IN_WIREHUB_PROXIES RBL A check: found 36.235.159.61.proxies.blackholes.wirehub.net., type: 127.0.0.2
    • T_RCVD_IN_GIPPER (0.0 points) RBL: T_RCVD_IN_GIPPER RBL A check: found 36.235.159.61.proxy.bl.gweep.ca., type: 127.0.0.1
    • T_RCVD_IN_WIREHUB_BH (0.0 points) RBL: T_RCVD_IN_WIREHUB_BH RBL A check: found 36.235.159.61.blackholes.wirehub.net., type: 127.0.0.2
    • RCVD_IN_DSBL (4.3 points) RBL: Received via a relay in list.dsbl.org RBL TXT check: found 36.235.159.61.list.dsbl.org., type: http://dsbl.org/listing?ip=61.159.235.36
    • RCVD_IN_BL_SPAMCOP_NET (0.0 points) RBL: Received via a relay in bl.spamcop.net RBL TXT check: found 36.235.159.61.bl.spamcop.net., type: Blocked - see http://spamcop.net/bl.shtml?61.159.235.36
    • T_RCVD_IN_SORBS (0.0 points) RBL: T_RCVD_IN_SORBS RBL A check: found 36.235.159.61.dnsbl.sorbs.net., type: 127.0.0.2
    • RCVD_IN_SBL (1.1 points) RBL: Received via SBLed relay, see http://www.spamhaus.org/sbl/ RBL TXT check: found 36.235.159.61.sbl.spamhaus.org., type: Listed on SBL - see http://spamhaus.org/SBL/sbl.lasso?query=SBL5950
    • RCVD_IN_OPM (4.3 points) RBL: Received via a relay in opm.blitzed.org RBL TXT check: found 36.235.159.61.opm.blitzed.org., type: open proxy - see http://blitzed.org/proxy/?ip=61.159.235.36
    • T_RCVD_IN_OSSOCKS (0.0 points) RBL: T_RCVD_IN_OSSOCKS RBL A check: found 36.235.159.61.socks.relays.osirusoft.com., type: 127.0.0.9
    • T_RCVD_IN_MONKEYS_UPL (0.0 points) RBL: Received via a relay in proxies.relays.monkeys.com. RBL TXT check: found 36.235.159.61.proxies.relays.monkeys.com., type: BLOCKED: See http://www.monkeys.com/upl/listed-ip-0.cgi?ip=61.159.235.36
    • T_RCVD_IN_OPM_HTTP_CONNECT (0.0 points) RBL: T_RCVD_IN_OPM_HTTP_CONNECT
    • T_RCVD_IN_SORBS_HTTP (0.0 points) RBL: T_RCVD_IN_SORBS_HTTP
    • T_RCVD_IN_FIVETEN_SPAM (0.0 points) RBL: T_RCVD_IN_FIVETEN_SPAM
    • T_RCVD_IN_OPM_HTTP_POST (0.0 points) RBL: T_RCVD_IN_OPM_HTTP_POST

    Aha. looking it up, it's in China. That explains it... Full message here.

    Date: Thu, 17 Apr 2003 07:51:51 +0000
    From: "HGH Free Sample" ...
    To: ...
    Subject: SPAM(40.60) Shed Weight While You Sleep with HGH hyvsjpilripyoiebf

    This is a multi-part message in MIME format.

    ------------=_3E9E19A5.69236551

    Content-Disposition: inline

    This mail is probably spam. The original message has been attached along with this report, so you can recognize or block similar unwanted mail in future. See http://spamassassin.org/tag/ for more details.

    Content preview: As seen on NBC, CBS, CNN, and even Oprah! The health

    discovery that actually reverses aging while burning fat.

    Content analysis details: (40.60 points, 5 required) T_DATE_SPAMWARE_Y2K (0.0 points) Date header uses unusual Y2K formatting ADDR_FREE (0.8 points) From Address contains FREE RATWARE_EGROUPS (4.3 points) Bulk email software fingerprint (eGroups) foun d in headers FROM_ENDS_IN_NUMS (0.7 points) From: ends in numbers BANG_OPRAH (4.3 points) BODY: Talks about Oprah with an exclamation! SOME_BREAKTHROUGH (0.9 points) BODY: Describes some sort of breakthrough WHILE_YOU_SLEEP (2.6 points) BODY: While you Sleep REVERSE_AGING (2.9 points) BODY: Reverses Aging BANG_EXERCISE (2.7 points) BODY: Talks about exercise with an exclamation ! DIET (0.0 points) BODY: Lose Weight Spam AS_SEEN_ON (3.3 points) BODY: As seen on national TV! T_AS_SEEN_ON (0.0 points) BODY: /seenn\b\s*(?:TV|ABC|NBC|CBS|CNN|Op rah|USA Today|48 Hours|(The )?New York Times|\w+\s+TV|:)/i T_BLANK_LINE_RATIO_01_08_10 (0.0 points) BODY: T_BLANK_LINE_RATIO_01_08_10 HTML_50_60 (0.1 points) BODY: Message is 50% to 60% HTML BAYES_90 (2.9 points) BODY: Bayesian classifier says spam probabilit y is 90 to 99%

    [score: 0.9050] HTML_MESSAGE (0.0 points) BODY: HTML included in message T_BLANK_LINE_RATIO_20_08_10 (0.0 points) BODY: T_BLANK_LINE_RATIO_20_08_10 T_BLANK_LINE_RATIO_04_08_10 (0.0 points) BODY: T_BLANK_LINE_RATIO_04_08_10 T_BLANK_LINE_RATIO_08_08_10 (0.0 points) BODY: T_BLANK_LINE_RATIO_08_08_10 HTML_TAG_BALANCE_HTML (0.0 points) BODY: HTML has unbalanced "html" tags T_MIME_QP (0.0 points) RAW: T_MIME_QP MIME_HTML_NO_CHARSET (0.0 points) RAW: Message text in HTML without specified charset FORGED_RCVD_HELO (1.0 points) Received: contains a forged HELO DATE_IN_FUTURE_03_06 (1.5 points) Date: is 3 to 6 hours after Received: date T_RCVD_IN_DEADBEEF (0.0 points) RBL: T_RCVD_IN_DEADBEEF

    [RBL A check: found 36.235.159.61.bl.deadbeef.com., type: 12 7.0.0.2] RCVD_IN_NJABL (1.2 points) RBL: Received via a relay in dnsbl.njabl.org

    [RBL A check: found 36.235.159.61.dnsbl.njabl.org., type: 12 7.0.0.9] RCVD_IN_OSIRUSOFT_COM (0.5 points) RBL: Received via a relay in relays.osiruso ft.com

    [RBL A check: found 36.235.159.61.relays.osirusoft.com., typ e: 127.0.0.9]
    RCVD_IN_UNCONFIRMED_DSBL (0.0 points) RBL: Received via a relay in unconfirmed .dsbl.org

    [RBL TXT check: found 36.235.159.61.unconfirmed.dsbl.org., t ype: http://dsbl.org/listing?ip=61.159.235.36]
    T_RCVD_IN_WIREHUB_PROXIES (0.0 points) RBL: T_RCVD_IN_WIREHUB_PROXIES

    [RBL A check: found 36.235.159.61.proxies.blackholes.wirehub .net., type: 127.0.0.2] T_RCVD_IN_GIPPER (0.0 points) RBL: T_RCVD_IN_GIPPER

    [RBL A check: found 36.235.159.61.proxy.bl.gweep.ca., type: 127.0.0.1] T_RCVD_IN_WIREHUB_BH (0.0 points) RBL: T_RCVD_IN_WIREHUB_BH

    [RBL A check: found 36.235.159.61.blackholes.wirehub.net., t ype: 127.0.0.2]
    RCVD_IN_DSBL (4.3 points) RBL: Received via a relay in list.dsbl.org

    [RBL TXT check: found 36.235.159.61.list.dsbl.org., type: ht tp://dsbl.org/listing?ip=61.159.235.36] RCVD_IN_BL_SPAMCOP_NET (0.0 points) RBL: Received via a relay in bl.spamcop.ne t

    [RBL TXT check: found 36.235.159.61.bl.spamcop.net., type: B locked - see http://spamcop.net/bl.shtml?61.159.235.36] T_RCVD_IN_SORBS (0.0 points) RBL: T_RCVD_IN_SORBS

    [RBL A check: found 36.235.159.61.dnsbl.sorbs.net., type: 12 7.0.0.2] RCVD_IN_SBL (1.1 points) RBL: Received via SBLed relay, see http://www. spamhaus.org/sbl/

    [RBL TXT check: found 36.235.159.61.sbl.spamhaus.org., type:

    Listed on SBL - see http://spamhaus.org/SBL/sbl.lasso?query=SBL5950]
    

    RCVD_IN_OPM (4.3 points) RBL: Received via a relay in opm.blitzed.org

    [RBL TXT check: found 36.235.159.61.opm.blitzed.org., type: 
    

    open proxy - see http://blitzed.org/proxy/?ip=61.159.235.36] T_RCVD_IN_OSSOCKS (0.0 points) RBL: T_RCVD_IN_OSSOCKS

    [RBL A check: found 36.235.159.61.socks.relays.osirusoft.com
    

    ., type: 127.0.0.9] T_RCVD_IN_MONKEYS_UPL (0.0 points) RBL: Received via a relay in proxies.relays .monkeys.com.

    [RBL TXT check: found 36.235.159.61.proxies.relays.monkeys.c
    

    om., type: BLOCKED: See http://www.monkeys.com/upl/listed-ip-0.cgi?ip=61.159.23 5.36] T_RCVD_IN_OPM_HTTP_CONNECT (0.0 points) RBL: T_RCVD_IN_OPM_HTTP_CONNECT T_RCVD_IN_SORBS_HTTP (0.0 points) RBL: T_RCVD_IN_SORBS_HTTP T_RCVD_IN_FIVETEN_SPAM (0.0 points) RBL: T_RCVD_IN_FIVETEN_SPAM T_RCVD_IN_OPM_HTTP_POST (0.0 points) RBL: T_RCVD_IN_OPM_HTTP_POST MISSING_MIMEOLE (0.1 points) Message has X-MSMail-Priority, but no X-MimeOL E MIME_HTML_ONLY (0.1 points) Message only has text/html MIME parts HG_HORMONE (1.0 points) Talks about hormones for human growth T_MIME_HTML_NO_DOCTYPE (0.0 points) T_MIME_HTML_NO_DOCTYPE MISSING_OUTLOOK_NAME (0.0 points) Message looks like Outlook, but isn't

    The original message did not contain plain text, and may be unsafe to open with some email clients; in particular, it may contain a virus, or confirm that your address can receive spam. If you wish to view it, it may be safer to save it to a file and open it with an editor.

    ------------=_3E9E19A5.69236551

    Content-Description: original message before SpamAssassin
    Content-Disposition: attachment

    by localhost.jmason.org (Postfix) with ESMTP id 714158B318 for ... Wed, 16 Apr 2003 23:03:54 -0400 (EDT)

    by localhost with IMAP (fetchmail-5.9.0) for ... (single-drop); Wed, 16 Apr 2003 20:03:54 -0700 (PDT)

    From: "HGH Free Sample" ...
    To: ...
    Subject: Shed Weight While You Sleep with HGH hyvsjpilripyoiebf
    Date: Thu, 17 Apr 03 07:51:51 GMT

    This is a multi-part message in MIME format.

    --8_0AED7_CBCE_D_E.1F.

    > As seen on

    NBC, CBS, CNN, and even Oprah!

    > The health

    discovery that actually reverses aging while burning fat.

    > Without dieting

    or exercise!

    > Forget aging

    and dieting forever!

    > l, Helvetica, sans-serif">Get

    Your Free Bottle Now! Visit Us Here


    Why was this email sent to you? At some point you registered or made a purchase on a Web site with privacy policies explaining that they may share your information with partners who will send you valuable offers from time to time.

    If you no longer wish to be notified of th= e latest

    scientific breakthroughs or valuable offers, you may simply choo= se to

    take yourself out of the database permanently by choosing this link.

    aumyfi flmpycuoji wv siskt u g jhuqxgtzvhftswxogtid xpypp

    --8_0AED7_CBCE_D_E.1F.--

    ------------=_3E9E19A5.69236551--

    anti-spam dnsbls spam

    Priorities

    Good to see the US troops in Baghdad were kept busy keeping an eye on the important stuff -- like surrounding the Oil Ministry building with 50 tanks and snipers, while the largest collection of antiquities in the Middle East got trashed. That's keeping your priorities straight!

    The imposing building in the Al-Mustarisiya quarter is guarded by around 50 US tanks which block every entrance, while sharpshooters are positioned on the roof and in the windows.

    The curious onlooker is clearly unwelcome. Any motorist who drifts within a few metres of the main entrance is told to leave immediately.

    Residents noted that the irrigation ministry, just next door, was torched.

    (Sydney Morning Herald) (more in attached mail).

    Date: Wed, 16 Apr 2003 08:07:44 -0000
    From: "uncle_slacky" ...
    To: ...
    Subject: Re: Baghdad looting

    --- In ... Roy Stilling ... wrote:


    > On "Yesterday in Parliament" yesterday, one of the awkward squad MPs
    > made the claim that while the mob was looting Iraq's museums and
    > public buildings, US forces guarded one ministry only - the Oil
    > Ministry. Anyone seen any corroboration of that claim anywhere?

    A quick News Google indicates, for example:

    Oil ministry an untouched building in ravaged Baghdad http://www.smh.com.au/articles/2003/04/16/1050172643895.html

    Since US forces rolled into central Baghdad a week ago, one of the sole public buildings untouched by looters has been Iraq's massive oil ministry, which is under round-the-clock surveillance by troops.

    The imposing building in the Al-Mustarisiya quarter is guarded by around 50 US tanks which block every entrance, while sharpshooters are positioned on the roof and in the windows.

    The curious onlooker is clearly unwelcome. Any motorist who drifts within a few metres of the main entrance is told to leave immediately.

    Baghdad residents have complained that US troops should do more to protect against the looters, most of them Shi'ite Muslims repressed by Saddam Hussein's Sunni-dominated regime who live in the vast slum known as Saddam City on the northern outskirts.

    But while museums, banks, hotels and libraries have been ransacked, the oil ministry remains secure.

    The symbolism is loaded, considering how vehemently the United States and Britain denied war opponents' accusations that the campaign to oust Saddam was driven by oil lust.

    "They came from the other side of the world. Do you believe they're going to do much for me? They've just come for the oil," fumed Salam Mohammad Hassan, a doctor who lives near the ministry.

    Residents noted that the irrigation ministry, just next door, was torched.

    US forces, who say they cannot prevent looting across the capital of five million, respond that they are not trying to seize Iraq's oil resources but preserve them.

    "Anyone who says we're protecting this ministry to steal Iraqi oil doesn't know what's really going on in this country," US Captain Scott McDonald told AFP at the ministry gates.

    The United States, he said, is only safeguarding Iraq's potential which would otherwise be considered game for looters.

    "Oil belongs to the Iraqi people; it's their property. It must be protected because it'll go, indirectly, to build schools and hospitals," he said.

    McDonald said a few looters had managed to sneak into the ministry- cum-fortress after US troops entered Baghdad. A few offices were robbed but nearly all files and archives remain intact, he said.

    Coalition forces also say they control all of Iraq's oilfields.

    Amnesty International has criticised the attention on controlling oilfields, which it said must have taken "much planning and resources."

    "However, there is scarce evidence of similar levels of planning and allocation of resources for securing public and other institutions essential for the survival and well-being of the population," the London-based rights group said.

    Iraq has the world's largest oil resources after Saudi Arabia, with 112 billion barrels of proven reserves.

    Before the start of the war, Iraq was producing about 2.5 million barrels a day, of which just under two million were exported under UN supervision through the "oil-for-food" program.

    In front of the oil ministry, a young Iraqi sat down in hopes of selling cigarettes.

    "Before, lots of people would stop here to buy from me, that's why I've kept coming. But there hasn't been anyone for a few days."

    Upon saying that, he was kicked out unceremoniously by a soldier.

    *

    and going back to last week, from

    http://www.guardian.co.uk/worldlatest/story/0,1280,-2547131,00.html

    "U.S. troops occupied the Oil Ministry. But the nine-story Ministry of Transport building was gutted by fire, as was the Iraqi Olympic headquarters, while the Ministry of Education was partially burned. Near the Interior Ministry, the office building of Saddam Hussein's son Odai stood damaged, its upper floors blackened."

    and from

    http://www.guardian.co.uk/worldlatest/story/0,1280,-2556458,00.html

    "The Oil Ministry also seemed intact with a heavy U.S. military presence inside."

    BTW these reports are duplicated on many other news sites, they're not just the product of the Grauniad's fevered imagination...

    Rob

    politics us-politics history

    Iraqwar.ru Redux

    Did Russians Use Blog To Aid Iraq? Some slightly paranoid theories, IMO. Interesting to note, though, that Stratfor reckons it was written by GRU (or ex-GRU) staff.

    The bottom line of the article, more or less, is that it was written by some ex-GRU people who possibly wanted to help the Iraqis, who indirectly received the intelligence from folks still employed by the agency.

    Interesting snippet:

    Denisov said 'a high-level source' told him that sensitive information being promulgated in the Russian media, Iraqwar.ru included, was one ... item on the agenda during Bush national security advisor Condoleezza Rice's meeting the day before at the Kremlin with Russian President Vladimir V. Putin.

    politics history spam

    For reference: email usability

    I was clearing out my mail last night, and came across a message that referenced a mail I sent a few years back; it's a selection of feature requests I made at the start of development of Evolution, the GNOME mail reader/contact manager/Outlook clone. (Not sure if any got implemented BTW ;)

    Since I still think some of these are killer ideas that would really improve email readers, and since the only copy is sitting in a mailing list archive, I'll take a local copy here by posting it.

    Worth noting that the reason it came up was a quick mail exchange with Kaitlin 'Duck' Sherwood, who's the queen of email usability, and will be working on the OSAF's Chandler PIM (and mail) application. Not only had she read the CHI'96 paper in question, she noted it as a 'profound influence'! Cool -- and bodes well for Chandler!

    Kaitlin also replied with some excellent plans for folder-overview presentation; I can't wait to see the results in Chandler, personally. If you want an idea of this stuff, her page on the Perfect Email Client lives here.

    Quick top tip: filtering or colorizing messages based how you're addressed in the headers is immediately beneficial. Quoting Ducky:

    My pet view also color-codes messages based on how you were addressed.
    • to me and only me
    • to me and other people
    • cc me and only me
    • cc me and other people
    • bcc me
    • Most people who have implemented the above techniques (you can do it
      with either Outlook or Eudora, though it's somewhat painful to set up) tell me they've saved between 25% and 50% of their prior email time.

    She's right, too!

    From: Justin Mason ...
    Date: Fri, 02 Jun 2000 12:11:56 +0100
    Subject: CHI'96 paper on mail usability and some thoughts

    Hi guys,

    Dunno if you've seen this, it's a good paper on email usability and some recommendations to improve same...

    http://www.acm.org/sigchi/chi96/proceedings/papers/Whittaker/sw_txt.htm

    Basically it says:

    1. heavy mail users use incoming mail as a to-do list and appointment tracker

    (I personally would add "as a reference bookshelf" as well in my case);

    1. filing into folders doesn't work in a lot of cases; once it's out of the

    inbox it's off the radar and soon forgotten about; and folder names are hard to pick and remember;

    1. users quite often do not delete mails in case they become valuable context

    for an ongoing discussion, resulting in inbox bloat and an interleaved stack of messages from threads filling up the inbox;

    1. inbox bloat means important mails from a day or two ago soon scroll out

    of the "main" window and are lost in the noise.

    to fix these:

    • it recommends threading (makes sense, and we know that). This reduces

    the visual impact of inbox bloat and sorts 3. and 4.

    • close links to PIM functions such as todo and datebook would be good to help

    with 1. (that's the plan isn't it!)

    • vfolders should deal with 2.

    A few ideas I came up with myself during reading it:

    • I previously added some code to ExMH to colorise messages, and used

    the colours as a way of differentiating "todo low-priority", "todo high-pri", "support mails", "pals chatting", etc. This worked very well as a way to scan a lot of mails and immediately work out the rough categorisation without having to read and parse the from and subject. (unfortunately the code stopped working in the next ver of ExMH and my Tk knowledge wasn't good enough to fix it!) Helps with problem 4 and aids scanning.

    • up to now there's been essentially 3 states for mail messages -- "unread",

    "read" and "deleted" (ie. not there anymore). I would like to see another state, "saved_as_context", which would be similar to deleted; ie. the mail would not be visible to the user at all. However, if another mail came in that referenced the "saved_as_context" mail, it would be possible (probably through hitting a "view context thread" button) to see all of that new msg's context mails. This sorts out problem 3 in a nice way IMHO. BTW it may even be better to use "saved_as_context" instead of "deleted", ie. keep deleted msgs around for possible context use, and purge them periodically.

    • Retitling mails (ie. changing their subjects after they've been received)

    would help deal with problem 1 as well -- e.g. changing a mail from "Re: help" to "How to fix the latest Outlook worm" is obviously handy for future visual message retrieval ;)

    • It would be handy if an incoming mail can be converted into a To-Do list item

    in the PIM interface; ie. right-click on mail, select "add to to-do list", and that mail (and/or thread!) would be visible in the To-Do PIM interface in some way (even just as a "see this mail" link a la the "note" attached to Palm To-Do list items). It'd also be cool if this went both ways so the To-Do list position/priority of a mail was visible in the inbox view.

    Anyway, these are some ideas I thought I'd throw in. I'm pretty excited by the possibilities of Evolution, and I'm looking forward to trying it out; after reading that paper, I just had to share ;)

    BTW I haven't used MS Outlook, so forgive me if Outlook sorts out these problems and I just didn't notice -- ditto for Evolution too, I haven't had the time to get it compiling yet! ;)

    --j.

    mail email smtp ui unix

    'And if she back with new coalition of da willing you better know fi run fast'

    SomethingAwful: Livin' In A Dictator's Paradise. Possibly the funniest thing I've read in weeks:

    Those of you who follow the minor news related to the recent war in Iraq might have noticed a story about the CIA broadcasting an insulting rap song about Saddam Hussein on their radio airplane. While this may seem like a fairly good idea if you're say drunk or waging a war against a rival gangsta rapper when you're fighting a real war it seems a little silly. Oh how wrong I was! Set to the tune of 'Gangsta's Paradise' this rap is roughly two minutes of distilled pathos, no doubt swaying the thoughts of many Iraqis against their brutal dictator and earning the United States a reputation for intelligence. Think about it, one day you're strapped to a mattress spring with a car battery hooked up to your testicles being shocked for mispronouncing 'Tikrit'. The next day you're listening to the radio and on comes this 'awesome' rap song about Saddam with lines like 'My days are finished and I will die - all I need is chili fries' and 'Everybody in the house say we hate you'.

    That's about when you say goodbye to your family, strap some dynamite to your chest, and sprint to the nearest Marine Corps checkpoint. What a fucking travesty. There is so much wrong with this whole concept, let alone the cringe inducing execution, that it's hard to know where to start a rant about it. The whole thing reeks of the clumsy hipster appeal of something like 'Poochy' from the 'The Simpsons' only ten times worse because instead of a stodgy corporate think-tank it was done by the government. Asking them to create anything that's in touch with the youth market is sort of like going to a retirement home and asking a bunch of septuagenarians with Alzheimer's disease to pen a film script about teens coming of age in the ghetto.

    Helpfully, Zack provides some suggested new tunes to cover for the next conflict with Syria... read on...

    politics spam 419

    Amazing photo of London by night

    Wow. An incredible shot up at Astronomy Pic of the Day, taken by an unnamed astronaut on-board the ISS with a digital camera. Hyde Park, Regent's Park, and the M25 are all very clearly visible.

    So I guess that means the Great Wall is no longer the only man-made structure visible from space then ;)

    art history london

    Reasons Not To Buy Dell Laptops, pt. XVII

    While trying to figure out why my loaner laptop is SO SLOW, I found this on the Linux Dell laptop temperature-control i8k driver website:

    No credits to DELL Computer who has always refused to give support on Linux or provide any useful information on the I8K buttons and their buggy BIOS.

    Makes you wonder if there are any laptop manufacturers with a concept of open hardware support.

    (BTW, current theories on the woeful speed are (a) 128megs of RAM just isn't enough to use GNOME or KDE on linux these days, and (b) a 4200rpm disk with feck-all cache can't handle any hard work.)

    Other bad news: my heavy-lifting desktop PC's arrived and won't power on. yikes.

    But -- on a brighter note: the sun's come out; I saw an eagle yesterday; and it rained last night, and all the birds are twittering in the trees, catching worms etc. In the meantime, the lazy cat sits on the balcony and watches idly, even when one lands on the railing less than 3 feet away. I suppose catfood is a lot easier to get hold of. ;)

    hardware home linux

    'Crows shall feed on Gordon Brown's pancreas'

    Ben Hammersley links to these two works of comedic genius: Mohammed Saeed al-Sahaf's new column in the Grauniad:

    Earlier in the week I watched as joyous Iraqis celebrated our triumph by pulling down - with the help of defecting American soldiers - Baghdad's only statue of actor Robert Donat as Mr Chips. I understand it was quite a good film, but we have no need of your imperialist icons now. Saddam has freed us from your oppressive rule, so we are saying goodbye to your Mr Chips. Ha! I have made myself laugh! I will not gloat further over this thrilling but predictable defeat which vindicates me so completely.

    Also, a blog here. Brilliant.

    funny politics uk

    Tim Bray on Drugs

    Tim Bray's weblog is a great read; I've added it to my daily list. Today, he's provided a fantastic article about the drugs problem in Vancouver's Downtown Eastside.

    Dublin has historically had a serious of up-and-down swings with a heroin problem; at one stage, it was one of the worst in Europe. It improved quite a lot during the 90's, but it's going downhill again, apparently; maybe the legislators need to read this article.

    (The big problem as far as I can see is that treatment centres are horrifically underfunded, it being a lot easier, and -- while not cheaper -- at least already budgeted for, to ship the junkies off to prison. Business as usual. Of course, while they're there, they're (a) off the streets (out of sight, out of mind), and (b) learning all the latest criminal techniques, and getting well hooked on all the cheap heroin in there.)

    (BTW did you know that one reason heroin is massively popular in prisons, is due to drug-testing? Apparently, marijuana can be detected a month after use, whereas heroin is undetectable 48 hours afterwards. So prison drug-testing regimes indirectly encourage heroin use. Oops!)

    Linux: Linux Journal: report from LinuxWorld Ireland. Sounds like a great talk from maddog and Michael Meeks. And if you look carefully at the photo on that article page, you can see Proinnsias in the background!

    Mind you, I would probably have just done my 'incomprehensible question about software patents' schtick with the IBM guy again...

    What with this and GUADEC coming to Dublin, I'm missing all the good piss-ups^Wevents it seems ;)

    ireland dublin politics cocaine drugs

    Z/Yen and RSA UK: purveyors of clueless FUD, as expected

    BoingBoing and /. get to work on that Z/Yen/RSA press release:

    But the amazing thing is what Z/Yen and its client, RSA conclude: that the 25% of the people who deliberately associated with the network were 'malicious,' and that the 71% who sent email were sending spam. This is such a transparently, deliberately (heh) stupid conclusion, it boggles the mind: how can 'deliberate' equate to 'malicious?' How can 'sending email' equate to 'sending spam?'

    So in other words, there were 2 honeypot access points, left open for 2 weeks in the City of London.

    25% of the people who connected to the APs, did so deliberately (whatever that means -- see below).

    Then, 71% of those people sent mail. Not spam: no 'make money fast', no 'URGENT ASSISTANCE' etc.; they just hit the 'Send / Receive' button in Outlook.

    But obviously Z/Yen and RSA felt the need to spice things up a bit, so:

    • s/accessed WLAN deliberately/accessed WLAN maliciously/

    • s/sent mail/sent SPAM/

    • s/read slashdot/ate babies/

    OK, I made that last one up. But I would not be surprised.

    Some more digging reveals that the report in question is now up on the RSA UK website (it wasn't yesterday), and can be downloaded here (PDF) . It's 5 slim pages written by Phil Cracknell, of CISSP (Cracknell Information Systems Security Partnership), who has a history of spreading WiFUD, it seems. The report leads with

    The many wireless security surveys ... do not actually show how real the threat of wireless hacking is. Less dramatically, they do not show the threat of someone using your network for non-malicious use (theft of service).

    Sheesh. He forgot to mention the bit about operating a wireless network without switching on any security features.

    Also, there's no explanation of what the difference is between a 'deliberate' and 'accidental' connection. As far as I can tell, an 'accidental' connection is one where the user disconnected reasonably quickly; there's no indication that any of the connections were caused by anything other than Windows XP's ability to associate with any network it can find within range.

    It then goes on to scare-monger about the use of 'exterior chalk markings', noting that 'you will be found and your networks will be used/attacked'.

    So, in other words, the paper says:

    • if you run an open WiFi AP, people will use it to send/receive mail, and possibly surf the web.

    • this is Bad

    • people may draw nerdy things with chalk on the pavement outside, which will Make It Worse

    And there's two things to pick up from it:

    • this Phil Cracknell guy is really short of clients

    • It's amazing how scare-mongering a 200-word report can become, when it's bad to start with, and then filtered through 3 layers of PR gibbons and crappy journos who don't have a clue what it's on about

    One good thing to come out of it: the term WiFUD, perfect for the next Phil Cracknell escapade.

    spam anti-spam filtering botnets security

    Aeronautics.RU

    Joe Haslam (hi Joe!) mailed about Aeronautics.RU, wondering if it's a fake. I'm pretty sure not, and John Sutherland at The Guardian concurs, noting that it was big in the City of London:

    You don't factor news into your model, but intelligence. There is a surfeit of war news, but reliable intelligence is hard to come by. The canny (stock market) trader in these parlous days has a first port of call - GRU (Glavnoye Razvedyvatelnoye Upravleniye), the espionage arm of the Russian military.

    GRU is the most sophisticated agency of its kind in the world. And, since Glasnost, the most transparent. GRU has thousands of agents worldwide (especially in countries such as Iraq, where Russia has traditional trade links). Intelligence has always been a top priority for Ivan. The number of agents operated by the GRU during the Soviet era was six times the number of agents operated by the KGB.

    Russia, superpower that it was, still has spy satellites, state-of-the-art interception technology and (unlike the CIA) men on the ground. The beauty of GRU is that it does not (like the CIA) report directly to the leadership but to the Russian ministry of defence. In its wisdom, it makes its analyses publicly available. These are digested as daily bulletins on www.iraqwar.ru.

    ... and syndicated onto Aeronautics.RU as well. Sadly, since the Russians closed up their Baghdad embassy and got out of Iraq, just in time it seems, all the reports have dried up. Ah well.

    The reporting was incredibly detailed, and modulo a big chip on their shoulder about US imperialism, pretty informative.

    Joe also points to another Aeronautics.RU article, 'how military communications are intercepted'. Venik, the author, notes that the US is using SINCGARS 'frequency-hopping' radios, which use a daily-broadcast shared secret as an initial vector for the algorithm which determines what frequencies to 'hop' through, throughout the day.

    However, security afforded by frequency-hopping methods is very dependant on the strict adherence to protocols for operating such radios. The US troops and other operators of frequency-hopping radio sets frequently disregard these protocols. An example would be an artillery unit passing digital traffic in the frequency-hopping mode, which would enable an unauthorized listener to determine the frequency-hopping algorithm and eavesdrop on the transmission. (jm: sounds like a known-plaintext attack; similar attacks were used by the Allies on German use of Enigma during WWII.)

    Even when proper protocols for using frequency-hopping radios are being adhered to interception and decryption of these signals is still possible. The frequency-hopping interceptors are special advanced reconnaissance wideband receivers capable of simultaneously tracking a large number of frequency-hopping encrypted transmissions even in high background noise environments.

    It then details some seriously specialized equipment for breaking frequency-hopping radio transmissions, which can 'process the complete 30 to 80 MHz ground-to-ground VHF band within a 2.5 ms time slot'.

    So judging by all of that, the chances of finding one of those 'FH-1 frequency-hopping interceptors', 'manufactured by VIDEOTON-MECHLABOR Manufacturing and Development Ltd of Hungary', sitting in the Russian embassy in Iraq about 2 weeks ago, would have been pretty high I'd bet. ;)

    He doesn't detail why encryption the system uses, or how that is supposedly being broken. But I don't doubt it was, personally. Given the 'artillery unit' hole noted above, there were probably quite a few ways to get hold of the day's key, given enough time and thought; and from what I've read, it can only be very tricky to use good crypto, and keep it secure, in a battlefield environment. And those Russians have had plenty of time to think about US military systems after all. ;)

    security politics hacking nsa

    RSA, Z/Yen report open WiFi hot-spots used to send spam

    Well, this is bad news. It seems one of the biggest bugbears for open Wifi hot-spots, 'what if it's used to spam', may now be happening on a wide scale...

    Unauthorized WLAN Connections Used to Send Spam (2 April 2003)

    Data gathered from a wireless LAN (WLAN) honeypot showed that nearly 75% of intentional unauthorized connections made were used to send spam. (newsfactor.com)

    The honeypots were set up in the City of London for 2 weeks, as default, open WLANs. This is the nearest I can come to a source. Both RSA Security UK and Z/Yen don't list it on their press releases pages.

    My thoughts: it could be the Jeem or Rewt spam-relaying trojans searching for open nets automatically, from infected machines. Strikes me that there wouldn't be too many spammers war-driving around London, in person.

    Thanks to Tony Earnshaw for forwarding it on from SANS NewsBytes...

    Date: 09 Apr 2003 19:57:32 +0200
    From: Tony Earnshaw ...
    To: ...
    Subject: SANS Newsbytes for today

    SANS stuff is always interesting; those who care about their network and computer security should really subscribe - not to mention the SANS GIAC stuff.

    The undermentioned is interesting to SA Talk.

    -- Unauthorized WLAN Connections Used to Send Spam (2 April 2003) Data gathered from a wireless LAN (WLAN) honeypot showed that nearly 75% of intentional unauthorized connections made were used to send spam.

    http://www.newsfactor.com/perl/story/21168.html

    Tony

    --

    Tony Earnshaw

    e-post
    tonniatbillydotdemondotnl
    www

    http://www.billy.demon.nl


    This SF.net email is sponsored by: Etnus, makers of TotalView, The debugger for complex code. Debugging C/C++ programs can leave you feeling lost and disoriented. TotalView can help you find your way. Available on major UNIX and Linux platforms. Try it free. www.etnus.com

    Spamassassin-talk mailing list ... https://lists.sourceforge.net/lists/listinfo/spamassassin-talk

    spam anti-spam security botnets

    Military dialect and 'clearing' (fwd)

    "There's even dialects of 'english' military jargon. An ex-general giving analysis on Sky (TV) commented that during the last Gulf War, confusion was caused because when a US commander said they'd 'cleared' a town they meant they'd gone past it, but when a british commanders said he'd 'cleared' a town he meant he'd dealt with most pockets of enemey and there was no signifigant resitence left in it and it was now 'safe' for occupation.

    The two confusions caused american comanders to wonder what a british comander was still doing in a town he'd said he'd 'cleared', and british troops wondering who the hell was shooting at them out of towns the americans had said they'd 'cleared'." (via Barbara Barrett on the forteana list)

    languages funny history

    Artprice/artlist: winners of the address-scraping spammer speed record

    Wow. A spammer has already scraped my blog and caught that one-use cdt_comment_go address I posted a week or so ago. That has to be a record. Ah well, Bayes and the SBL are catching it nicely...

    The spammer in question is artprice.com, aka. artlist.com, aka a bunch of unrepentant spammers who've been out-and-out spamming for years, from France. Nothing worse than a full-time spamhaus. My consolation is that if they do this after August, I can prosecute them for it, since France is in the EU ;)

    Just for reference, if anyone finds this on a Google search: the address was a one-use disposable job, for comments on a survey, posted once, and never used for sign-ups or even to send a single mail message. This is 100% spam, through and through.

    spam anti-spam email

    US Air Force Bombs John Simpson

    Nice one! 'Friendly fire' reaches the nadir! The USAF have just dropped a bomb on John Simpson and a convoy of US special forces

    (RealAudio report)
    :

    Simpson: 'So there are Americans dead. It was an American plane that dropped the bomb right beside us - I saw it land about 10 feet, 12 feet away I think. This is just a scene from hell here. All the vehicles on fire. There are bodies burning around me, there are bodies lying around, there are bits of bodies on the ground. This is a really bad own goal by the Americans. We don't really know how many Americans are dead.'

    Presenter: 'John, just to recap for the viewers, an American plane dropped a bomb on your convoy of American special forces - many dead, many injured?'

    Simpson: 'I am sorry to be so excitable. I am bleeding through the ear and everything but that is absolutely the case. I saw this American convoy, and they bombed it. They hit their own people - they may have hit this Kurdish figure, very senior, and they've killed a lot of ordinary characters, and I am just looking at the bodies now and it is not a very pretty sight.'


    (context: John Simpson is one of the BBC's top reporters in the field. Apparently, Ted Koppel would be roughly equivalent in stature in the US.)

    Sarah Carey notes some interesting aspects of the NYTimes coverage of the incident:

    1. This article is placed 27th on their full listing of international headlines. The top headlines are all concerned with the victories in Baghdad and Basra and the likely format of post-Saddam government. The only reason I found the article was because I deliberately went looking for it.

    2. Note how many quotes are from wounded Kurds insisting that they do not blame the Americans.

    3. They say that one American was wounded when the live BBC reports conclusively stated that American soldiers were killed.

    4. They neglect to mention that the BBC translator was one of those killed.

    5. Finally, and most insultingly, they give one short quote from John Simpson, the BBC World Affairs Editor, pointing out how US soldiers treated the wounded. It neglects to mention the ... quotes he also provided in his report (see above).

    Unsurprisingly, the rumour mill reports that the British 'Desert Rats' are now painting the stars and stripes on their vehicles, to avoid yet more 'friendly fire' incidents...

    Propaganda: FARK's Photoshop Phriday this week is on the theme of how Fox News would have covered events in history. Some hand-picked works of genius:

    Brilliant. (via boingboing)

    journalism politics media

    Spamming my HTTP referrer logs, pt. 2

    I've been getting a very wierd attack on my sites recently, including this blog, the SpamAssassin websites, and http://jmason.org/ , whereby some luser is sending lots of requests, using made-up URLs in the referral field. Initially, I thought it was some kind of underpowered retaliation for SpamAssassin, but if that's the case, they need to bone up a bit more on how these things work ;)

    Alternatively, it could be an attempt to gain Googlejuice, by getting links from public referrer logs (my ones are).

    Up 'til about a month ago, it was all porn sites. Recently, though, it's been a selection of real domains that sound like they were put together by combining dictionary words or something.

    All the attempts have come from IP address 216.127.68.58, owned by Everyone's Internet, Inc. in Houston, TX:

    216.127.68.58 - - [31/Mar/2003:00:01:53 +0100] "GET / HTTP/1.1" 200 72143 "http://www.aircheckfactory.com" "User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.0)''

    Here's the domains in question:

    • AIRCHECKFACTORY.COM
    • ALTOTECHNOLOGY.COM
    • BAIDYANATHINDIA.COM
    • NXTCENTURY.COM
    • TIMEART.NET
    • WOTEVA.COM

    Perhaps they're recent lapsed domains which the spammer has picked up. Otherwise, what's the connection between Baidyanath (a manufacturer of Ayurvedic products in India, thx Suresh) and 'woteva' (which sounds like 'whatever' in a UK english accent)?

    I've whois'd them all, and they all seem to share two things: the name 'Robert Woodley' (or its initials), and the number (772) 594-2421. Area code 772 is -- guess where -- Florida. They should just cut to the chase and put 'The Spammer State' on their numberplates.

    The pages on those sites are automatically-generated using what looks like USENET postings and google image search results, with a link to Commission Junction.

    None of the names are in ROKSO, it seems. Do they ring a bell with anyone reading?

    Date: Thu, 03 Apr 2003 13:20:06 -0800
    From: ... (Justin Mason)
    Subject: whois details on referrer spam

    Registrant:
    Michael Lewisham
    RW Internet
    PO Box 4723
    Grand Cayman,  8621
    Cayman Islands
    Registered through: ozwebsites 
    Domain Name: AIRCHECKFACTORY.COM
    Created on: 03-Jan-03
    Expires on: 03-Jan-04
    Last Updated on: 03-Jan-03
    Administrative Contact:
    Lewisham, Michael  ...
    RW Internet
    PO Box 4562
    Grand Cayman,  7238
    Cayman Islands
    (772) 594-2421      Fax -- 
    Technical Contact:
    Lewisham, Michael  ...
    RW Internet
    PO Box 4562
    Grand Cayman,  7238
    Cayman Islands
    (772) 594-2421      Fax -- 
    Domain servers in listed order:
    NS1.MYDOMAIN.COM
    NS2.MYDOMAIN.COM
    NS3.MYDOMAIN.COM
    NS4.MYDOMAIN.COM
    Registrant:
    Michael Lewisham
    RW Internet
    PO Box 4723
    Grand Cayman,  8621
    Cayman Islands
    Registered through: ozwebsites 
    Domain Name: ALTOTECHNOLOGY.COM
    Created on: 29-Dec-02
    Expires on: 29-Dec-03
    Last Updated on: 29-Dec-02
    Administrative Contact:
    Lewisham, Michael  ...
    RW Internet
    PO Box 4562
    Grand Cayman,  7238
    Cayman Islands
    (772) 594-2421      Fax -- 
    Technical Contact:
    Lewisham, Michael  ...
    RW Internet
    PO Box 4562
    Grand Cayman,  7238
    Cayman Islands
    (772) 594-2421      Fax -- 
    Domain servers in listed order:
    NS1.MYDOMAIN.COM
    NS2.MYDOMAIN.COM
    NS3.MYDOMAIN.COM
    NS4.MYDOMAIN.COM
    Registrant:
    Robert Woodley
    Robert Woodley Internet
    PO Box 401
    Grand Cayman,  7651
    Cayman Islands
    Registered through: Go Daddy Software (http://www.godaddy.com)
    Domain Name: BAIDYANATHINDIA.COM
    Created on: 09-Jan-03
    Expires on: 09-Jan-04
    Last Updated on: 09-Jan-03
    Administrative Contact:
    Woodley, Robert  ...
    Robert Woodley Internet
    PO Box 4634
    Suite 205
    Port Vila,  8621
    Vanuatu
    (772) 594-2421      Fax -- (772) 594-2421
    Technical Contact:
    Woodley, Robert  ...
    Robert Woodley Internet
    PO Box 4634
    Port Vila,  8621
    Vanuatu
    (772) 594-2421      Fax -- (772) 594-2421
    Domain servers in listed order:
    NS1.MYDOMAIN.COM
    NS2.MYDOMAIN.COM
    NS3.MYDOMAIN.COM
    NS4.MYDOMAIN.COM
    Registrant:
    Wanker Engineering
    PO Box 9816
    Auckland,  3522
    New Zealand
    Registered through: Go Daddy Software (http://www.godaddy.com)
    Domain Name: NXTCENTURY.COM
    Created on: 21-Mar-01
    Expires on: 21-Mar-04
    Last Updated on: 21-Mar-03
    Administrative Contact:
    Engineering, Wanker  ...
    Wanker Engineering
    PO Box 9816
    Auckland,  3522
    New Zealand
    3530912167      Fax -- 
    Technical Contact:
    Engineering, Wanker  ...
    Wanker Engineering
    PO Box 9816
    Auckland,  3522
    New Zealand
    3530912167      Fax -- 
    Domain servers in listed order:
    NS1.LYNXWEBHOSTING.COM
    NS2.LYNXWEBHOSTING.COM
    Registrant:
    Robert Woodley
    Robert Woodley Internet
    PO Box 4634
    Port Vila,  8621
    Vanuatu
    Registered through: Go Daddy Software (http://www.godaddy.com)
    Domain Name: TIMEART.NET
    Created on: 16-Mar-01
    Expires on: 16-Mar-04
    Last Updated on: 16-Mar-03
    Administrative Contact:
    Woodley, Robert  ...
    Robert Woodley Internet
    PO Box 4634
    Suite 205
    Port Vila,  8621
    Vanuatu
    (772) 594-2421      Fax -- (772) 594-2421
    Technical Contact:
    Woodley, Robert  ...
    Robert Woodley Internet
    PO Box 4634
    Port Vila,  8621
    Vanuatu
    (772) 594-2421      Fax -- (772) 594-2421
    Domain servers in listed order:
    NS1.MYDOMAIN.COM
    NS2.MYDOMAIN.COM
    NS3.MYDOMAIN.COM
    NS4.MYDOMAIN.COM
    Registrant:
    Robert Woodley
    PO Box 4573
    Grand Cayman,  871251
    Cayman Islands
    Registered through: Go Daddy Software (http://www.godaddy.com)
    Domain Name: WOTEVA.COM
    Created on: 16-Mar-00
    Expires on: 16-Mar-04
    Last Updated on: 16-Mar-03
    Administrative Contact:
    Woodley, Robert  ...
    Robert Woodley Internet
    PO Box 4573
    Grand Cayman,  87125
    Cayman Islands
    (772) 594-2421      Fax -- (772) 594-2421
    Technical Contact:
    Woodley, Robert  ...
    Robert Woodley Internet
    PO Box 4753
    Suite 205
    Grand Cayman,  87125
    Cayman Islands
    (772) 594-2421      Fax -- (772) 594-2421
    Domain servers in listed order:
    NS1.MYDOMAIN.COM
    NS2.MYDOMAIN.COM
    NS3.MYDOMAIN.COM
    NS4.MYDOMAIN.COM
    

    spam google security

    Habeas Suing (Alleged) Spammers

    Habeas: Avalend, Intermark Media, BigDogSecrets.com, Clickbank, and Keynetics Sued for Using Counterfeit Habeas Trademark to get Unwanted Email Through, Trademark Infringement, and Breach of Contract.

    The first suit, against Avalend and Intermark Media, alleges infringement of the Habeas trademark, including infringing use of the Habeas trademark in email in order to help ensure its delivery. The second lawsuit, against Heller, Stuchinski, Clickbank and Keynetics, includes a breach of contract claim against Heller, based on the signing of a Habeas license and then using the Habeas trademark in email which did not comply with the Habeas license. The companies advertised in Heller's email are named as co-defendants.

    Sweet. Sounds like the first two are alleged to have out-and-out forged the mark without a license, and the latter three are alleged to have gained a license and breached it. Habeas' business model relies on successful enforcement, and actively being a threat against spammers who attempt to abuse their mark. I hope this goes well for them.

    BTW, for folks who cannot countenance the idea of paying for a mark to send bulk mail: Habeas' model is just like that of Underwriters Laboratories, which performs (physical) product safety testing, and provides a mark to certify that a product has passed those tests -- and can therefore be judged 'safer' than products that do not have the mark. In Habeas' case, instead of a product's safety, they vouch for a mail's non-spamminess.

    It's not a 'mail protection racket' -- it's a way for you to send a mail saying 'this trustworthy agency has vouched that this is not spam'. And if I trust Habeas, it allows me to extend that trust to you, even if I've never heard of you before.

    patents swpats spam

    'Calibrate Me, Dick'

    The Guardian notes the latest bizarre phraseology to emerge from the White House -- Calibrate me, Dick:

    From Donald Rumsfeld - the man who brought you known unknowns and unknown unknowns - comes a phrase so disorienting in its weirdness that even seasoned Rumsfeldologists have been taken aback by its increasingly frequent use at Pentagon briefings. Uttered one way, it sounds combative like Dirty Harry; uttered another, camp like Austin Powers.

    In fact, it appears to be just a hi-tech, precision-guided version of 'correct me if I'm wrong', the Dick in question being General Richard Myers, chairman of the joint chiefs of staff. Worryingly, 'Calibrate me' is also the name of a song by the scary indie rock group Atombombpocketknife: could Rumsfeld be a fan?

    Typical recent usage: 'The Republican Guard has - calibrate me, Dick - they pulled south in the north and they went north in the southern portion of the country.'

    Context in which it almost certainly did not occur, circa 2002: 'Calibrate me, Dick, but I really don't think we're going to need all that much heavy infantry to take Baghdad, are we?'

    us-politics funny politics

    Portuguese TV Journalists Beaten Up By US Military Police

    Reporters From Portuguese Television Tortured By US Military Police (Indymedia):

    Two Western journalists have arrived safely back in Kuwait City after being arrested, beaten up and deprived of food and water in Iraq -- by members of the US Army's military police. ....

    Despite possessing the proper 'Unilateral Journalist' accreditation issued by the Coalition Forces Central Command, both journalists were detained. ...

    Castro and Silva entered Iraq 10 days ago. They had been to Umm Qasr and Basra and were traveling to Najaf when they were stopped by the military police. According to Castro, their accredited identification was checked and they were given the all clear to proceed. 'Suddenly, for no reason, the situation changed,' Castro told Arab News. 'We were ordered down on the ground by the soldiers. They stepped on our hands and backs and handcuffed us.

    'We were put in our own car. The soldiers used our satellite phones to call their families at home. I begged them to allow me to use my own phone to call my family, but they refused. When I protested, they pushed me to the ground and kicked me in the ribs and legs.' ....

    After being held for four days, they were transported to the 101st Airborne Division to be escorted out of Iraq.

    privacy politics history

    linky goodness from th' oul' sod

    So it looks like Sarah Carey, a good friend of me mate Lean, has a blog, and it's a great one too! Excellent. Added to the Irish blogroll on the right.

    In other news, Simon Boyle got in touch to mention that the Saddam's top tips for tourists interview in the Fermanagh-based Impartial Reporter was actually written by an contemporary of ours at TCD by the name of Maria Rolston. Apparently she's good mates with my mate Wooder, too. Simon notes:

    She's the intrepid impartial reporter who wrote the story (and who's had it reprinted minus attribution all over the world now). Oh the joys of being a first year reporter on a small local paper...

    While we're talking about small local papers, might as well note - tangentially - that Ireland's local press has a long history of bizarre stories. One favourite, in particular, has gone down in journo legend (and Ulysses): the 19th-century editorial from The Skibbereen Eagle, which solemnly told Lord Palmerston that it had 'got (its) eye both upon him and on the Emperor of Russia.' Classic.

    ireland history funny dublin

    IP company hoist by own petard

    Forbes: A Patent On Porn. It seems Acacia Research, an intellectual-property 'shell' company, has a bunch of crappy software patents on streaming media (to go with their patent on the 'V-Chip', remember that?).

    Things haven't been going too good recently. Apparently, they decided to 'monetize' these streaming-media patents -- in other words get all Sopranos on a bunch of small players, namely 700 porn site operators, sending some legal threats to 'pay up -- 1-2% of gross -- or get sued' their way.

    What happened? Did the pr0nsters roll over and cough up? Not a hope.

    Eight firms (of 700) agreed to Acacia's terms. But 40 didn't, and Acacia promptly slapped them with lawsuits. Rather than buckling, though, several of the porno sites joined together and stood their ground. Now Acacia is in the fight of its life and may even face a shareholder revolt as a result.

    Read on for the rest...

    swpats patents internet ireland web

    Comment links back again

    the (discuss) links are back, and about time too, things were getting quiet. Anyway, it's a unified comments forum now. All posts go into one forum, instead of creating a new forum for each weblog posting. Having comments pages for each story just didn't work for a small-scale blog -- and it was impossible to see if there was any new posts for all those individual forums.

    meta blogs Links

    Interconnect speed cheat-sheet

    posting this so the googlebrain will pick it up next time I need to find it -- Padraig Brady's interconnect speed cheat sheet. It lists a whole stack of interconnect protocols, from 802.11b, 10Mb/s LAN, to SPP parallel port, to 8mm DAT tape, along with their effective transfer rates in megabytes per second. (I never realised Bluetooth was only as fast as SPP parallel ports -- 0.1MB/s. That sucks.)

    networking linux hardware optimization

    Saddam Hussein's top tips for tourists

    Newsflash! Irish local newspapers come through with bizarre-ness yet again:

    Fermanagh man Tom Daly (72) is a former schoolteacher and lecturer who spent 15 years working in the Middle East. In an interview with the paper Mr Daly told how in 1988 he arrived in Baghdad and was on his way to the city of Basra ...

    'All these taxi drivers were coming down to me offering to take my bags and drive me down to Basra for 60 quid and I wasn't sure what to do. Then a man in a long dark coat came over to me, put his hand up and said: 'Don't listen to them. Take a taxi (sic), it will cost you £10'. I thought this was a much better idea and was glad of the help. All the taxi drivers had also backed away so I asked some of them afterwards: 'Who was that man?'

    They said: 'That was Mr Saddam Hussein'.'

    Tune in next week, when Saddam helps out with some tricky carpet-buying negotiations...

    Date: Mon, 31 Mar 2003 09:21:19 +0100
    From: Joe McNally ...
    To: Yahoogroups Forteana ...
    Subject: And on the lighter side...

    http://www.irishnews.com/access/daily/current.asp?SID=429949

    Irish farmer is 'a cut above the rest'

    Paper Clips: A round-up of the weekly press

    By Tony Bailie

    MOST of the north's regional papers again carried stories last week giving a local perspective on the war in Iraq, but the most remarkable was in the Impartial Reporter.

    Fermanagh man Tom Daly (72) is a former schoolteacher and lecturer who spent 15 years working in the Middle East.

    In an interview with the paper Mr Daly told how in 1988 he arrived in Baghdad and was on his way to the city of Basra to take up a lecturing post.

    He told the paper: "I had just flown into the country and landed at Baghdad airport in the dead of night. I took a taxi to the bus station to make my way down to Basra which was about 60 kilometres away.

    "All these taxi drivers were coming down to me offering to take my bags and drive me down to Basra for 60 quid and I wasn't sure what to do.

    "Then a man in a long dark coat came over to me, put his hand up and said: 'Don't listen to them. Take a taxi (sic), it will cost you £10'.

    "I thought this was a much better idea and was glad of the help. All the taxi drivers had also backed away so I asked some of them afterwards: 'Who was that man?'

    and they said: 'That was Mr Saddam Hussein'."

    According to the Larne Times the borough council found itself in an awkward position because of the war.

    The town, which is due to host Iraqi athletes during the Special Olympics in June, had put up a sign declaring: "Larne Host Town to Iraq".

    However, according to the paper the wife of a serving British soldier, currently in southern Iraq, objected and called for the sign to be taken down.

    The paper reported: "She said she felt the wording of the sign and the timing of its erection was 'inappropriate'."

    "Others took more direct action, however, spray painting the head of the town sign 'No Way'." A few days later the words "Ulster Says No" where added.

    According to the Larne Times the sign was subsequently removed, a decision described by Larne Borough Council chief executive Colm McGarry as "common sense".

    The soldier's wife who lodged the objection stressed that she had no objections to the Special Olympics.

    "It was the wording of the sign that annoyed me - I nearly crashed my car when I saw it," she told the paper.

    However, Larne's mayor, Councillor Bobby McKee, told the paper that while he sympathised with the objectors he believed the sign should have stayed up.

    "The war is against Saddam Hussein and his regime, not against disabled people. I find great difficulty in getting my head around any opposition to people with a disability,'' he told the paper.

    -- Joe McNally :: Flaneur at Large :: http://www.flaneur.org.uk

    ireland politics funny

    SpamAssassin Needs Your Help!

    while thinking about the CDT's report on spammer address-scraping techniques again, it occurred to me that one finding is very significant; high-traffic websites probably get much more spam than low-traffic ones.

    Now, I've got spamtraps up on pretty much all my sites, using a variety of methods:

    • plain mailto links, with instructions to human users not to use them (don't mail that one either, obviously ;)
    • hidden mailto links in the page's <head> block (browsers will not display text elements outside the <body> block)
    • hidden mailto links in a <!-- HTML comment -->
    • empty mailto links in the text (ie. <a href="mailto:foo></a>)
    • mod_rewrite pages, which are displayed to spam-scraping bots instead of the real thing

    But all my sites are small-time, really. ;) So -- anyone out there in the blogosphere care to help out the SpamAssassin project, by feeding us trapped spam? It'd be simply a matter of adding a mailto: link, hidden in a comment on a prominent page of your high-traffic website. Gimme a mail to this address if you do.

    (warning: that address will expire in 6 months. if you're reading this after Aug 2003, use the addr on this page instead.)

    The spam trapped in such a way is fed into a number of spamtrap-fed network systems, like Razor, DCC, Pyzor, and the Blitzed OPM blacklist. It's also used during the SpamAssassin score-regeneration process.

    anti-spam spamassassin weblogs

    Regular expressions win again

    Rael: secrets of the XML gods:

    In response to Tim Bray's dirty little habit of parsing XML with regular expressions, Jon Udell writes: 'If the XML gods are resorting to Perl and Python hackery to shred documents, are we just spinning our wheels? I don't think so. But this is, perhaps, an unusual case. ... I can, however, make excellent use of the text stream underlying XML abstractions. So, which way to regard a document becomes a kind of Necker cube puzzle. The bad news: it's confusing. The good news: it's useful.'

    .... I just co-authored a book, 1/4 of which relied heavily on the availability of not only an XML parser, but a SOAP stack. Faced with the reality that more than a handful of readers wouldn't have either at their disposal, I wrote a hack sure to turn the stomach of any XML purist while turning many a hacker frown upside-down... 'NoXML, Another SOAP::Lite Alternative' for the Google Web API. '... NoXML is a drop-in alternative to SOAP::Lite. As its name suggests, this home-brewed module doesn't make use of an XML parser of any kind, relying instead on some dead-simple regular expressions and other bits of programmatic magic. ' Elegant? Depends on your definition. Pure? As the driven beach sand. Work? You betcha!

    And I thought it was just me. ;)

    coding text rob-pike

    Kim Jong Il's IM logs

    Craig links to the livejournal of Kim Jong Il, featuring IM logs with GWB -- very funny.

    Forteana: on a totally unrelated note -- The Lab @ ABC.net.au notes:

    An Australian neuroscientist claims he can conjure up the mysterious Australian outback phenomenon of the Min Min lights, now that he has worked out what causes them.

    Fantastic description of how, exactly, he did this, by using a temperature inversion, and landscape features, to simulate it. Very interesting, and it makes a lot of sense. Another wierd 'floating lights' phenomenon explained... (link via the forteana list, of course).

    The article also discusses the fata morgana__ phenomenon, in which landforms that are beyond the horizon appear to float above it in an inverted form. This is interesting, as it explains the Chinese legend of the Blessed Isles, which says that there's a group of islands that appears infrequently floating above the sea, shaped like mushrooms (if I recall correctly, can't find much about it online).

    science weather funny australia

    BBC: 'more truth out of Baghdad than the Pentagon at the moment'

    BBC news chiefs have met to discuss the increasing problem of misinformation coming out of Iraq as staff concern grows at the series of premature claims and counter claims by military sources. 'By last Sunday the southern Iraqi seaport of Umm Qasr had been reported 'taken' nine times' ... 'We're getting more truth out of Baghdad than the Pentagon at the moment'.

    Date: Fri, 28 Mar 2003 09:05:27 +0000
    From: "Tim Chapman" ...
    To: forteana ...
    Subject: Fun with disinformation

    http://media.guardian.co.uk/broadcast/story/0,7493,924169,00.html

    BBC chiefs stress need to attribute war sources

    Claims and counter-claims in the media

    Ciar Byrne Friday March 28, 2003

    BBC news chiefs have met to discuss the increasing problem of misinformation coming out of Iraq as staff concern grows at the series of premature claims and counter claims by military sources.

    As a result the corporation has reinforced the message to correspondents that they must clearly attribute information to the military when it has not been backed up by another source.

    "There's been a discussion about attribution and it's been reinforced with people that we do have to attribute military information," said a BBC spokeswoman.

    "We have to be very careful in the midst of a conflict like this one to be very sure when we're reporting something we've not seen with our own eyes that we attribute it," she added.

    On nearly every day of the war so far there have been reports that could be seen as favourable to coalition forces, which have later turned out to be inaccurate.

    Earlier this week there was confusion over whether there had been an uprising in the key southern city of Basra. A British forces spokesman, Group Captain Al Lockwood, said on Thursday there had been a "popular uprising", but this was denied by Iraqi authorities.

    By last Sunday the southern Iraqi seaport of Umm Qasr had been reported "taken" nine times, while reports of the discovery of a chemical weapons factory in An Najaf have not been confirmed - just two more examples of the confusion over what is coming out of military sources.

    "We're absolutely sick and tired of putting things out and finding they're not true. The misinformation in this war is far and away worse than any conflict I've covered, including the first Gulf war and Kosovo," said a senior BBC news source.

    "On Saturday we were told they'd taken Basra and Nassiriya and then subsequently found out neither were true. We're getting more truth out of Baghdad than the Pentagon at the moment. Not because Baghdad is putting out pure and morally correct information but because they're less savvy about it, I think.

    "I don't know whether they (the Pentagon) are putting out flyers in the hope that we'll run them first and ask questions later or whether they genuinely don't know what's going on - I rather suspect the latter."

    Earlier this week the BBC's director of news, Richard Sambrook, admitted it was proving difficult for journalists in Iraq to distinguish truth from false reports, and that the pressures facing reporters on 24-hour news channels had led to premature or inaccurate stories.

    Veteran war correspondent Martin Bell has called for 24-hour news channels to "curb their excitability'' and warned against unsubstantiated reports which may help the allied cause, but later turn out to be false.

    The Times journalist Janine di Giovanni has also said that the demands of real-time television, combined with the restrictions placed on reporters in Baghdad by the Iraqis and the difficulties of getting to the front line are making it virtually impossible for journalists to cover the war properly.

    politics google law

    Network Solutions the weakest link, again

    Yahoo: al-Jazeera website redirected:

    The hacker was able to gain control of the domain name by asking domain seller Network Solutions for the account password on official al-Jazeera stationery, said an industry source speaking on condition of anonymity.

    A spokesman for Network Solutions' parent company declined to comment on how the hacker was able to hijack the domain name, but said the company had fixed the problem and was trying to track the impostor down.

    'We followed our procedures, in this particular instance someone was able to get around those procedures,' said Brian O'Shaughnessy, a spokesman for Internet security firm VeriSign.

    They fixed the problem? Surely this is exactly what happened with the sex.com domain several years ago?

    spam http censorship domains

    rottenflesh: freshmeat gets parodied

    Rottenflesh.net, a piss-take of Freshmeat.net (found via Sweetcode).

    About: openJ-GNU is a web secure server that quickly generates backgrounds. It uses mv for menubars. openJ-GNU generates user-interfaces.

    Changes: openJ-GNU 3.24.7 enhances robustness for sites that also use newGeekNr. It also was rewritten in Tcl and patches a remote root bug in configuration. One of the developers was sacked. It also compiles.

    politics nsa privacy

    The Problem with Anti-spam Challenge-Response Systems

    A great summary of the issues surrounding challenge-response anti-spam systems, from Kee Hinckley on the ASRG list. Summary: they'll work fine for one-person-to-one-person email, but anything beyond that -- and there is lots beyond that, in current email use -- gets hairier and hairier. Read on for the message.

    Date: Tue, 25 Mar 2003 09:13:46 -0500
    From: Kee Hinckley ...
    To: Brad Templeton ...
    cc: Steve Schear ... ...

    ... Subject: Re: FC: Will new "spam reduction" service result in... more spam?

    At 5:32 PM -0800 3/24/03, Brad Templeton wrote:
    > I wrote a challenge/response system six years ago that simply asks for any
    > reply at all -- it doesn't put any burden on the other party, and would be
    > easy to defeat with something as simple as an autoresponder. Yet it works,
    > the spammers have not attempted to use this simple defeat. Once they start,

    If a challenge response system puts messages in the "look at me later" queue if you don't respond, then I don't think spammers will care. (And it's not clear that you'll be that much happier as a user of the system. You will have to scan the queue.)

    Why is not clear to me is a) how anyone expects your typical user to whitelist commercial addresses and mailing lists in advance and b) how a challenge response system (which had *better* respond to envelope from) avoids getting them removed from said list, or not receiving notification about their purchase or what not.

    Just consider the following.

    (jm note: I've replaced at signs with (AT) in the text below, as otherwise this blog software's anti-spam features will hide the addresses.)

    1 User sends email to asrg-request (AT) ietf.org?subject=subscribe

    2 Think quick. What address should you whitelist? asrg (AT) ietf.org? asrg-request (AT) ietf.org? Nope. asrg-admin (AT) ietf.org. And you knew that because...?

    3 asrg sends back a confirmation request. Now as it happens, it does this from asrg-admin (AT) ietf.org (envelope) and asrg-request (from). But some mailers use a custom address for this. But let's assume we're dealing with the average user here. They either didn't do anything at all (forgot they had to) or their software whitelisted based on the To: address (asrg-request).

    4.1 A challenge gets sent back to the asrg list. The result depends on a combination of how the list software works and how the challenge software constructed its reply.

    4.1.1 It's treated as a bounce and the user is not added

    4.1.2 It's treated as a confirmation and the user is added

    4.1.3 It goes to the admin, who says something I can't repeat and throws it in the trash.

    4.2 It makes it through because we whitelisted the right thing.

    5 The first list message comes through. If you had whitelisted asrg-admin, you're fine. If you whitelisted asrg-request, we challenge it. If the list software uses a different envelope from each time, you got problems.

    Now, let's take amazon.com.

    I've received automated email from payments-messages (AT) amazon.com, orders (AT) amazon.com, auto-confirm (AT) amazon.com, eyes (AT) amazon.com, amazon-news-sender (AT) amazon.com, editer-sender (AT) amazon.com, science-fiction-editor (AT) amazon.com... and they actually send mail from their domain--never mind what happens if they higher m0.net or someone to deliver it.

    And if you start sending challenges to those--Amazon's going to see them as bounces and dump me.

    Of course we could just whitelist all of amazon.com. But I rather suspect the spammers might figure that one out.

    If you want challenge/response to work, the first thing you should do has nothing to do with challenge/response. The first thing is to come up with an RFC for a standard format for challenges so that automated mail systems can recognize that they aren't the same as bounces. And come up with a protocol whereby they can reply and say "Yo! I'm an automated system you idiot." Where you go from there I don't know.

    However, see my next message on "Protocols".

    -- Kee Hinckley http://www.puremessaging.com/ Junk-Free Email Filtering http://commons.somewhere.com/buzz/ Writings on Technology and Society

    I'm not sure which upsets me more: that people are so unwilling to accept responsibility for their own actions, or that they are so eager to regulate everyone else's.


    Asrg mailing list ... https://www1.ietf.org/mailman/listinfo/asrg

    anti-spam spam challenge-response backscatter email spamassassin smtp bounces

    Robin Cook's viewpoint

    Robin Cook, who resigned from the UK cabinet last week:

    ... If you take a response to 9/11 as being a driving force of the American approach to international affairs, I would strongly argue that one of the greatest assets that came out of that was the extraordinarily rich and powerfully diverse coalition against international terrorism.'

    That coalition, according to Cook, has now been shattered on the altar of pre-emptive diplomacy. America has long planned to attack Iraq and splits in the UN, Nato and in the European Union were a price worth paying.

    'Now, I'm not an American politician but if I was I would be inveighing against the extent to which the Bush administration had allowed that terrific asset to disintegrate,' Cook said.

    'Instead the US is left embarking on military action from a position of diplomatic weakness, unable to get any major international organisation to agree with it. We are heading for a very serious risk of a big gulf between the Western and Islamic world. That seems to me to have thrown away a powerful asset for the US which relates to its number one security concern.'

    Also, some history (thanks to Dan Brickley for forwarding this): Ireland as the pivot of a league of nations, written by Michael Collins in 1921, shortly after Ireland's declaration of independence from the UK:

    Into such a League might not America be willing to enter? By doing so America would be on the way to secure the world ideal of free, equal, and friendly nations on which her aspirations are so firmly fixed. Ireland's inclusion as a free member of this League would have a powerful influence in consolidating the whole body, for Ireland is herself a mother country with world-wide influences, and it is scarcely to be doubted that were she a free partner in the League as sketched the Irish in America would surely wish America to be associated in such a combination. In that League the Irish in Ireland would be joined with the Irish in America, and they would both share in a common internationality with the people of America, England, and the other free nations of the League. Through the link of Ireland a co-operation and understanding would arise between England and America, and would render unnecessary those safeguards which England wishes to impose upon Ireland and which by preserving an element of restraint might render less satisfactory the new relations between the two countries.

    It's incredible to consider how much has changed in world politics since those words were written 82 years ago.

    And finally, some humour: Power Phillips Home Page:

    Powers Phillips, P.C., is a small law firm located in downtown Denver, Colorado within convenient walking distance of over fifty bars and a couple of doughnut shops. Powers Phillips also maintains a small satellite office-in-exile on the cow-covered hillsides near Carbondale, Colorado, where it puts out to pasture some of its aging attorneys.

    The firm is composed of lawyers from the two major strains of the legal profession, those who litigate and those who wouldn't be caught dead in a courtroom.

    Litigation lawyers are the type who will lie, cheat and steal to win a case and who can't complete a sentence without the words 'I object' or 'I demand another extension on that filing deadline.' Many people believe that litigation lawyers are the reason all lawyers are held in such low esteem by the public. Powers Phillips, P.C. is pleased to report that only three of its lawyers, Trish Bangert, Tom McMahon, and Tamara Vincelette are litigation lawyers, and only one of them is a man.

    And it gets worse from there on.

    ireland nsa coding

    The Perils of 'Raw' News

    Mark Lawson in today's Guardian:

    This time, digital satellite viewers can even use their red interactive buttons to call the shots of the shots: zapping between battle zones and international capitals like a James Bond baddie watching the world come down on 30 TV screens in his underground bunker... We belong to a generation which has largely ceased to be surprised by television, but think about this: those who wanted to were able to watch an enemy operation live from the banks of the Tigris. This weekend's pictures have widened the eyes like nothing since the moon landings, though with rather greater moral complications. The essential problem is that in seeming to know everything, we know nothing. There are wise old journalists who will tell you that the word 'raw' is usually a warning. It is unwise to eat raw meat or smell raw sewage and it may be equally foolish to consume raw news coverage.

    Forwarded by Tim Chapman on the forteana list.

    Kind of irrelevant to me, seeing as I'm now based in the US, and the concept of unbiased, unfiltered TV news doesn't really seem to exist over here.

    Instead, the war coverage consists of an endless array of human interest stories with the troops and whizz-bang explosion footage. There's absolutely no interpretation, apart from what it might imply for relatives of the US servicemen involved -- that's it. As far as I can see, there is no real liberal news, or a balancing viewpoint, on TV over here.

    In about 3 hours of news on TV, I think I saw one opposing viewpoint, 5 minutes with ex-senator George McGovern. That was it.

    I'm finding this to be a serious culture shock. Thankfully, I've got the web to read and listen to the European stuff instead, so I'm doing that instead. The old Barlow line about the internet and censorship springs to mind...

    politics news internet media history google ireland

    zkjl IMPORTANT information on NOT DYING!!! kfdjsd aowopqq (fwd)

    Ben notes this passage from this SFGate story:

    '(Saddam's) generals have been getting personal messages, including e-mail and cell phone calls, urging them not to fight.'

    Then speculates exactly what such a message might look like...

    Date: Thu, 20 Mar 2003 12:30:18 -0800
    From: ben ...
    Subject: speculation

    Dear friend,
    This is for real!!!!!!!!!!!!1
    ================================================
    ================================================
    This is a ''ONE-TIME MESSAGE'' you were randomly
    selected to receive this.  There is no need to reply
    to remove, you will receive no further mailings from
    us.  If you have interest in this GREAT INFORMATION,
    please do not click reply, use the contact information
    in this message. Thank You! :-)
    ================================================
    ================================================
    * Print This Now For Future Reference *
    The following opportunity is one you may be interested
    in taking a look at.  It can be started with VERY
    LITTLE risk and the return is TREMENDOUS!!!
    $$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$$
    You are about to not get killed by the most powerful
    military force in the world.
    Please read the enclosed program...THEN READ IT
    AGAIN!!!
    <>  <>  <>  <>  <>  <>  <>  <>  <>  <>  <>  <>  <>  
    The enclosed information is something I almost let
    slip through my fingers.Fortunately, sometime later I
    re-read everything and gave some thought and study to
    it.
    My name is Major Hassan al-Ramidi. Twelve years ago,
    the unit I commanded at for the past twelve years was
    eliminated. After unproductively wandering around in
    the desert in terror for a while, I incurred many
    unforeseen problems. Enormous numbers of men and
    high-tech weapons surrounded me and were trying to
    kill me. I truly believe it was wrong for me to be in
    trouble like this.  AT THAT MOMENT something
    significant happened in my life and I am writing to
    share my experience in hopes that this will change
    your life FOREVER!!!
    In mid-December, I received this program via email.  I
    had been sending away for information on various
    opportunities for not dying.  All of the programs I
    received, in my opinion, were not practical.  They
    were either too difficult for me to comprehend or they
    involved me getting killed by the US military or dying
    of thirst in the desert. 
    But like I was saying, in December I received this
    program.  I didn't send for it, or ask for it, they
    just got my name off a mailing list. THANK GOODNESS
    FOR THAT!!!  After reading it several times, to
    make sure I was reading it correctly, I couldn't
    believe my eyes.  Here was a NOT GETTING KILLED
    PHENOMENON.
    After I got a pencil and paper and figured it out, I
    at least had a chance of not dying horribly and
    painfully.  After determining that the program is
    LEGAL and NOT A CHAIN LETTER, I decided ''WHY NOT''.
    I AM LIVING PROOF THAT IT WORKS !!!
    

    history politics funny

    precision mincemeat manufacture

    IraqBodyCount.net on the JDAM bomb:

    The B-2 bomber carries sixteen 2'000 lb. JDAM bombs. If all goes 100% as planned (the bomb does not fall outside of its specified margin of error of 13 meters, and the GPS guidance system is not foiled by a $50 radio jammer kit, easily purchased), then here is what one such bomb does :
    • everyone within a 120 meter radius is killed;
    • to be safe from serious shrapnel damage, a person must be at least 365
      • meters away;
    • to be really safe from all effects of fragmentation, a person must be 1000 meters away, according to Admiral Stufflebeem.

      The B-2s will be used upon targets within Baghdad.

      -Prof Marc W. Herold, IBC Project Consultant

    Sounds like the perfect weapon for use in tight city streets. :(

    terrorism privacy aws

    blogging Dengue fever

    Thank ghod this is one experience of SE Asia I missed. I came across this blog through some random blog-hopping last night; it's two farang tourists blogging their backpacking trip through the region. All great fun until they both catch Dengue fever:

    Dengue is commonly called 'break bone fever', and I found out why at about 2 AM on the train. I woke up with a 102 fever, in the most intense pain I can recall having in years. Everything hurt, but especially my back and legs. Harper later described the sensation as one of having someone scrape your bones with a knife, and that sounds about right.

    Jesus. I am so thankful I missed out on that particular aspect (a mild bout of food poisoning with a fever of 104 was all I had to put up with!)

    Dengue fever is endemic to many parts of the region, even Bangkok , the capital city of Thailand. It gets a lot less attention than malaria, since it's not fatal in the vast majority of cases (unless you get the rarer haemorrhagic version), but it is excruciating by all accounts, and I've met quite a few travellers who've met someone who caught it. Unfortunately there's not much you can do to avoid it but slather on the DEET, cover up, and hope for the best.

    health healthcare papers

    On a lighter note...

    Well, despite the covert bugging of the European Council offices of 3 major EU delegations, the apparatus of some states, at least, is bringing a smile to my face. The German federal secret service, the Bundesnachrichendienstes (BND), has just published Topf Secret, their official cookbook. Really. The Guardian notes:

    The book consists of recipes sent in from around the world by German spies in the field. Thus, there are two recipes from Iraq, several from central Africa, the Philippines and Scotland.

    Again, more questions than answers. The Germans have spies in Scotland? Do they really eat haggis? ('Attention: fill only 2/3 of the stomach since the oat flour will expand. If the stomach is too full it can explode while cooking!') Do the two recipes from Iraq - for fattousch and tabouleh - have to be so boring (use only crunchy lettuce leaves for the fattousch)? Why are there German agents in Iraq? What are they doing in the US as well, and do they like that nation's recipe for pumpkin pie?

    food ireland internet privacy law

    The Beeb via the 'net

    wow, the Beeb fed 29,200 simultaneous RealMedia streams at one point today; that breaks down to 18,400 listeners in the UK, 12,800 elsewhere in the world.

    Since getting back to bandwidth, I've been listening to a lot of Radio 4, waking up to the Today programme in particular. Definitely recommended; nothing like a few clipped RP tones to fill you in on all the details.

    Also recommended: the Beeb's live streams collection, featuring all the FM and digital-radio stations streamed with excellent quality. Who needs Napster when you've got internet radio ;)

    bbc ireland music

    Maximum turd length standardized by NASA

    for your delectation, I present the NASA standard for acceptable turds in space: 'c) The fecal collector shall accommodate a maximum BOLUS length of 330 mm (13 in).'

    My favourite bit: 'd) Quantities in excess of these amounts shall not result in an unrecoverable condition.' I should hope not!

    Thanks to James Rogers on the FoRK list for this fine source of bits...

    funny science health

    The second coming -- as a fish

    The Guardian reports that 'an obscure Jewish sect in New York has been gripped in awe by what it believes to be a mystical visitation by a 20lb carp that was heard shouting in Hebrew, i n what many Jews worldwide are hailing as a modern miracle.' ... 'According to two fish-cutters at the New Square Fish Market, the carp was about to be slaughtered and made into gefilte fish for Sabbath dinner when it sudden ly began shouting apocalyptic warnings in Hebrew.'

    Date: Sun, 16 Mar 2003 10:14:20 +0000
    From: "Dohrn List" ...
    To: ...
    Subject: God reveals himself as a fish

    Word is made flesh as God reveals himself... as a fish

    Edward Helmore New York Sunday March 16, 2003 The Observer

    An obscure Jewish sect in New York has been gripped in awe by what it believes to be a mystical visitation by a 20lb carp that was heard shouting in Hebrew, i n what many Jews worldwide are hailing as a modern miracle.

    Many of the 7,000-member Skver sect of Hasidim in New Square, 30 miles north of

    Manhattan, believe God has revealed himself in fish form. 
    

    According to two fish-cutters at the New Square Fish Market, the carp was about

    to be slaughtered and made into gefilte fish for Sabbath dinner when it sudden
    

    ly began shouting apocalyptic warnings in Hebrew.

    Many believe the carp was channelling the troubled soul of a revered community elder who recently died; others say it was God. The only witnesses to the mysti cal show were Zalmen Rosen, a 57-year-old Hasid with 11 children, and his co-wo rker, Luis Nivelo. They say that on 28 January at 4pm they were about to club t he carp on the head when it began yelling.

    Nivelo, a Gentile who does not understand Hebrew, was so shocked at the sight o f a fish talking in any language that he fell over. He ran into the front of th e store screaming: 'It's the Devil! The Devil is here!' Then the shop owner hea rd it shouting warnings and commands too.

    'It said "Tzaruch shemirah" and "Hasof bah",' he told the New York Times, 'whic h essentially means that everyone needs to account for themselves because the e nd is near.'

    The animated carp commanded Rosen to pray and study the Torah. Rosen tried to k ill the fish but injured himself. It was finally butchered by Nivelo and sold.

    However, word spread far and wide and Nivelo complains he has been plagued by p hone calls from as far away as London and Israel. The story has since been ampl ified by repetition and some now believe the fish's outburst was a warning abou t the dangers of the impending war in Iraq.

    Some say they fear the born-again President Bush believes he is preparing the w orld for the Second Coming of Christ, and war in Iraq is just the opening salvo

    in the battle of Armageddon. 
    

    Local resident Abraham Spitz said: 'Two men do not dream the same dream. It is very rare that God reminds people he exists in this modern world. But when he d oes, you cannot ignore it.'

    Others in New Square discount the apocalyptic reading altogether and suggest th e notion of a talking fish is as fictional as Tony Soprano's talking-fish dream

    in an episode of The Sopranos . 
    

    Stand-up comedians have already incorporated the carp into their comedy routine s at weddings. One gefilte company has considered changing it's slogan to: 'Our

    fish speaks for itself.' 
    

    Still, the shouting carp corresponds with the belief of some Hasidic sects that

    righteous people can be reincarnated as fish. They say that Nivelo may have be
    

    en selected because he is not Jewish, but a weary Nivelo told the New York Time s : 'I wish I never said anything about it. I'm getting so many calls every day , I've stopped answering. Israel, London, Miami, Brooklyn. They all want to hea r about the talking fish.'

    A devout Christian, he still thinks the carp was the Devil. 'I don't believe an y of this Jewish stuff. But I heard that fish talk.'

    He's grown tired of the whole thing. 'It's just a big headache for me,' he adde

    1. 'I pull my phone out of the wall at night. I don't sleep and I've lost weigh

    t.'

    Guardian Unlimited © Guardian Newspapers Limited 2003

    funny food usa

    Peter Kay's Observations of Life

    About time I posted this -- everyone who's read 'em agrees vehemently with at least 5 of these; and a quick Google (tm) reveals that this list hasn't ever had a page to itself out there on the interweb. So here it is.

    My personal favourites: 6, 8, 15, 20, 33, and best of all, 28...

    • 1) Triangular sandwiches taste better than square ones.
    • 2) At the end of every party there is always a girl crying.
    • 3) One of the most awkward things that can happen in a pub is when your pint-to-toilet cycle gets synchronised with a complete stranger.
    • 4) You've never quite sure whether it's ok to eat green crisps.
    • 5) Everyone who grew up in the 80's has entered the digits 55378008 into a calculator.
    • 6) Reading when you're drunk is horrible.
    • 7) Sharpening a pencil with a knife makes you feel really manly.
    • 8) You're never quite sure whether it's against the law or not to have a fire in your back garden.
    • 9) Nobody ever dares make cup-a-soup in a bowl.
    • 10) You never know where to look when eating a banana.
    • 11) Its impossible to describe the smell of a wet cat.
    • 12) Prodding a fire with a stick makes you feel manly.
    • 13) Rummaging in an overgrown garden will always turn up a bouncy ball.
    • 14) You always feel a bit scared when stroking horses.
    • 15) Everyone always remembers the day a dog ran into your school.
    • 16) The most embarrassing thing you can do as schoolchild is to call your teacher mum or dad.
    • 17) The smaller the monkey the more it looks like it would kill you at the first given opportunity.
    • 18) Some days you see lots of people on crutches.
    • 19) Every bloke has at some stage while taking a pee flushed half way through and then raced against the flush.
    • 20) Old women with mobile phones look wrong!
    • 21) Its impossible to look cool whilst picking up a Frisbee.
    • 22) Driving through a tunnel makes you feel excited.
    • 23) You never ever run out of salt.
    • 24) Old ladies can eat more than you think.
    • 25) You can't respect a man who carries a dog.
    • 26) There's no panic like the panic you momentarily feel when you've got your hand or head stuck in something.
    • 27) No one knows the origins of their metal coat hangers.
    • 28) Despite constant warning, you have never met anybody who has had their arm broken by a swan.
    • 29) The most painful household incident is wearing socks and stepping on an upturned plug.
    • 30) People who don't drive slam car doors too hard
    • 31) You've turned into your dad the day you put aside a thin piece of wood specifically to stir paint with.
    • 32) Everyone had an uncle who tried to steal their nose.
    • 33) Bricks are horrible to carry.
    • 34) In every plate of chips there is a bad chip.

    ireland memes linux

    laugh and you're dead

    Humour:Guardian: The joke's on Saddam: In northern Iraq, they're laughing at Saddam Hussein. Luke Harding meets two comedians who have dared to cock a snook at the ruthless dictator - and annoyed him so much that he ordered their assassination.

    The film was screened on Kurdish television; and after decades of official repression, it was a huge hit. Saddam's vigilant agents dispatched a CD copy to Baghdad. The Iraqi president was not amused. His response, when it came, was predictable: he sent several assassins to northern Iraq to kill the entire cast. 'Fortunately the guys were all arrested (by the Kurdish authorities),' Hassan recalls. 'They were found carrying a list. All our names were on it.'

    politics funny media

    With your fetlocks flowing in the... wind

    Life imitates Father Ted. It seems the Irish Eurovision entry sounds very similar to the Danish entry from 2000, which, if true, is almost exactly the subject of a classic episode of cult comedy TV show Father Ted, My Lovely Horse.

    Dougal: 'So we wouldn't be stealing the song then?' Ted: 'No, it'd be more like we were keeping their memory alive.' Dougal: 'So if we won we could give the prize money to their relatives?' Ted: 'Yeah, we'll play that by ear.'

    The full low-down on the episode is here. Classic...

    Anyway, I'm now in sunny SoCal, set up with more bandwidth than I've had in over a year. In fact, I'm swimming in bandwidth. Plus a decent pair of speakers for the ol' MP3 collection, at last (my last set are in storage and have been for 3 months)... happy happy joy joy.

    Myself and my cat had a 16-hour flight, and somehow or other, he seems satisfied. Well, I suppose as long as the catfood and lots of petting is forthcoming, life is grass for this fella. Easily satisfied!

    Date: Tue, 11 Mar 2003 17:09:01 +0000
    From: Joe McNally ...
    To: Yahoogroups Forteana ...
    Subject: My Lovely Horse

    http://www.irishnews.com/access/daily/current.asp?SID=428546

    Real life repeat of Father Ted feared

    By Staff reporter

    IRELAND'S Eurovision hope Mickey Joe Harte has rubbished claims that his song bears a close resemblance to Denmark's winning entry of 2000.

    Eurovision fans were complaining of deja vu yesterday when listening to We've Got the World, which will be sung by the Lifford father-of-two. The song - written by Mark Brannigan and Keith Molloy

    • is said to sound eerily like Fly on the Wings of Love, sung by the

    Danish Olsen Brothers three years ago.

    Mickey Joe last night said he 'honestly couldn't see the similarity', but added that the first line of the chorus could be said to resemble the Danish entry.

    Phil Coulter, one of the judges who watched thousands of young hopefuls perform in RTE's You're a Star talent show - which Mickey Joe won on Sunday night - also insisted any similarity between the two songs was purely coincidental.

    But RTE's Joe Duffy radio programme was inundated with calls from listeners who were terrified that Ireland was setting itself up for a Father Ted-like fiasco.

    Listener Frank O'Reilly told Duffy that his daughter Claire, a Eurovision fanatic, spotted the similarity immediately and revealed that the words of one song could be sung over the melody of the second.

    A second listener, called Margaret, also said she and her children had started singing the Danish song in their sitting room on the first night they heard We've Got the World.

    Ironically, an episode of the hit Channel 4 comedy Father Ted featured the title character, played by Dermot Morgan, and his sidekick Fr Dougal, bidding for Eurovision glory with a 'borrowed' song from another Scandinavian country in a previous year.

    Phil Coulter admitted that the Irish song was reminiscent of the Olsen ditty, but insisted there 'was nothing intrinsically original' about the Danish song.

    'There is no question that there is going to be any kind of objection and there is no question that any objection would be upheld,' he added. -- Joe McNally :: Flaneur at Large :: http://www.flaneur.org.uk

    ireland dublin funny

    More on SCO v IBM

    LWN on the case. An excellent commentary, and features this lovely user-posted comment as well:

    'Without access to such equipment, facilities, sophisticated methods, concepts and coordinated know-how, it would be difficult or impossible for the Linux development community to create a grade of Linux adequate for enterprise use.'

    Alan Cox wrote the first SMP version of Linux. Do you know who bought Alan the hardware? It was Caldera :-)

    Not IBM, after all, but Caldera -- who are now part of the SCO group. This usenet posting from 1995 backs that up, as does the Caldera-badged Linux SMP page.

    history linux aws

    'Prestigious Non-Accredited Degree' sites shut down

    The BBC reports that trading standards officials from the UK and US have successfully shut down an Israeli/Romanian/US-based fake-degree spam operation. Or maybe they've just shut down 3 websites, which is all I can see in that report -- that's not going to make a whole lot of difference, so let's hope not.

    Date: Fri, 07 Mar 2003 14:09:32 +0000
    From: "Tim Chapman" ...
    To: forteana ...
    Subject: Bogus degree sites shut down

    http://news.bbc.co.uk/1/hi/education/2829237.stm

    Last Updated:  Friday, 7 March, 2003, 12:19 GMT Bogus degree sites shut down

    Several websites offering fake British degrees for up to £1,000 each have been closed down following a joint operation in the UK and US.

    The certificates, from 14 made-up institutions, were used by hundreds of unqualified people, mainly in North America, to gain jobs in areas such as teaching, computing and childcare.

    The operation, which employed 30 staff in Romania, targeted millions of people every day with circular e-mails.

    Trading standards officers in Enfield, north London, worked with their US counterparts for four years before the US District Court ordered the closure of the sites.

    Investigator Tony Allen said: "It was a difficult operation to crack. The problem was that the people sending out the e-mails weren't conning anyone.

    'Worrying'

    "Those people who bought the degrees knew exactly what they were doing. The complaints we received were actually from colleagues of those who got jobs by lying.

    "It's worrying that they got into such important and responsible positions using the fake degrees."

    Among the institutions created for the websites were the University of Palmers Green, the University of Wexford and Harrington University. The operation, run by a man and a woman, both Israeli, was based at offices in Israel, Romania and the US. It is thought to have made millions of pounds.

    The bogus institutions used a drop box in Green Lanes, London, as a postal address.

    Under the Education Reform Act of 1988 it is an offence to supply a degree unless approved to do so by the Education Secretary.

    Higher education minister Margaret Hodge said: "Many overseas organisations use the UK's name and higher education reputation to offer their own 'degrees' over the internet, so I welcome this action to clamp down on such operations.

    "This demonstrates that action can be taken with the use of international co-operation. I take this matter very seriously.''

    security http internet spam uk law

    SCO sues IBM over Linux

    SCO sues IBM (via Slashdot) . Talk about self-immolation: sue IBM, of all companies, with an intellectual property case. One SCO claim:

    'It is not possible for Linux to rapidly reach Unix performance standards for complete enterprise functionality without the misappropriation of Unix code.'

    Apart from the fact that SMP is just not a state-of-the-art thing any more; things move on! Perhaps if SCO/Novell/USL hadn't sat on their hands for 10 years, swapping IP and suing BSDI, they'd still be in the game. Anyway, here's what the analysts think:

    'It's a fairly end-of-life move for the stockholders and managers of that company,' said Jonathan Eunice, an Illuminata analyst. 'Really what beat SCO is not any problem with what IBM did; it's what the market decided. This is a way of salvaging value out of the SCO franchise they can't get by winning in the marketplace.'

    He said it.

    patents swpats work

    Cough Cheat Millionaire transcript

    The transcript of the "Who Wants To Be A Millionaire" episode at the centre of a current UK court case; the producers claim that the contestant cheated, with the aid of a coughing accomplice. Going by this transcript, it's an open-and-shut case IMO.

    Date: Thu, 06 Mar 2003 09:56:42 +0000
    From: Tom Farrell ...
    To: ...
    Subject: cough cheat millionaire transcript

    The major answered the first three questions, but got into difficulty on question six, using the "ask the audience" lifeline when confronted with a question about Coronation Street. He struggled on the next question about the location of the river Foyle and phoned a friend.

    As the questions became harder, Major Ingram often appeared unsure and wrestled out loud with several options, often going for a different answer from the one he initially appeared to choose.

    Mr Hilliard said there was "a bit of an attempt to make it look like a sweat, some furrowing of the brow ... complete changes of mind coincide with the coughs; if you look at the whole picture, that's what's going on."

    Major Ingram struggled on question eight, when he was asked who Jacqueline Kennedy's second husband had been. On two occasions, when he said the correct answer - Aristotle Onassis - out loud, a cough was heard, which the prosecution claims came from Mr Whittock.

    For £125,000, Major Ingram was asked about the Holbein painting the Ambassadors.

    Major Ingram: "I think I'm going to go for Holbein."

    A cough is heard. Major Ingram says this is his final answer, and is told he is right.

    During the next question there was a series of coughs as Major Ingram struggled with the question.

    Tarrant asked: "What kind of garment is an Anthony Eden? An overcoat, hat, shoe, tie?"

    Major Ingram: "I think it is a hat."

    Cough.

    Major Ingram: "Again I'm not sure. I think it is..."

    Coughing.

    Major Ingram: "I am sure it is a hat. Am I sure?"

    Cough.

    Major Ingram: "Yes, hat, it's a hat."

    To cheers, Tarrant told him it was the right answer. Then for the £500,000 question, he was asked: "Baron Haussmann is best known for his planning of which city? Rome, Paris, Berlin, Athens."

    Major Ingram: "I think it is Berlin. I think Haussmann is a more German name than Italian or Parisian or Athens. I am really not sure. I'm never sure. If I was at home, I would be saying Berlin if I was watching this on TV."

    A loud cough was then heard, and the prosecution claim that Mr Whittock resorted to the "desperate measure" of saying the word "no" under cover of a cough.

    Major Ingram: "I do not think it's Paris."

    Cough.

    Major Ingram: "I do not think it's Athens, I am sure it is not Rome. I would have thought it's Berlin but there's a chance it is Paris but I am not sure. Think, think, think! I know I have read this, I think it is Berlin, it could be Paris. I think it is Paris."

    Cough.

    Major Ingram: "Yes, I am going to play."

    Tarrant: "Hang on, where are we?"

    Major Ingram: "I am just talking to myself. It is either Berlin or Paris. I think it is Paris."

    Cough.

    Major Ingram: "I am going to play Paris."

    Tarrant: "You were convinced it was Berlin."

    Major Ingram: "I know. I think it's Paris."

    Tarrant: "He thought it was Berlin, Berlin, Berlin. You changed your answer
    to Paris. That brought you £500,000. What a man! What a man. Quite an amazing man."

    Then came the £1m pound question: "A number one followed by 100 zeros is known by what name? A googol, a megatron, a gigabit or a nanomole?"

    Major Ingram: "I am not sure."

    Tarrant: "Charles, you've not been sure since question number two."

    Major Ingram: "The doubt is multiplied. I think it is nanomole but it could be a gigabit, but I am not sure. I do not think I can do this one. I do not think it is a megatron. I do not think I have heard of a googol."

    Cough.

    Major Ingram: "Googol, googol, googol. By a process of elimination I have to think it's a googol but I do not know what a googol is. I do not think it's a gigabit, nanomole, and I do not think it's a megatron. I really do think it's a googol."

    Tarrant: "But you think it's a nanomole. You have never heard of a googol."

    Major Ingram: "It has to be a googol."

    Tarrant: "It's also the only chance you will have to lose £468,000. You are
    going for the one you have never heard of."

    Major Ingram: "I do not mind taking the odd risk now and again. My strategy has been direct so far - take it by the bit and go for it. I've been very positive, I think. I do not think it's a gigabit, I do not think it's a nanomole or megatron. I am sure it's a googol."

    Cough.

    Major Ingram: "Surely, surely."

    Tarrant: "You lose £468,000 if you are wrong."

    Major Ingram: "No, it's a googol. God, is it a googol? Yes, it's a googol. Yes, yes, it's a googol."

    Cough.

    Major Ingram: "I am going to play googol."

    After a break, Tarrant said: "He initially went for nanomole, he then went through the various options again. He then went for googol because he had never heard of it and he had heard of the other three. You've just won £1m."

    tv fraud law uk

    Who the fuck is Amanda Perez?

    and why is she spamming me?

    From: "Amanda Perez" amandaperez@virginrecords.com To: 20021202123631.31AB416F1F@jmason.org

    Let's send Amanda Perez and her new video 'Angel' to the top of MTV's Total Request Live!

    I don't think so. How's about reporting her to SpamCop instead?

    Wow, Virgin Records, you are in so much trouble; spamming me with this crap, using a scraped address -- in fact, not even a valid address; it's a Message-Id! That address has never existed to receive mail. Out and out spamming. Unbelievable.

    Update: actually, it's probably nothing to do with Virgin, on reflection; nothing in the headers indicates anything apart from a dialup PacBell customer. So, Virgin Records, sorry for all the shouting ;)

    Return-path: ...
    Delivered-to: ...
    Received: from localhost (jalapeno [127.0.0.1])
    by jmason.org (Postfix) with ESMTP id 4FC7816F17
    for ... Thu,  6 Mar 2003 11:10:38 +0000 (GMT)
    Received: from jalapeno [127.0.0.1]
    by localhost with IMAP (fetchmail-5.9.0)
    for ... (single-drop); Thu, 06 Mar 2003 11:10:38 +0000 (GMT)
    Received: from pavillion (adsl-63-202-108-251.dsl.lsan03.pacbell.net
    [63.202.108.251]) by dogma.slashnull.org (8.11.6/8.11.6) with ESMTP id
    h268Nin26527 for ... Thu,
    6 Mar 2003 08:23:44 GMT
    Message-id: ...
    Mime-version: 1.0
    Content-type: text/plain; charset=''iso-8859-1''
    Content-transfer-encoding: 7bit
    X-spam-status: No, hits=-5.7 required=5.0
    tests=AWL,BAYES_01,CLICK_BELOW,MSG_ID_ADDED_BY_MTA_3,
    RCVD_IN_BL_SPAMCOP_NET,T_BLANK_LINE_RATIO_01_40_50,
    T_BLANK_LINE_RATIO_04_40_50,T_BLANK_LINE_RATIO_08_40_50,
    T_BLANK_LINE_RATIO_20_00_02
    version=2.60-cvs
    X-spam-level: 
    X-spam-checker-version: SpamAssassin 2.60-cvs (1.178-2003-03-03-exp)
    Subject: They put me on MTV!
    From: ''Amanda Perez'' ...
    Date: Thu, 06 Mar 2003 00:32:25 -0800 (08:32 GMT)
    To: ...
    Let's send Amanda Perez and her new video ''Angel'' to the top of MTV's Total Request 
    Live!
    Thanks for helping Amanda get to the top, please try to vote before the week 
    is out, and you can see the results on MTV's TRL.
    Just click on the link below or paste it into your browser's Address window and 
    hit enter to vote for Amanda's video at MTV.com.
    http://www.mtv.com/onair/trl/votevideo.jhtml
    

    spam anti-spam spamassassin

    very nasty new sendmail vulnerability

    Remote Sendmail Header Processing Vulnerability.

    Attackers may remotely exploit this vulnerability to gain 'root' or superuser control of any vulnerable Sendmail server. Sendmail and all other email servers are typically exposed to the Internet in order to send and receive Internet email. Vulnerable Sendmail servers will not be protected by legacy security devices such as firewalls and/or packet filters. This vulnerability is especially dangerous because the exploit can be delivered within an email message and the attacker doesn't need any specific knowledge of the target to launch a successful attack.

    Sendmail versions from 5.79 to 8.12.7 are vulnerable.

    Protection mechanisms such as implementation of a non-executable stack do not offer any protection from exploitation of this vulnerability. Successful exploitation of this vulnerability does not generate any log entries.

    Great...

    security smtp email gmail spam anti-spam

    Recent history of the written word, with William Gibson

    William Gibson, talking about why he uses all-caps book titles, gives a short history lesson regarding the rendering of book titles, back in the age of the mimeograph:

    Much of my earliest typewriting experience had to do with mimeography, a pre-thermocopy form of reproduction once fairly universal in the world's offices. You typed, once, on a waxed paper 'stencil', clipped this over a silkscreen device with a moving pad or drum of ink behind it, and your mimeograph ran off (or silkscreened, really) as many copies of your document as you required. Owing to the physical peculiarities of the medium, though, it was unwise to underline too frequently on a mimeograph stencil: the single unbroken line was particularly prone to tear, producing leaks and smudging.

    People who liked books, and frequently wrote letters, on typewriters, to other people who liked books, tended, free from the constraints of an academic stylesheet, to render titles in all-caps. People who wrote about books for publication in amateur journals (mimeo was an authentic medium of the American samisdat) rendered titles in all-caps in order to avoid stencil-tears. At various times, I was both.

    It's such a pleasure having this kind of stuff to read every day!

    copyright law ip history

    Returnadores

    Returnadores: a New Life in the Old World. 'Imported from Argentina to help save the village from a decades-long decline in population which threatened its very future, the Paez family has travelled backwards along the path of the first conquistadores and the generations of Spanish emigrants who followed them.'

    history spain travel

    Random Word of BIG LETTERS

    Leonard notes the 'Random word of mixed symbols with length 1 to 27' type spammer obfuscation, suggesting it's 'open source spam'; I reckon it's more 'literate programming spam', in that it's self-documenting. But it certainly is very wierd. Maybe some spamtool developer has a COBOL fetish.

    Anyway, just got back from a very enjoyable work trip to find my visa documents have arrived -- so things are probably going to heat up 'round about Thursday, when I have my interview at the US Embassy. Once that happens, it's full speed ahead on flights, shipping, figuring out how to transport the cat, handing over house to new tenants, etc. etc...

    spam anti-spam security

    Bitstream come through with Vera

    Bitstream Vera released as a beta. The full release, sometime next month, will use an extremely open license. To quote the FAQ:

    Are derivative works allowed?

    Yes!

    I want to sell a software package that uses these fonts: Can I do so?

    Sure. Bundle the fonts with your software and sell your software with the fonts. That is the intent of the copyright.

    Hey presto -- open source fonts! Good work by Jim Gettys, Bitstream and GNOME in making these available.

    copyright linux coding hardware law ip

    World's first 419 revenge killing? (fwd)

    BlogStart:

    Spam: The Register: World's first 419 revenge killing?

    Michael Lekara Wayid, 50, Nigeria's consul in the Czech Republic, was shot dead at the embassy yesterday morning. The embassy's 37-year-old receptionist was shot in the hand during the melee which began after a suspect opened fire after visiting the embassy to discuss an unspecified business matter yesterday morning. A 72-year-old Czech man was arrested at the scene on suspicion of murder, the BBC reports. Unconfirmed, and thus far sketchy reports, suggest the unnamed suspect was a victim of a 419 (AKA advanced fee) fraud.

    Now that's taking it a bit too far IMO ;)

    security spam 419 scams law

    A new world for radio regulators

    GNU Radio, which (as noted on Boing Boing) has just released screenshots of a successfully-decoded HDTV signal, is a totally new way to receive (and possibly, in the future, send) radio-frequency signals. The FCC ponder the implications:

    The emergence of the low-cost, generally available SDR which can be configured with ... open software will present a new issue for regulators. What will be placed in the hands of the public entrepreneurs, amateurs, and even those with malicious intent will be machines which in principal can emulate, send, and receive any radio signal on any band. ...

    Then, with the world-wide availability of software that can even be modified if needed, any radio transmitter or receiver can be emulated. Bans on receiver types will be circumventable with ease. Mandates such as the proposed ATSC broadcast flag will be hard to enforce (and may even fail in the presence of a single web-connected noncompliant receiver). And, although not generally an issue for the Commission, it will be possible to implement proprietary systems without the benefit of any license from the patent holder. Because the software is open, as a practical matter virtually all mandated restrictions will be at risk (except for total power output which remains a classical hardware issue). ...

    In the GNU SDR environment, we have the makings of a powerful new technology that has the potential of solving the spectrum management problem, but we may also have other people in the world writing and distributing software with their own agenda.

    Wow. That's a brave new world. I wish I knew enough about radio tech to really get a handle on this stuff...

    security privacy law dublin ireland

    AOL reports on its spam-blocking efforts

    Lycos: AOL reports to Members on Its Efforts to Fight Spam. 'Members Now Reporting 4.1 Million Junk E-Mails Daily To AOL' .... 'AOL announced that its proprietary anti-spam filtering technology is blocking up to 780 million pieces of junk mail every day from reaching member e-mail inboxes, which amounts to an average of 22 blocked spam e-mails per account daily.'

    Of course, they don't say how much mail overall arrives at AOL, but I'd hazard a guess it's not much over 1,300 million messages per day based on those figures.

    anti-spam spam aol

    Hotmail getting tough on spammers

    Reg: Hotmail files anti-spam lawsuit. 'Microsoft has targeted spammers with a lawsuit aimed at bulk mailers who harvest email addresses of Hotmail subscribers in order to bombard them with junk. ... In the suit, Microsoft alleges that unnamed bulk mailers used tools to randomly generate email addresses prior to testing this list out to see which accounts were active. Essentially this is a form of dictionary attack, which Microsoft argues violates federal laws including the Computer Fraud and Abuse Act. Trespass is also involved in the attacks, the software giant argues.' Go Hotmail!

    Also noteworthy: Out-Law.com: The Spammers Are Watching You: 'Eight out of ten spam e-mails contain covert tracking codes which allow the senders to record and log recipients' e-mail addresses as soon as they open the message.' well, duh, that's why SpamAssassin has a WEB_BUGS rule. Unfortunately, eight out of ten legit HTML newsletter mails also contain web bugs, too. :(

    spam anti-spam spamassassin

    Incredible Documentary on the Venezuelan Coup

    last night RTE showed Chavez - Inside The Coup, a documentary about the 2-day coup d'etat in Venezuela in April 2002 which overthrew Hugo Chavez, and was then in turn overthrown in a popular uprising.

    It was incredible. The team had amazing access to Chavez and the presidential palace while the 2-day coup and mass protests went on. The cameras are right there while Chavez is taken into custody by the generals, carries on rolling through the censorship of the media, through the street protests and shotgun-blasting riot police, and then catches the loyal-to-Chavez presidential guard retaking the palace from the inside.

    Finally, it follows the negotiations to get Chavez returned from custody etc.; his cabinet are right there, on screen, talking to the generals on the phone while you watch and listen. Incredible footage, right from the thick of it.

    As far as I could tell, it's called Chavez - Inside The Coup, and is by Power Pictures, Irish lads from Galway, no less.

    I've never seen anything like it. If you get a chance, don't miss it.

    politics privacy google

    Sony's Civil War

    Wired: The Civil War Inside Sony.

    By rights, Sony should own the portable player business. The company's first hit product, back in the '50s, was the transistor radio, the tinny-sounding invention that took rock and roll out of the house and away from the parents and allowed the whole Elvis thing to happen. A quarter-century later, the Walkman enabled the kids of the '70s to take their tapes and tune out the world. But the 21st-century Walkman doesn't bother with tapes or CDs or minidiscs; it stores hundreds of hours of music on its own hard drive. And it sports an Apple logo. ....

    Where the iPod simply lets you sync its contents with the music collection on your personal computer, Walkman users are hamstrung by laborious 'check-in/check-out' procedures designed to block illicit file-sharing. And a Walkman with a hard drive? Not likely, since Sony's copy-protection mechanisms don't allow music to be transferred from one hard drive to another - not an issue with the iPod. 'We do not have any plans for such a product,' says Kimura, the smile fading. 'But we are studying it.' ....

    What's changed since the original Walkman debuted is that Sony became the only conglomerate to be in both consumer electronics and entertainment. As a result, it's conflicted: Sony's electronics side needs to let customers move files around effortlessly, but its entertainment side wants to build in restraints, because it sees every customer as a potential thief.

    music mp3 filesharing copyright apple ireland software

    Ashutosh Varshney on ethnic conflicts

    Great interview with Ashutosh Varshney, an Indian political scientist investigating ethnic violence. From New Scientist, via Damien Morton on FoRK.

    So what is the key to predicting which communities will turn violent and which will remain peaceful in times of ethnic unrest?

    It comes down to how the cities or villages are structured, and the networks that people form across religious or ethnic divides. In India I have identified two types of civic network, which I call the associational and the everyday. The everyday type covers things such as Hindu and Muslim children playing together and their families and friends visiting each other or eating with each other, or taking part in festivals together. The associational type involves the two groups being members of the same trade unions, sports clubs, student unions, reading clubs, political parties or business organisations. Associational structures go beyond neighbourhood warmth, and in times of unrest they are much more robust. They can be a serious constraint on the polarising strategies of political elites. Places with strong networks of this kind are very likely to remain peaceful.

    ireland history tech

    Reverse-engineering: now even easier with added XML

    Slashdot posts a story about 'Hacking the Streamium' -- the Streamium is an 'internet micro hi-fi' made by Philips. The poster writes 'the main gripes (are) that Philips controls which Internet radio stations you can listen to and that the PC-link software ... only runs on Windows. I managed to fix both of these problems by reverse engineering the PC-link protocol and writing my own pc-link server in perl, which can be run on practically any OS, *and* can trick the Streamium into playing any Internet MP3 stream that you want'.

    A quick look at his page notes 'the protocol consists of fairly simple xml tags'. It sure does; I'd imagine it took all of 5 minutes with a tcpdump reversing that! In fact, it looks so easy to reverse-engineer, you'd have to wonder if the engineers at Philips weren't hoping something like this might happen ;)

    music linux mp3 apple ireland esd

    Marching on Traffic-cam

    traffic-camera pictures of the London anti-war march! What would J. G. Ballard make of this? ;)

    and here's Hyde Park:

    Unfortunately none similar of Dublin.

    In passing -- an interesting factoid found on Adam Back's PGP Timeline page: 'While Iraq was still a secret US ally against Iran, Iraqi exchange students (in the US) using the same literature as (Phil Zimmermann, inventor of PGP) later did, wrote a working (Public Key) cryptosystem for (the Iraqi) military - which was using poison gas against the Kurds at the time.' Hmm, ironic!

    ireland dublin politics

    Everest Base Camp to get internet cafe

    BBC: High hopes for Everest cybercafe. 'Tsering Gyalzen hopes the internet facility at Mount Everest base camp will open by March. Proceeds from the venture will support pollution control at the camp, which is used by climbers hoping to scale the world's highest peak. Mr Gyalzen, a member of the Sherpa community, says launch plans for the ambitious project are in the final stage. He told the BBC he was awaiting permission from the authorities to install VSAT digital satellite and other equipment at the base camp, which is over 5,000 metres above sea level.' How cool is that?

    internet climate-change art uk ireland

    Mark Fletcher and Trustic

    Mark Fletcher is the guy behind Trustic, a new system which combines aspects of DNSBLs with (what Raph reckons is) a 'PageRank-ish trust metric'.

    My take on Trustic is that it needs a way to accumulate trusted, non-spam-relaying addresses; I'm not sure how they intend to get that, apart from people setting up accounts to say 'this is my server'.

    Anyway, he also has a blog, with this very interesting (and scary) snippet:

    Elance, Spammers, and the Global Economy

    eLance is a web site that connects contractors with companies looking to outsource projects. Companies post projects, including detailed descriptions of the work to be done, and contractors or contract houses bid on them. ... So what were many of the projects on eLance about? A quick scan revealed project titles such as: Email Address Extraction From Web Site, Ebay Email Extractor, Linux highspeed directmailer, and Bulk E-Mail and E-Mail Extraction Project. Elance is providing a way for spammers to develop new spam technologies, utilizing a cheap, skilled global work force!

    Yikes. Sure enough, a search of eLance for 'bulk mail' reveals a seller called bulkemail01 (1-5 employees, headquartered in the USA): Bulk Mailing and Offshore Hosting Solutions: ' We provide bulk email soultions and offshore hosting for the advanced bulk mailer.'

    And these projects -- as Mark notes, the project descriptions require a login, but the prospective-seller comments do not, so I've reproduced some snippets here. A search for bulk mail reveals 11 open projects, including: Bulk Mail Server and Bulk Mail Service Needed Immediately, Bulk E-Mail and Targeted E-Mail Extraction Project, Distributed Bulk Emailer, and bulletproof hosting and mailing needed.

    A bunch called DbInnovation, 10-13 employees, based in Hungary and Russia, comments on one project that 'we are developing a high performance linux e-mailer. Sends through all kinds of proxies, uses several antifitering techniologies, uses random subjects and 'from' addresses, etc, etc, etc (LOTS of other features). Web-based control centre for it. The mailer can be run on 30-50 servers simmultaniously and controlled from one place. Every server sends LIGHT FAST - 5-7 millions daily. It is VERY complicated and POWERFULL clustered software. It was written on C and it tunes Linux kernel to make the speed as fast as possible. The sw is under redevelopment and will be ready to March.'

    Hostrus, aka 'Hosting R Us', 6-19 employees, Toronta, Canada: comments 'We offer reliable spam tolerant bullet proof hosting that will NEVER get shut down!! we provide reliable bullet proof hosting We can provide you with references,test IPs and provide you with a solution'.

    dsln (profile 'no longer available'): We have servers in Jakarta, Indonesia, India, Japan , Brazil, Arentina, Russia. And all of them are BULK EMAIL FRIENDLY. You server will never e SHUT DOWN due to complains. The ISP's will take up all the heat,what soever. The line would be 2MBPS one.You will also get 16 IPs per server, which can be changed every 15 days as you want. New Pool of IPs can be given to you every 15 days. These servers can be utilised very well for the mailing, you ae looking at. ... We can do these kind of mailing for you. We mail arround 8-10 Million email IDs , using several servers and can do this kind of mailing for you as well. The cost for sending 10 Million emails would be $1050.

    MobileSoft (Karachi, Pakistan): 'We can provide you the SPAM Friendly Dedicated servers with control panel , we can handle more than 50 K Complaints daily, we will provide you the ips as your requirement'.

    prompt (Anmol Solutions, Argentina): 'I can host you at 4 bullet proof places, 2 in Arg and brazil each, i can give you 2 *256 ips if you want and you will have 10 MPBS line. For each server you will be charged $250 per month and $400 setup charges, you may easyly go upto 25 servers with the same amt of bw yes u may mail u may host u may do what ever you want :)'

    A couple of other sites show the same situation: here's a project at ContractedWork.com to build a 'Bulk Mailer using open Proxies'.

    In other words, these sites provide what seems to be a good look into the heart of spamware development. Scary stuff.

    BTW an open invitation: if any 'white hats' out there get their hands on specific spamware, I'd appreciate them dropping me a line (email addr here). The idea is to analyze the tools and get good signatures for their spam, then add those signatures to SpamAssassin.

    In other news, Slashdot reports that SpamAssassin apparently blocks Crypto-Gram. Not quite the case: as Dan points out, it gets 3.2 on version 2.44, and 1.9 on the nearly-released 2.50. That's well inside the 'this is ham' range. However, this comment reports that the mail has been listed in Razor, which pushes it up to 5.9...

    So more correctly -- Razor thinks it's spam, not SpamAssassin ;)

    anti-spam spam web weblogs

    Richard Dawkins on GM foods

    Richard Dawkins: why Prince Charles is so wrong (via BB).

    An interesting read, if only because Richard Dawkins misses several massive chunks of the anti-GMO argument, as several folks point out on the BB discussion board. Firstly, the profit drive is the only thing driving deployed GM products, and that's already been shown to produce unsafe results, in the UK with BSE. Secondly, as one of the posters says, 'Oh, yeah -- Dawkins is absolutely right (in comparing GM to modifying running software): Nothing to gripe about when people tinker with your mission critical apps'.

    patents ip law

    **GTA: Vice City**

    Grand Theft Auto: Vice City has been nominated for the Designer of the Year award in London:

    'We will be highlighting the reason why it is worthy for this prize,' (the curator) added, noting the game's attention to detail in costuming, music and atmosphere.

    'I've never been so excited to just watch a video game, never mind playing it,' said Sellers. 'It is really great to see all the details and feel the nuances. Playing it is even better.'

    I must say, I have to agree. It's easily one of the best games I've ever played; insanely playable and full of amazing attention to detail. The content's a bit strong in places, but the same can be said of Mean Streets or Scarface, and I'm sure they may have picked up an award or two themselves, along the way. It's just (interactive) fiction.

    gaming games movies

    Proposed Irish data retention laws

    Karlin notes this about 'the extraordinary letter the Department of Justice sent out this week to various parties'.

    According to the letter, the Department will hold a preliminary forum to 'initiate' a consultation process on its proposed three-year data retention bill ... The forum begins at 3pm -- clearly making sure no long and unruly discussions will develop! -- and starts with a 20-minute address by the Minister, followed by a 20-minute address by the Dept of Communications on the 1997 EU Data Privacy Directive (which, BTW, Ireland STILL has not implemented despite being under legal threat by the EU -- and note that there's no mention of the far more crucial 2002 amended Directive, voted in last May by a spineless and ill-informed EU Parliament, which allows for up to SEVEN YEARS data retention.

    Then -- and this is the amazing bit -- attendees get a 20 minute pep talk by An Garda Siochana (the Irish police force) 'on the contribution of data retention in the fight against crime.'

    When you pick yourself up off the floor, remind yourself that this is the Irish government's formal initiation of a purported public discussion on data retention -- brought to you by the Irish police. Amazing. You'd have thought they'd at least *pretend* to be balanced and disinterested, and perhaps ask Joe Meade, the Irish Data Protection Commissioner, to contribute as well. ...

    The Department of Justice itself should have nothing whatsoever to do with ANY consultation process on this proposed bill. Instead, as in the UK, an independent Dail group should hold hearings and get public input into this.

    ireland privacy eu law data-protection data-retention dri

    They seek him here, they seek him there...

    Looking for an old mate, Alan Toner, and it's turning out to be tricky; the last mail address I had for him now bounces.

    It seems all three. He gets around!

    security uk 419

    IraqBlog

    Dear Raed -- a blog from an Iraqi bloke called Salam Pax. It's amazing to read this; a true, educated, passionate, reasonable voice from inside Iraq.

    The trenches and sandbag mountains I wrote about last week are now all over Baghdad. They are not being put there by the army; they are part of the Party's preparations for an insurgence. Each day a different area of Baghdad goes thru the motions. Party members spread in the streets of that area, build the trenches, sit in them polishing their Kalashnikovs and drink tea. The annoyance-factor of these training days depend on the zeal of the party members in that area. Until now the worst was the (14th of Ramadan) street, they stopped cars searched them and asked for ID and military cards, good thing I wasn't going thru that street, I still have not stamped my military papers to show that I have done my reserves training.

    Totally off on a tangent, but that street-name reminds me of a line from McCarthy's Bar (extract here):

    In Germany once, in the military garrison town of Erlangen, I had a few drinks with three American GIs who were planning to visit England because it would be neat to see where John Lennon and Elvis grew up'. They also wanted to know if they could use dollars, and would the street signs be in English? I tried to tell them about Elvis coming from Tennessee, but it seemed to make them want to kill me. The Twenty-eighth Rule states: Never Get Drunk with Soldiers (particularly in countries where the streets are named after dates).

    politics coding privacy

    SHOWDOWN in the CRISIS in the WAR in IRAQ in the GULF

    SomethingAwful provide their own inimitable spin on how the potential war in Iraq will be fought, featuring Operation: Fifty Legions of Sardaukar ('Imperial strategists estimate minimal casualties among the Sardaukar troops and allied forces of Baron Tony Blair and House United Kingdom'), and Operation: Winnuke ('US_of_A(NATO) wants to send you the file Dance_Routine(Funny!).wmv.vbs').

    history funny games

    Spam about spamming

    how unfortunate! I guess this spammer hit the wrong key when selecting which set of addresses to send this mail to...

    Joshua,

    Here is the harvested list 165 names for telecom central office installation. Put together a email promo that we can send out.

    Dad

    Subject: Telecom email broadcast marketing
    From: "Larry" ...
    Date: Fri, 7 Feb 2003 07:12:43 -0700 (14:12 GMT)
    To: "Joshua Dyer (E-mail)" ...

    (Here's the full text, headers and all:)

    From ... Fri Feb 7 17:57:50 2003 Return-Path: ... Delivered-To: ... Received: from localhost (jalapeno)
    by jmason.org (Postfix) with ESMTP id 119CB16F17 for ... Fri, 7 Feb 2003 17:57:49 +0000 (GMT) Received: from jalapeno by localhost with IMAP (fetchmail-5.9.0) for ... (single-drop); Fri, 07 Feb 2003 17:57:49 +0000 (GMT) Received: from mail.oelsales.com ([216.205.114.98]) by dogma.slashnull.org (8.11.6/8.11.6) with ESMTP id h17Fv7E22990; Fri, 7 Feb 2003 15:57:09 GMT Received: from LARRY by mail.oelsales.com with ESMTP (SMTPD32-7.13) id AF4F931006A; Fri, 07 Feb 2003 08:14:39 -0600 From: "Larry" ... To: "Joshua Dyer (E-mail)" ... Subject: Telecom email broadcast marketing Date: Fri, 7 Feb 2003 07:12:43 -0700 Message-Id: ... MIME-Version: 1.0 Content-Type: multipart/alternative; boundary="----=_NextPart_000_0503_01C2CE78.4F82BA40" X-Priority: 3 (Normal) X-Msmail-Priority: Normal X-Mailer: Microsoft Outlook CWS, Build 9.0.2416 (9.0.2911.0) X-Mimeole: Produced By Microsoft MimeOLE V6.00.2800.1106 Importance: Normal X-Spam-Status: No, hits=4.5 required=5.0 tests=BAYES_30,HTML_70_80,HTML_FONT_COLOR_BLUE,
    HTML_FONT_COLOR_GREEN,HTML_FONT_COLOR_RED, HTML_FONT_FACE_ODD,HTML_MESSAGE,RCVD_IN_NJABL, SMTPD_IN_RCVD,X_NJABL_OPEN_PROXY version=2.50-cvs X-Spam-Level: X-Spam-Checker-Version: SpamAssassin 2.50-cvs (1.167-2003-02-03-exp)
    This is a multi-part message in MIME format.

    ------=_NextPart_000_0503_01C2CE78.4F82BA40

    Content-Type: text/plain; charset="iso-8859-1" Content-Transfer-Encoding: 7bit
    Joshua,

    Here is the harvested list 165 names for telecom central office

    installation.

    Put together a email promo that we can send out.

    Dad

    Larry Dyer, President

    OEL WORLDWIDE INDUSTRIES : Worldwide Optics PO Box 445 Palmer Lake, CO 80133 websites: www.oelsales.com & www.worldwideoptics.com Corporate: 719 559-0951 Fax: 719 559-0955 National Sales: 800 818-2244
    ------=_NextPart_000_0503_01C2CE78.4F82BA40
    Content-Type: text/html; charset="iso-8859-1" Content-Transfer-Encoding: quoted-printable
    Joshua,
     
    Here=20 is the harvested list 165 names for telecom central office=20 installation.
     
    Put=20 together a email promo that we can send out.
     
    Dad
     
    Larry Dyer,=20 President
    OEL=20 WORLDWIDE INDUSTRIES :
    Worldwide =
    Optics
    PO Box 445
    Palmer Lake, CO = 80133
    Corporate: 719 = 559-0951
    Fax: 719 = 559-0955
    National Sales: = 800 818-2244


    ------=_NextPart_000_0503_01C2CE78.4F82BA40--

    spam anti-spam spamassassin smtp

    Jhai Foundation notes bus attack in Laos

    The latest Jhai Foundation newsletter notes an attack on a bus in Laos:

    Some of you may have heard about a 'terrorist attack' in Laos yesterday. The reports are true. Eight People on a bus and two people on motorcycles were killed after a robbery. Two of them were internationals. Their identities and nationalities have not yet been confirmed. The attackers are thought to be Lao citizens, probably Hmong, possibly still caught up in the war that ended 28 years ago here. This will not be confirmed until they are caught.

    This incident took place more than 30 km North of Vang Vieng or about 100 km North of our launch site. This is a sad day in Laos.

    Whoa, I think I was on that bus a year ago! As I recall, that area of Laos is still noted for occasional bandit attacks...

    Date: 07 Feb 2003 22:29:44 +1100
    From: ...
    To: ...
    Subject: Jhai Foundation Remote Villages Network Update, Security Issues, New FAQs, Press Visas

    Jhai

    Foundation Remote Villages Network.

    An

    update from Lee,
    New FAQ's,
    Security Issues and

    If You Need a Press Visa

    Contacts:


    Jesse Thorn 1 415 225 1665, ...


    Earl Mardle 612 9787 4527, ...

    Enthusiastic "Ground Level"

    support team.

    Jhai's

    From

    Lee Thorn in Laos

    Dear friends,

    We are on

    track and we will launch on 13 February. Lee Felsenstein arrived last

    night and is whipping us into shape in his gentle, nerdish way. Ed Gaible

    arrived with him and is now up a tree on a mountain above the village

    of Phon Kham. All of us - about 40 people between the village and our

    staff and volunteers - are working hard and our spirits are high.

    A

    Sad Day For Laos

    Some

    of you may have heard about a 'terrorist attack' in Laos yesterday. The

    reports are true. Eight People on a bus and two people on motorcycles

    were killed after a robbery. Two of them were internationals. Their identities

    and nationalities have not yet been confirmed. The attackers are thought

    to be Lao citizens, probably Hmong, possibly still caught up in the war

    that ended 28 years ago here. This will not be confirmed until they are

    caught.

    This incident

    took place more than 30 km North of Vang Vieng or about 100 km North of

    our launch site. This is a sad day in Laos.

    Security

    Arrangements For The Launch

    As I write, Vorasone Dengkayaphichith, our great country coordinator,

    is meeting with officials in Hin Heup District and Vientiane Province

    to make final arrangements for security for all people at our launch and

    party on 13 February. Vor and I know many, many children in the village

    of Phon Kham and the other villages and Bounthanh has nieces and nephews,

    and sisters and brothers and her parents there, too. Those children will

    be safe - and, I believe, we will be safe, too.

    Our remote

    village project is a sophisticated, appropriate high tech endeavor designed

    by Lee Felsenstein and his excellent team specifically for the needs as

    expressed by the villagers who are getting the system.

    And this

    project rests in Jhai Foundation, ... which is a reconciliation organization

    which, now, has worked for over five years in Laos, and nearly three,

    now, on state-of-the-art IT projects. Jhai Foundation is we people in

    it and our relationships - and there are hundreds of us doing something

    every day - and we are located all over the world.

    Reconciliation,

    like peace - and like development - is the opposite of war. Reconciliation

    is the process of recognizing our connection - something that always was

    and always will be, something very, very valuable. Jhai - in Lao - means

    the spirit and energy of connection, as well as hearts and minds working

    together ... and many other similar things. It is neutral. It is up to

    us how we act, how we respect.

    War and peace

    are matters of choice. Sometimes we choose to close down and kill. For

    this - I know and most Lao people know - you pay until you die. The price

    is unbelievably huge. Other times we choose to open up and connect. For

    this - thanks to Lao people who teach me about this daily by the way the

    are and act - I know you get the chance for joy, the chance to recognize

    others as just plain people ... and the chance to know and like yourself.

    The choice, it seems, is easy. What shall we take?

    In an age

    of terrorism - which breeds fear like a virus - it is best to connect.

    We choose to connect, to move forward, to do what we can do - with you

    • to help some poor folks who are friends of ours connect with one another and when they want to, with us. The benefit, we hope, is unbelievably huge.
      • Come to our launch. We will dazzle you with fun!

        Join us,

        Lee Thorn chair, Jhai Foundation

        PS Please do not hesitate to consult our FAQ or to email Jesse Thorn, ... or earl mardle, ... face="Verdana, Arial, Helvetica, sans-serif" size="2">. If you need to talk with one of us in Laos, that can be arranged.

        New FAQ's

        What Were The Greatest Problems To Create The Technical Solution?
        From Jhai's perspective it has been funding and localization. We have done this on a very small budget - lower five digits in US dollars - with the help of many engineers and other technical people. The technical lead was taken by renown computer designer Lee Felsenstein.

        A team of over 20 people donated their time. This time is worth, we estimate, perhaps $0.5 million. Localization has not been easy. For example, the team had to create new Unicode mappings for existing fonts. The relation of English to Lao is anything but direct.

        Which Impact Will The Internet Access Probably Have On The Villagers?
        They believe it will give them the opportunity to have a closer relationship with their extended families and to get better prices for their products at market. It is like a road for them.

        Is A Prototype Already Working?
        We have tested all components. The Jhai PC works. We are now completing the 'marriage' of the software and the hardware.

        Do You Think The Jhai PC Will Help Bring Access To Remote Sites In Other Countries As Well?
        The answer is 'yes'. We have had inquiries from 40 countries and we expect observers from about several major development funding agencies to see our launch in the village of Phon Kham on 13 February.

        We designed specifically in terms of the expressed needs of people in five villages that have no electricity, no phones or hope of cell phone connectivity, and no good roads in the rainy season. I learned years ago from the Independent Living Movement of People with Disabilities that when people design for the folks with the most challenges, the tool works for many people equally or less challenged. I suspect this principle works with the Jhai Computer and Communications System.

        How Important Is The Way Jhai Works?
        I suspect that our development efforts - using the reconciliation model we have developed based on relationships between people on opposite sides of a devastating war, also will have wide application. Jhai Foundation and the villagers of Phon Kham have gotten to know each other over five years. Each of us brings our whole selves and our whole experience to the table. We all are through with war. It is amazing what happens when people are willing to stay in the room and communicate - no matter how hard it is.

        Many technology projects fail because the application becomes focused on the technology first; that often doesn't work. Jhai's model focuses on people and communication, the need for the technology grows out of that. We get to the technology through communication, not the other way round.

        Press Visa Requirements
        If you plan on coming to the launch and you are press, please make arrangements for a press visa and minder immediately. Jhai may be able to help if you follow these steps:

        1. Send the following Information to ...
        2. Email Subject Line:
          PLEASE RUN PRESS VISA PERMISSION
        3. In the email we need the following information:
          • Full
            • name as it appears on the person's passport
          • Country of the passport
          • Passport Number
          • Date of Arrival in Laos
          • Date of Departure from Laos
        4. Explicit detailed list of any equipment (taperecorders, cameras, etc.) you are bringing.
          Including BRAND NAME and MODEL #.
        5. Complete Laotian itinerary in detail. For example,
          • 10 February
            • Arrive Vientiane
        • 11 and 12 February - Travel to Phon Hong, Vientiane Province
        • 13 and 14 February - Travel to Phon Kham, Vientiane Province 13 Feb.
        • 15 February Depart Vientiane

        politics china phones ireland

    A sextet of ales!

    subject line of the week -- sounds like the spammer's been listening to Homer's Vocabulary Builder tape:

    Subject: < Hi Jm, I am Bella, concupiscent youngster >

    spam anti-spam funny

    Apple's 'Bounce To Sender' a Bad Idea

    Matt journals a snippet from Apple's eNews newsletter (originally forwarded by Skip Montanaro on the spambayes list), as follows:

    Delivering a One-Two Punch to Spammers

    Yes, Mac OS X Mail can help you deliver a staggering blow to spammers. Simply pull down the Mail menu, choose Junk Mail, and select Automatic. The next time you receive email, Mail will move suspect email into a Junk folder.

    Now you're ready to deliver a real knockout punch to spammers by taking advantage of yet another potent spam-fighting weapon:

    1. Click on the Junk folder.
    2. Type Command-a to select all of the email in the Junk folder.
    3. Choose Bounce to Sender from the Message menu.

      Mail will return the selected messages to the senders marked User unknown, making them think your email address invalid, encouraging them to drop you from their lists, and, thus, eliminating spam at its source.

    Read on for details as to why this does not work (warning: long).

    Subject: Bad move, Apple
    From: Skip Montanaro ...
    Date: Thu, 6 Feb 2003 11:45:24 -0600 (17:45 GMT)
    To: ...

    Got this in today's Apple eNews mailing:

    1. Delivering a One-Two Punch to Spammers .........................................

      Yes, Mac OS X Mail can help you deliver a staggering blow to spammers. Simply pull down the Mail menu, choose Junk Mail, and select Automatic. The next time you receive email, Mail will move suspect email into a Junk folder.

      Now you're ready to deliver a real knockout punch to spammers by taking advantage of yet another potent spam-fighting weapon:

    2. Click on the Junk folder.
    3. Type Command-a to select all of the email in the Junk folder.
    4. Choose "Bounce to Sender" from the Message menu.

      Mail will return the selected messages to the senders marked "User unknown," making them think your email address invalid, encouraging them to drop you from their lists, and, thus, eliminating spam at its source.

      http://www.apple.com/macosx/jaguar/mail.html

    Justin's comments:

    This sounds like an attractive idea at first -- mail 'user unknown' Delivery Status Notifications back to the spammers, and they'll take your address off their lists. However, it doesn't work, and may actually send more noise to non-spammers. Here's why.

    • First of all, most spam these days is sent using one of three
      • originating-address methods. The first is totally randomly generated From, Reply-To and/or Errors-To addresses, typically at a big ISP like Yahoo! or Hotmail. So replying to these with a 'user unknown' DSN will result in nothing more than wasting your own, and that ISP's, bandwidth, as the address never existed anyway.
    • The second method is for the spammers to use a random address plucked from the same 'addresses to spam' list your name is on. So your 'user unknown' DSN will be sent to someone else on the spam-list, increasing the amount of crap they get in their mailbox. Oops.
    • Third is the joe-job. This is where the spammer has deliberately picked the address of someone they dislike, so that a barrage of complaints, legitimate 'user unknown' messages, and -- yes -- forged 'user unknown' messages! -- will be sent to that person. Generally, if an spam-fighter gets joe-jobbed, you can be sure they're doing something right ;)

    Next -- even if the spammers were to see your 'user unknown' message, they do not act on it:

    • There is a way for 'user unknown' messages to be communicated back to
      • the spammer (by doing it in the very first SMTP transaction). However, many folks who have tried this method have noted that it has no effect; spamware tools take a 'fire and forget' approach.

        After all, spammers want to send the mail as fast as possible, before they're blocked from the relay or proxy they're abusing, and before the DNSBLs and Razor react. So the method is simply to send as much mail as possible, without waiting for replies, and with as little identifying information as possible (to make it hard for them to be tracked down). In other words, any data coming back from the receiver is worthless to them, and may in fact get them shut down, so must be avoided.

    • Another factor is that, if your address is one of those 'Addresses on CD', you've got hundreds of spammers you'll need to send bounces to (and hope they honour them). Each one of those spammers has a different copy of the address list, so removal from one -- if it happens -- won't help with removal from the others.
    • Yet another aspect is that they do not want to reduce the number of addresses they send to. Spam economics is such that 2,000,000 addresses on CD are worth more than 1,000,000 addresses on CD, and who cares if half of them bounce, 'cos you've paid your money already ;)

    So, anyway, that's why sending fake-bounces in response to spam is bad.

    One pay-off, however, is that it makes the creation of spam-traps easy:

    HOW TO MAKE A SPAM-TRAP

    • Take an old account that gets too much spam, set up an auto-reply saying
      • "this person has moved to ... (although probably using a less machine-readable address format).
    • 3 months later, delete the account so it bounces with 'user unknown'. That should clear out all the well-behaved mailing lists.
    • 6 months later, redirect it to yourself and monitor it, to catch the badly-behaved legitimate bulk mailers who do not handle bounces correctly (yes, there's a few of these, unfortunately.)

    • 1 month after that, set up an alias that runs "spamassassin -r". Install Razor, DCC and Pyzor. Set up a Razor account. Fix the old account's addresses so they forward to this alias. Also worth piping it to the Blitzed.org OPM checker.

    • Hey presto, there's your spam trap!

      anti-spam smtp spamassassin backscatter email bounces spam

      GNOME 2.2

      GNOME 2.2 includes nifty new font technology, I see; including 'drag into ~/.fonts' font installation, at last, thanks to Keith Packard. I especially like this:

      Jim Gettys and the GNOME Foundation Board worked with Bitstream, Inc. to arrange the donation of the Vera font family to the Free Software community.

      Here's what Vera looks like; very nice. Finally, some decent free fonts -- kudos to Bitstream.

      And I see subpixel smoothing is now right in there, in the basic font preferences. Excellent news!

      But where TF is the Metacity documentation? Maybe there's none, in the tradition set down over generations of GNOME hacks^Wapplications. (Pet peeve: every command in the default PATH should have a manual page IMO.)

      The 'documentation' and 'home page' links I can find all lead to a directory of tarballs. Great. The best result Google can find, after the aforementioned tarballs, is a blog posting complaining about Metacity. Hmm -- scary -- I really don't like the implication that the only way to do my own key-binding prefs, is to run a batch of 15 gconftool commands every time I log in... ah shaggit, I'll use sawfish ;)

      (PS: yes, I'm still on GNOME 1. That's what happens when you're stuck on the wrong end of dial-up.)

      Crypto: The Crypto Gardening Guide and Planting Tips by Peter Gutmann. Excellent advice on how crypto designers should design protocols so that they can actually get implemented. Also, as a corollary; good tips on common crypto gotchas for implementors to watch out for. Some bonus funnies, too:

      Note: PGP adopts each and every bleeding-edge technology that turns up, so it doesn't figure in the above timeline. Looking at this the other way, if you want your design adopted quickly, present it as the solution for an attack on PGP.

      A little bit more introduction on some of the items would be worthwhile though. I don't have a clue what OAEP is for example ;)

      history storage open-source google

      Auth cookies in SMTP

      Jeremy describes a way to kill off 'joe-jobs' -- the practice of forging somebody's address on spam, generally used to get around 'does this user exist' spam-filters, also used to 'punish' folks the spammer doesn't like. Anyway, JZ's suggestion is this:

      One of the ideas tossed about was to implement a system that would make it easy for any MTA (Mail Transfer Agent--the programs that deliver e-mail on the Internet) to verify that a message that claims to be from somebody@yahoo.com really is from a yahoo.com user.

      This is technically doable. And it might be a good idea. Especially, as I argued, if one of the other big players (AOL or MSN/Hotmail) jumps on board and uses the same technique. If either one began to do the same, I expect that a domino effect would follow. Boom. Instant adoption.

      But then he doesn't say how to do this in a way that a spammer can't forge. Dammit. ;)

      Anyway, on with the message.

      ... However, one interesting objection was raised during the debate...

      Wouldn't that just cause spammers to prey on domains that are less equipped to 'swallow a few million bounces per hour without breaking a sweat'? (To paraphrase a co-worker.)

      Yep, it would -- until those domains also instituted similar systems. Anyway, those domains are victims now anyway; I would say only about 50% of my spam comes from forged Yahoo!, Hotmail or other domains -- the rest uses domains of small ISPs, and the occasional joe-job.

      But back to the system. I would guess what Jeremy's talking about is pretty similar to the system Pedro Melo describes in the comments. It consists of 2 components:

      • a header added by the MTA at relay time -- X-Originator-Signature.
        • This contains 'an internal identifier for the person who sent it ..., a timestamp, and a MD5 of those two fields and a third secret passphrase I keep.'
      • a CGI script on a web server, which validates a pasted X-Originator-Signature header against what hashing those values with the secret passphrase produces, and responds 'yea' or 'nay'.

      A nifty idea. Jeremy, was that what you were thinking?

      anti-spam email spam smtp gmail

      SOAP and firewalls

      Taking a look at the referrers, I came across Mark O'Neill's weblog, which lists taint.org on the blogroll; Mark's the CTO of Vordel. They have a product called VordelSecure, which seems to be a SOAP firewall proxy, in the same way the Wonderwall product I wrote for Iona was a proxy for CORBA:

      When a firewall examines a SOAP request received over HTTP, it might conclude that this is valid HTTP traffic and let it pass. Firewalls tend to be all-or-nothing when it comes to SOAP. A SOAP-level firewall should be capable of:
      1. Identifying if the incoming SOAP request is targeted at a Web service which is intended to be available

      2. Identifying if the content of the SOAP message is valid. This is analogous to what happens at the Network Layer, where IP packet contents are examined. However, at the Application Layer it requires data that the Web service expects.

      Cool!

      I hear Wonderwall is still around, but rewritten from the ground up. Sorry about that to whoever had to rewrite it ;)

      security http internet ireland web

      FTC to hold spam summit

      FTC to Hold Three Day Public Spam Workshop. 'The Federal Trade Commission will host a three-day 'Spam Forum' Wednesday, April 30 through Friday, May 2, to address the proliferation of unsolicited commercial e-mail and to explore the technical, legal, and financial issues associated with it. The forum will be held at the Federal Trade Commission, 601 New Jersey Avenue, N.W., Washington, D.C. It will be open to the public and preregistration is not required.

      A Federal Register notice to be issued shortly says, 'To explore the impact that spam has on consumers' use of e-mail, e-mail marketing and the Internet industry, the Commission will convene a public forum. E-mail marketers, anti-spammers, Internet Service Providers (ISP), ISP abuse department personnel, spam filter operators, other e-mail technology professionals, consumers, consumer groups, and law enforcement officials are especially encouraged to participate.''

      anti-spam spam email filtering spamassassin

      Anti-Americanism and Anti-Europeanism

      In the last few weeks, there's been a growing discussion of what's being perceived as an 'anti-American' point of view in Europe; see Thomas Friedman on the subject. On the other side, The New York Review of Books carries an interesting essay on this subject: Anti-Europeanism in America. It contains this revealing summary of a December 2002 study:

      Asked to choose one of four statements about American versus European approaches to diplomacy and war, 30 percent of Democratic voters but only 6 percent of Republican voters chose 'The Europeans seem to prefer diplomatic solutions over war and that is a positive value Americans could learn from.' By contrast only 13 percent of Democrats but 35 percent of Republicans (the largest single group) chose 'The Europeans are too willing to seek compromise rather than to stand up for freedom even if it means war, and that is a negative thing.'

      The divide was even clearer when respondents were asked to pick between two statements about 'the way in which the war on Iraq should be conducted.' Fifty-nine percent of Republicans as opposed to just 33 percent of Democrats chose 'The US must remain in control of all operations and prevent its European allies from limiting the States' room to maneuver.' By contrast, 55 percent of Democrats and just 34 percent of Republicans chose 'It is imperative that the United States allies itself with European countries, even if it limits its ability to make its own decisions.'

      It seems a hypothesis worth investigating that actually it's Republicans who are from Mars and Democrats who are from Venus.

      politics eu google

      Cannabis Economics

      and now, on a lighter note, The Observer reports that the 'cannabis economy' in the UK is worth 11 billion UKP a year:

      A major new study is being used to advise well known household and high-street companies about the gains and losses they face as cannabis smoking becomes commonplace. Research has revealed that Britain's 'cannabis economy' is worth 5 billion a year in sales alone. Now it has been discovered that a further 6bn of consumer expenditure each year is closely linked to the growing cannabis-users' market.

      'Young people between 15 and 30 are very trend-conscious and aspirational,' said Andy Davidson, who commissioned the study for The Research Business International, trend analysts who tracked the spending habits of young people for six months.The study found that cannabis users spend an average of UKP 20 on products that accompany their drug use each time they smoke.

      Because smoking cannabis heightens appetite, users are providing a UKP 120 million weekly windfall to a string of takeaway food suppliers, such as Domino and Pizza Hut, and manufacturers of 'munchie' products such as Mars bars and Haribo jellies.

      ireland food health

      The explosion of Columbia

      as everyone knows by now, the space shuttle Columbia has exploded on re-entry over Texas. It's an extremely sad occasion, and a terrible thing to happen.

      Lots of people look on space exploration, and the astronauts who do it, as something mundane. No way -- it takes a certain kind of bravery and heroism to do this. Every astronaut (from what I've read) is clearly aware of the odds that the vehicles they use have a large likelihood of suddenly exploding beneath their feet -- and is therefore taking a huge risk on behalf of humanity, and the expansion of human knowledge. They should be viewed as heroes, as a result.

      I just hope the ISS project, and manned spaceflight in general, continues...

      Some off-beat news links you may not have seen:

      games gaming open-source

      Durian fruit

      CNN: A box of durian, sprinkled with carpet deodorizer, sparked an aviation alert in Australia on Thursday (via monkeybum):

      When they finally found the source of the smell, it was a box of durian, a large, spiny tropical fruit renowned for its fetid aroma. While many people in Southeast Asia consider the durian a delicacy, it is banned from Singapore's subway and some restaurants in the region because of its overpowering smell.

      'This wasn't a safety issue, this was gross issue -- no one wants to fly in an airplane that smells like that,' (Virgin Blue boss Brett Godfrey) said. He compared the smell of the gourmet fruit to 'something you'd find in your outdoor dunny' adding that 'it just is the most pungent, disgusting smell.'

      No shit -- durian really stinks. I've tried to cultivate the taste for it, but failed miserably. Worse, for 3 hours in the passenger seat from Khao Sok to Surat Thani in Thailand, I was stuck with a selection of 'em by my feet -- no escape!

      The nearest thing to their odor is really pungent, cheesy socks. 'foetid' is the word for it.

      food thailand fruit

      7.5% of Euro households have broadband

      SiliconRepublic: Ireland second last in Europe for broadband. But I think regular readers will know that ;) 'Ireland's already shaky claim to the title European digital hub was looking even more risible than usual today, following the latest internet penetration survey, which shows us to be languishing in second last place out of 16 European countries in terms of broadband internet penetration. '

      The usual story -- with quotes from IO's Dave Long -- and that's not surprising. I should imagine things will improve a lot this year, now that the ComReg seems a little more on the job, and eircom have halved their prices.

      But the really interesting thing is this: 'Among the survey's other findings were that 7.5pc (12 million) of all European households now subscribed to a broadband internet service. 6.3 million customers signed up for broadband for the first time in 2002 -- an increase of 55pc over 2001. ... It further predicted that a further 7.2 million European homes will acquire broadband for the first time this year, bringing the total to 19.1 million or 11.9pc of total households.'

      That's excellent news, and wipes out the FUD put about by some telcos (guess which ones) that there just isn't demand in the current market. Clearly there is strong demand throughout the rest of Europe -- and there really isn't much difference between there and here. In fact, if anything, I reckon there would be more demand here, based on the take-up of other high-tech accessories like mobile phones and games consoles.

      ireland broadband filesharing uk eircom copyright piracy

      Latency and DSL

      'It's the Latency, Stupid!', a fantastic article explaining why latency is sometimes more important than simple bandwidth.

      This was found via Karl Jeacle's comments on eircom's DSL, which are very illuminating in themselves -- although probably not too interesting for non-Irish folks ;). But the relevant part is the explanation of why they enabled interleaving on eircom's DSL network (summary: to get more reach, as far as I can see).

      ireland internet broadband networking eircom

      more Watchcam

      I found a load of snaps from my Casio Watch Camera that I hadn't uploaded yet. I'd uploaded them, but forgot to add them to CVS ;) Here's a nice one -- a ca. 19th century hygrometer made in the Mason family's opticians shop in Essex Bridge, Dublin, found in the museum at Collins Barracks:

      ireland hardware science

      The Onion comes through

      U.N. Orders Wonka To Submit To Chocolate Factory Inspections:

      UNITED NATIONS -- Responding to pressure from the international community, the U.N. ordered enigmatic candy maker William 'Willy' Wonka to submit to chocolate-factory inspections Monday. 'For years, Wonka has hidden the ominous doings of his research and development facility from the outside world,' U.N. Secretary General Kofi Annan said. 'Given the reports of child disappearances, technological advances in glass-elevator transport, and Wonka-run Oompa-Loompa forced-labor camps, the time has come to put an end to three decades of secrecy in the Wonka Empire.'

      politics ireland amazon funny

      We Are Made For Higher Timings

      a memorable mistranslation found in a guesthouse at Annapurna Base Camp :

      Photo of a memorably-mistranslated poster

      Help! I'm being underclocked! ;) Perhaps that explained the shortness of breath and dizziness...

      (I did some scanning of the hundreds of photos from last year's trip about a month ago, but haven't had a chance to fix 'em all up yet. And I'm not uploading anything until I get to CA and some decent bandwidth.)

      funny travel photos

      Monkey sense (fwd)

      A funny letter from New Scientist regarding the use of monkeys to collect specimens in the field, which was pioneered by John Corner in Singapore.

      The botanist noticed that local fruit-pickers trained monkeys to collect fruit, and reasoned that a monkey could similarly be trained to collect flowers, leaves and nuts for his own work. The result was the collection of hundreds of otherwise inaccessible specimens -- and this gem:

      Travelling with mule and monkey on a narrow path in the uplands, he spied a new and unrecognised flower on a liana hanging from the path, down a near-vertical cliff face too steep for him to climb down. So he instructed the monkey to descend and collect the flower. But the monkey just looked at him questioningly with its head on one side.

      'Go down!' repeated the eminent botanist. At which the monkey gave an eloquent shrug, took hold of the liana and pulled it up hand over hand to collect the flower. No human being, said Corner, had ever, before or since, made him feel so much of a fool.

      animals funny science

      Bank of America ATMs are net-connected!

      Boing Boing notes that the SQL Slammer worm 'caused service outages at tens of thousands of Bank of America ATMs and wreaked havoc at Continental Airlines. Apparently, customers at most of the #3 American bank's 13,000 automatic teller machines were unable to process transactions for a period of time.'

      Does anyone else find it very scary to contemplate an ATM network connected to the internet, with a sufficiently open set of firewalls that a semi-documented Microsoftish SQL protocol can traverse as far as the ATM servers? Sure, it probably took a few hops, compromising a couple of SQL servers along the way, but each of the firewalls in question must have had that MS-SQL port open for those servers. Yikes.

      Someone should teach those guys about network compartmentalization for security; something like an ATM network, where security is hugely essential, should never have a direct IP-based connection to the internet, no matter how many firewalls and gateways are in place.

      Spam: NACS: Spam Detection. Great, Catherine's new email system at UCI uses SpamAssassin. Nothing like getting bug reports from your SO ;)

      On the other side, though, they've written an excellent set of pages on how to detect and act on the SpamAssassin markup in various MUAs.

      security banking hacking ireland fraud

      deny udp any any eq 1434

      it looks like the the latest internet worm is making the rounds, and this one's a biggie. It's been dubbed 'SQLSlammer', since it hammers on the Microsoft SQL ports, attempting to exploit yet another commonly-unpatched 7-month-old MS vulnerability. The best bit: it uses UDP broadcasts to do this, so the traffic load is massive compared to previous worms, so there's lots and lots of backbone hosage as a result. Coverage:

    • Matrix NetSystems: nice (live?) graph of The State Of The Net
    • BugTraq thread

    • Disassembly and analysis of the worm

    • The SQL Server 2000 bug it exploits

    • Slashdot: MS SQL Server Worm Wreaking Havoc

    • Quick fix: update those router filters to deny all traffic, both UDP and TCP, on port 1434. (you shouldn't need to update the firewall filters of course, because nobody's stupid enough to allow access to open-internet MS SQL traffic, right? ;)

      security ddos anti-spam malware hacking ireland

      Kim Jong Il, Giant Robot

      Kim Jong Il Unfolds Into Giant Robot (Onion). Met up with Paddy Benson last night for a few drinks, and he let me into the secret that The Onion is, once again, officially funny:

      'If we add Kim Jong Il's transformation into a giant robot to his already defiant isolationist stance and his country's known nuclear capability, the diplomatic terrain definitely becomes more rocky,' U.S. envoy James Kelly said. 'Kim has made it clear that, if sufficiently threatened, he will not hesitate to use nuclear weapons or his arm-mounted HyperBazooka.'

      'We are also forced to consider the possibility that Kim may attempt to robo-meld with other members of the Axis of Evil, forming a MegaMecha-Optima-Robosoldier. Kim would make a powerful right arm -- or even a torso -- for such a mechanism.'

      Wotcher Paddy!

      funny politics usa

      Matt Blaze vs master keys

      Matt Blaze has posted a very neat exploit against 'weaknesses in most master-keyed lock systems, such as those used by offices, schools, and businesses as well as by some residential facilities (particularly apartment complexes, dormitories, and condominiums). These weaknesses allow anyone with access to the key to a single lock to create easily the master key that opens every lock in the entire system. Creating such a key requires no special skill, leaves behind no evidence, and does not require engaging in recognizably suspicious behavior. The only materials required are a metal file and a small number of blank keys, which are often easy to obtain.'

      'The vulnerability was discovered by applying the techniques of cryptanalysis, ordinarily used to break secret codes, to the analysis of mechanical lock design.'

      Paper here.

      security linux exploits

      Tardis-noise inventor dies

      Daphne Oram, one of the pioneers of electronic music, has died. (BBC)

      Almost un-noticed by the wider world, one of the pioneers of electronic music has died. Without Daphne Oram, we may never had known what the Tardis sounded like. Electronic music - as much a part of today's life as whistling a tune to yourself - grew up amid milk bottles, gravel, keys, and yards of magnetic tape and wires. These were the sort of tools typically scattered around the BBC's Radiophonic Workshop in the 1950s and 60s, when they were used to generate wonderful and ethereal sounds for the airwaves. The mother of this great legacy was Daphne Oram. Aged 18, and armed with a passionate interest in sound, music and electronics, she started work at the BBC in 1943 as a sound engineer.

      music history uk art

      Lotsa SpamConf linkage and commentary

      Another good trip report, from 'babbage' at perl.org.

      • Again, and interestingly, quite a few folks agreed with one of SA's core tenets; no single approach (stats, RBLs, rules, distributed hashes) can filter effectively on its own, as spammers will soon figure out a way to subvert that technique. However, if you combine several techniques, they cannot all be subverted at once, so your effectiveness in the face of active attacks is much better.

      • Also interesting to note how everyone working with learning-based approaches commented on how hard it was to persuade 'normal people' to keep a corpus. Let's hope SA's auto-training will work well enough to avoid that problem.

      • in passing -- babbage noted the old canard about Hotmail selling their user database to spammers. That must really piss the Hotmail folks off ;) I think it's much more likely that, with Moore's Law and the modern internet, a dictionary attack *will* find your account eventually.

      • Good tip on the legal angle from John Praed of The Internet Law Group: if a spam misuses the name of a trademarked product like 'Viagra', get a copy to Pfizer pronto. Trademark holders have a particular desire to follow up on infringements like this, as an undefended trademark loses its TM status otherwise.

      • David Berlind, ZDNet executive editor: 'They don't want to be involved (in developing an SMTPng)'. He might say that, but I bet their folks working on sending out their bulk-mailed email newsletters might disagree ;). Legit bulk mail senders have to be involved for it to work, and they will want to be involved, too.

      • Brightmail have a patent on spam honeypots? Must take a look for this sometime.

      • the plural of 'corpus' is 'corpora' ;)

      Great report, overall.

      It's interesting to see that Infoworld notes that reps from AOL, Yahoo! and MS were all present.

      Since the conf, Paul Graham has a new paper up about 'Better Bayesian Filtering', and lists some new tokenization techniques he's using:

      • keep dollar signs, exclamation and most punctuation intact (we do that!)

      • prepend header names to header-mined tokens (us too!)

      • case is preserved (ditto!)

      • keep 'degenerate' tokens; 'Subject:FREE!!!' degenerates to 'Subject:free', to 'FREE!!!', and 'free'. (ditto! well, partly. We use degeneration of tokens, but we keep the degenerate tokens in a separate, prefixed namespace from the non-degenerate ones, as he contemplates in footnote 7. It's worth noting that case-sensitivity didn't work well compared to the database bloat it produced; each token needs to be duplicated into the case-insensitive namespace, but that doubled the database size, and the hit-rate didn't go up nearly enough to make it worthwhile.)

      Most of these were also discovered and verified experimentally by SpamBayes, too, BTW.

      When we were working on SpamAssassin's Bayesian-ish implementation, we took a scientific approach, and used suggestions from the SpamBayes folks and from the SpamAssassin community on tokenizer and stats-combining techniques. We then tested these experimentally on a test corpus, and posted the results. In almost all cases, our results matched up with the SpamBayes folks' results, which is very nice, in a scientific sense.

      (PS: update on the Fly UI story -- 'apis' is not French, it's Latin. oops! Thanks Craig...)

      anti-spam spamassassin dnsbls spam

      Trip Report from the SpamConf

      Kaitlin Duck Sherwood writes a trip report. Good tidbits:

      • many big players in the mail-sending side want to see an SMTPng; a new protocol which is spam-resistant.

      • Jon Praed of the Internet Law Group said that 'better spam filters make his job easier: the more contortions that a spammer goes through to make sure that the messages go through, the easier it is to convince a judge that the spammer knew it was wrong.' Excellent!

      anti-spam filtering spam spamassassin challenge-response

      Toilet Flies

      Andrew McGlinchey writes about a Fly UI: 'I have seen one of the finest instances of user interface design ever, and I saw it in the men's room at Schipol airport in Amsterdam. In each of the urinals, there is a little printed blue fly. It looks a lot like a real fly, but it's definitely iconic - you're not supposed to believe it's a real fly. It's printed near the drain, and slightly to the left.'

      I've heard of this one before, and yes, it is an aiming-improvement UI. It started in France around the turn of the century, if I recall correctly. One important fact: it's not a fly -- it's a bee. You see, it's also a visual pun -- the french for 'bee' is 'apis', geddit?

      (I'd have commented on the blog, itself, but it's one of those 'create an account to comment' places -- too much trouble!)

      He's also spot-on about why tea is big in Ireland: 'The climate is cool, grey and damp. Steady doses of warm drink with a nice gentle caffeine push really keeps you going.' Hey, works in the Himalayas too ;)

      ireland dublin funny

      UL alert: 'out-of-office' autoreplies help burglars

      BoingBoing, back in December, forwarded this snippet: 'A report issued by UK-based Infrastructure Forum ('TIF') says spam-savvy thieves are using info from 'out of office' email autoresponders and cross-referencing it with publicly available personal data to target empty homes.'

      Criminals are buying huge lists of email addresses over the internet and sending mass-mailings in the hope of receiving 'out of office' auto-responses from workers away on holiday.

      By cross-reference such replies with publicly available information from online directories such as 192.com or bt.com, the burglars can often discover the name, address and telephone number of the person on holiday. Tif is advising users to warn their staff to be careful of the information they put in their 'out of office' messages.

      "You wouldn't go on holiday with a note pinned to your door saying who you were, how long you were away for and when you were coming back, so why would you put this in an email?" said David Roberts, chief executive at Tif. (via VNUNet)

      My take on this? Bullshit.

      I mean, how many house burglars (a) have the know-how to set up a fast internet connection, get hold of an addresses CD, and send a spam; and then (b) how often does a Reply-To address on a spam stay active once it's sent -- assuming it ever worked in the first place -- before the ISP whacks their account? I would guess 6 hours at the most, and most spam runs wouldn't even be halfway through by that stage (from what I hear).

      Self-promoting bullshit of the highest order I reckon.

      security ireland privacy spam data-protection law anti-spam gmail

      Six Degrees Tested

      Steppe by Step (Guardian). "I started wondering if (the 'six degrees of separation' theory) was true today. ... So 35 years on from the original experiment, I decided to test out the urban myth on a world stage: how many steps would it really take to get to someone on the other side of the planet?"

      The London-based "city girl" author, Lucy Leveugle, makes it in 9 steps (hey, the world has expanded!) to Purev-Ochir Gungaa, a nomadic herdsman in the middle of the steppes of Outer Mongolia. Amazing.

      mapping statistics travel

      wierd referrers

      308 referrer hits from www.xxxstoryarchive.com, 282 from amateur-porn.us, 282 from nude-lesbians.us, etc. Somehow I doubt it. All the hits are 404s, looking for e.g.

      nn.nn.nn.nn - - [12/Jan/2003:18:52:13 +0000] GET /pics54754-96 HTTP/1.1 404 284 http://www.celebrity-nude-pics.com/ "Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1; .NET CLR 1.0.3705)"

      Hits from hosts at AT&T WorldNet Services and an SBC PPPoX pool. They're all MSIE 6 on Windows, and it's been going on for a month or so.

      Theory: sounds like MSIE's download-to-'view'-offline functionality has bugs; when it hits a 404, maybe it requeues that request but then sends it to entirely the wrong IP.

      Alternative theory: it's a pathetically underpowered DDoS. ouch!

      Anyone else seen this?

      ireland censorship security spam

      Still Moving

      Who knew relocating with a cat could be so tricky? Well, actually, I did. He hates travel. I'm considering just putting him in a crate and handing him off to a courier to do it.

      Paul Graham's Spam Conference seems to be doing great; they've moved to a bigger room, and are expecting 480 (!!) attendees.

      I still can't make it due to all this movage, but thankfully there's a few SpamAssassin folks going, so we'll still be able to snarf some good tricks with any luck.

      In other news, the public mass-check submission run for SpamAssassin 2.50 is about to start; with the new with-bayes and with-net-tests dimensions in the matrix, it's going to be the biggest run yet. Should be fun.

      spamassassin anti-spam jobs

      The good news

      Frequent drinking cuts heart attack risk (New Scientist). ' Half an alcoholic drink every other day, be it wine, whisky or beer, can reduce the risk of heart attacks by a third, a new study shows. The 12-year study published in The New England Journal of Medicine found that the frequency of drinking was the key to lowering the risk of heart disease, rather than the amount, the type of alcohol, or whether or not it was drunk with food.'

      health science papers

      minor bloglet

      New Scientist: Turing tests filter spam email. "Simple tests designed to distinguish computers from humans are increasingly being used to clamp down on unsolicited, or 'spam', email advertising."

      The article notes that Yahoo! has imposed such a test to block automated account-signup-then-spam bots. (Thankfully -- that might discourage some of the more automated 419 spammers.)

      Sorry 'bout the lack of blogging -- very busy 'round here, what with a new SpamAssassin release in the pipeline and a move to the US in the offing...

      anti-spam spam funny